mirror of
https://github.com/supabase/supabase.git
synced 2026-10-13 21:29:08 +03:00
ebe236e5ff5853b8971229ffc96bbe5105eff4e7
1977
Commits
| Author | SHA1 | Message | Date | |
|---|---|---|---|---|
 Joshen Lim |
1de298ff31 |
Reinstate https://github.com/supabase/supabase/pull/45143 into latest master (#47433)
## Context Previous PR was [here](https://github.com/supabase/supabase/pull/45143) but it got stale with lots of conflicts so figured it'll be easier redo it off the latest master Moves policies page from Auth to Database under an Access Control section along with Roles. This moves all existing files, applies redirects, and updates urls to point to the new route <img width="274" height="412" alt="image" src="https://github.com/user-attachments/assets/7952c185-64ae-4355-ba36-45397efe1787" /> <img width="453" height="471" alt="image" src="https://github.com/user-attachments/assets/04b3dcb3-48a5-4049-9893-d01109fb46a9" /> ## To test - [ ] Verify that policies now live under Database correctly <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added a quick navigation shortcut to open **Database > Policies (RLS)**. * **Bug Fixes** * Updated Policies and RLS-related links across the product to open the **Database policies** area (menus, command palette, context actions, alerts, and link-outs). * Added a permanent redirect from the old **auth policies** URL to the new **database policies** URL. * **Documentation** * Updated RLS Dashboard and security checklist instructions to reference **Database > Policies**. * **Tests** * Adjusted automated tests to validate the new Policies route. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Etienne Stalmans
|
baff377621 |
chore: update docs for temporary access alpha (#47439)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? Docs update ## Additional context Small errata fix and adds note about pgbouncer not being supported <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Documentation** * Clarified temporary access guidance: it works with direct connections and IPv4 pooler connections, but not with the IPv6 transaction pooler. * Updated the example connection options to use `jit=true` for temporary access setup. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
|
635b2d6050 |
docs: standardise next steps on overview pages with content listings (#47097)
## I have read the CONTRIBUTING.md file. YES ## What kind of change does this PR introduce? This PR helps standardise link sections which is useful for overview pages that frequently use similar sections such as "Next steps", "Get started", or "Examples". Six high-traffic overview pages are migrated as a pilot, with a skill in the new [supabase/docs-agent-skills](https://github.com/supabase/docs-agent-skills) repo to audit and convert the rest in a follow-on PR. Refactored from an initial YAML front matter approach per review feedback from @jeremenichelli. Now implemented as a React component and using existing linting & Markdown export functionality. A second round of review feedback further simplified the architecture: the per-listing component registry was removed in favor of a single `<ContentListings id="..." />` component backed by an ID-keyed data lookup, the listing data moved out of `apps/docs/components/` into `apps/docs/data/content-listings/`, the listing-specific link wrapper was replaced with the existing `<Link>` + `<GlassPanel>` pattern from the rest of the docs, and the headings now defer to the shared `<Heading>` from `MdxBase.shared.tsx` (no parallel marker-to-tag mapping, no typography overrides). Great feedback, thank you! 🙏 Relates to DOCS-1032. ## What is the current behavior? Authors implement these sections however they wish. As a result, overview and index pages use inconsistent patterns for orientation links: some use hand-rolled Markdown lists, some use custom panel/grid components, some use buttons, and some have no guidance about where to go next at all. There is no shared component for these sections and no analytics on those clicks. ## What is the new behavior? Authors add orientation sections in two steps: 1. Define listing data in a `.data.ts` file under `apps/docs/data/content-listings/` (for example, `storage.data.ts`). Each `ContentListingGroup` has a globally-unique `id` like `storage-get-started`. 2. Place a single `<ContentListings id="..." />` component inline in guide MDX. The ID is also the telemetry `listingId`, so the same value disambiguates the section in PostHog dashboards. Grid and list layouts, optional icons (such as `/docs/img/icons/github-icon` with `-light.svg` variants for dark mode), and external URLs are supported. Conditionals that use `$Show` around inline components are also supported, for example for auth pricing. ### Usage example from "Storage" overview page `apps/docs/data/content-listings/storage.data.ts`: ```ts export const storageGetStarted: ContentListingGroup = { id: 'storage-get-started', heading: 'Get started', description: 'Choose the bucket type that fits your use case:', type: 'grid', items: [ { title: 'Files buckets', href: '/guides/storage/quickstart', description: 'Store and serve images, videos, documents, and general-purpose files with direct URL access and row-level security.', }, { title: 'Analytics buckets', href: '/guides/storage/analytics/introduction', description: 'Store data in Apache Iceberg tables for data lakes, logs, and ETL. Query from Postgres via foreign tables with partitioning.', }, { title: 'Vector buckets', href: '/guides/storage/vector/introduction', description: 'Store embeddings and run similarity search for semantic matching, AI, and RAG. Use HNSW indexing, distance metrics, and metadata filtering.', }, ], } ``` `apps/docs/content/guides/storage.mdx`: ```mdx <ContentListings id="storage-get-started" /> ``` Renders as: <img width="689" alt="Storage Get started listing — Files, Analytics, and Vector buckets" src="https://github.com/user-attachments/assets/0d1b9531-962f-40ae-891e-b1e93ff1c939" /> <br>Exported in Markdown as: ```md ## Get started Choose the bucket type that fits your use case: - **[Files buckets](/docs/guides/storage/quickstart):** Store and serve images, videos, documents, and general-purpose files with direct URL access and row-level security. - **[Analytics buckets](/docs/guides/storage/analytics/introduction):** Store data in Apache Iceberg tables for data lakes, logs, and ETL. Query from Postgres via foreign tables with partitioning. - **[Vector buckets](/docs/guides/storage/vector/introduction):** Store embeddings and run similarity search for semantic matching, AI, and RAG. Use HNSW indexing, distance metrics, and metadata filtering. ``` Click tracking fires via PostHog (`docs_content_listing_clicked`): ```json { "action": "docs_content_listing_clicked", "custom_properties": { "targetPath": "/guides/storage/quickstart", "linkTitle": "Files buckets", "groupTitle": "Get started", "listingId": "storage-get-started" } } ``` Still finding my way around PostHog, but I verified on preview deploy that clicking a content listing on `/docs/guides/auth` sends `docs_content_listing_clicked` to `https://api.supabase.green/platform/telemetry/event` and receives HTTP 201. ### Authoring experience Three ways to add or convert content listings: copy the agent prompt first, use snippets for manual edits, or invoke the audit skill for batch follow-on work. Refer to `CONTRIBUTING.md` for the full authoring guide. #### 1. Agent prompt Copy into Cursor or another AI assistant: ```text Add a content listing block for [TOPIC] / [SECTION] (for example, Storage / Examples). Follow CONTRIBUTING § Content listings in apps/docs. - Add data to apps/docs/data/content-listings/[topic].data.ts - Use a globally-unique kebab-case id like `[topic]-[section]` - Place inline in the guide MDX with <ContentListings id="..." /> - Copy structure from storageGetStarted in apps/docs/data/content-listings/storage.data.ts - Run pnpm test:local lib/content-listings.test.ts from apps/docs ``` #### 2. VS Code / Cursor snippets Type these prefixes in the docs workspace (`.vscode/content-listing.code-snippets`): | Prefix | Inserts | | ----------- | -------------------------------------------------------- | | `cl-data` | `ContentListingGroup` export skeleton with namespaced id | | `cl-inline` | `<ContentListings id="…" />` in guide MDX | <img width="658" height="274" alt="image" src="https://github.com/user-attachments/assets/5ef20954-7aee-4925-887d-79a5ae766b37" /> #### 3. Batch audit skill For follow-on overview page conversion or maintenance, use the [`audit-content-listings`](https://github.com/supabase/docs-agent-skills/blob/main/.claude/skills/audit-content-listings/SKILL.md) skill in `docs-agent-skills` (skill, `conversion-manifest.json`, and validation script). Example: ```text Use audit-content-listings. Audit getting-started.mdx, update conversion-manifest.json, then convert the next unconverted section only. ``` ## Additional context The implementation includes a presentational `<ContentListings />` component (grid/list layouts, GlassPanel, telemetry) backed by ID-keyed data modules, and a single markdown export handler that reads the same `id` prop from the JSX and looks up data via the shared registry. Key files: - **Data:** `apps/docs/data/content-listings/` (one `.data.ts` file per guide topic, plus `index.ts` exporting `CONTENT_LISTINGS` and `getContentListingById`) - **Renderer:** `apps/docs/components/ContentListings/` (single `<ContentListings id="…" />` component); registered in `apps/docs/features/docs/MdxBase.shared.tsx` - **Types/helpers:** `apps/docs/lib/content-listings.schema.ts` (zod schemas, type aliases, grid/heading/href helpers) - **Markdown export:** `apps/docs/internals/markdown-schema/Listings.ts` (single ID-driven handler) wired into `apps/docs/internals/generate-guides-markdown.ts` - **Telemetry:** `docs_content_listing_clicked` defined in `packages/common/telemetry-constants.ts`, fired from `ContentListings.client.tsx` - **Authoring guide:** `apps/docs/CONTRIBUTING.md` (Components and elements → Content listings) - **VS Code snippets:** `.vscode/content-listing.code-snippets` (`cl-data`, `cl-inline`) ### Before & After #### Auth | [Before (production)](https://supabase.com/docs/guides/auth) | [After (preview)](https://docs-git-fork-nrichers-nikrichers-docs-1032-sta-e2a8cb-supabase.vercel.app/docs/guides/auth) | | --------------------------------------------------------------------------------------------------------------------------- | --------------------------------------------------------------------------------------------------------------------------- | | 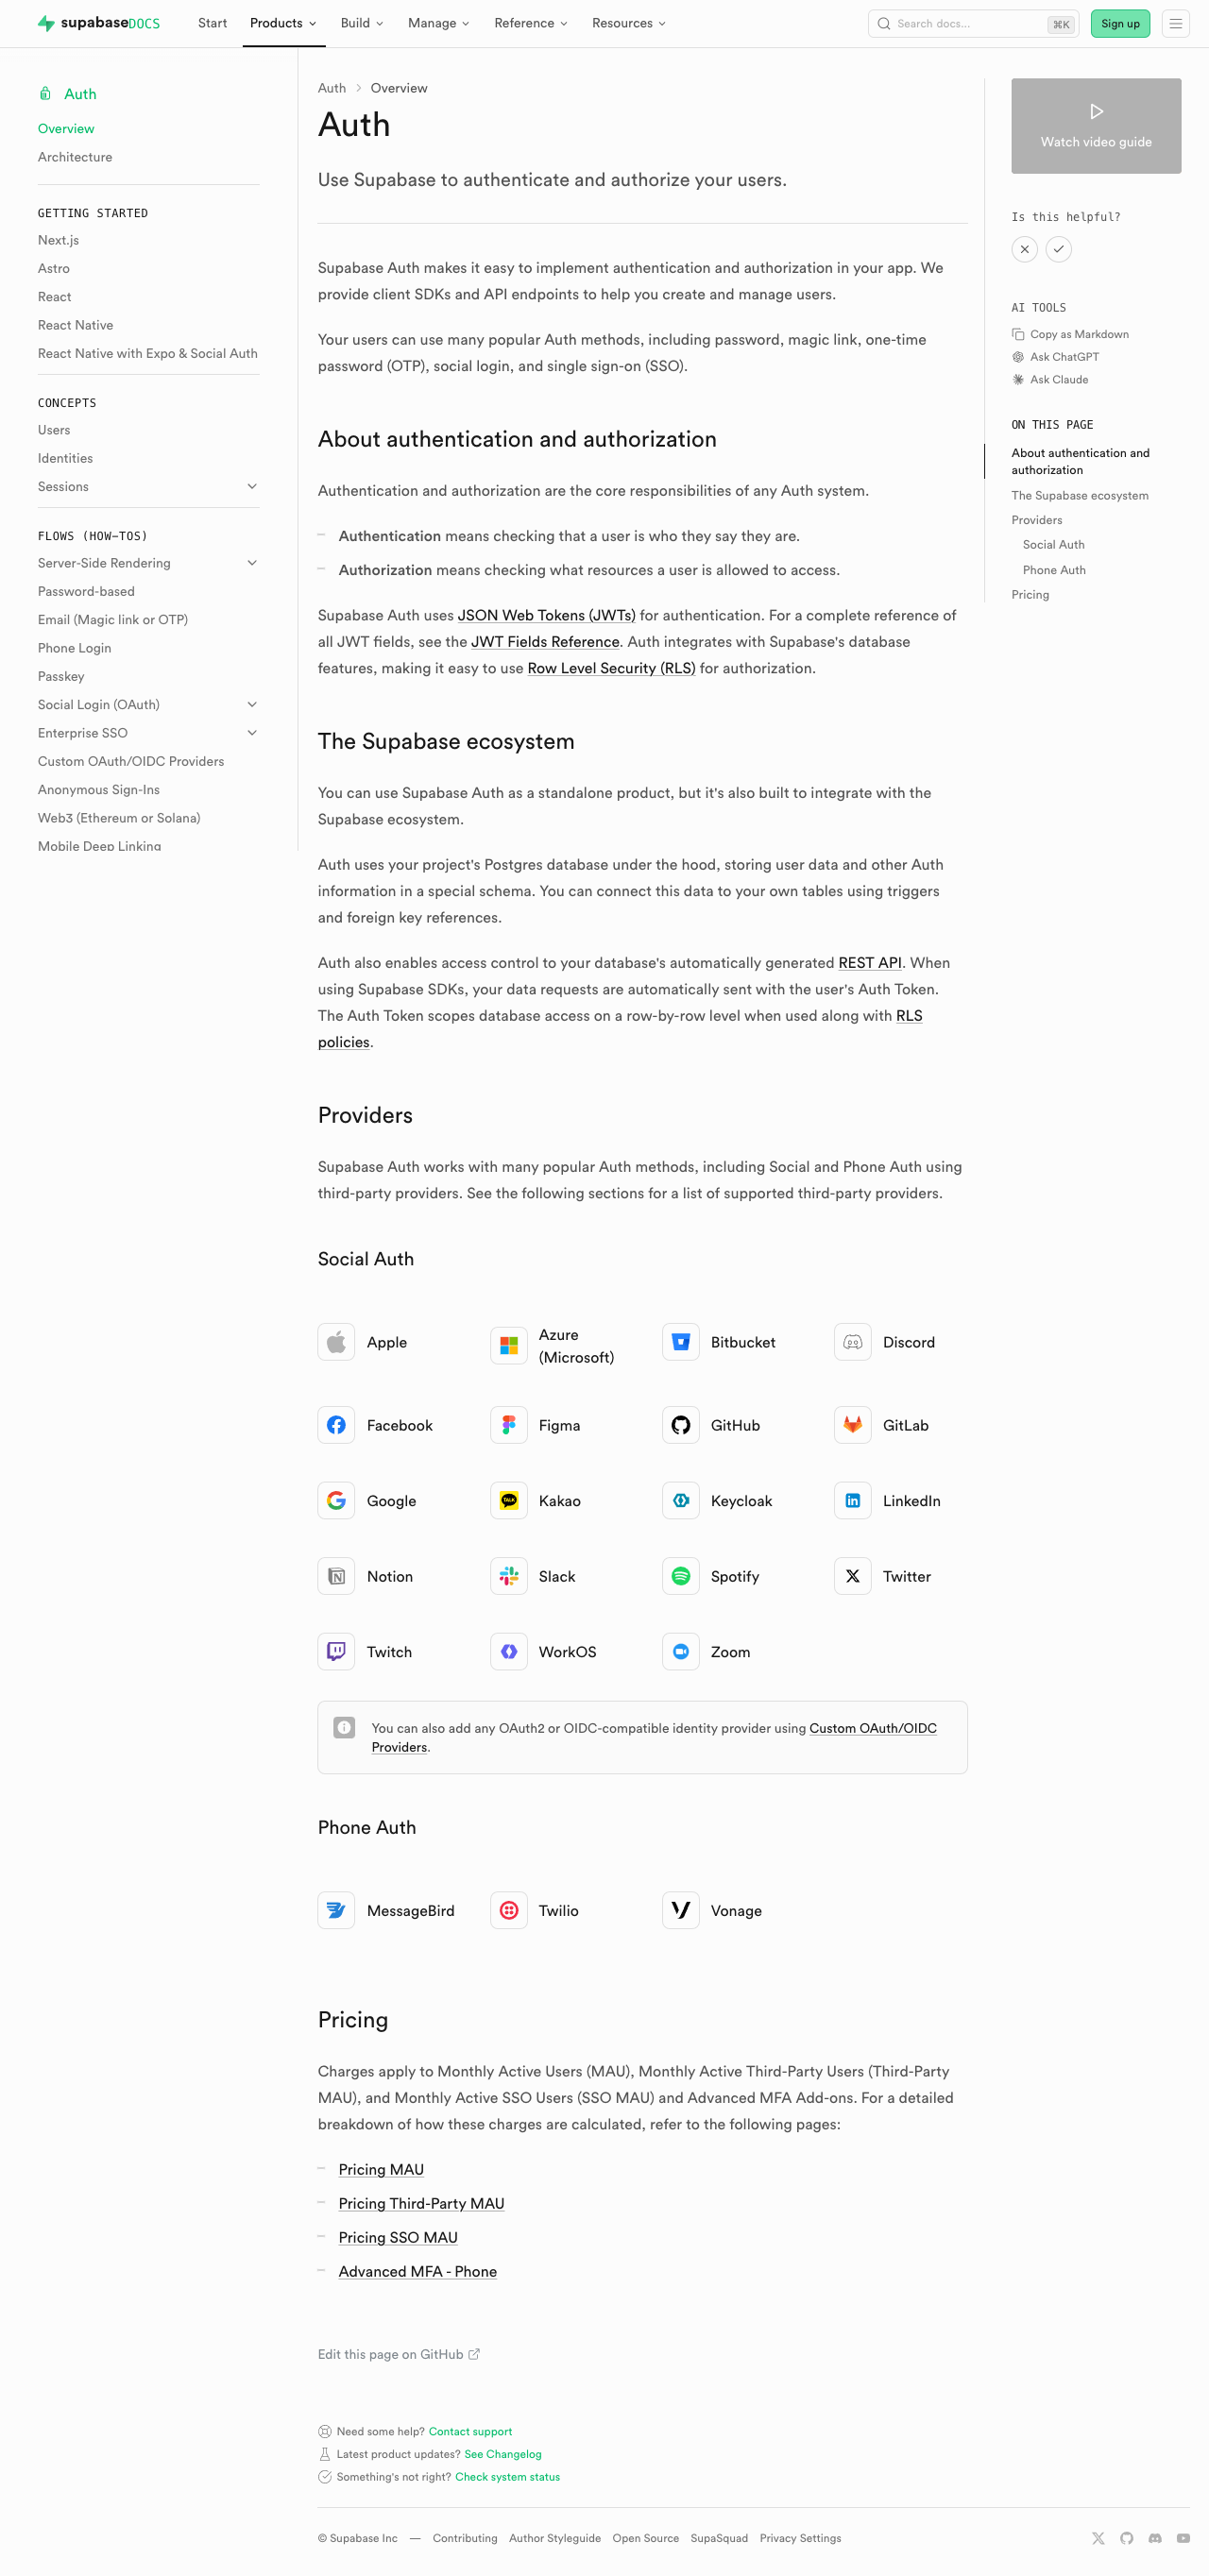 | 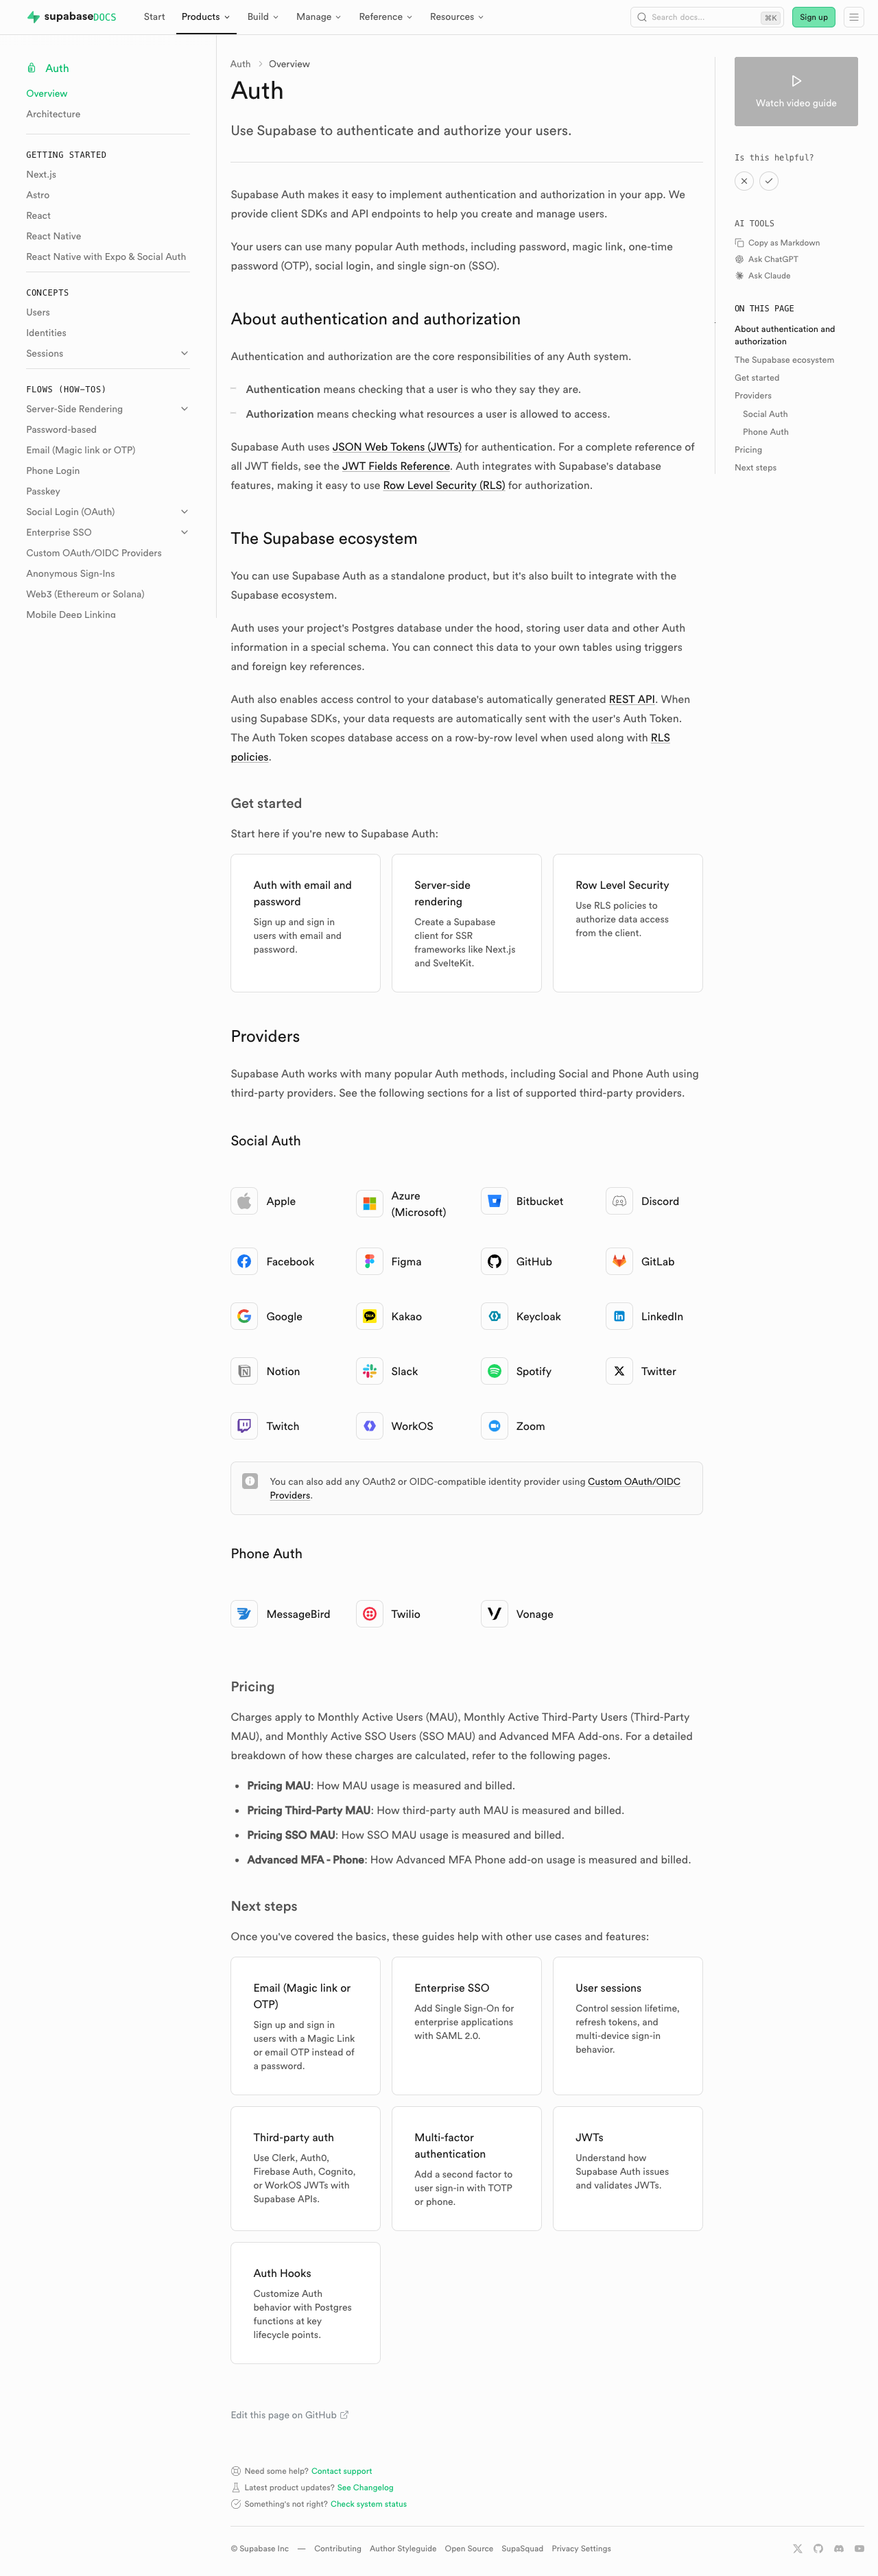 | #### Database overview | [Before (production)](https://supabase.com/docs/guides/database/overview) | [After (preview)](https://docs-git-fork-nrichers-nikrichers-docs-1032-sta-e2a8cb-supabase.vercel.app/docs/guides/database/overview) | | -------------------------------------------------------------------------------------------------------------------------------------------------- | -------------------------------------------------------------------------------------------------------------------------------------------------- | | 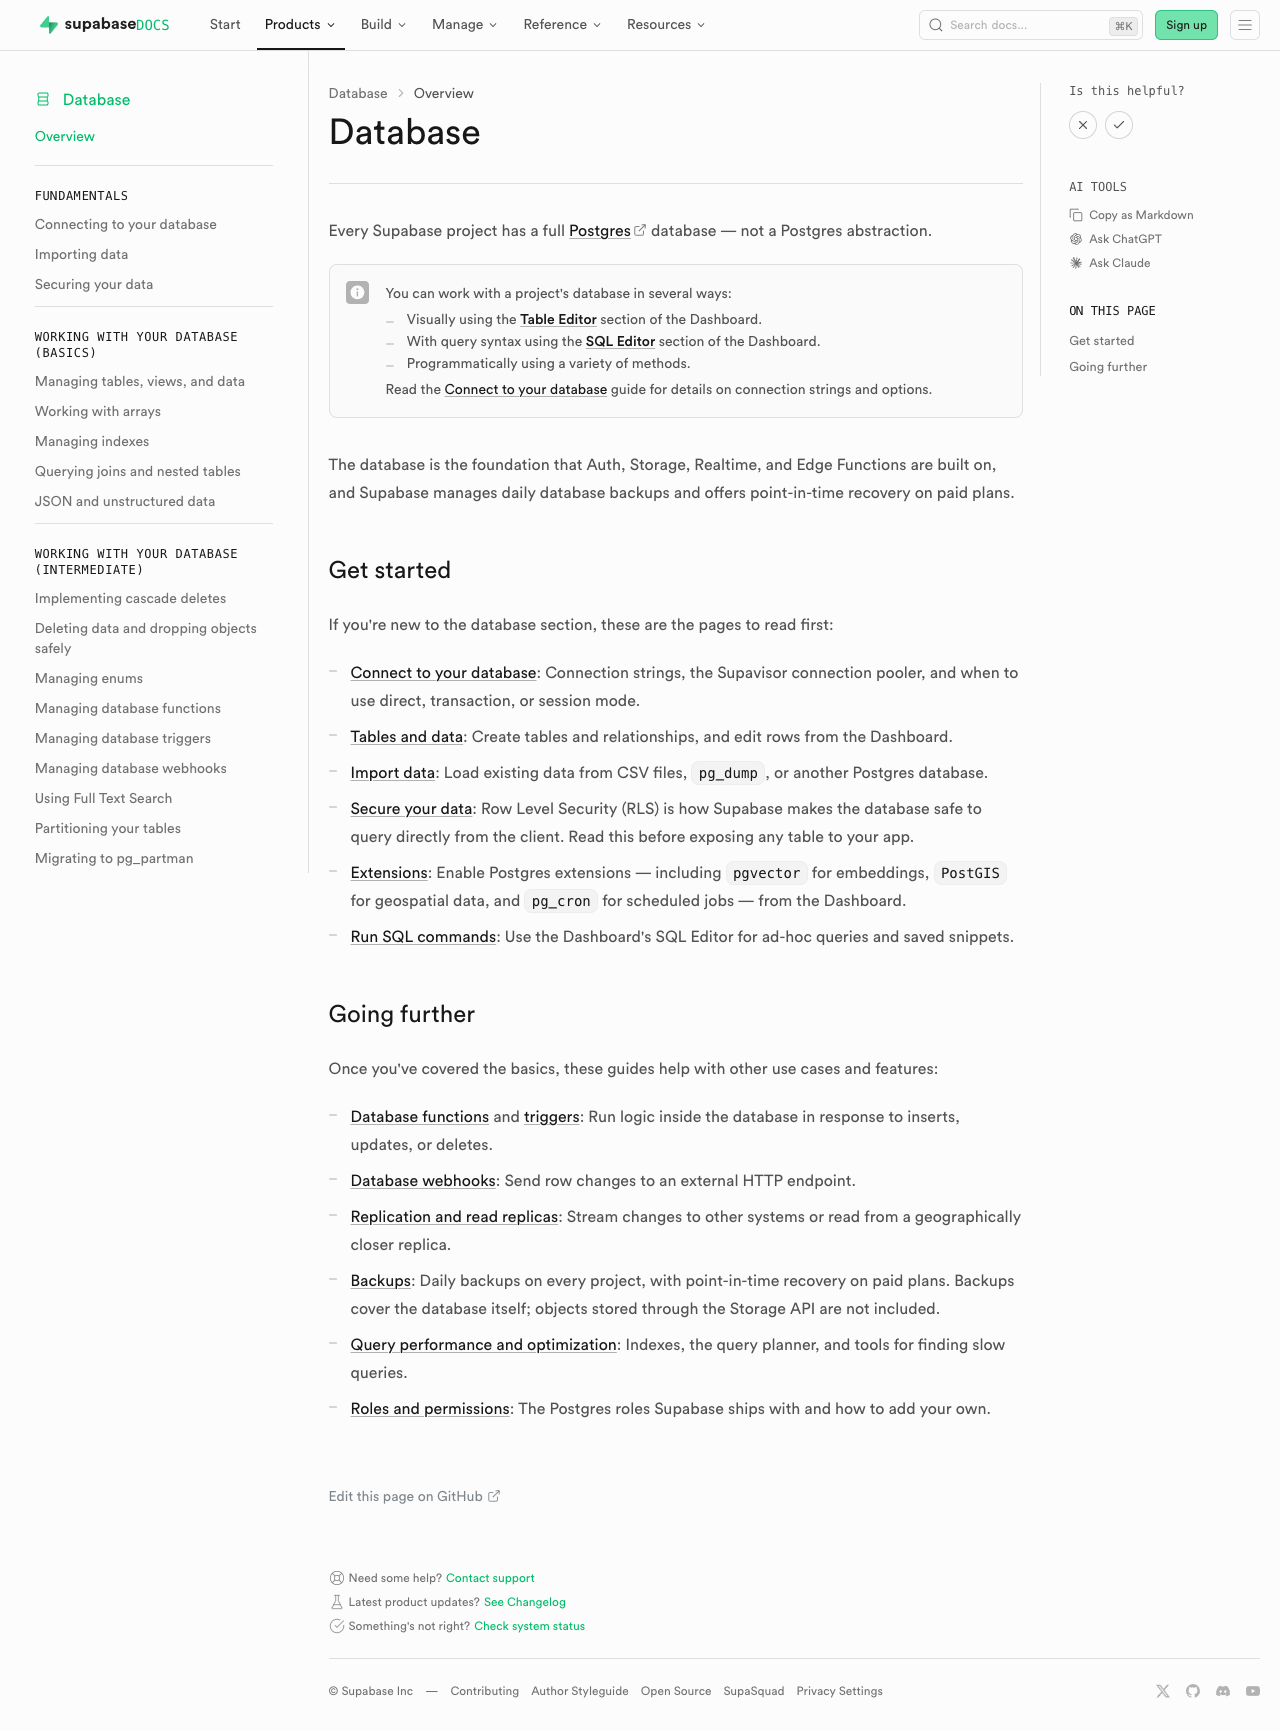 | 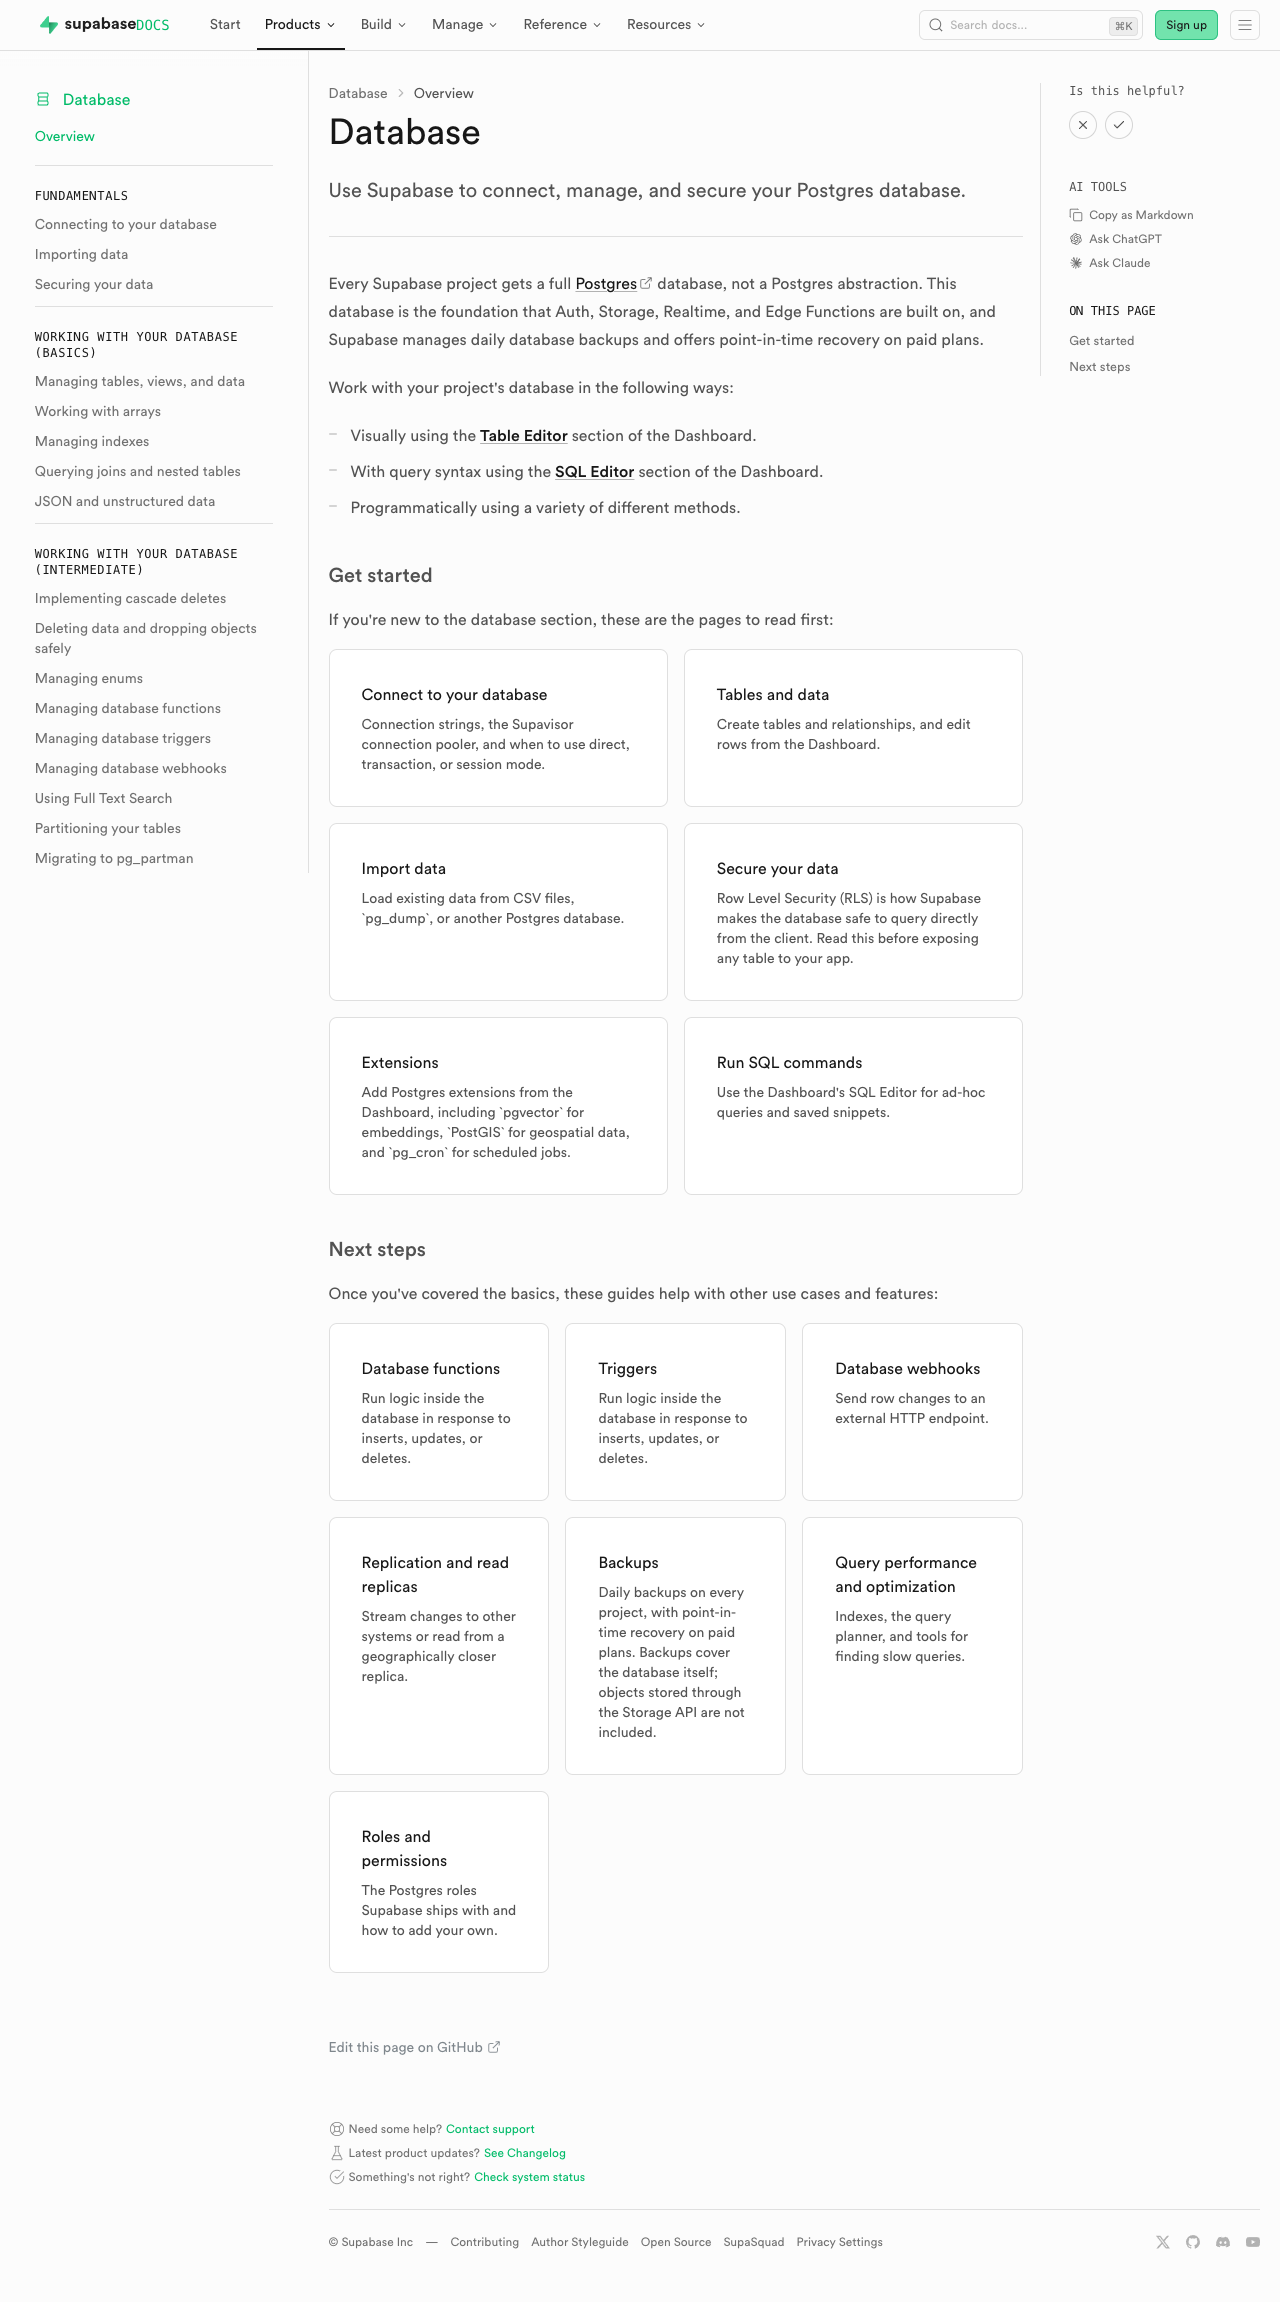 | #### Edge Functions | [Before (production)](https://supabase.com/docs/guides/functions) | [After (preview)](https://docs-git-fork-nrichers-nikrichers-docs-1032-sta-e2a8cb-supabase.vercel.app/docs/guides/functions) | | -------------------------------------------------------------------------------------------------------------------------------------------- | -------------------------------------------------------------------------------------------------------------------------------------------- | | 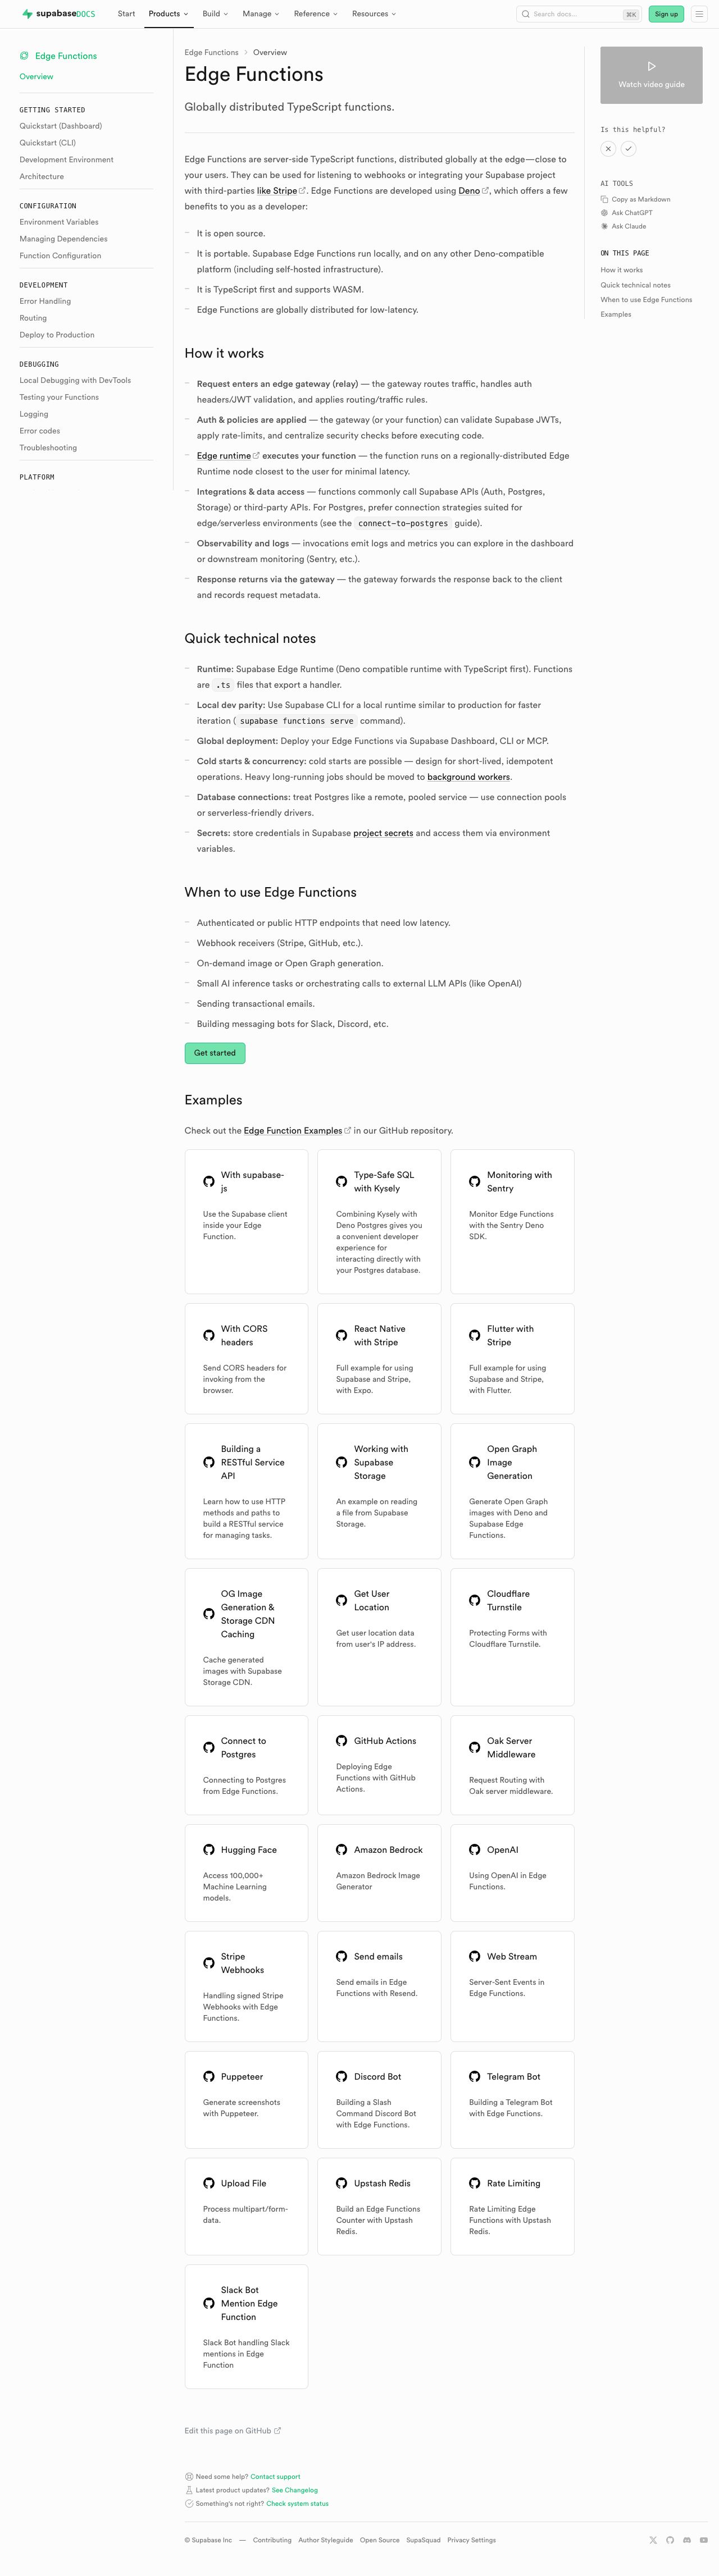 | 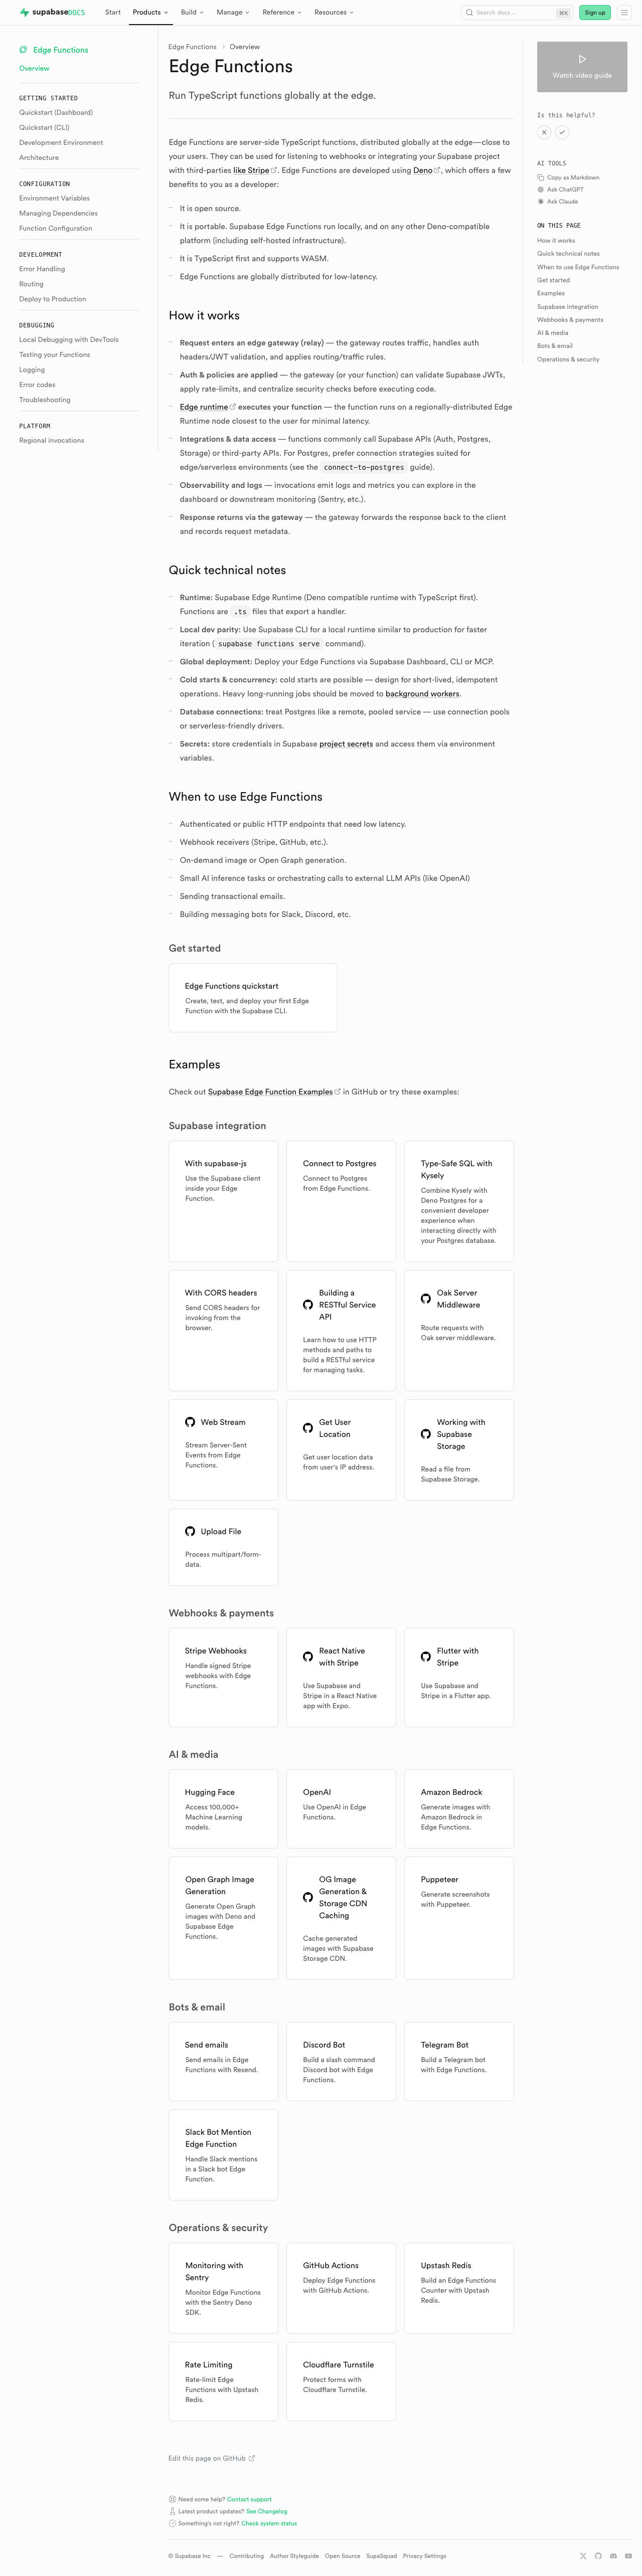 | #### Storage | [Before (production)](https://supabase.com/docs/guides/storage) | [After (preview)](https://docs-git-fork-nrichers-nikrichers-docs-1032-sta-e2a8cb-supabase.vercel.app/docs/guides/storage) | | ---------------------------------------------------------------------------------------------------------------------------------------- | ---------------------------------------------------------------------------------------------------------------------------------------- | | 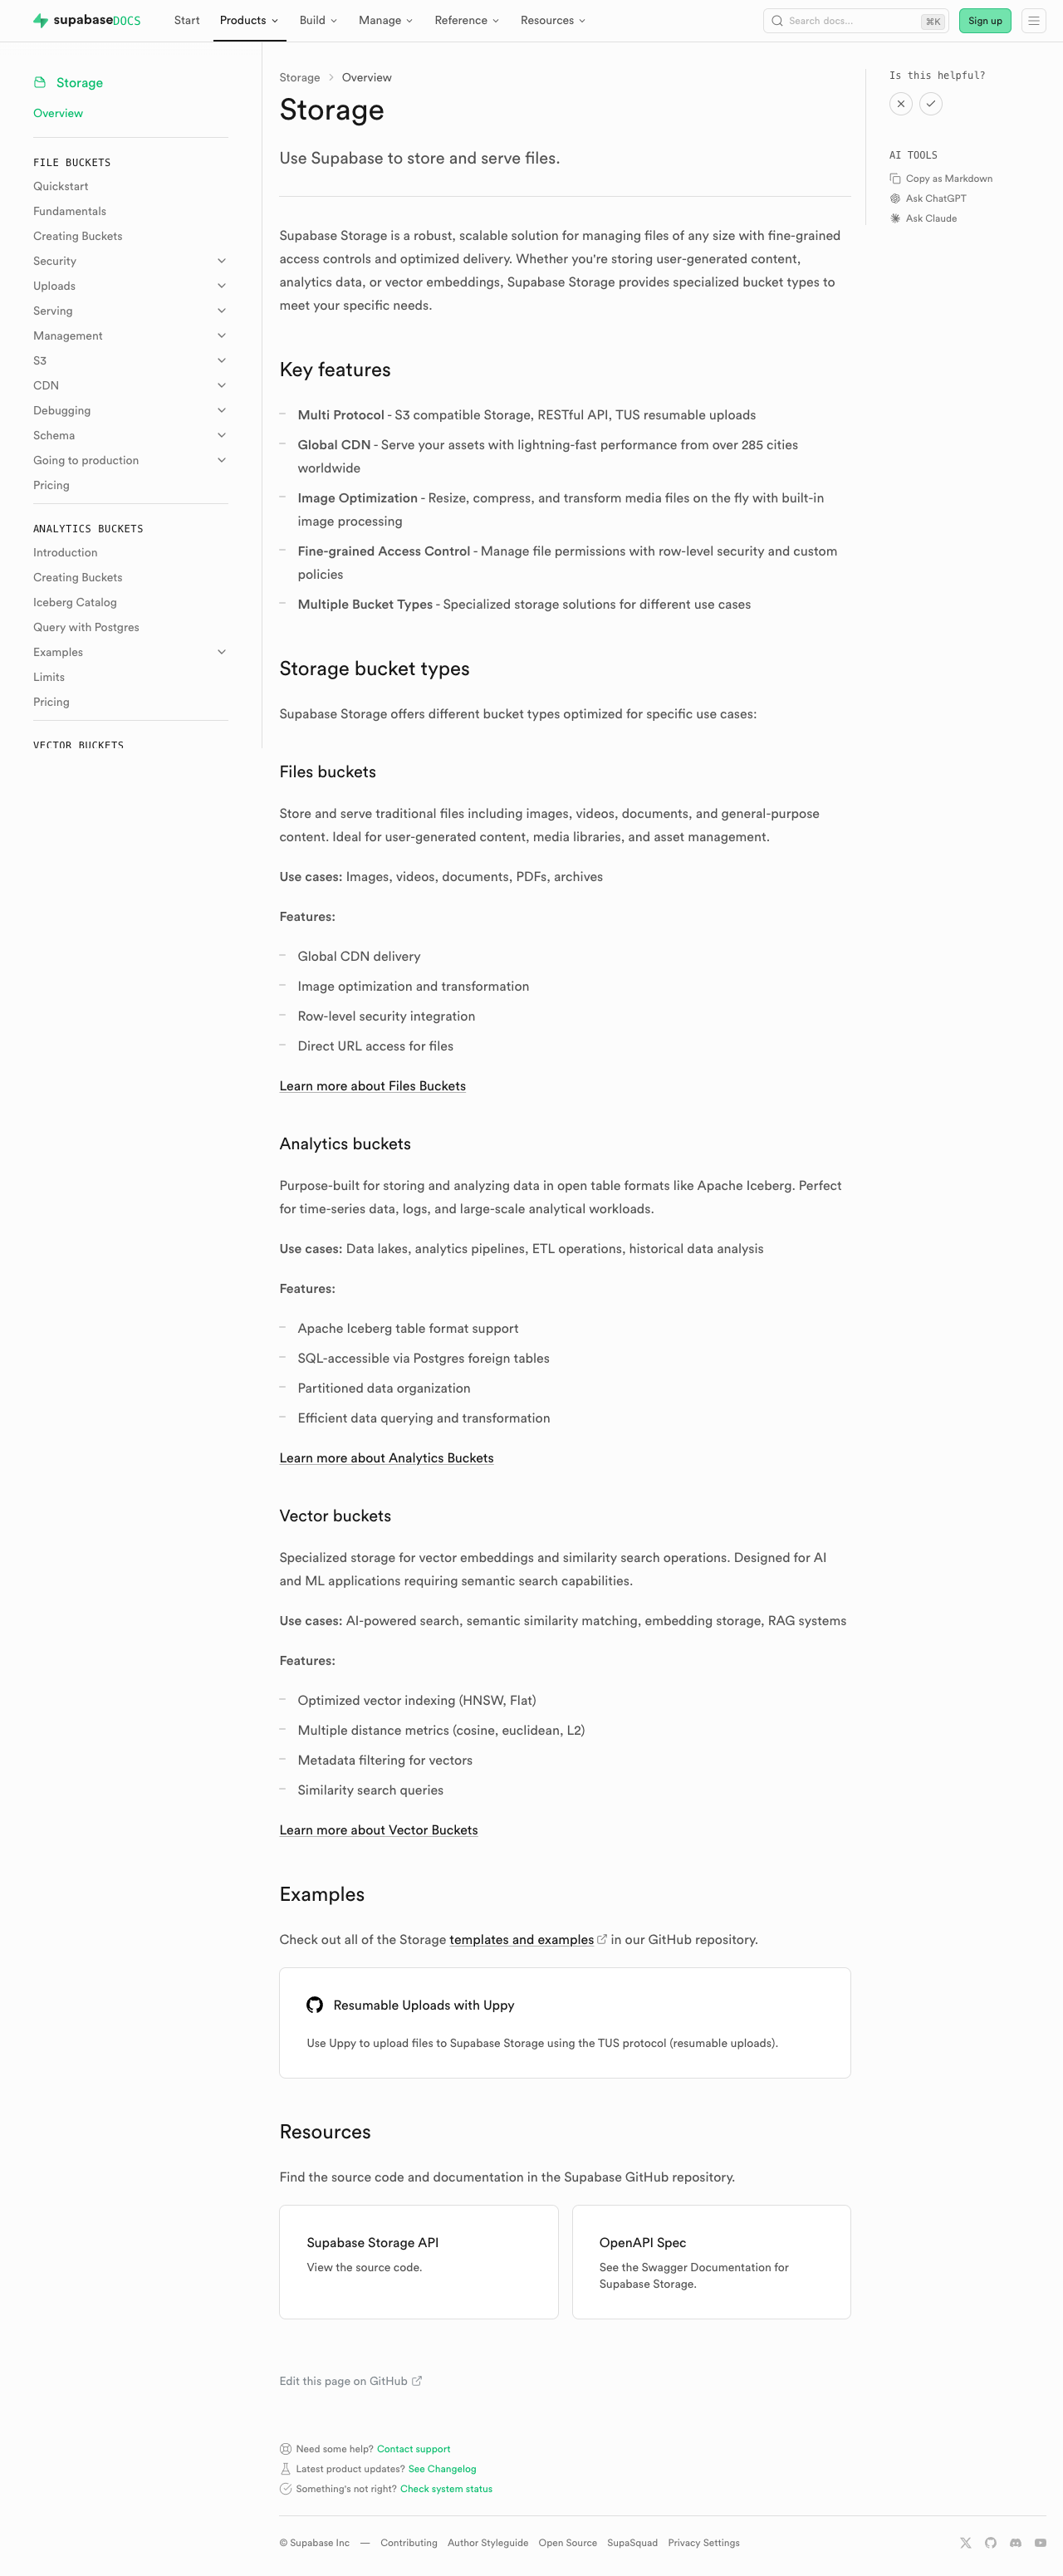 | 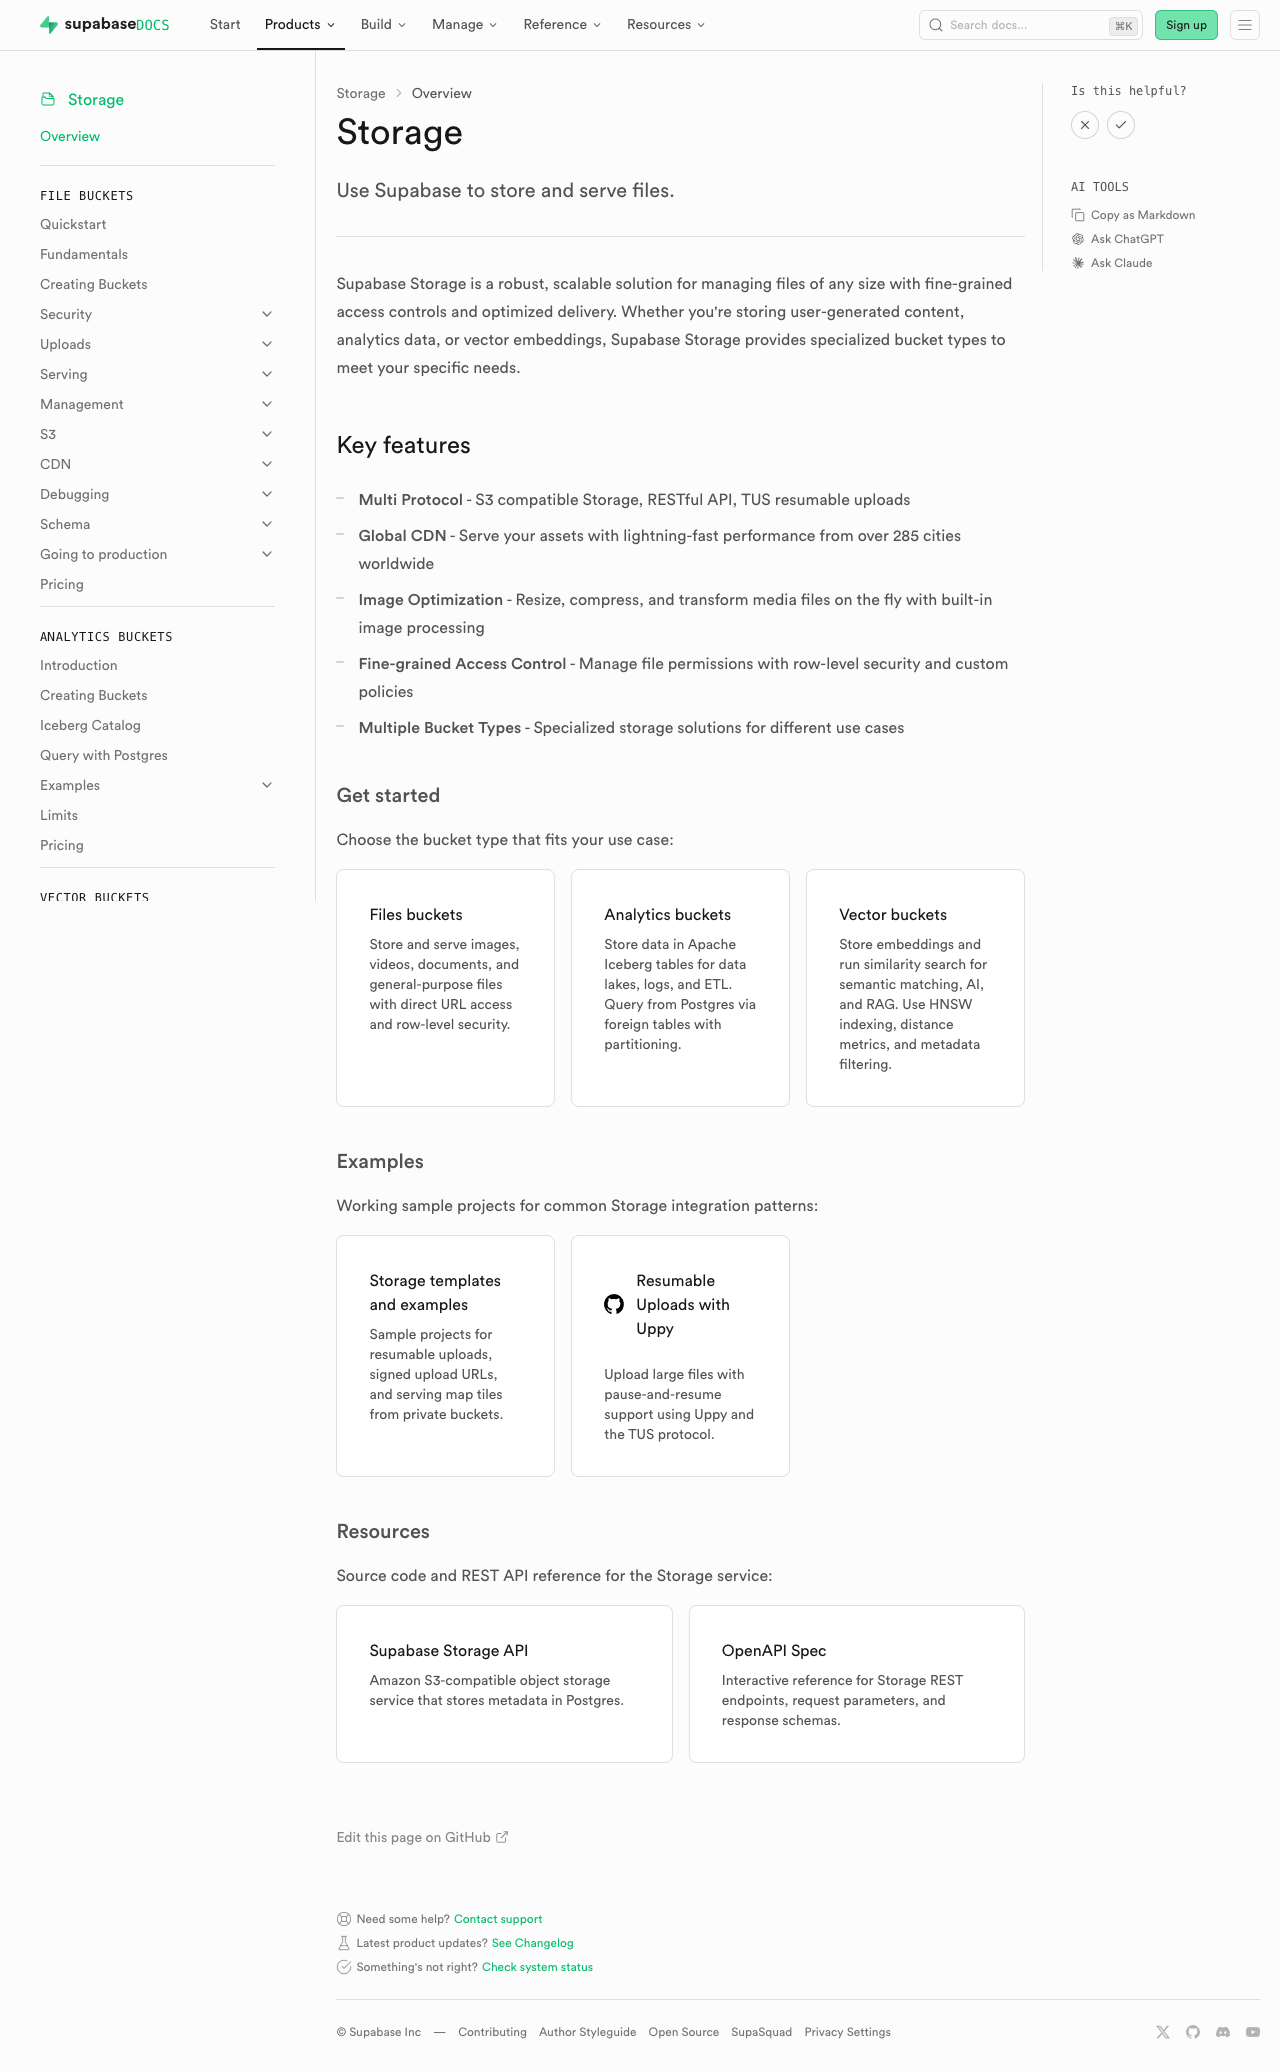 | #### Realtime | [Before (production)](https://supabase.com/docs/guides/realtime) | [After (preview)](https://docs-git-fork-nrichers-nikrichers-docs-1032-sta-e2a8cb-supabase.vercel.app/docs/guides/realtime) | | ------------------------------------------------------------------------------------------------------------------------------------------- | ------------------------------------------------------------------------------------------------------------------------------------------- | | 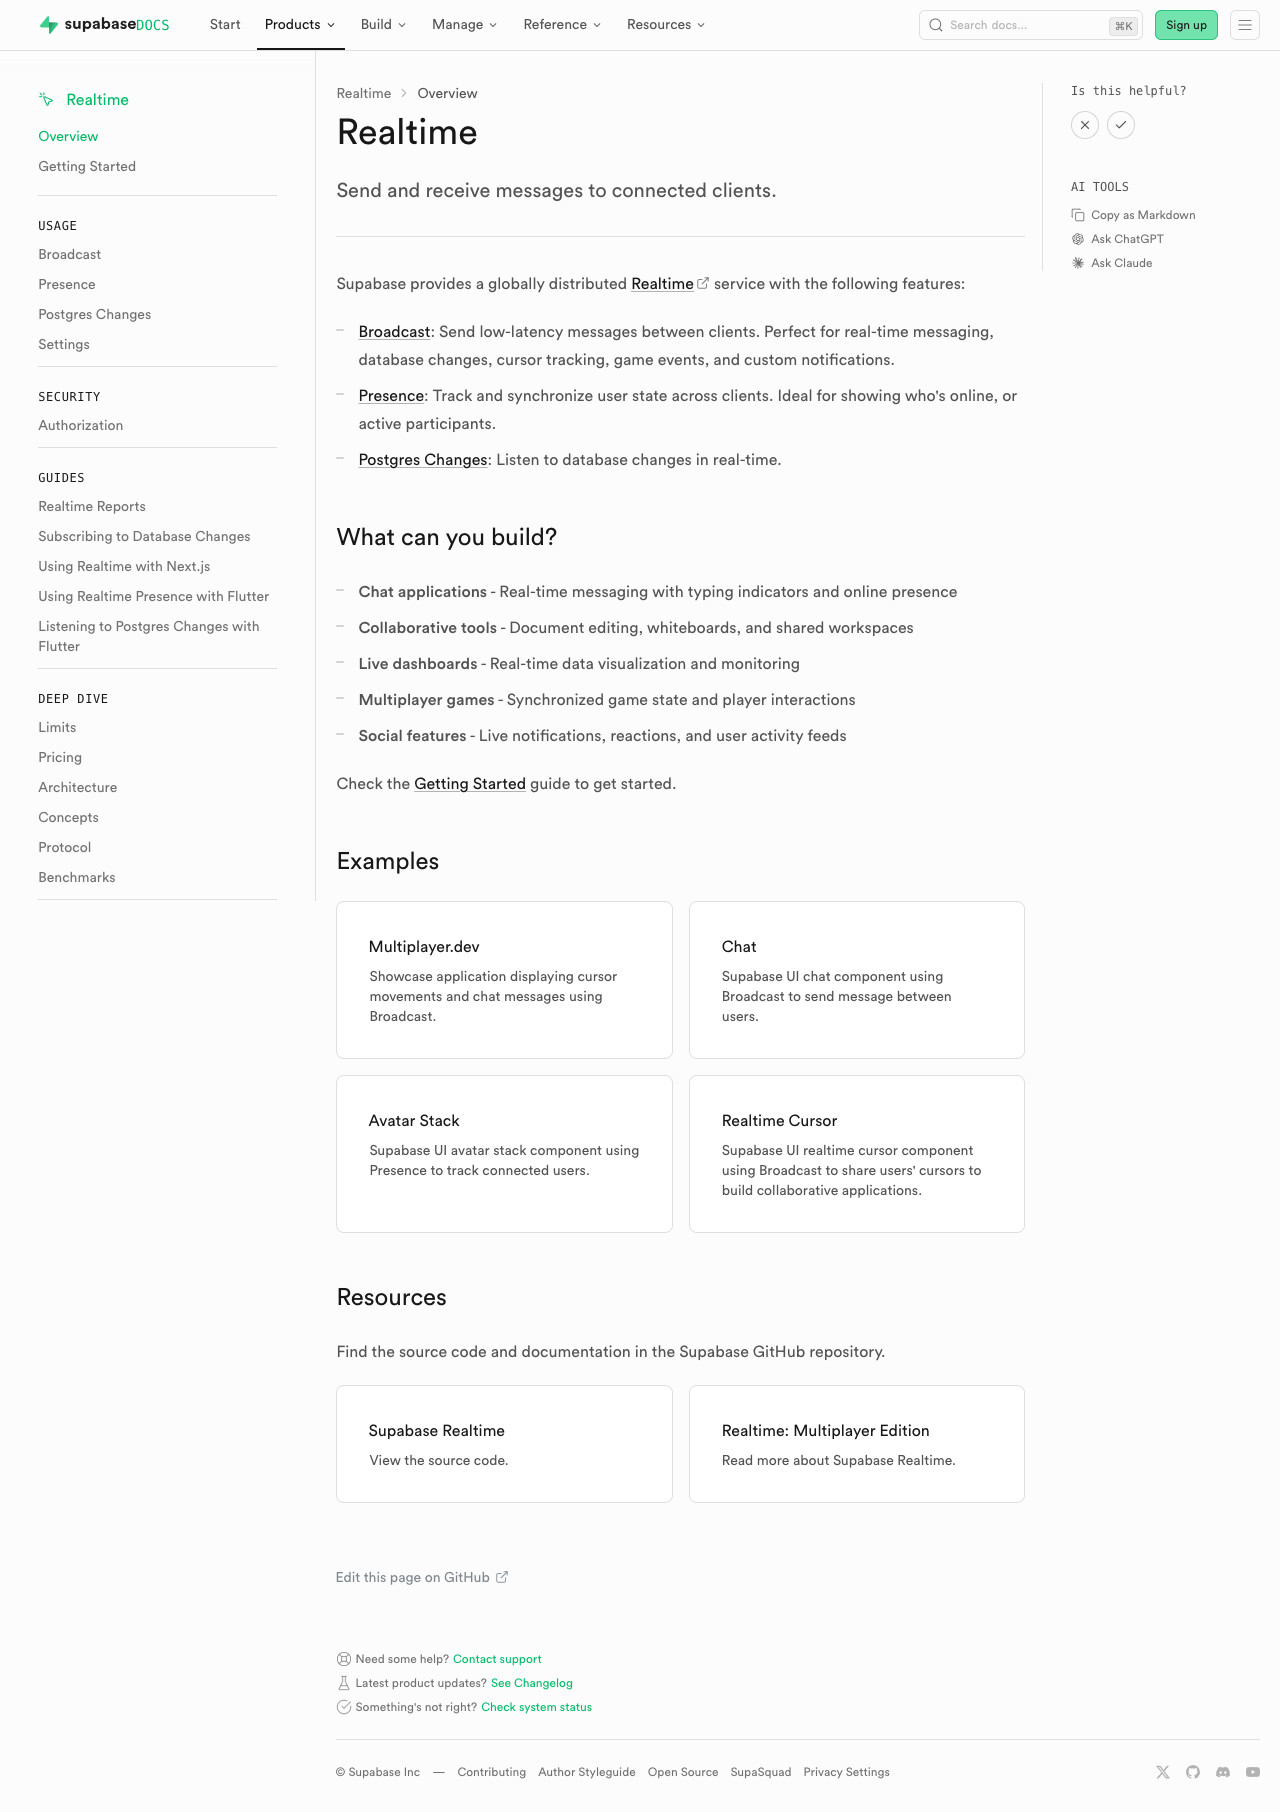 | 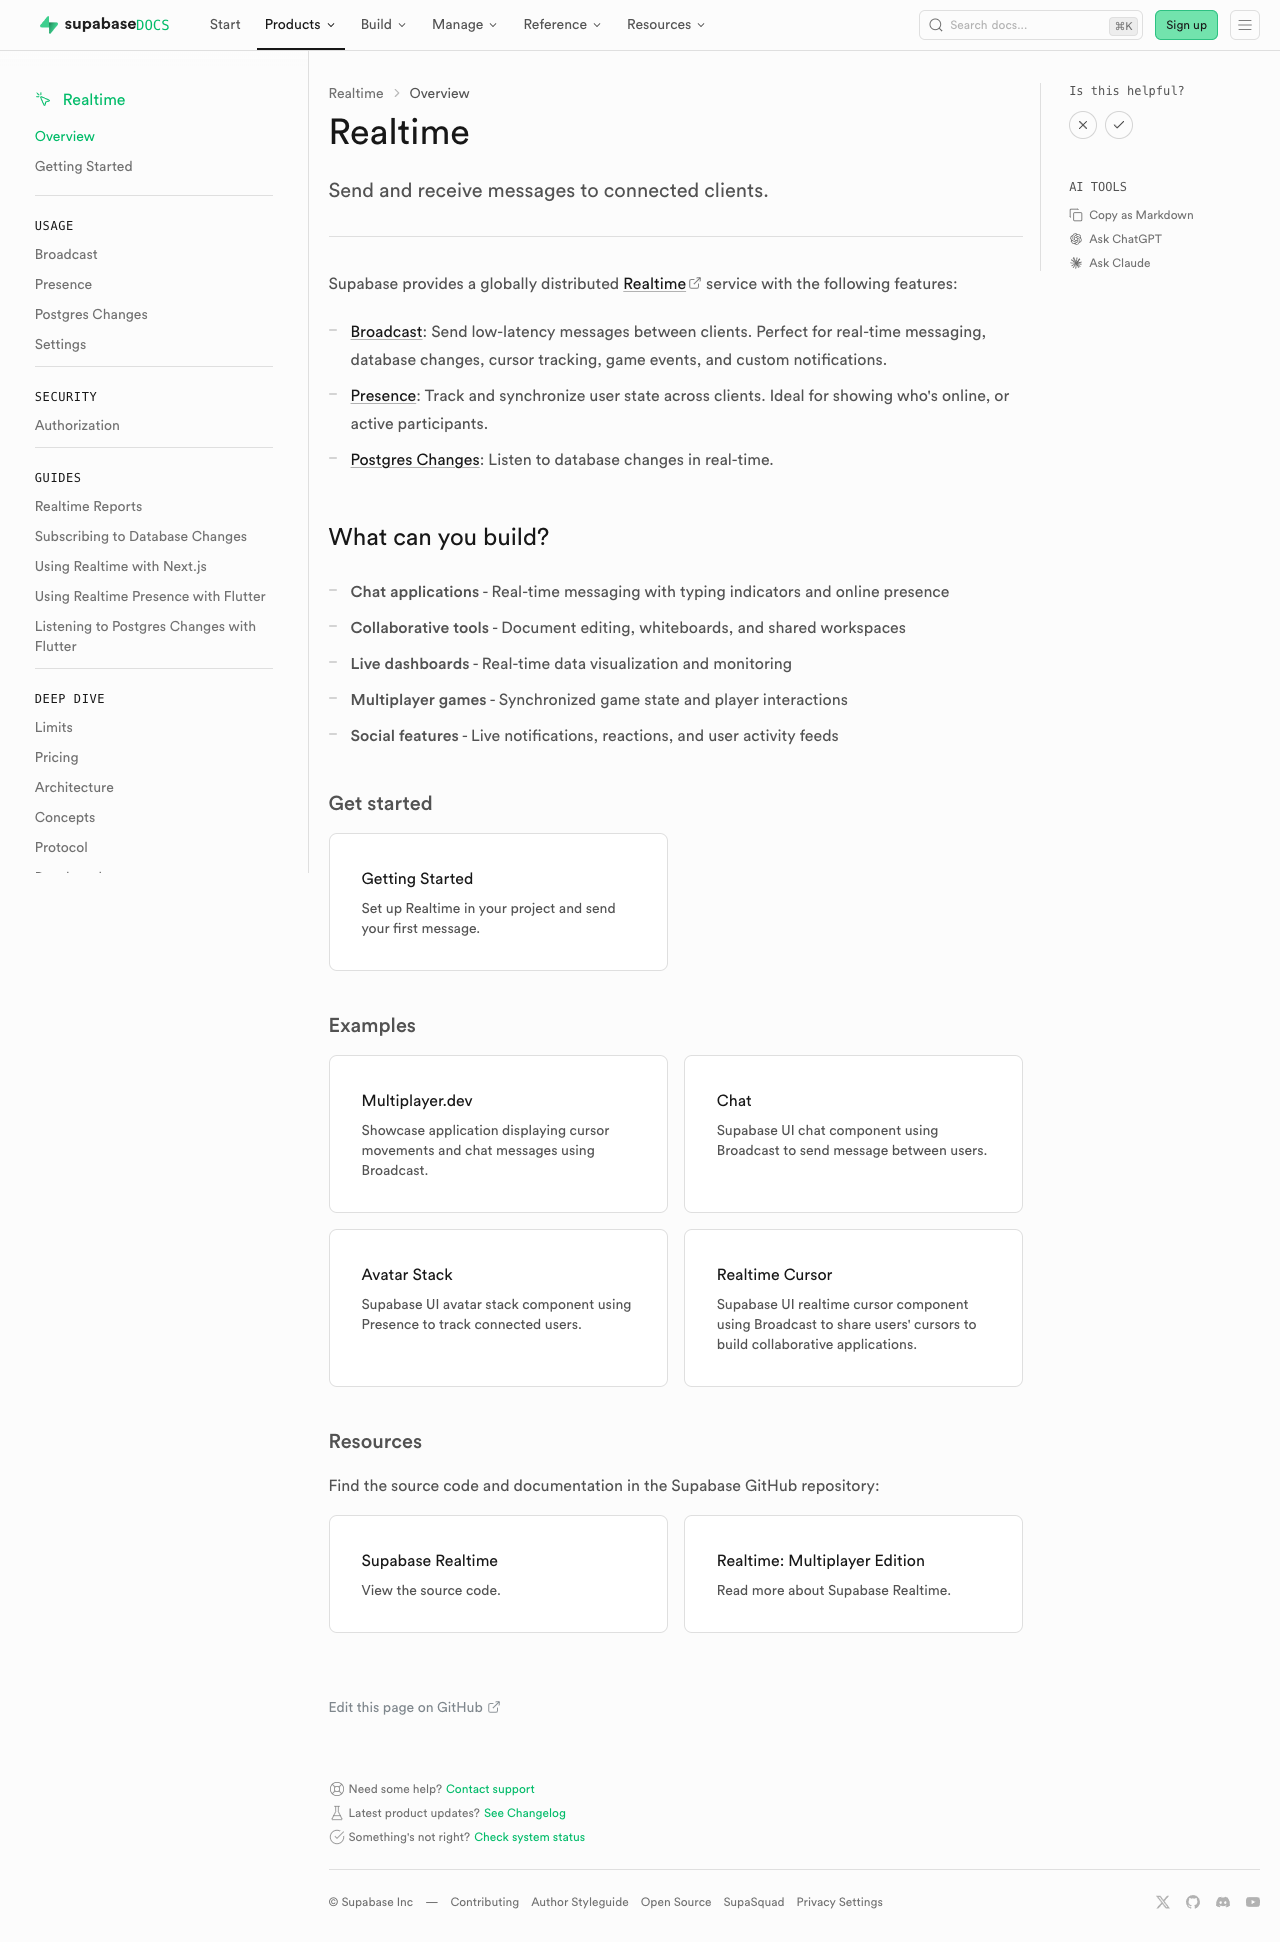 | #### Getting Started (partial migration for demoing) | [Before (production)](https://supabase.com/docs/guides/getting-started) | [After (preview)](https://docs-git-fork-nrichers-nikrichers-docs-1032-sta-e2a8cb-supabase.vercel.app/docs/guides/getting-started) | | ------------------------------------------------------------------------------------------------------------------------------------------------------ | ------------------------------------------------------------------------------------------------------------------------------------------------------ | | 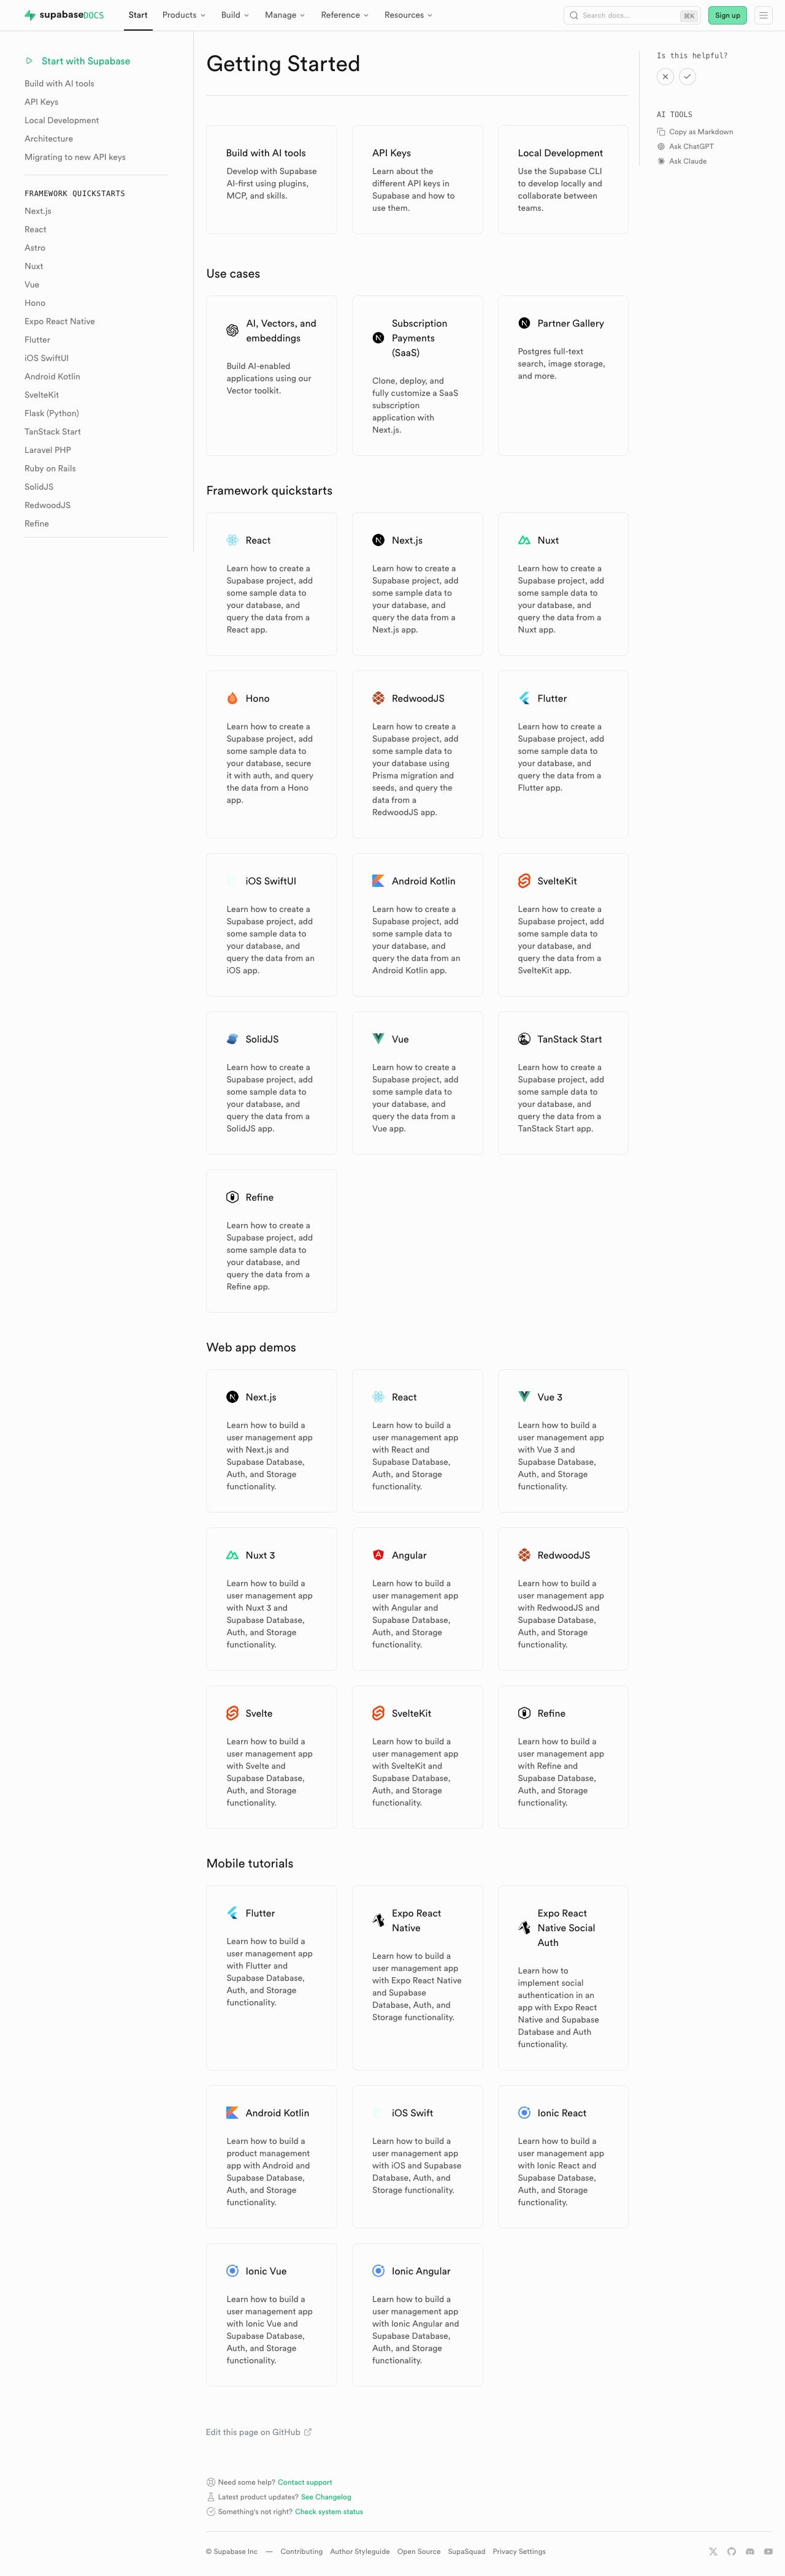 | 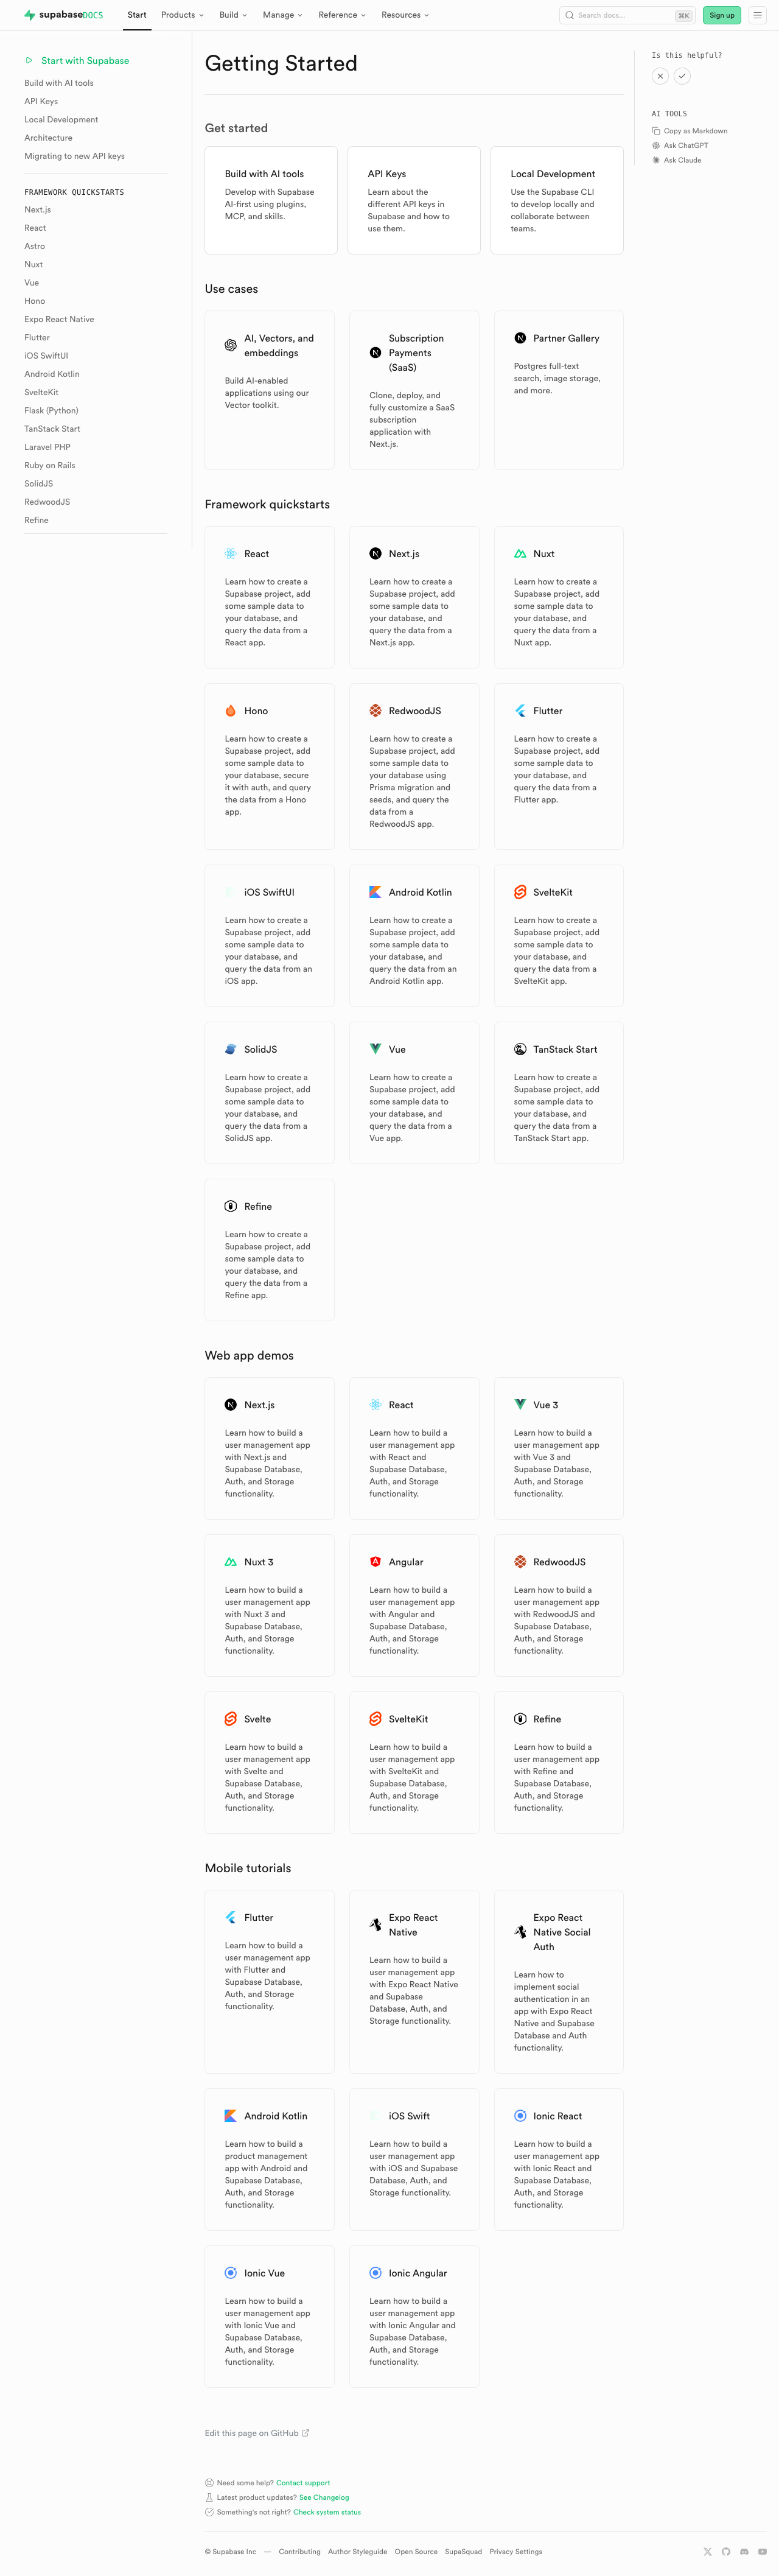 | ### Test plan - [ ] Visually verify migrated pages render correctly: - [ ] `/guides/auth` — grid "Get started", conditional pricing list, grid "Next steps" - [ ] `/guides/database/overview` — get started + next steps listings - [ ] `/guides/getting-started` — top 3-column grid - [ ] `/guides/functions` — get started + example listings - [ ] `/guides/storage` — get started, examples, resources listings - [ ] `/guides/realtime` — get started, examples, resources listings - [ ] Confirm listings render at explicit page positions - [ ] Click a content listing link and verify `docs_content_listing_clicked` fires in PostHog with expected properties (the new `listingId` is the namespaced kebab-case id, e.g. `storage-get-started`) - [ ] Build docs and confirm `.md` alternate output includes listing sections at component placement (e.g. `public/markdown/guides/storage.md`) - [ ] Run unit tests: `pnpm test:local lib/content-listings.test.ts` in `apps/docs` ## Summary by CodeRabbit ## Release Notes * **New Features** * Introduced a standardized content listings system for organizing related guides and resources. * Content listings now support both grid and list layouts for consistent presentation. * Added click telemetry for content listing interactions. * **Documentation** * Updated authentication, database, functions, getting started, realtime, and storage guide pages to use the new content listing components. * Improved MDX structure examples and listing markup formatting in contributor documentation. <!-- end of auto-generated comment: release notes by coderabbit.ai --> <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit ## Release Notes * **New Features** * Introduced a new content listings component for displaying guide content in list and grid layouts across documentation pages. * Added telemetry tracking for content listing interactions to measure user engagement. * **Documentation** * Updated guide pages (Authentication, Database, Functions, Storage, Realtime, Getting Started) to use the new listings layout. * Added contribution guidelines for creating and managing content listings in documentation. * **Tests** * Added comprehensive test coverage for content listings validation, serialization, and rendering. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Nik Richers <nik@validmind.ai> Co-authored-by: Jeremias Menichelli <jmenichelli@gmail.com> |
||
|
|
3dffdefd6e |
fix(docs) Resolve 196 mdx lint warnings for just, quickly, actually, PostgreSQL (#47358)
Closes DOCS-1057 Contributes to DOCS-1052 ## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## Problem We have hundreds of MDX lint warnings in our docs going against style best practices. ## Solution Remove and replace in context the following: - PostgreSQL. There was only one. There was concern about exceptions, but I found none. - Just - Quickly - Actually ### What changed Edits follow the [Google developer documentation style guide](https://developers.google.com/style): concise, direct, active voice. The flagged words were removed when the sentence still read well, or replaced when meaning needed to be preserved. ### Common patterns | Flagged word | Approach | Example | |---|---|---| | **just** (filler) | Removed | "you just installed" → "you installed" | | **just** (limiting) | **only** | "just one row" → "only one row" | | **just like** | **like** / **the same as** | "function just like regular users" → "function like regular users" | | **not just** | **not only** | "not just errors" → "not only errors" | | **quickly** (performance) | **efficiently** or removed | "find rows quickly" → "find rows efficiently" | | **quickly** (time) | **soon** / **rapidly** / removed | "expires too quickly" → "expires too soon" | | **actually** (filler) | Removed | "actually execute" → "execute"; "is actually the most common" → "is the most common" | ## Tophatting 1. See the diff. 2. See that content continues to make sense in context. 3. Locally, `cd apps/docs` and run `pnpm run lint:mdx`. 4. Search for "just," "actually," "quickly", and "PostgreSQL" and see there are 0 warnings. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Documentation** * Updated wording across quickstarts, guides, and troubleshooting articles for grammar, clarity, and consistent step-by-step phrasing. * Clarified key concepts including Row Level Security policy evaluation across Supabase products, deferred foreign key constraint behavior, and when `EXPLAIN ANALYZE` executes queries (and related side effects). * Refined several troubleshooting instructions and added guidance to cap log payload size to reduce billed Logs Ingest volume. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: github-actions[bot] <41898282+github-actions[bot]@users.noreply.github.com> Co-authored-by: Nik Richers <nrichers@gmail.com> Co-authored-by: Chris Chinchilla <chris.ward@supabase.io> |
||
|
Nik RichersandNik Richers
|
032a368221 |
fix(docs): overhaul Ionic Vue tutorial auth flow and example app (#47142)
## I have read the CONTRIBUTING.md file.
YES

## What kind of change does this PR introduce?
Bug fix, docs update

Closes DOCS-353.

## What is the current behavior?
- Linear item: Overhaul Ionic Vue tutorial
- Debug email shown on login page after submit
- Login redirect / route guard issues
- Email missing on account page
- HTML5 `type="url"` blocks profile update for `example.com`
- Tutorial `.env` used `VUE_APP_SUPABASE_KEY` but app expects
`VUE_APP_SUPABASE_PUBLISHABLE_KEY`

## What is the new behavior?
- Removed debug `<p>{{ email }}</p>` from Login.vue
- Route guards in `router/index.ts`; simplified App.vue user sync
- Account email from `getClaims()`; website `type="text"`;
`useIonRouter` for logout
- Store typed as `User | null`
- Tutorial MDX env var fixed
- Audit skills moved to
[supabase/docs-agent-skills](https://github.com/supabase/docs-agent-skills):
[`audit-ionic-vue-tutorial`](https://github.com/supabase/docs-agent-skills/blob/main/.claude/skills/audit-ionic-vue-tutorial/SKILL.md),
[`audit-docs-tutorials`](https://github.com/supabase/docs-agent-skills/blob/main/.claude/skills/audit-docs-tutorials/SKILL.md)
— both require **live Supabase platform** E2E (not just build/lint)

**Tutorial preview:** [Build a User Management App with Ionic
Vue](https://supabase.com/docs/guides/getting-started/tutorials/with-ionic-vue)


## Additional context
- Verification (author): `npm install && npm run build` — **pass**
(warnings only)
- E2E: profiles migration applied to project `moijyfpvgnmgoxvwcikq`; add
`.env` from `.env.example` with publishable key for full auth flow test

### Test plan
- [ ] `cd examples/user-management/ionic-vue-user-management && npm
install && npm run build`
- [ ] Confirm tutorial MDX `.env` uses
`VUE_APP_SUPABASE_PUBLISHABLE_KEY`
- [ ] Copy Project URL + publishable key into `.env`
- [ ] `npm run dev` — login page shows no email after magic-link submit
- [ ] Magic link redirects to `/account`
- [ ] Email displays on account page
- [ ] Update profile with `example.com` and `https://example.com` — both
save
- [ ] Logout returns to `/`; `/account` blocked without auth
- [ ] Install audit skills from
[docs-agent-skills](https://github.com/supabase/docs-agent-skills) (`ln
-sf
~/GitHub/supabase/docs-agent-skills/.claude/skills/audit-ionic-vue-tutorial
~/.claude/skills/audit-ionic-vue-tutorial` and same for
`audit-docs-tutorials`), then run
[audit-ionic-vue-tutorial](https://github.com/supabase/docs-agent-skills/blob/main/.claude/skills/audit-ionic-vue-tutorial/SKILL.md)
platform E2E (magic link, profile update verified via SQL)
- [ ] Run
[audit-docs-tutorials](https://github.com/supabase/docs-agent-skills/blob/main/.claude/skills/audit-docs-tutorials/SKILL.md)
— confirm platform E2E column is filled for with-ionic-vue


<!-- This is an auto-generated comment: release notes by coderabbit.ai
-->

## Summary by CodeRabbit

* **New Features**
* Improved authentication handling in the Ionic Vue user-management
example, with smoother sign-in/sign-out redirects and account access
checks.
  * Updated account details to display the user’s email more reliably.

* **Bug Fixes**
* Adjusted navigation so authenticated users are routed to the account
page and unauthenticated users are sent back to the home page.

* **Documentation**
* Updated setup instructions and example environment variables for the
Supabase integration.

<!-- end of auto-generated comment: release notes by coderabbit.ai -->

---------

Co-authored-by: Nik Richers <nik@validmind.ai>
|
||
|
Nik RichersandNik Richers
|
c7c6cca9ed |
chore(docs): align Next.js quickstart demo with monorepo catalog (#47144)
## I have read the CONTRIBUTING.md file. YES ## What kind of change does this PR introduce? Docs update, example maintenance Closes DOCS-362. ## What is the current behavior? - Linear item: Next JS checks (DOCS-362) - `@supabase/ssr: "latest"` and unpinned `next` in nextjs-user-management - Duplicate `next.config.js` + `next.config.ts` - Auth quickstart linked to non-existent `/guides/auth/server-side/nextjs` ## What is the new behavior? - Pinned `next@16.2.6`, `@supabase/ssr@0.10.2` per monorepo catalog - Removed duplicate `next.config.js` - Auth quickstart links to `creating-a-client?framework=nextjs` - Audit skills moved to [supabase/docs-agent-skills](https://github.com/supabase/docs-agent-skills): [`audit-nextjs-docs`](https://github.com/supabase/docs-agent-skills/blob/main/.claude/skills/audit-nextjs-docs/SKILL.md), [`audit-quickstarts`](https://github.com/supabase/docs-agent-skills/blob/main/.claude/skills/audit-quickstarts/SKILL.md) ## Additional context - Verification (author): `npm install && npm run build` in nextjs-user-management — **pass** (Next.js 16.2.6) - Skill audit: no stale `middleware.ts` in Next docs paths; broken link fixed; duplicate config removed | Check | Result | |-------|--------| | Version matrix | Pass (pinned to catalog) | | proxy.ts / no middleware refs | Pass | | nextjs-user-management build | Pass | | Auth quickstart link | Fixed | ### Test plan - [ ] `cd examples/user-management/nextjs-user-management && npm install && npm run build` - [ ] `cd apps/docs && pnpm codegen:examples && pnpm lint:mdx` on changed MDX - [ ] Framework quickstart — `create-next-app -e with-supabase` and publishable key env vars - [ ] Auth quickstart — "Learn more" resolves (no 404) - [ ] Web app tutorial — code samples use `proxy.ts` - [ ] Start nextjs-user-management locally with `.env.local` — login/account flow - [ ] Install audit skills from [docs-agent-skills](https://github.com/supabase/docs-agent-skills) (`ln -sf ~/GitHub/supabase/docs-agent-skills/.claude/skills/audit-nextjs-docs ~/.claude/skills/audit-nextjs-docs` and same for `audit-quickstarts`), then run checklists in [audit-nextjs-docs](https://github.com/supabase/docs-agent-skills/blob/main/.claude/skills/audit-nextjs-docs/SKILL.md) and [audit-quickstarts](https://github.com/supabase/docs-agent-skills/blob/main/.claude/skills/audit-quickstarts/SKILL.md) <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Documentation** * Updated resource links in authentication quickstart guides for improved navigation. * **Chores** * Updated dependencies in the Next.js user management example to latest stable versions. * Removed unused configuration settings from the example application. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Nik Richers <nik@validmind.ai> |
||
|
Andrew ValleteauandClaude
|
b12fe6ea1b |
docs: note cron.log_statement requires a database restart (#47313)
## What Documents that `cron.log_statement` is a Management-API-configurable Postgres parameter that **requires a database restart** to take effect. ## Why While aligning the platform's `RESTART_REQUIRED_KEYS` with `pg_settings.context` (supabase/platform#34691), `cron.log_statement` surfaced as a parameter that: - is accepted by the Management API `PUT /v1/projects/{ref}/config/database/postgres` endpoint (it's in the request schema), so project Owners/Admins can set it — though it's **not** exposed via the CLI; - is registered by pg_cron as `PGC_POSTMASTER` (context `postmaster`), so it only takes effect after a restart. It wasn't documented anywhere user-facing (it only appeared in the auto-generated OpenAPI spec). This adds a short note in the "Management API only parameters" section so the restart requirement is discoverable. 🤖 Generated with [Claude Code](https://claude.com/claude-code) --- _Generated by [Claude Code](https://claude.ai/code/session_01VaRQMeVMf4g5biiYPoZHLW)_ <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Documentation** * Updated the database configuration guide to include `cron.log_statement` in the list of Management API-only parameters. * Clarified that this setting requires a database restart before changes take effect. <!-- end of auto-generated comment: release notes by coderabbit.ai --> Co-authored-by: Claude <noreply@anthropic.com> |
||
|
Jonathan FultonandLukas Klingsbo
|
759dde2176 |
docs(auth): fix Dart signInWithOtp return type in email passwordless docs (#42339)
## What kind of change does this PR introduce? Bug fix for incorrect documentation. ## What is the current behavior? The Dart/Flutter examples in the email passwordless authentication documentation incorrectly show `signInWithOtp` returning an `AuthResponse`: ```dart final AuthResponse res = await supabase.auth.signInWithOtp(email: 'valid.email@supabase.io'); ``` However, according to the [official Flutter package documentation](https://pub.dev/documentation/supabase_flutter/latest/supabase_flutter/GoTrueClient/signInWithOtp.html), `signInWithOtp` returns `Future<void>`, not `AuthResponse`. ## What is the new behavior? Updated the Dart examples to correctly show that `signInWithOtp` returns `Future<void>`: ```dart await supabase.auth.signInWithOtp(email: 'valid.email@supabase.io'); ``` Also fixed a typo in the method name (`signinwithotp` -> `signInWithOtp`). ## Additional context - [Flutter Package Docs - signInWithOtp](https://pub.dev/documentation/supabase_flutter/latest/supabase_flutter/GoTrueClient/signInWithOtp.html) - shows return type is `Future<void>` - [Flutter Package Docs - verifyOTP](https://pub.dev/documentation/supabase_flutter/latest/supabase_flutter/GoTrueClient/verifyOTP.html) - this method returns `AuthResponse` Fixes #39447 <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Documentation** * Updated passwordless email authentication guide with corrected API method naming conventions in code examples. Examples now properly reference the current public API standards, ensuring developers follow best practices when implementing email-based authentication flows. <sub>✏️ Tip: You can customize this high-level summary in your review settings.</sub> <!-- end of auto-generated comment: release notes by coderabbit.ai --> Co-authored-by: Lukas Klingsbo <lukas.klingsbo@gmail.com> |
||
|
|
f2f346dfde |
feat(docs): add page documenting free project pausing behavior (#47279)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? Docs update ## What is the new behavior? Adds a page to Platform > Project & Account Management subsection to covers project pausing behavior for the Free plan. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added a new “Project Pausing” guide link under **Platform → Project & Account Management**. * Published a new guide explaining Free Plan automatic project pausing, the 7-day inactivity determination, the warning/confirmation email flow, how to prevent pausing via activity, restoration within 90 days, and how to avoid future pauses by upgrading. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Chris Chinchilla <chris.ward@supabase.io> Co-authored-by: Chris Chinchilla <chris@chrischinchilla.com> |
||
|
Chris ChinchillaandMiranda Limonczenko
|
3c26fd071b |
docs: Improve readability of page elements by LLM and AI tools (#47275)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Documentation** * Improved AI, database, storage, and platform guides with clearer explanations and more detailed workflow steps. * Added descriptive captions and accessible alt text for multiple diagrams and benchmark charts. * Expanded MFA, connection, replication, partitioning, and integration docs with clearer decision points and setup/login flow guidance. * Clarified database schema and seed-data examples to better explain how tables and relationships fit together. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Miranda Limonczenko <miranda.limonczenko@supabase.io> |
||
|
Leandro Pereira
|
32764ec483 |
docs(realtime): broadcast replay retention limits - REAL-874 (#47270)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? Docs to expose current Realtime Broadcast Replay limits. -- Fixes REAL-874 <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Documentation** * Clarified how broadcast replay storage retention works, including the daily-partition behavior and that replays are dropped after 72 hours (messages are available for at least 72 hours and up to ~4 days depending on send time). * Updated the “Limits by plan” table with broadcast replay retention (72 hours) and broadcast replay messages per request (25) across all plans. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
|
32d1bdd534 |
fix(studio): reduce doc link density in auth email template builder (#47250)
## I have read the CONTRIBUTING.md file. YES ## What kind of change does this PR introduce? - Studio UI update (auth email template builder) - Docs update (hosted email templates guide + local dev cross-link) Closes DOCS-1086. ## What is the current behavior? - Linear item: Reduce link density in the template builder UI - Page header shows a **Terminology** link and **Docs** button (local development guide) - Template variables footer shows **Terminology** · **Local development** - Local development editing is only mentioned in one sentence on the hosted docs page; easy to miss once Studio no longer links there directly ## What is the new behavior? - Page header: **Docs** button only → `/guides/auth/auth-email-templates` - Template variables: single **Terminology** link → `#terminology` (variable pills still have hover tooltips) - Hosted docs: **Editing email templates** split into hosted vs local/self-hosted, with a callout linking to the local development guide - Local dev guide: opening paragraph links back to the hosted guide for shared terminology and patterns ### Proof: Template builder has fewer outbound doc links | Before | After | |--------|-------| | Header Terminology + Docs (local dev guide); footer Terminology · Local development <img width="1440" height="1100" alt="image" src="https://github.com/user-attachments/assets/3325f43b-5830-4b85-ba56-2ba4c5b04bcd" /> | Docs button only (hosted guide); single Terminology link above variables <img width="1440" height="1100" alt="image" src="https://github.com/user-attachments/assets/90c8cfff-89bd-46d5-b336-2f9dd50d37e3" /> | **Before (`origin/master`)** - Header: **Terminology** link + **Docs** button → local development guide - Template variables: **Terminology** · **Local development** **After (this PR)** - Header: **Docs** button only → [Email templates](https://docs-git-nikrichers-docs-1086-reduce-link-densi-bf6705-supabase.vercel.app/docs/guides/auth/auth-email-templates) (preview) - Template variables: single **Terminology** link → [Terminology](https://supabase.com/docs/guides/auth/auth-email-templates#terminology) - Local development path documented at [Editing email templates](https://docs-git-nikrichers-docs-1086-reduce-link-densi-bf6705-supabase.vercel.app/docs/guides/auth/auth-email-templates#editing-email-templates) (preview; replacing the in-builder Local development link) **Capture notes:** Content-area screenshots were captured locally from component markup because the template editor body requires platform auth config in self-hosted Studio. Local files: worktree `.pr-screenshots/template-builder-links-{before,after}.png`. ### Proof: Docs clarify local development path **Verified:** Vercel docs preview (pass) · `supa-mdx-lint` (pass) | Page | Before (production) | After (PR preview) | |------|---------------------|--------------------| | Email templates — Editing | [Editing email templates](https://supabase.com/docs/guides/auth/auth-email-templates#editing-email-templates) | [Editing email templates](https://docs-git-nikrichers-docs-1086-reduce-link-densi-bf6705-supabase.vercel.app/docs/guides/auth/auth-email-templates#editing-email-templates) | | Customizing email templates | [Customizing email templates](https://supabase.com/docs/guides/local-development/customizing-email-templates) | [Customizing email templates](https://docs-git-nikrichers-docs-1086-reduce-link-densi-bf6705-supabase.vercel.app/docs/guides/local-development/customizing-email-templates) | ## Additional context ### Test plan - [ ] Open **Authentication → Emails → Confirm sign up** on a hosted project - [ ] Confirm header has **Docs** only (no Terminology link) - [ ] Confirm **Docs** opens `/docs/guides/auth/auth-email-templates` - [ ] In source view, confirm template variables show one **Terminology** link (no Local development) - [ ] Hover variable pills — tooltips still explain each placeholder - [ ] Compare [production Editing email templates](https://supabase.com/docs/guides/auth/auth-email-templates#editing-email-templates) vs [preview](https://docs-git-nikrichers-docs-1086-reduce-link-densi-bf6705-supabase.vercel.app/docs/guides/auth/auth-email-templates#editing-email-templates) — hosted vs local/self-hosted sections and local dev callout are clear - [ ] Compare [production Customizing email templates](https://supabase.com/docs/guides/local-development/customizing-email-templates) vs [preview](https://docs-git-nikrichers-docs-1086-reduce-link-densi-bf6705-supabase.vercel.app/docs/guides/local-development/customizing-email-templates) — intro links back to hosted email templates guide <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit ## Summary by CodeRabbit * **Documentation** * Clarified how to edit authentication email templates for hosted vs. self-hosted and local development setups. * Added clearer navigation to template terminology and customization guidance, with updated examples and notes. * **New Features** * Updated the email template UI to use centralized documentation links for the terminology section. * **Tests** * Added coverage to ensure the “Terminology” docs anchor stays consistent. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Nik Richers <nik@validmind.ai> Co-authored-by: Danny White <3104761+dnywh@users.noreply.github.com> Co-authored-by: Cursor <cursoragent@cursor.com> |
||
|
Riccardo Busetti
|
df7a0ca3f7 | feat(replication): Evaluate new product name (#47066) | ||
|
Wen Bo Xie
|
30cdd18db5 | fix: add migrations endpoint duration is 5 minutes (#43350) | ||
|
TheOtherBrian1
|
a0179250f9 |
docs: Change IPv6 compatibility test link (#46923)
Updated the link for checking IPv6 compatibility. ## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? docs update ## What is the current behavior? https://test-ipv6.com, the original site we recommended to users to check for IPv6 compatibility appears to be dead. ## What is the new behavior? Changed the link to https://ipv6test.google.com/ <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Documentation** * Updated IPv6 network support guidance to reference a new testing resource. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Chris Chinchilla
|
f3c4ead337 |
docs: Make easier images more readable by AI tools (#47132)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What is this PR? This PR makes some images easier to understand by AI tools. Some are removed as they served minimal purposes. Some are replaced with mermaid versions instead, which are more understandable by AI tools. Next steps after this PR are to continue migrating harder images as well as improving the text around images in general. ## Testing ``` pnpm install pnpm dev --filter=docs # or: cd apps/docs && pnpm dev ``` Then visit each converted page and verify: Diagrams render as Mermaid (not a broken image / raw code fence) in both light and dark mode: - /docs/guides/auth/auth-mfa/phone, /totp - /docs/guides/database/connecting-to-postgres - /docs/guides/platform/read-replicas (inside the accordion) - /docs/guides/storage/schema/design - /docs/guides/local-development/seeding-your-database - /docs/guides/auth/signing-keys (image gone, prose + table intact) |
||
|
Nik RichersandNik Richers
|
eecedb44aa |
docs(security): note July 9 effective date for log_connections default (#47252)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? - docs update Follow-up to DOCS-1080 / PSQL-1307 after #47199 merged. ## What is the current behavior? - Docs state that `log_connections` is off by default for new projects (#47199) but do not note when that platform default takes effect. - The `log_connections=off` default is not live until **July 9, 2026**. ## What is the new behavior? - Adds a shared note admonition (via partial) on all five pages that state the `log_connections=off` default. - Admonition copy: "This default takes effect for new projects from July 9, 2026." ### Proof: admonition renders on preview **Verified:** `supa-mdx-lint` (pass) · Vercel docs preview (all changed pages 200) | Check | Result | |-------|--------| | `supa-mdx-lint` | pass | | Preview — Postgres connection logging | [200](https://docs-git-nikrichers-docs-1080-log-connections-e-b80046-supabase.vercel.app/docs/guides/platform/postgres-connection-logging) | | Preview — Logs | [200](https://docs-git-nikrichers-docs-1080-log-connections-e-b80046-supabase.vercel.app/docs/guides/telemetry/logs#logging-postgres-connections) | | Preview — HIPAA compliance FAQ | [200](https://docs-git-nikrichers-docs-1080-log-connections-e-b80046-supabase.vercel.app/docs/guides/security/hipaa-compliance) | | Preview — Shared responsibility model | [200](https://docs-git-nikrichers-docs-1080-log-connections-e-b80046-supabase.vercel.app/docs/guides/deployment/shared-responsibility-model#managing-healthcare-data) | | Preview — SOC 2 compliance | [200](https://docs-git-nikrichers-docs-1080-log-connections-e-b80046-supabase.vercel.app/docs/guides/security/soc-2-compliance) | **Screenshots (Default behavior section):**    **Quick review links:** - [Postgres connection logging — Default behavior](https://docs-git-nikrichers-docs-1080-log-connections-e-b80046-supabase.vercel.app/docs/guides/platform/postgres-connection-logging) - [Logs — Logging Postgres connections](https://docs-git-nikrichers-docs-1080-log-connections-e-b80046-supabase.vercel.app/docs/guides/telemetry/logs#logging-postgres-connections) - [HIPAA compliance — FAQ](https://docs-git-nikrichers-docs-1080-log-connections-e-b80046-supabase.vercel.app/docs/guides/security/hipaa-compliance) - [Shared responsibility model — Managing healthcare data](https://docs-git-nikrichers-docs-1080-log-connections-e-b80046-supabase.vercel.app/docs/guides/deployment/shared-responsibility-model#managing-healthcare-data) - [SOC 2 compliance — Customer responsibilities](https://docs-git-nikrichers-docs-1080-log-connections-e-b80046-supabase.vercel.app/docs/guides/security/soc-2-compliance) ## Additional context - Scheduled cleanup PR: #47253 removes this admonition on **July 9, 2026**. - Review screenshots live in `.github/pr-screenshots/docs-1080/` on this branch for PR proof only. ### Test plan - [ ] Open [preview guide](https://docs-git-nikrichers-docs-1080-log-connections-e-b80046-supabase.vercel.app/docs/guides/platform/postgres-connection-logging) — note admonition appears under Default behavior - [ ] Confirm admonition on [Logs](https://docs-git-nikrichers-docs-1080-log-connections-e-b80046-supabase.vercel.app/docs/guides/telemetry/logs#logging-postgres-connections), [HIPAA FAQ](https://docs-git-nikrichers-docs-1080-log-connections-e-b80046-supabase.vercel.app/docs/guides/security/hipaa-compliance), [shared responsibility bullet](https://docs-git-nikrichers-docs-1080-log-connections-e-b80046-supabase.vercel.app/docs/guides/deployment/shared-responsibility-model#managing-healthcare-data), and [SOC 2 item 5](https://docs-git-nikrichers-docs-1080-log-connections-e-b80046-supabase.vercel.app/docs/guides/security/soc-2-compliance) - [ ] Merge #47253 on July 9 after the platform default is live --------- Co-authored-by: Nik Richers <nik@validmind.ai> |
||
|
Illia Basalaiev
|
ca48e596cf |
chore: add audit logs drains to documentation (#47190)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES/NO ## What kind of change does this PR introduce? docs update ## What is the current behavior? missing mention of the audit logs drains ## What is the new behavior? add audit logs drains info ## Additional context <img width="942" height="396" alt="CleanShot 2026-06-22 at 18 10 06" src="https://github.com/user-attachments/assets/7ca29e42-3d18-4a6a-9e2e-e9a274f393f4" /> <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Documentation** * Added a new **“Accessing Audit Log Drains”** section explaining how to stream platform audit log events in real time using **Audit Log Drains**, including where to configure this in the dashboard. * Updated the guide’s introduction to reference external streaming via Audit Log Drains. * Revised the **“Limitations”** section to remove the prior note about lacking drain setup, while retaining the dashboard-export limitation and the plan-based retention information. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Miranda Limonczenko
|
ea539b4f83 |
fix(docs) Remove unneeded double border on docs Accordion (#47202)
Closes DOCS-974 <img width="891" height="328" alt="Screenshot 2026-06-22 at 3 11 13 PM" src="https://github.com/user-attachments/assets/d7b49d56-cf77-4c1d-a933-7cbeab3168c2" /> ## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## Problem From Linear: Accordion usage in the docs is inconsistent and can render with double lines instead of single lines. The current docs contribution guidance appears to recommend wrapping accordions with an extra div, which seems to be the cause of the extra divider in some pages. ## Solution This PR: - Removes all wrapping `divs` to AccordionItems that adds an extra border - For a11y, adds a cursor pointer and a slight bg color change on hover to make the clickable area more obvious - For a11y, adds reduce-motion option for animation and `aria-hidden` on the chevron **Note:** It is good for a11y to have more than one hover-state indicator. For example, color-change and an underline. ## Tophatting To review changes on the preview environment: 1. Go to `/docs/guides/platform/backups` and `/docs/guides/platform/migrating-to-supabase/auth0#frequently-asked-questions-faq`. 2. Expand accordion. 3. See nothing visually odd such as strange spacing or double borders. **Note:** To be exhaustive in your review, view all affected URLs and scan the docs for `border-b` to see if there are any stragglers. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Style** * Enhanced accordion components with improved hover state styling for better visual feedback. * **Refactor** * Simplified accordion markup across documentation pages for cleaner, more consistent layout and improved component nesting structure. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Jeremias Menichelli
|
21785b2418 | fix: Fix torubleshooting frontmatter validation (#47220) | ||
|
|
d1f71464f1 |
docs(security): document log_connections=off default and re-enable path (#47199)
## I have read the CONTRIBUTING.md file. YES ## What kind of change does this PR introduce? - docs update Closes DOCS-1080. ## What is the current behavior? - Linear item: [DOCS-1080](https://linear.app/supabase/issue/DOCS-1080/update-hipaa-and-security-docs-to-reflect-the-log-connectionsoff) (parent: PSQL-1307) - Docs do not mention that Postgres `log_connections` defaults to off for new projects, or how customers re-enable it for HIPAA/SOC 2 audit needs. - No customer-facing how-to for the Management API `log_connections` setting. ## What is the new behavior? - New guide: "Postgres connection logging" — default behavior, dashboard instructions, Management API curl examples, compliance notes. - HIPAA shared-responsibility, HIPAA projects, SOC 2, HIPAA compliance FAQ, logs guide, custom-postgres-config, and product-security updated with cross-links. - Platform nav entry added under **Platform → Postgres Connection Logging**. ### Proof: new guide and cross-links render **Verified:** `pnpm lint:mdx` (pass) · local dev (all changed pages 200) · Vercel preview (new page 200) | Check | Result | |-------|--------| | `pnpm lint:mdx` | pass (exit 0) | | Preview new guide | [200](https://docs-git-nikrichers-docs-1080-update-hipaa-and-e3b13d-supabase.vercel.app/docs/guides/platform/postgres-connection-logging) | | Preview HIPAA bullet | [shared-responsibility-model#managing-healthcare-data](https://docs-git-nikrichers-docs-1080-update-hipaa-and-e3b13d-supabase.vercel.app/docs/guides/deployment/shared-responsibility-model#managing-healthcare-data) | **Quick review links:** - [Postgres connection logging — New guide for the `log_connections=off` default and re-enabling via dashboard and Management API](https://docs-git-nikrichers-docs-1080-update-hipaa-and-e3b13d-supabase.vercel.app/docs/guides/platform/postgres-connection-logging) - [Shared Responsibility Model — Managing healthcare data — Added customer responsibility to keep connection logging enabled](https://docs-git-nikrichers-docs-1080-update-hipaa-and-e3b13d-supabase.vercel.app/docs/guides/deployment/shared-responsibility-model#managing-healthcare-data) - [HIPAA Projects — Added connection logging to required project configuration](https://docs-git-nikrichers-docs-1080-update-hipaa-and-e3b13d-supabase.vercel.app/docs/guides/platform/hipaa-projects) ## Additional context - **Before ready for review:** add dashboard screenshots once FE-3666 merges; add changelog cross-link when PSQL-1307 entry is published. - CLI does not expose `log_connections`; how-to documents Management API only until dashboard screenshots are added. ### Test plan - [ ] Open [preview guide](https://docs-git-nikrichers-docs-1080-update-hipaa-and-e3b13d-supabase.vercel.app/docs/guides/platform/postgres-connection-logging) — default behavior, API examples, compliance sections present - [ ] Confirm [HIPAA shared-responsibility bullet](https://docs-git-nikrichers-docs-1080-update-hipaa-and-e3b13d-supabase.vercel.app/docs/guides/deployment/shared-responsibility-model#managing-healthcare-data) links to the new guide - [ ] Confirm Platform nav includes **Postgres Connection Logging** - [ ] Spot-check Management API paths against `/docs/reference/api/v1-update-postgres-config` - [ ] After FE-3666: add Database Settings screenshots to the guide and PR proof section <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit ## Summary by CodeRabbit * **Documentation** * Added a full guide for enabling/disabling Postgres connection logging (dashboard + Management API), including verification steps and examples. * Clarified which Postgres parameters are Management API–only (CLI limitations), with `log_connections` as an example. * Updated HIPAA, SOC 2, and shared responsibility guidance to recommend keeping Postgres connection logging enabled, plus added related FAQ/resources. * Expanded telemetry logs documentation with “Logging Postgres connections” and Logs Explorer visibility notes. * **UI / Navigation** * Added the new “Postgres Connection Logging” entry to the Platform configuration navigation. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Nik Richers <nik@validmind.ai> Co-authored-by: Chris Chinchilla <chris.ward@supabase.io> Co-authored-by: Chris Chinchilla <chris@chrischinchilla.com> |
||
|
|
bf0f66900a |
docs: Add troubleshooting guide for Kong under heavy load (#47198)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? Docs update ## What is the current behavior? There is no documentation explaining why Kong stops responding under heavy load during local development with the CLI, or how to resolve it. ## What is the new behavior? Added a new troubleshooting guide (`kong-stops-responding-under-heavy-load-locally.mdx`) that: - Explains why Kong becomes unresponsive under heavy load in local development (single nginx worker process by default to minimize memory usage) - Provides clear solutions using the `KONG_NGINX_WORKER_PROCESSES` environment variable - Shows multiple usage examples (auto, fixed number, exported variable) - Includes instructions for restarting the stack after changes - Links to related resources (local development guide and CLI repository) ## Additional context This guide helps developers troubleshoot a common issue when running bulk operations (e.g., Storage API operations) against a local Supabase stack. The solution is straightforward but not immediately obvious without documentation. https://claude.ai/code/session_01DXB9PjcuKsNeWYyLFbTXoy <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Documentation** * Added troubleshooting guide for Kong API gateway connectivity issues under heavy load in local development, including symptom identification, resolution steps for worker process configuration, and links to related resources. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Claude <noreply@anthropic.com> Co-authored-by: Chris Chinchilla <chris.ward@supabase.io> |
||
|
supabase-supabase-autofixer[bot]andgithub-docs-bot
|
6af0a5a9f0 |
[bot] Sync from supabase/troubleshooting (#47207)
This PR syncs the latest troubleshooting guides from the supabase/troubleshooting repository. Co-authored-by: github-docs-bot <github-docs-bot@supabase.com> |
||
|
Utkarash Kumar Singh
|
432b339ff9 |
docs: fix ltree reindex detection + specify Postgres version in upgrade guide (#47188)
## What Two fixes to the **Ltree indexes require reindexing** and **Custom operator selectivity estimators** sections of the upgrade guide (added in #47003): 1. **ltree affected-check was incomplete.** The section only showed how to *find* ltree indexes — not how to determine whether the database is actually affected. A project on a single-byte (e.g. LATIN1) + `libc` database would run it, see its ltree indexes, and needlessly reindex. Added the canonical `reindex_required` check (multibyte encoding **or** non-`libc` collation provider) so unaffected users correctly see "no action needed." This matches the detection used in the customer email, the support playbook, and the dashboard upgrade warning. 2. **No version specified.** Neither section said which Postgres version it applies to. Added `_Applies when upgrading to Postgres 15.18 or 17.10._` to both. ## Notes - Docs-only change. - supa-mdx-lint + prettier clean. - Follow-up to #47003. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Documentation** * Updated upgrade guides for Postgres 15.18 and 17.10 with explicit applicability notes * Clarified the Ltree indexes reindexing workflow by adding an initial “reindex required” check before identifying affected indexes * Improved documentation for custom operator selectivity estimators with clearer version-specific guidance <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Jeremias Menichelli
|
9de5b16909 | chore: Refactor ErrorCodes component and data. Offer markdown alternative (#47189) | ||
|
Pamela Chia
|
d549e1f16b | fix(billing): clarify averaged usage messaging (#47181) | ||
|
Vaibhav
|
549c1fb6ca |
fix(docs): align edge function docs (#47148)
## TL;DR aligns the remaining Phase 2 Edge Functions docs snippets with `@supabase/server` ## Whats Fixed? updated outdated imports and version references, and refreshed JSON examples to use Response.json() where it makes sense. left non-JSON responses as is where the integration or format actually needs them ## Ref: - towards COM-269 <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Documentation** * Updated numerous Edge Function guides and examples to use modern `npm:`/`jsr:` import specifiers instead of legacy Deno URL imports. * Standardized success and error responses to return JSON consistently (using `Response.json()` and equivalent helpers) and added/clarified appropriate HTTP status codes. * Improved example error payload shapes in several guides for clearer, structured failures. * **Chores** * Refreshed version ranges in documentation and examples across SDKs and client libraries. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
TheOtherBrian1andChris Chinchilla
|
bd18ff98e9 |
Changed order that CLI flags are applied in (#47098)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? Docs update ## What is the current behavior? A bug causes the CLI to fail when the `--project-ref` flag is not applied last in the chain ## What is the new behavior? Moved it to the end of the chain ## Additional context Slack: - https://supabase.slack.com/archives/C02BJ2239GA/p1781816645742719 <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Documentation** * Updated CLI command examples for managing Postgres configuration, including corrected parameter ordering and improved line formatting for the related `postgres-config` update/delete commands. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Chris Chinchilla <chris.ward@supabase.io> |
||
|
Utkarash Kumar Singh
|
a5b820d51b |
feat(upgrade): surface ltree reindex + operator estimator upgrade warnings (#47003)
## What Studio + docs support for two **non-blocking** upgrade-eligibility warnings for the PG 15.18 / 17.10 release: - **`ltree_reindex_required`** — ltree indexes on a multibyte / non-libc database must be `REINDEX`ed after upgrade. - **`operator_estimator_gate`** — operators referencing a non-built-in selectivity estimator (CVE-2026-2004) can't be recreated by a non-superuser. ## Changes - `UpgradeWarnings.tsx` — title/description/link for both types; unrecognized warning types are skipped rather than rendering an empty admonition. - `apps/docs/.../platform/upgrading.mdx` — two upgrade-guide sections (with detection + remediation SQL) that the warnings link to. - `api-types` — the two types added to `ProjectUpgradeEligibilityResponse.warnings`. ## Server side Detection/emission lives in the platform repo: **supabase/platform#34161**. Both warnings are version-gated there (only fire when upgrading to ≥ 15.16 / 17.8). Refs: PSQL-1247 <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Upgrade warnings now support additional warning types, with type-specific titles, descriptions, and optional “Read upgrade notes” links. * The project upgrade eligibility response now returns these additional warning types. * **Bug Fixes** * Upgrade warnings are rendered consistently for all warning entries (no special-casing). * **Documentation** * Added Postgres `ltree` upgrade warnings, including detection queries and `REINDEX INDEX CONCURRENTLY` remediation guidance. * Added operator selectivity estimator warnings, including superuser requirements and how to detect affected operators. * **Chores** * Updated spelling lint exceptions for common terms. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
|
93d3de9954 |
feat(docs): update edge function testing guide (#47055)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES Based on the contents from: @kallebysantos https://github.com/kallebysantos/play.supabase.unit-tests ## What kind of change does this PR introduce? Bug fix, feature, docs update, ... ## What is the current behavior? Please link any relevant issues here. ## What is the new behavior? Feel free to include screenshots if it includes visual changes. ## Additional context Add any other context or screenshots. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit ## Release Notes * **Documentation** * Completely redesigned the unit and integration testing guide for Deno-based Supabase Edge Functions using a concrete example * Added a recommended test folder structure and example business-rule module * Introduced BDD-style unit testing patterns with runnable commands * Expanded end-to-end integration testing guidance, including mocking of outgoing REST calls * Updated test utilities for environment setup and JWT generation * Refreshed best practices and resources sections <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: github-actions[bot] <41898282+github-actions[bot]@users.noreply.github.com> Co-authored-by: Kalleby Santos <kalleby_santos@hotmail.com> Co-authored-by: Kalleby Santos <105971119+kallebysantos@users.noreply.github.com> |
||
|
Miranda LimonczenkoandNik Richers
|
801244463a |
chore(docs) Demote h1s in the doc body to avoid multiple h1s (#47061)
Closes DOCS-875 **Before:** <img width="1465" height="755" alt="Screenshot 2026-06-17 at 2 19 31 PM" src="https://github.com/user-attachments/assets/5768e7d5-0ef9-43a3-8223-e28b340b3c08" /> **Caption:** "Errors" at the bottom of the screen is just as large as the title. The right sidebar shows h3s. Source: https://supabase.com/docs/guides/database/prisma/prisma-troubleshooting#solution-server-has-closed-the-connection **After:** <img width="1409" height="750" alt="Screenshot 2026-06-17 at 2 20 44 PM" src="https://github.com/user-attachments/assets/e39c797c-5b1f-4fce-a1a6-b3eff9e65f18" /> **Caption:** The "Errors" at the bottom of the screen is smaller than the main h1. The right drops the "Solutions" headers. Source: https://docs-git-demote-h1s-in-body-docs-supabase.vercel.app/docs/guides/database/prisma/prisma-troubleshooting#solution-server-has-closed-the-connection ## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## Problem The `title` frontmatter generates an `h1`. However, several pages have multiple h1s. ## Fix This PR demotes pages with h1s in the markdown body to h2s and so on. See [a troubleshooting page in production](https://supabase.com/docs/guides/troubleshooting/supabase--your-network-ipv4-and-ipv6-compatibility-cHe3BP) and in [in preview](https://docs-git-demote-h1s-in-body-docs-supabase.vercel.app/docs/guides/troubleshooting/supabase--your-network-ipv4-and-ipv6-compatibility-cHe3BP). ## Future improvements Possibly, we can add a linting rule to prevent this in the future. We'd also want to check that the heading hierarchy is always consistent. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit ## Summary by CodeRabbit * **Documentation** * Updated multiple guides and troubleshooting articles to enforce consistent heading hierarchy and improved section nesting for clearer in-page structure. * Refreshed troubleshooting pages with cleaner table of contents and navigation, including added guide links and re-leveled subsections. * Reformatted Prisma troubleshooting content (including a deprecated redirect) without changing the underlying guidance. * Added a warning about manually setting database connection limits and adjusted related warning/formatting across the max-connections guide. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Nik Richers <nrichers@gmail.com> |
||
|
Chris ChinchillaandRodrigo Mansueli
|
5c08ef4233 |
docs: clarify pgmq rls documentation and integration dashboard (#47082)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Documentation** * Updated the Queues quickstart guide for improved clarity, including revised “Create queue” button labeling, allowed queue-name character guidance, and refreshed light/dark screenshots. * Reworked the “What happens when you create a queue?” section, including Data API exposure guidance and required RLS enablement details. * Expanded the permissions section with a clearer enabled-vs-blank role table and strengthened warnings against client-side exposure. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Rodrigo Mansueli <rodrigo@mansueli.com> |
||
|
Peter Chen J.
|
4a57a95755 |
docs: update stale auth hook links (#46948)
This updates the remaining stale auth hook references after the auth hooks guide moved from hash anchors to dedicated subpages. It switches the RBAC guide to the current custom access token hook page, updates the MFA verification hook reference in both the docs error-code source and the shared-data export, and fixes the matching custom access token hook comments in the Slack Clone SQL examples. Testing: not run. Link-target updates only. Refs #46947 <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit ## Release Notes * **Documentation** * Updated error code and auth hook documentation reference links to point to more specific canonical documentation pages, improving accuracy of references for developers. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Syed Osama Ali Shah
|
c11411e2c6 |
docs: fix broken Drizzle connection snippet (#43920) (#46894)
## What kind of change does this PR introduce? Bug fix (documentation) — fixes #43920. ## What is the current behavior? The Drizzle connection example (`db.ts`) at [`apps/docs/content/guides/database/drizzle.mdx`](https://github.com/supabase/supabase/blob/master/apps/docs/content/guides/database/drizzle.mdx) does not compile or run as written: ```ts let connectionString = process.env.DATABASE_URL if (connectionString.includes('postgres:postgres@supabase_db_')) { const url = URL.parse(connectionString)! url.hostname = url.hostname.split('_')[1] connectionString = url.href } // ... export const db = drizzle(client); ``` - `process.env.DATABASE_URL` is `string | undefined`, so `.includes(...)` errors with **"Object is possibly 'undefined'"** — copy-pasting the snippet fails to type-check (the core of #43920). - `URL.parse()` is a very recent static method (Node 22.1+/modern runtimes only) and isn't portable for a docs example. - The final line ends with a stray `;`, which violates this repo's prettier config (`semi: false`). ## What is the new behavior? Three surgical fixes to the snippet: ```ts let connectionString = process.env.DATABASE_URL! if (connectionString.includes('postgres:postgres@supabase_db_')) { const url = new URL(connectionString) url.hostname = url.hostname.split('_')[1] connectionString = url.href } // ... export const db = drizzle(client) ``` - `DATABASE_URL!` — the example assumes the env var is set (it's set in the step above), matching Drizzle's own docs. - `new URL(connectionString)` — standard and portable. - Dropped the trailing semicolon to satisfy `semi: false`. No prose changes; the docker hostname-rewrite logic is unchanged. ## Validation The corrected snippet is **prettier-clean** under this repo's config (`semi: false`, `singleQuote: true`, `printWidth: 100`) — verified idempotent with `prettier --parser typescript`. The change is a single code block in one MDX file. ## Additional context Fixes #43920. The undefined-variable / type-unsafe form was introduced in #40288. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Documentation** * Updated Drizzle database quickstart: added explicit validation for the DATABASE_URL environment variable and improved connection-string parsing to better handle Docker/Supabase hostnames, plus clarified client/DB initialization steps. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
|
80b1b3e04d |
docs: update PostgreSQL upgrading guide (#46939)
Committer: Divya Sharma <divya.sharma@supabase.io> ## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? docs update ## What is the current behavior? Current doc link : https://github.com/supabase/supabase/blob/master/apps/docs/content/guides/platform/upgrading.mdx ## What is the new behavior? Changed the doc to reflect the upgrade process ## Additional context - Added pre-upgrade and post-upgrade best practices - Document upgrade pre-requisites - Re-arranged the sections - removed outdated info <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Documentation** * Restructured the database upgrade guide into a single, explicit step-by-step “How we upgrade” flow * Added new pre-upgrade and post-upgrade best practices sections * Expanded upgrade prerequisites, including read-replica requirements, `pg_upgrade` limitations, and deprecated/unsupported extension guidance * Updated Postgres 17 upgrade guidance, including handling deprecated extensions and `pg_cron`-related implications * Refreshed caveats with updated disk sizing, timing-window details, and restore guidance <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Divya Sharma <divyasharma@Divyas-MacBook-Pro.local> Co-authored-by: github-actions[bot] <41898282+github-actions[bot]@users.noreply.github.com> Co-authored-by: Chris Chinchilla <chris@chrischinchilla.com> Co-authored-by: Chris Chinchilla <chris.ward@supabase.io> |
||
|
Chris Chinchilla
|
188b7d5e28 |
docs: Fix some troubleshooting links (#47076)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Documentation** * Updated documentation links in Realtime guides and troubleshooting sections to reflect new URL structure. * Reorganized internal navigation paths for channel management, error handling, and performance monitoring resources. * Improved link consistency across multiple Realtime documentation sections. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
|
0aa7b4965f |
chore(docs) Remove instances of let's to resolve mdx lint warnings (#47013)
Contributes to DOCS-1052 Contributes to DOCS-1057 ## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? Resolves linting warning for "let's" and adds an exception for product name. ## Tophatting 1. Read the diff and see if changes make sense in context. 2. Run `pnpm lint:mdx`, search for "let's" and see no instances. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Documentation** * Updated instructional copy across multiple AI, authentication, database, functions, realtime, storage, and troubleshooting guides to improve clarity and consistency. * Replaced conversational phrasing (for example, “Let’s…/Let’s see…”) with direct imperatives, tightened example lead-ins, and adjusted a few step explanations for readability. * Refreshed some tutorial text and code-sample presentation in guides (no behavioral changes). * Added/adjusted minor MDX lint guidance in a couple of documents. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: github-actions[bot] <41898282+github-actions[bot]@users.noreply.github.com> Co-authored-by: Nik Richers <nrichers@gmail.com> |
||
|
Miranda LimonczenkoandChris Chinchilla
|
58cb199db0 |
chore(docs) Replace utilize with use (#47010)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? Resolves utilize lint warnings. ## What is the current behavior? Utilize lint warnings are present. ## Tophatting To see that this issue is resolved: 1. See the diff for content clarity. 2. Run `pnpm lint:mdx` to see no more remaining utilize errors. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit ## Documentation - Improved documentation clarity and consistency across platform guides, including AI going-to-prod, custom claims/RLS RBAC, authentication (anonymous, Web3, social login), and database connection/configuration. - Refined technical wording throughout database, realtime, storage, billing, performance, telemetry, and troubleshooting guides (for example, standardizing phrasing like “use” vs “utilize”). - Updated select guidance for clearer wording on database pre-warming and clarified the scope of the Postgres logging note. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Chris Chinchilla <chris.ward@supabase.io> |
||
|
fadymak
|
5babf1092a |
feat(auth): accept Android app origins for WebAuthn RP origins (#47043)
Allow `android:apk-key-hash:<base64url SHA-256>` entries in `WEBAUTHN_RP_ORIGINS` alongside https/localhost-http origins. Non-http(s) origins are matched as-is downstream and Android is responsible to binding the origin to the RP ID via digital asset links. |
||
|
Katerina SkroumpelouandChris Chinchilla
|
6eb40f17a7 |
docs: purge safeGetSession + getUser from auth example code (#47042)
Sweeps the example code that creating-a-client.mdx and other auth docs pull via $CodeSample, so the rendered pages match the "use getClaims()" guidance. Also adds Database type stubs and parameterizes SupabaseClient<Database> across SvelteKit and Hono examples. Fixes #40985 <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit ## Release Notes * **Documentation** * Updated OAuth server getting-started guide to use a claims-based consent/auth gate and preserve the authorization identifier on redirect. * Added the `auth_methods` partial across framework sections in the server-side “creating a client” guide. * **Refactor** * Updated authentication examples for Hono, Next.js, and SvelteKit to rely on JWT claims for logged-in checks and protected routes. * Streamlined example auth state and UI rendering to use claims-derived information. * **Type Updates** * Improved TypeScript typing for Supabase clients and app auth data across examples, including generated database type stubs. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Chris Chinchilla <chris@chrischinchilla.com> |
||
|
Jeremias Menichelli
|
90b15736aa | chore: Repurpose CostWarning component as partial only (#46996) | ||
|
Andrey A.
|
f6d0b9eda1 | docs(self-hosted): update pg 17 upgrade how-to (#46989) | ||
|
Katerina Skroumpelou
|
8b05c769fb |
docs: add Nuxt/SolidStart server routes, fix stale getClaims docs (#47001)
Resolves four docs gaps surfaced in #40985. The Nuxt SSR example in `creating-a-client.mdx` now uses `getClaims()` instead of `getUser()`, matching the file's own guidance at `:253`. The SvelteKit tutorial drops a stale `event.locals.safeGetSession` reference whose linked `app.d.ts` no longer declares one. The Nuxt and SolidJS tutorials each gain a new server-route section using `@supabase/server` (h3 adapter for Nuxt, `createSupabaseContext` for SolidStart), addressing the original complaint that those tutorials had no server setup at all. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Documentation** * Enhanced Nuxt 3 getting-started tutorial with new guidance on adding server routes, validating auth sessions, and using Supabase middleware for protected (and optional public) endpoints. * Updated the Nuxt Server route Supabase SSR example to validate authentication using token claims during server-side refresh. * Added a SolidJS → SolidStart SSR/API migration section, including an example protected profile route and how to make it public. * Refined SvelteKit tutorial wording around TypeScript-related session handling and updated terminology. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Guilherme SouzaandClaude
|
0c9d90051f |
docs: Update documentation from swift SDK changes (#47024)
## Summary Updates docs based on stable releases in `supabase/supabase-swift`. ## Changes analyzed - **SDK**: swift - **Repo**: https://github.com/supabase/supabase-swift - **Stable tag range**: `v2.47.2...v2.48.0` - **Commits**: `716e0de6e7e0ec8eba54c6c4dfb8e980b3d51370...e5020ae5a1d01c46cc60fb5eb01157666d7214b6` ## Documentation updates ### `apps/docs/spec/supabase_swift_v2.yml` - Added `sign-in-with-passkey` entry — `signInWithPasskey(presentationAnchor:)` high-level helper (iOS 16+/macOS 13+, experimental) - Added `register-passkey` entry — `registerPasskey(presentationAnchor:)` high-level helper (iOS 16+/macOS 13+, experimental) - Added `passkey-api` group stub with 7 lower-level method entries: - `passkey-list` — `listPasskeys()` - `passkey-update` — `renamePasskey(id:friendlyName:)` - `passkey-delete` — `deletePasskey(id:)` - `passkey-start-registration` — `getPasskeyRegistrationOptions()` - `passkey-verify-registration` — `verifyPasskeyRegistration(challengeId:credentialResponse:)` - `passkey-start-authentication` — `getPasskeyAuthenticationOptions()` - `passkey-verify-authentication` — `verifyPasskeyAuthentication(challengeId:credentialResponse:)` - Updated `auth-mfa-api` overview notes to mention WebAuthn MFA (experimental) - Updated `mfa-enroll` notes and added `enrollWebAuthnFactor` example - Updated `mfa-verify` notes and added `verifyWebAuthnFactor` example ### `apps/docs/content/guides/auth/passkeys.mdx` - Added Swift tabs to: Enable in the client, Register a passkey, Sign in with a passkey, Two-step API, Manage passkeys - Updated SDK version note to include `supabase-swift` v2.48.0 - Updated reference links to include Swift All new Swift passkey APIs are gated behind `@_spi(Experimental) import Supabase`. --- 🤖 Generated with [Claude Code](https://claude.com/claude-code) <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit ## Documentation * Expanded Swift SDK passkeys documentation to cover enabling, registering, signing in, managing, and Admin-related notes. * Added experimental Swift guidance for WebAuthn/passkeys, including updated minimum SDK version requirements. * Extended MFA to support WebAuthn/passkeys enrollment and verification (in addition to existing methods). * Added reference documentation for low-level passkey APIs to support custom authentication flows. ## Chores * Updated documentation linting spell-check allow list to include **visionOS**. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Claude <noreply@anthropic.com> |
||
|
Guilherme Souza
|
f4c3e26fd7 |
docs: Update documentation from dart SDK changes (#47006)
## Summary Updates docs based on stable releases in `supabase/supabase-flutter`. ## Changes analyzed - **SDK**: dart - **Repo**: https://github.com/supabase/supabase-flutter - **Stable tag range**: `supabase_flutter-v2.14.1...supabase_flutter-v2.15.0` - **Commits**: `81c1590728a5e08bebdc152bd59a7c1e7644c8b2...9030650b74e253020f8c614b3bfb2c993b6061af` ## Documentation updates `apps/docs/spec/supabase_dart_v2.yml` — adds entries for the new passkey APIs landed in `supabase_flutter-v2.15.0` ([gotrue#1392](https://github.com/supabase/supabase-flutter/pull/1392), [supabase_flutter#1408](https://github.com/supabase/supabase-flutter/pull/1408)): - `signInWithPasskey()` / `registerPasskey()` — high-level helpers on `supabase_flutter` that drive the full WebAuthn ceremony. - `auth.passkey.*` — server side of the WebAuthn ceremony: `list`, `update`, `delete`, `startRegistration`, `verifyRegistration`, `startAuthentication`, `verifyAuthentication`. - `auth.admin.passkey.*` — admin endpoints: `listPasskeys`, `deletePasskey`. `apps/docs/content/guides/auth/passkeys.mdx` — adds Dart code examples to every passkey section (Enable in the client, Register, Sign in, Two-step API, Manage, Admin API) and points the reference links at both the JavaScript and Dart specs. Bumps the "Requires" admonition to include `supabase_flutter v2.15.0`. Other v2.14.2 / v2.15.0 changes that did not require doc updates: - `feat(realtime): protocol format 2.0.0` — protocol versions are already documented in `realtime/protocol.mdx`; the SDK now defaults to v2.0.0 but exposes a `version: RealtimeProtocolVersion.v1` opt-out, which is an SDK detail rather than a docs change. - `fix(gotrue): support asymmetric JWTs in getClaims` — bug fix to the existing `auth.getClaims` (no new API). - The rest are bug fixes and internal refactors (storage `createSignedUrls` null handling, postgrest stack traces, gotrue refresh-token races, PKCE email-change, realtime deaf-socket guards, lint/test/CI hygiene). `common-client-libs-sections.json` already contains entries for every new spec `id`, so the sidebar nav picks them up automatically. --- 🤖 Generated with [Claude Code](https://claude.com/claude-code) <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Documentation** * Added Dart language examples to passkey authentication guide covering client initialization, user registration, sign-in workflows, two-step ceremony flows, and passkey management operations * Updated Dart client specification to document new passkey authentication functions and admin-level passkey management capabilities <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Gildas GarciaandIvan Vasilov
|
96d43099bb |
chore: refactor Button API so that it can be used a standard button (#46880)
## Problem Our `<Button>` component breaks the default `button` contract by redefining the `type` prop to set its variant (`primary`, `default`, etc) instead of the button type (`submit`, `button`, etc). This is confusing and forces to write more code when using it with shadcn components that expect/inject the standard button props. ## Solution - rename the `type` prop to `variant` - rename the `htmlType` prop to `type` - propagate the changes where necessary - format code ## How to test As this is just prop renaming, if it builds it's ok --------- Co-authored-by: Ivan Vasilov <vasilov.ivan@gmail.com> |
||
|
|
608040b8cb |
chore(docs) Resolve 'simple' style warnings where applicable (#46966)
Contributes to DOCS-1052 ## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? Resolves MDX linting errors related to "simple" where it applies. There was a couple cases that did not apply. For example, a product with "Simple" in the name. These changes are made in context, either by removing or using a more descriptive synonym like "minimal" or "basic". ## Tophatting 1. Read each of the diffs. 2. See that the text still makes sense in context. For extra due diligence, you can run `pnpm lint:mdx` locally and see the 'simple' errors that remain and whether they are worth addressing. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit ## Summary by CodeRabbit * **Documentation** * Updated many guide, tutorial, and troubleshooting pages with clearer “basic”/“minimal” wording across setup steps, local testing instructions, security cautions, and RLS guidance. * Refined headings, example descriptions, and inline comments for consistency (including deployment, MCP, metrics API, and search/function phrasing). * Improved readability with small snippet formatting tweaks (whitespace plus import/comment ordering) and added a self-hosting debugging note for Envoy admin endpoints via a short-lived `curl` container. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: github-actions[bot] <41898282+github-actions[bot]@users.noreply.github.com> Co-authored-by: coderabbitai[bot] <136622811+coderabbitai[bot]@users.noreply.github.com> Co-authored-by: Chris Chinchilla <chris.ward@supabase.io> Co-authored-by: Nik Richers <nrichers@gmail.com> |
||
|
|
726e226f66 |
[bot] Sync from supabase/troubleshooting (#46971)
This PR syncs the latest troubleshooting guides from the supabase/troubleshooting repository. --------- Co-authored-by: github-docs-bot <github-docs-bot@supabase.com> Co-authored-by: Chris Chinchilla <chris.ward@supabase.io> Co-authored-by: github-actions[bot] <41898282+github-actions[bot]@users.noreply.github.com> |
||
|
Chris Chinchilla
|
a1cc7294b2 |
docs: Add the ability to individually toggle AI features (#46807)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Agent Plugin, Agent Skills, and Prompts menu items added to navigation (now feature-gated). * **Documentation** * AI Prompts and Agent Skills sections are now conditionally shown in the docs based on feature flags. * **Chores** * New feature flags for docs (Agent Plugin, Agent Skills, Prompts) added and enabled in config/schema. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Kalleby Santos
|
67cfab1047 |
fix(docs): functions error codes into Debugging section and link references (#46957)
## What kind of change does this PR introduce? docs update ## What is the new behavior? Moving the new `error-codes` page to "Debugging" section. Adding link reference to it under `status-codes` page. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit ## Release Notes * **Documentation** * Reorganized Error Codes guide navigation to the Debugging section for improved discoverability * Enhanced status codes guide with details on HTTP status codes and error response headers in Edge Functions <!-- end of auto-generated comment: release notes by coderabbit.ai --> |














