mirror of
https://github.com/supabase/supabase.git
synced 2026-10-05 17:35:10 +03:00
98cfe3307eb99436bbf10fa74fa2d495e40ce483
19104
Commits
| Author | SHA1 | Message | Date | |
|---|---|---|---|---|
 Pamela Chia |
98cfe3307e |
feat(telemetry): fix creation-funnel tracking gaps (#47386)
## Summary The creation-funnel instrumentation that shipped Jun 25 (#47291, #47293) had real gaps, surfaced by the weekly telemetry audit and confirmed against production PostHog data before I touched code. The two automated reports also contradicted each other on `errorReason`; I checked production (every value is a controlled slug) and the emit path (only `useTrackFunnelError` sets it, and it only accepts classified slugs), so I left the type as-is rather than add a cross-package abstraction for a risk that cannot occur today. ## Changes - Classify HTTP 401/403/404 API errors as `unauthorized` / `forbidden` / `not_found` instead of the catch-all `other`. In production the `org_creation` `other` bucket was ~96% 401s (~1,300 real over 4 days), invisible in reason breakdowns. The status-code fallback runs after the message-pattern match, so specific reasons still win and it only rescues errors that would otherwise be `other`. - Add a single `tier` property (`tier_free` / `tier_pro` / `tier_payg` / `tier_team`) to `organization_creation_completed`, which previously carried no properties. One canonical billing slug (matching `SubscriptionTier`) instead of two overlapping plan/tier fields, so the org-creation funnel segments cleanly by tier and joins against subscription data. `tier_payg` is uncapped PRO. - Freeze the submitted tier at submit time (snapshot in `createOrg`) rather than reading live form state in the success callback, so the event records the tier that was actually created even if the user edits the form during the async payment flow. - Emit `project_creation_form_exposed` with `surface: 'vercel'` on the integration deploy-button project-creation page (the enum value existed but was never fired). Gated on the URL `slug` so the impression is captured as soon as the form renders, matching the sibling exposure hook on that page. I also checked the confirm-modal error path flagged in the insights post: it already classifies via the shared `useProjectCreateMutation.onError`, so adding instrumentation there would double-count. No change made. ## Testing These are analytics events with no UI change, so correctness is in what lands in PostHog. Post-deploy validation I will run against production (project 34344): - `dashboard_error_created` where `origin='org_creation'` and `errorReason='other'` drops ~96%, with `unauthorized` / `not_found` appearing. - `organization_creation_completed.tier` populated on 100% of new events with one of the four tier slugs. - `project_creation_form_exposed` with `surface='vercel'` goes from 0 to greater than 0. ## Linear - fixes GROWTH-948 <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added telemetry for organization creation completion that includes the selected billing tier. * Added one-time telemetry when the Vercel project creation form is exposed. * **Bug Fixes** * Improved API error classification to more accurately distinguish unauthorized, forbidden, and not found responses. * **Documentation** * Updated telemetry event definitions to require tier metadata for organization creation events. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Gildas Garcia
|
d7543d536f |
chore: www Tabs migration (#47449)
## Problem We're still maintaining the old `Tabs` component which is deprecated. ## Solution Cleanup its usages in `www`: - Remove dead code - Migrate actual tabs to the new Shadcn component - Migrate non tabs to use `Button` instead There should be almost no visual changes (slight background color change on the active button below): - https://zone-www-dot-8z5cao88c-supabase.vercel.app/solutions/agencies (at the bottom) Before: <img width="999" height="412" alt="image" src="https://github.com/user-attachments/assets/97675380-e5fb-4e7e-a39e-93bcc0f2f70f" /> After: <img width="732" height="377" alt="image" src="https://github.com/user-attachments/assets/c4150142-218d-4c32-b8ce-f68f4939706e" /> - https://zone-www-dot-8z5cao88c-supabase.vercel.app/blog/postgres-full-text-search-vs-the-rest#results <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Bug Fixes** * Simplified navigation in API examples and chart tabs for a more consistent browsing experience. * Updated chart tab switching to better match the current UI behavior. * **Refactor** * Removed several carousel and admin access components, along with related styling, reducing unused page elements. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Gildas Garcia
|
e92581a3c7 |
chore: migrate Tabs to Shadcn new component (#47446)
## Problem `Tabs` is deprecated in favour of the Shadcn `Tabs` component currently suffixed with `_Shadcn_ ## Solution Migrate the only studio usage Before: <img width="662" height="396" alt="image" src="https://github.com/user-attachments/assets/62f36e98-6754-4362-9375-f2a45bd8028e" /> After: <img width="666" height="434" alt="image" src="https://github.com/user-attachments/assets/a96f9e61-7420-4e77-a60a-a5db54b0e3d6" /> <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Updated the spreadsheet import panel to use a refreshed tab interface with clearer “Upload CSV” and “Paste text” options. * Improved the layout of the import flow so each tab’s content is displayed more consistently. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Andrey A.
|
4562af27c2 | test(studio): cover SQL content remap and upsert response remap (#47445) | ||
|
Jordi Enric
|
b9f76d95f7 | feat(studio): load ClickHouse query templates when OTEL logs are on (#47390) | ||
|
hallidayo
|
35df0898c8 |
fix: table editor search state (#47085)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? Supabase > Studio > Table Editor > Filters ## What is the current behavior? When you add a filter and you are on a different page from the first or total pages from the filter you have to manually go back to the first page: https://github.com/user-attachments/assets/d254c8d4-3a5a-4e90-b7be-25a3a16a5b6f ## What is the new behavior? Table editor now automatically redirects to the first page or page in which you will see data: https://github.com/user-attachments/assets/e77aa27e-884f-45a2-a951-7fd1c675e62f ## Additional context Add any other context or screenshots. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Bug Fixes** * Updated pagination so the current page automatically returns to page 1 whenever filters are changed, keeping results consistent with the new criteria. * The reset is skipped on the initial load to avoid disrupting the default starting state. * Prevents pagination from becoming out of sync after applying or modifying filters. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Gildas Garcia
|
0e3364bbad |
Chore/cleanup studio deps (#47399)
## Problem Knip reported some unused dependencies. Some are actually used in builds, etc but others are not. ## Solution Remove the really unused dependencies <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Chores** * Cleaned up unused dependencies and removed some obsolete test/support files. * Updated project ignore rules to better match current app structure and generated files. * **Bug Fixes** * No user-facing behavior changed; this release is focused on maintenance and cleanup. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Ivan Vasilov
|
0361d1b727 |
chore: Remove CDN loading for the Monaco editor in all environments (#47182)
<!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Chores** * Standardized Monaco Editor package versions across the workspace using the shared dependency catalog. * **Bug Fixes** * Improved Monaco initialization by configuring asset loading only on the client and serving Monaco assets from a single base-path URL (removing platform-specific switching). * Streamlined Monaco stylesheet injection in Studio’s document rendering. * **New Features** * Added/updated Monaco language support in Studio, including GraphQL, SQL, and PostgreSQL, with refreshed HTML, JSON, and CSS editor modes. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Joshen Lim
|
1de298ff31 |
Reinstate https://github.com/supabase/supabase/pull/45143 into latest master (#47433)
## Context Previous PR was [here](https://github.com/supabase/supabase/pull/45143) but it got stale with lots of conflicts so figured it'll be easier redo it off the latest master Moves policies page from Auth to Database under an Access Control section along with Roles. This moves all existing files, applies redirects, and updates urls to point to the new route <img width="274" height="412" alt="image" src="https://github.com/user-attachments/assets/7952c185-64ae-4355-ba36-45397efe1787" /> <img width="453" height="471" alt="image" src="https://github.com/user-attachments/assets/04b3dcb3-48a5-4049-9893-d01109fb46a9" /> ## To test - [ ] Verify that policies now live under Database correctly <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added a quick navigation shortcut to open **Database > Policies (RLS)**. * **Bug Fixes** * Updated Policies and RLS-related links across the product to open the **Database policies** area (menus, command palette, context actions, alerts, and link-outs). * Added a permanent redirect from the old **auth policies** URL to the new **database policies** URL. * **Documentation** * Updated RLS Dashboard and security checklist instructions to reference **Database > Policies**. * **Tests** * Adjusted automated tests to validate the new Policies route. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Etienne Stalmans
|
baff377621 |
chore: update docs for temporary access alpha (#47439)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? Docs update ## Additional context Small errata fix and adds note about pgbouncer not being supported <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Documentation** * Clarified temporary access guidance: it works with direct connections and IPv4 pooler connections, but not with the IPv6 transaction pooler. * Updated the example connection options to use `jit=true` for temporary access setup. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
supabase-supabase-autofixer[bot]andsupabase-releaser[bot]
|
a7e5445e46 |
docs: update js sdk docs (2.109.0) (#47432)
Updates JS sdk documentation following stable release.
Ran `make download.tsdoc.v2` in apps/docs/spec and refreshed the
reference-content snapshot.

**Details:**
- **Version:** `2.109.0`
- **Source:** `supabase-js-stable-release`
- **Changes:** Regenerated tsdoc files from latest spec files

🤖 Auto-generated from @supabase/supabase-js stable release.

Co-authored-by: supabase-releaser[bot] <223506987+supabase-releaser[bot]@users.noreply.github.com>
|
||
|
Chris Chinchilla
|
16ce2c1a8a |
Studio: Add quickstarts instruments example to dashboard examples (#47402)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES Adds a new SQL example to the SQL editor to make following quickstarts easier. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added a new SQL quickstart template called **“Instruments”**. * The template helps users create a sample `instruments` table, add example rows, and set up read access with row-level security. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Jordi EnricandClaude Opus 4.6
|
ebafe8dd05 |
fix(logs): quote numeric pipeline_id in otel etl logs filter (#47436)
## Problem

Opening replication/ETL logs via the "View logs" button on a pipeline
details view fails with "Error executing ClickHouse query" on the OTEL
logs path.

The button links to `/logs/replication-logs?f={"pipeline_id": <id>}`,
and `pipelineId` is a number (`Number(_pipelineId)` in
ReplicationPipelineStatus, typed `number` in PipelineStatus). The OTEL
ETL filter emitted that value as an unquoted numeric literal:

```sql
WHERE source = 'etl_replication_logs' AND (log_attributes['pipeline_id'] = 123)
```

`log_attributes` is a `Map(String, String)`, so comparing its string
value to a number is a type error in ClickHouse, which surfaces as the
generic "Error executing ClickHouse query".

## Fix

Coerce the value to a string in the OTEL ETL `pipeline_id` filter so it
always compares string-to-string:

```sql
WHERE source = 'etl_replication_logs' AND (log_attributes['pipeline_id'] = '123')
```

- OTEL-only change. The legacy BigQuery path (a numeric `pipeline_id`
column) is left untouched and still compares as a number.
- The existing unit test only passed a string `'42'`, which hid the bug.
Added a numeric `42` case that would emit the unquoted literal without
the fix.

## How to test

- Open a project with an ETL/replication destination, go to the pipeline
details view, and click "View logs".
- Expected result: the logs load instead of showing "Error executing
ClickHouse query".
- Run the unit tests: `pnpm test:studio` (or target
`Logs.utils.otel.test.ts`).
- Expected result: the new test "quotes a numeric etl pipeline_id so it
compares as a string" passes, asserting `log_attributes['pipeline_id'] =
'42'`.

<!-- This is an auto-generated comment: release notes by coderabbit.ai
-->

## Summary by CodeRabbit

* **Bug Fixes**
* Fixed filtering for ETL logs so `pipeline_id` values are consistently
treated as text, including numeric inputs.
* Improved matching behavior when using the pipeline filter, helping
ensure results appear as expected.
* **Tests**
* Updated and expanded test coverage for pipeline ID filtering to verify
the corrected SQL output.

<!-- end of auto-generated comment: release notes by coderabbit.ai -->

---------

Co-authored-by: Claude Opus 4.6 <noreply@anthropic.com>
|
||
|
|
2f90228f04 |
feat(studio): port API handlers to TanStack server routes (stack 4/6, from #46424) (#47113)
**Stack 4/6** of the TanStack Start migration (#46424). Stacked on **#47112** (S3). > [!NOTE] > Mechanical and homogeneous — every file is the same shape: a `createFileRoute(...)` whose `server.handlers` delegate to the existing `pages/api` handler via `toWebHandler` (the compat shim from S2). The pages-router handlers are unchanged; Next still serves them directly and ignores `routes/`. ## What's in this PR - `routes/api/**` (~104 files): platform (`pg-meta`, auth, storage, integrations, profile, telemetry, organizations, projects…), `ai/*`, `v1/*`, `connect`, `content`/`mcp`, and standalone endpoints (`deployment-mode`, `get-ip-address`, etc.). - `routeTree.gen.ts` — **regenerated** for the routes present so far (root + auth/app + api). ## Review tip The route files are near-identical wrappers, so this is fast to skim. The generated `routeTree.gen.ts` isn't meaningful review surface. ## Verification On top of S1–S3: `studio` typecheck ✓, lint (0 errors) ✓. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added Model Context Protocol (MCP) API endpoint with configurable feature support and read-only mode * Added function artifact streaming capability for self-hosted functions * **Chores** * Migrated API route infrastructure for improved system architecture <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Alaister Young <10985857+alaister@users.noreply.github.com> Co-authored-by: Ivan Vasilov <vasilov.ivan@gmail.com> |
||
|
shaziyaandClaude Sonnet 4.6
|
90526fe0b0 |
feat(www): OpenCode integration blog post (#47419)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? **Changes:** - New blog post: `/blog/agentic-coding-on-supabase-with-opencode` - New author entry: Eric Kharitonashvili (`ekhar`) in `authors.json` - Blog images and author avatar ## Checklist - [x] Blog post reviewed internally and approved - [x] Reviewed and approved by OpenCode ([doc](https://docs.google.com/document/d/1Azyt7Ot0Q8bxBF3YOLdks8CPME-SKVUr-WXGl2HDJR8/edit?tab=t.0)) - [x] Images added - [x] Video embed added - [x] Author added to `authors.json` - [ ] Marketing +1 in `#team-marketing` --------- Co-authored-by: Claude Sonnet 4.6 <noreply@anthropic.com> |
||
|
Francesco Sansalvadore
|
ba133afc4c |
www: blog (#47236)
Update blog layout. PR breakdown of #43455 Related: #47226 #47227 #47228 |
||
|
Jordi EnricandClaude Opus 4.6
|
25f1648e3a |
fix(logs): map metadata.function_id override to otel attribute key (#47434)
## Problem Individual edge function logs are broken on the OTEL logs path. The logs chart for a single function filters by the `metadata.function_id` override key passed from the function logs page. On the OTEL path this key has no filter template, so it falls through to the unknown-clause resolver and is emitted verbatim as `log_attributes['metadata.function_id']`. OTEL drops the `metadata` root, so the live attribute key is just `function_id`. The filter matched nothing and the chart came back empty. Generated before: ```sql WHERE source = 'function_logs' AND (log_attributes['metadata.function_id'] = '...') ``` ## Fix Strip a leading `metadata.` prefix in the OTEL unknown-clause resolver (`resolveUnknownOtelClause`). The same BigQuery-style override key now resolves to `log_attributes['function_id']`, matching the working invocations query. This is the documented OTEL convention (the `metadata` root is always dropped), so it also covers any other `metadata.*` override keys. Generated after: ```sql WHERE source = 'function_logs' AND (log_attributes['function_id'] = '...') ``` ## How to test - Enable the OTEL logs path and open an edge function's Logs tab for a project with recent invocations. - Confirm the logs chart renders ok/warning/error buckets instead of an empty chart. - Run the unit tests: `pnpm test:studio` (or target `Logs.utils.otel.test.ts`). - Expected result: the new test "drops the metadata root from an override key for function logs" passes, asserting the generated SQL uses `log_attributes['function_id']`. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Bug Fixes** * Fixed OTEL filter handling so keys that include the `metadata.` prefix are translated correctly for log searches. * Filters like `metadata.function_id` now generate the expected log-attribute predicates, improving Function logs matching. * **Tests** * Added/updated inline snapshot coverage to verify SQL generation for metadata-based log filter overrides in both chart and preview queries. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Claude Opus 4.6 <noreply@anthropic.com> |
||
|
Gildas Garcia
|
b30db91d71 |
chore: cleanup UI patterns exports (#47406)
## Problem We now export components under a subpath in ui-patterns to avoid barrel files as they slow down every tools (from IDE to linters, etc.) and may also affect bundles our users have to download. ## Solution - Remove the UI patterns index file - Fix invalid impors |
||
|
Prashant Sridharan
|
ff1941b35f | Revise State of Startups landing page (#47335) | ||
|
|
635b2d6050 |
docs: standardise next steps on overview pages with content listings (#47097)
## I have read the CONTRIBUTING.md file. YES ## What kind of change does this PR introduce? This PR helps standardise link sections which is useful for overview pages that frequently use similar sections such as "Next steps", "Get started", or "Examples". Six high-traffic overview pages are migrated as a pilot, with a skill in the new [supabase/docs-agent-skills](https://github.com/supabase/docs-agent-skills) repo to audit and convert the rest in a follow-on PR. Refactored from an initial YAML front matter approach per review feedback from @jeremenichelli. Now implemented as a React component and using existing linting & Markdown export functionality. A second round of review feedback further simplified the architecture: the per-listing component registry was removed in favor of a single `<ContentListings id="..." />` component backed by an ID-keyed data lookup, the listing data moved out of `apps/docs/components/` into `apps/docs/data/content-listings/`, the listing-specific link wrapper was replaced with the existing `<Link>` + `<GlassPanel>` pattern from the rest of the docs, and the headings now defer to the shared `<Heading>` from `MdxBase.shared.tsx` (no parallel marker-to-tag mapping, no typography overrides). Great feedback, thank you! 🙏 Relates to DOCS-1032. ## What is the current behavior? Authors implement these sections however they wish. As a result, overview and index pages use inconsistent patterns for orientation links: some use hand-rolled Markdown lists, some use custom panel/grid components, some use buttons, and some have no guidance about where to go next at all. There is no shared component for these sections and no analytics on those clicks. ## What is the new behavior? Authors add orientation sections in two steps: 1. Define listing data in a `.data.ts` file under `apps/docs/data/content-listings/` (for example, `storage.data.ts`). Each `ContentListingGroup` has a globally-unique `id` like `storage-get-started`. 2. Place a single `<ContentListings id="..." />` component inline in guide MDX. The ID is also the telemetry `listingId`, so the same value disambiguates the section in PostHog dashboards. Grid and list layouts, optional icons (such as `/docs/img/icons/github-icon` with `-light.svg` variants for dark mode), and external URLs are supported. Conditionals that use `$Show` around inline components are also supported, for example for auth pricing. ### Usage example from "Storage" overview page `apps/docs/data/content-listings/storage.data.ts`: ```ts export const storageGetStarted: ContentListingGroup = { id: 'storage-get-started', heading: 'Get started', description: 'Choose the bucket type that fits your use case:', type: 'grid', items: [ { title: 'Files buckets', href: '/guides/storage/quickstart', description: 'Store and serve images, videos, documents, and general-purpose files with direct URL access and row-level security.', }, { title: 'Analytics buckets', href: '/guides/storage/analytics/introduction', description: 'Store data in Apache Iceberg tables for data lakes, logs, and ETL. Query from Postgres via foreign tables with partitioning.', }, { title: 'Vector buckets', href: '/guides/storage/vector/introduction', description: 'Store embeddings and run similarity search for semantic matching, AI, and RAG. Use HNSW indexing, distance metrics, and metadata filtering.', }, ], } ``` `apps/docs/content/guides/storage.mdx`: ```mdx <ContentListings id="storage-get-started" /> ``` Renders as: <img width="689" alt="Storage Get started listing — Files, Analytics, and Vector buckets" src="https://github.com/user-attachments/assets/0d1b9531-962f-40ae-891e-b1e93ff1c939" /> <br>Exported in Markdown as: ```md ## Get started Choose the bucket type that fits your use case: - **[Files buckets](/docs/guides/storage/quickstart):** Store and serve images, videos, documents, and general-purpose files with direct URL access and row-level security. - **[Analytics buckets](/docs/guides/storage/analytics/introduction):** Store data in Apache Iceberg tables for data lakes, logs, and ETL. Query from Postgres via foreign tables with partitioning. - **[Vector buckets](/docs/guides/storage/vector/introduction):** Store embeddings and run similarity search for semantic matching, AI, and RAG. Use HNSW indexing, distance metrics, and metadata filtering. ``` Click tracking fires via PostHog (`docs_content_listing_clicked`): ```json { "action": "docs_content_listing_clicked", "custom_properties": { "targetPath": "/guides/storage/quickstart", "linkTitle": "Files buckets", "groupTitle": "Get started", "listingId": "storage-get-started" } } ``` Still finding my way around PostHog, but I verified on preview deploy that clicking a content listing on `/docs/guides/auth` sends `docs_content_listing_clicked` to `https://api.supabase.green/platform/telemetry/event` and receives HTTP 201. ### Authoring experience Three ways to add or convert content listings: copy the agent prompt first, use snippets for manual edits, or invoke the audit skill for batch follow-on work. Refer to `CONTRIBUTING.md` for the full authoring guide. #### 1. Agent prompt Copy into Cursor or another AI assistant: ```text Add a content listing block for [TOPIC] / [SECTION] (for example, Storage / Examples). Follow CONTRIBUTING § Content listings in apps/docs. - Add data to apps/docs/data/content-listings/[topic].data.ts - Use a globally-unique kebab-case id like `[topic]-[section]` - Place inline in the guide MDX with <ContentListings id="..." /> - Copy structure from storageGetStarted in apps/docs/data/content-listings/storage.data.ts - Run pnpm test:local lib/content-listings.test.ts from apps/docs ``` #### 2. VS Code / Cursor snippets Type these prefixes in the docs workspace (`.vscode/content-listing.code-snippets`): | Prefix | Inserts | | ----------- | -------------------------------------------------------- | | `cl-data` | `ContentListingGroup` export skeleton with namespaced id | | `cl-inline` | `<ContentListings id="…" />` in guide MDX | <img width="658" height="274" alt="image" src="https://github.com/user-attachments/assets/5ef20954-7aee-4925-887d-79a5ae766b37" /> #### 3. Batch audit skill For follow-on overview page conversion or maintenance, use the [`audit-content-listings`](https://github.com/supabase/docs-agent-skills/blob/main/.claude/skills/audit-content-listings/SKILL.md) skill in `docs-agent-skills` (skill, `conversion-manifest.json`, and validation script). Example: ```text Use audit-content-listings. Audit getting-started.mdx, update conversion-manifest.json, then convert the next unconverted section only. ``` ## Additional context The implementation includes a presentational `<ContentListings />` component (grid/list layouts, GlassPanel, telemetry) backed by ID-keyed data modules, and a single markdown export handler that reads the same `id` prop from the JSX and looks up data via the shared registry. Key files: - **Data:** `apps/docs/data/content-listings/` (one `.data.ts` file per guide topic, plus `index.ts` exporting `CONTENT_LISTINGS` and `getContentListingById`) - **Renderer:** `apps/docs/components/ContentListings/` (single `<ContentListings id="…" />` component); registered in `apps/docs/features/docs/MdxBase.shared.tsx` - **Types/helpers:** `apps/docs/lib/content-listings.schema.ts` (zod schemas, type aliases, grid/heading/href helpers) - **Markdown export:** `apps/docs/internals/markdown-schema/Listings.ts` (single ID-driven handler) wired into `apps/docs/internals/generate-guides-markdown.ts` - **Telemetry:** `docs_content_listing_clicked` defined in `packages/common/telemetry-constants.ts`, fired from `ContentListings.client.tsx` - **Authoring guide:** `apps/docs/CONTRIBUTING.md` (Components and elements → Content listings) - **VS Code snippets:** `.vscode/content-listing.code-snippets` (`cl-data`, `cl-inline`) ### Before & After #### Auth | [Before (production)](https://supabase.com/docs/guides/auth) | [After (preview)](https://docs-git-fork-nrichers-nikrichers-docs-1032-sta-e2a8cb-supabase.vercel.app/docs/guides/auth) | | --------------------------------------------------------------------------------------------------------------------------- | --------------------------------------------------------------------------------------------------------------------------- | | 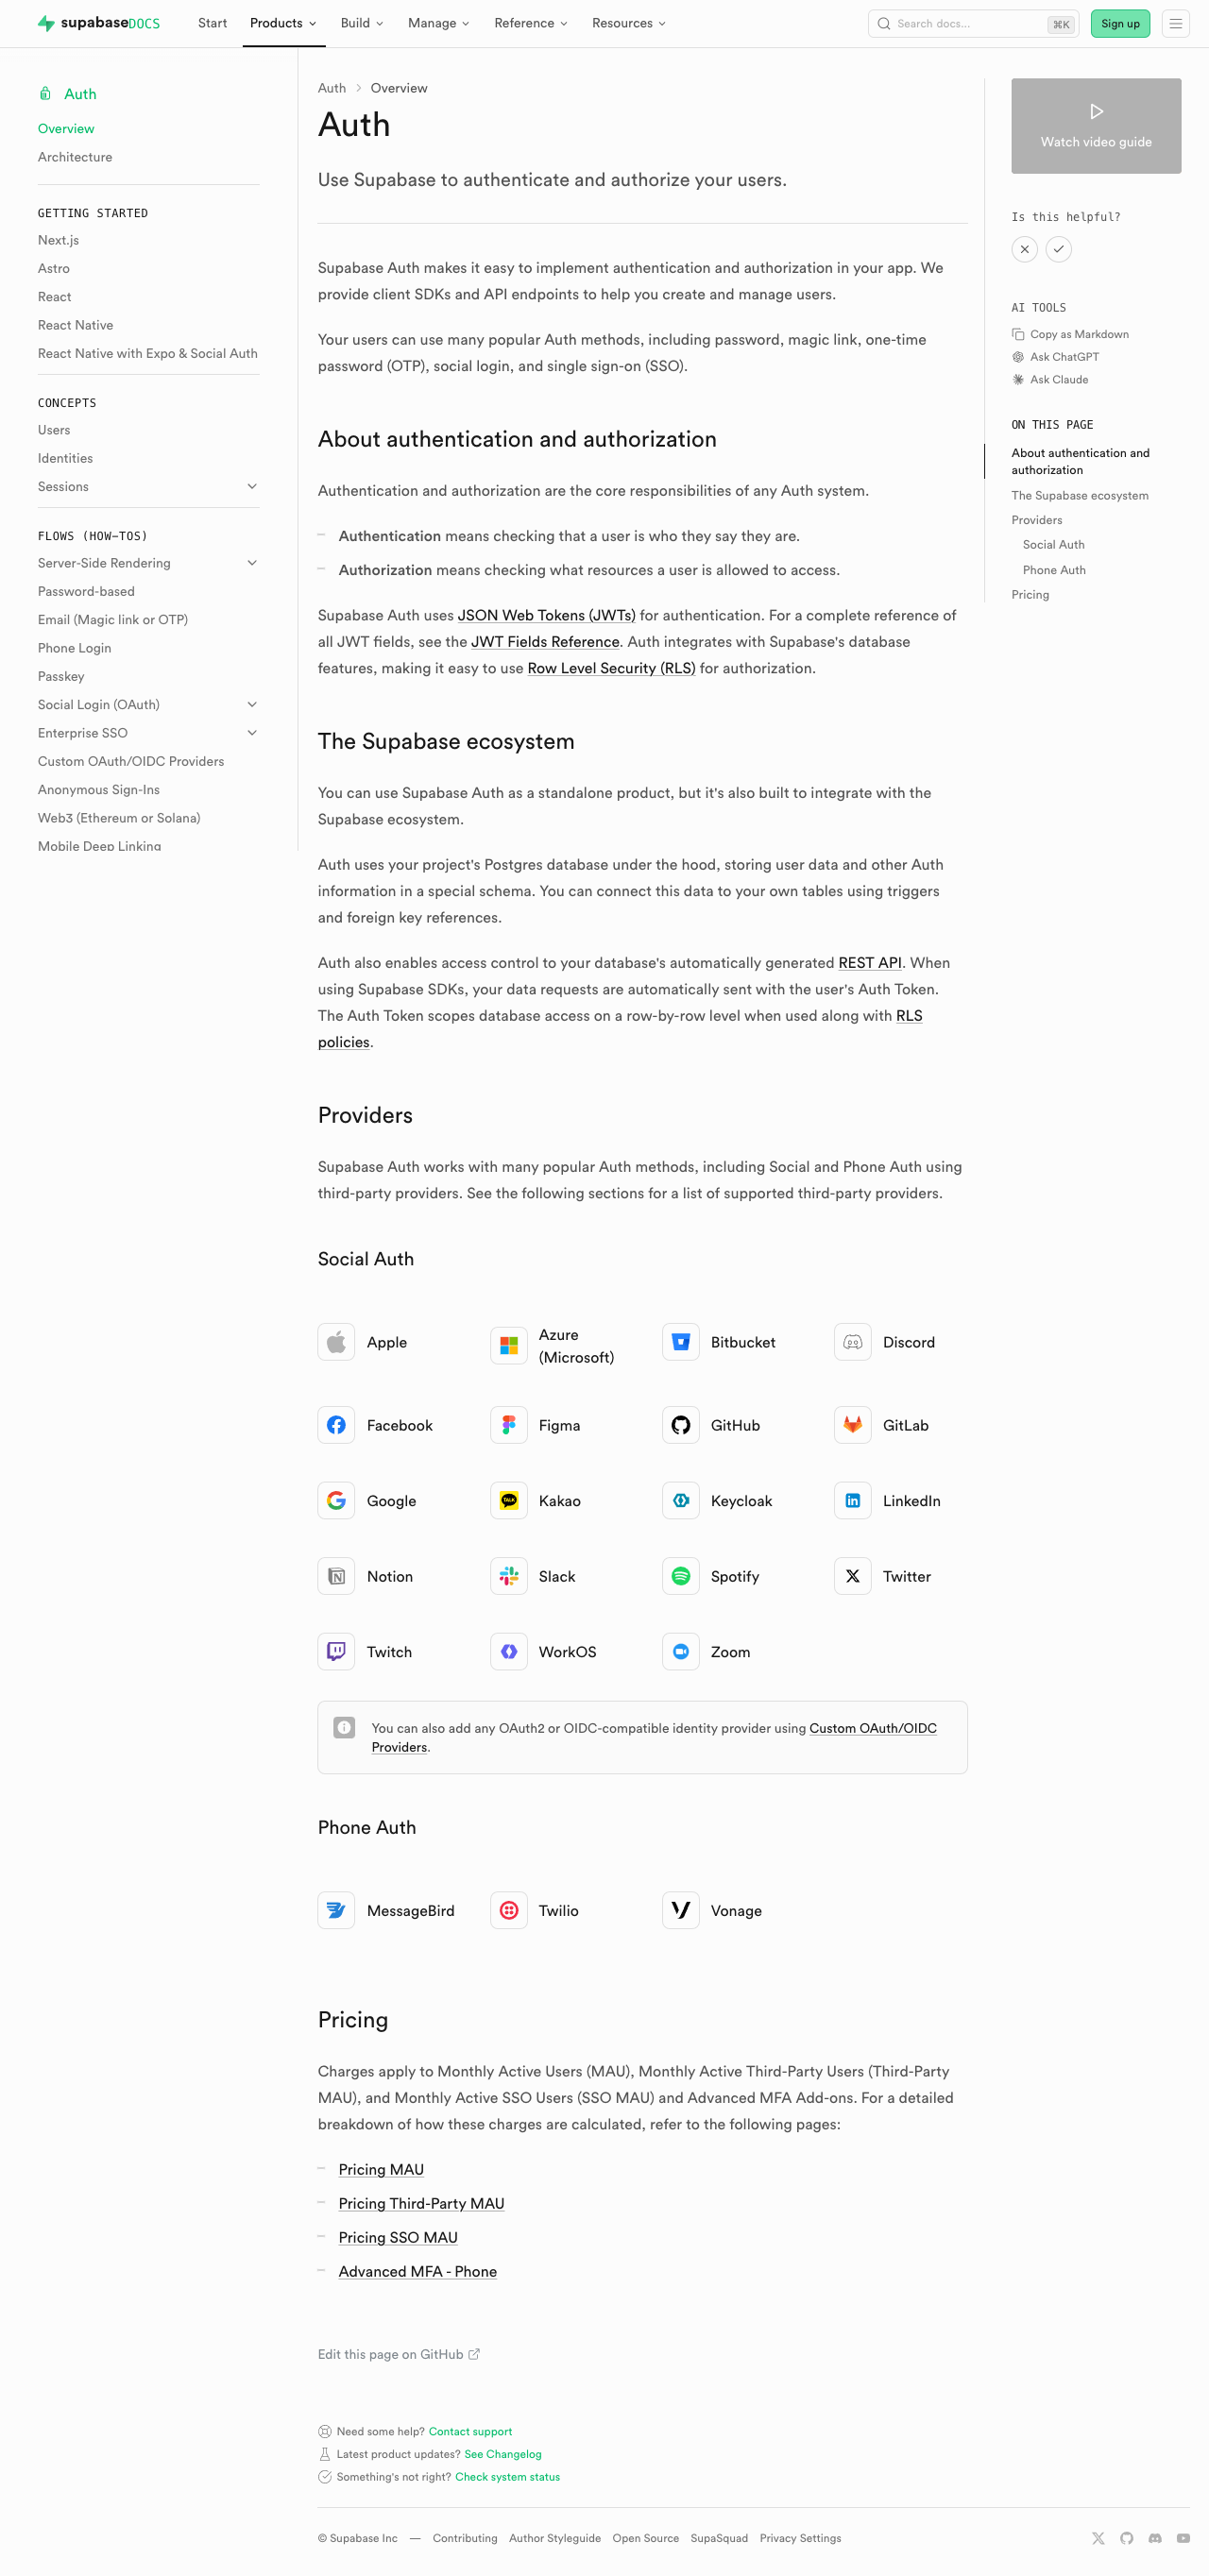 | 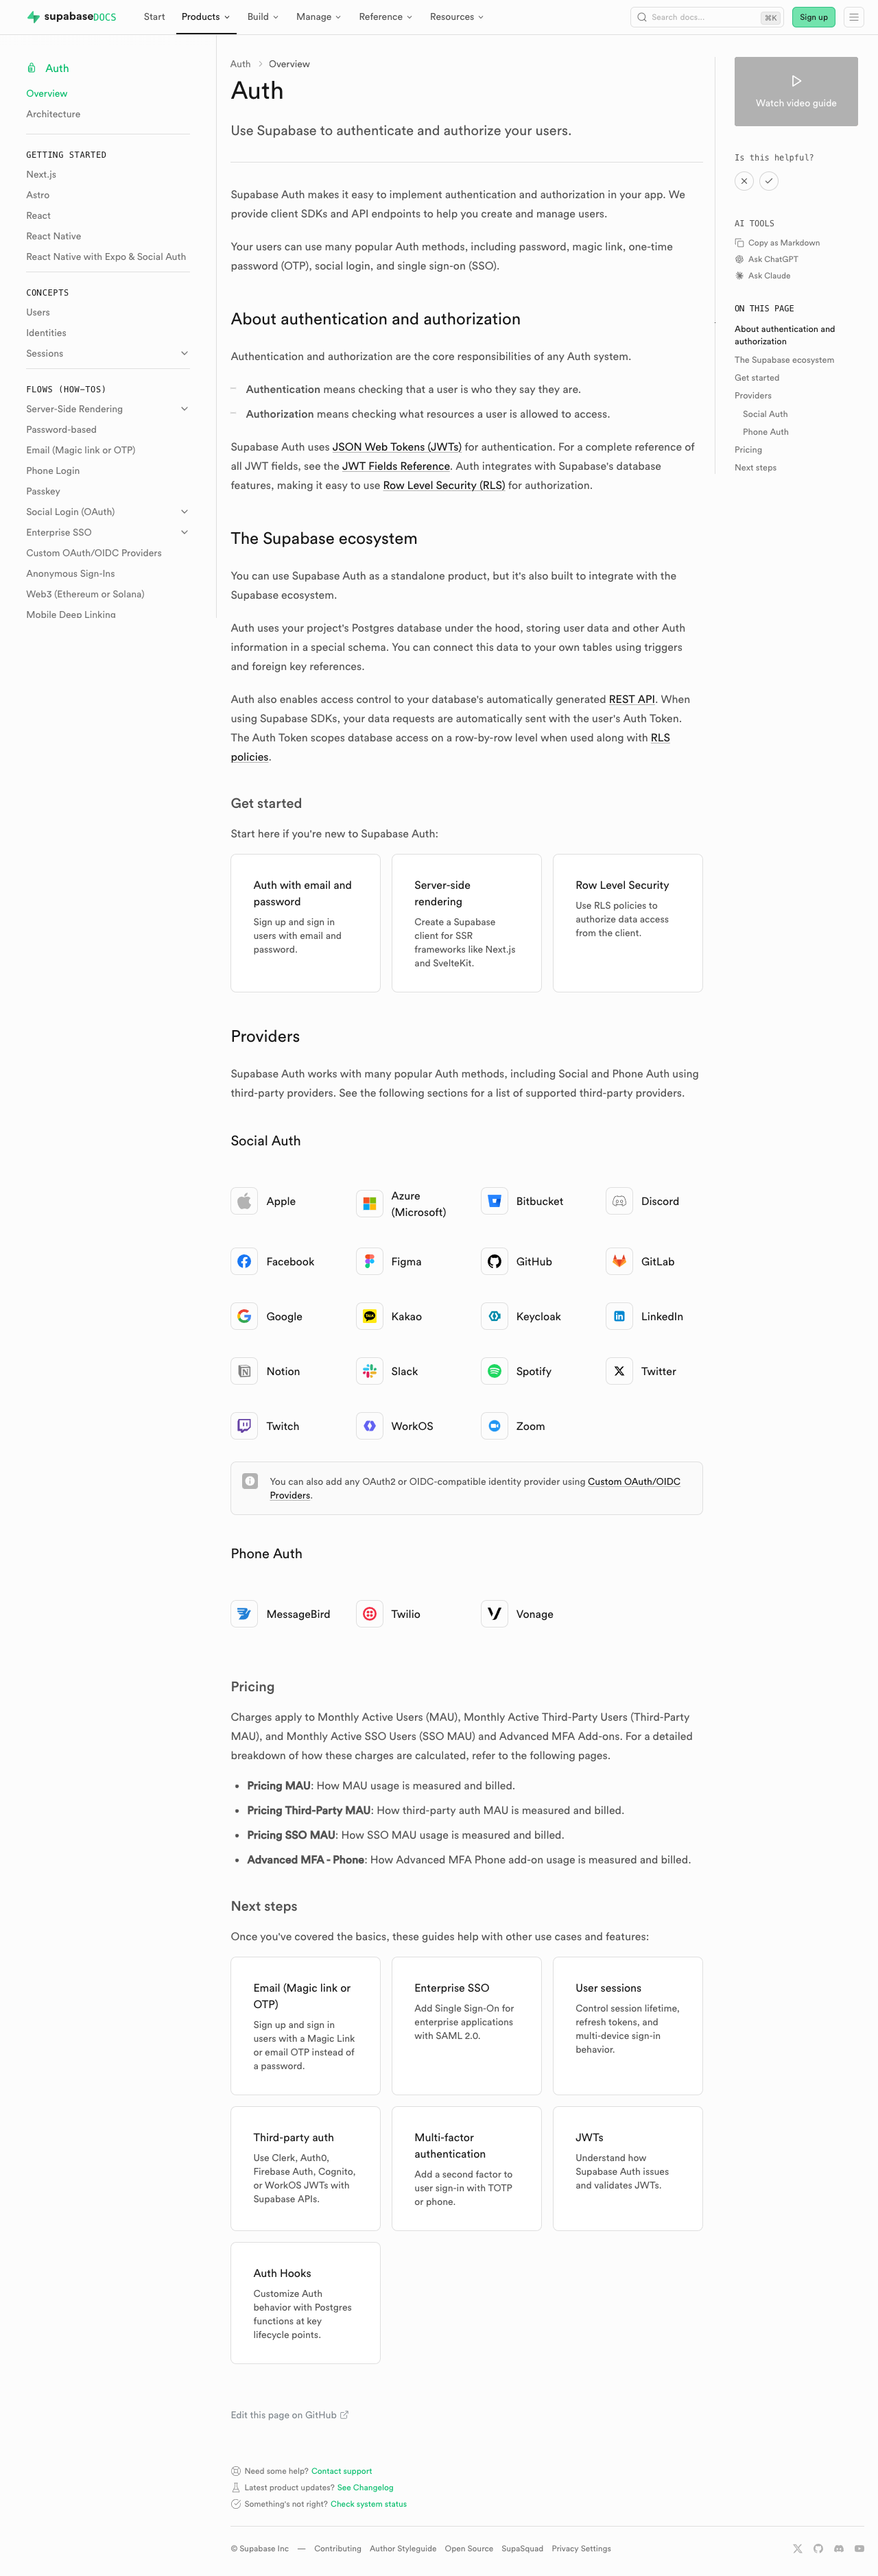 | #### Database overview | [Before (production)](https://supabase.com/docs/guides/database/overview) | [After (preview)](https://docs-git-fork-nrichers-nikrichers-docs-1032-sta-e2a8cb-supabase.vercel.app/docs/guides/database/overview) | | -------------------------------------------------------------------------------------------------------------------------------------------------- | -------------------------------------------------------------------------------------------------------------------------------------------------- | | 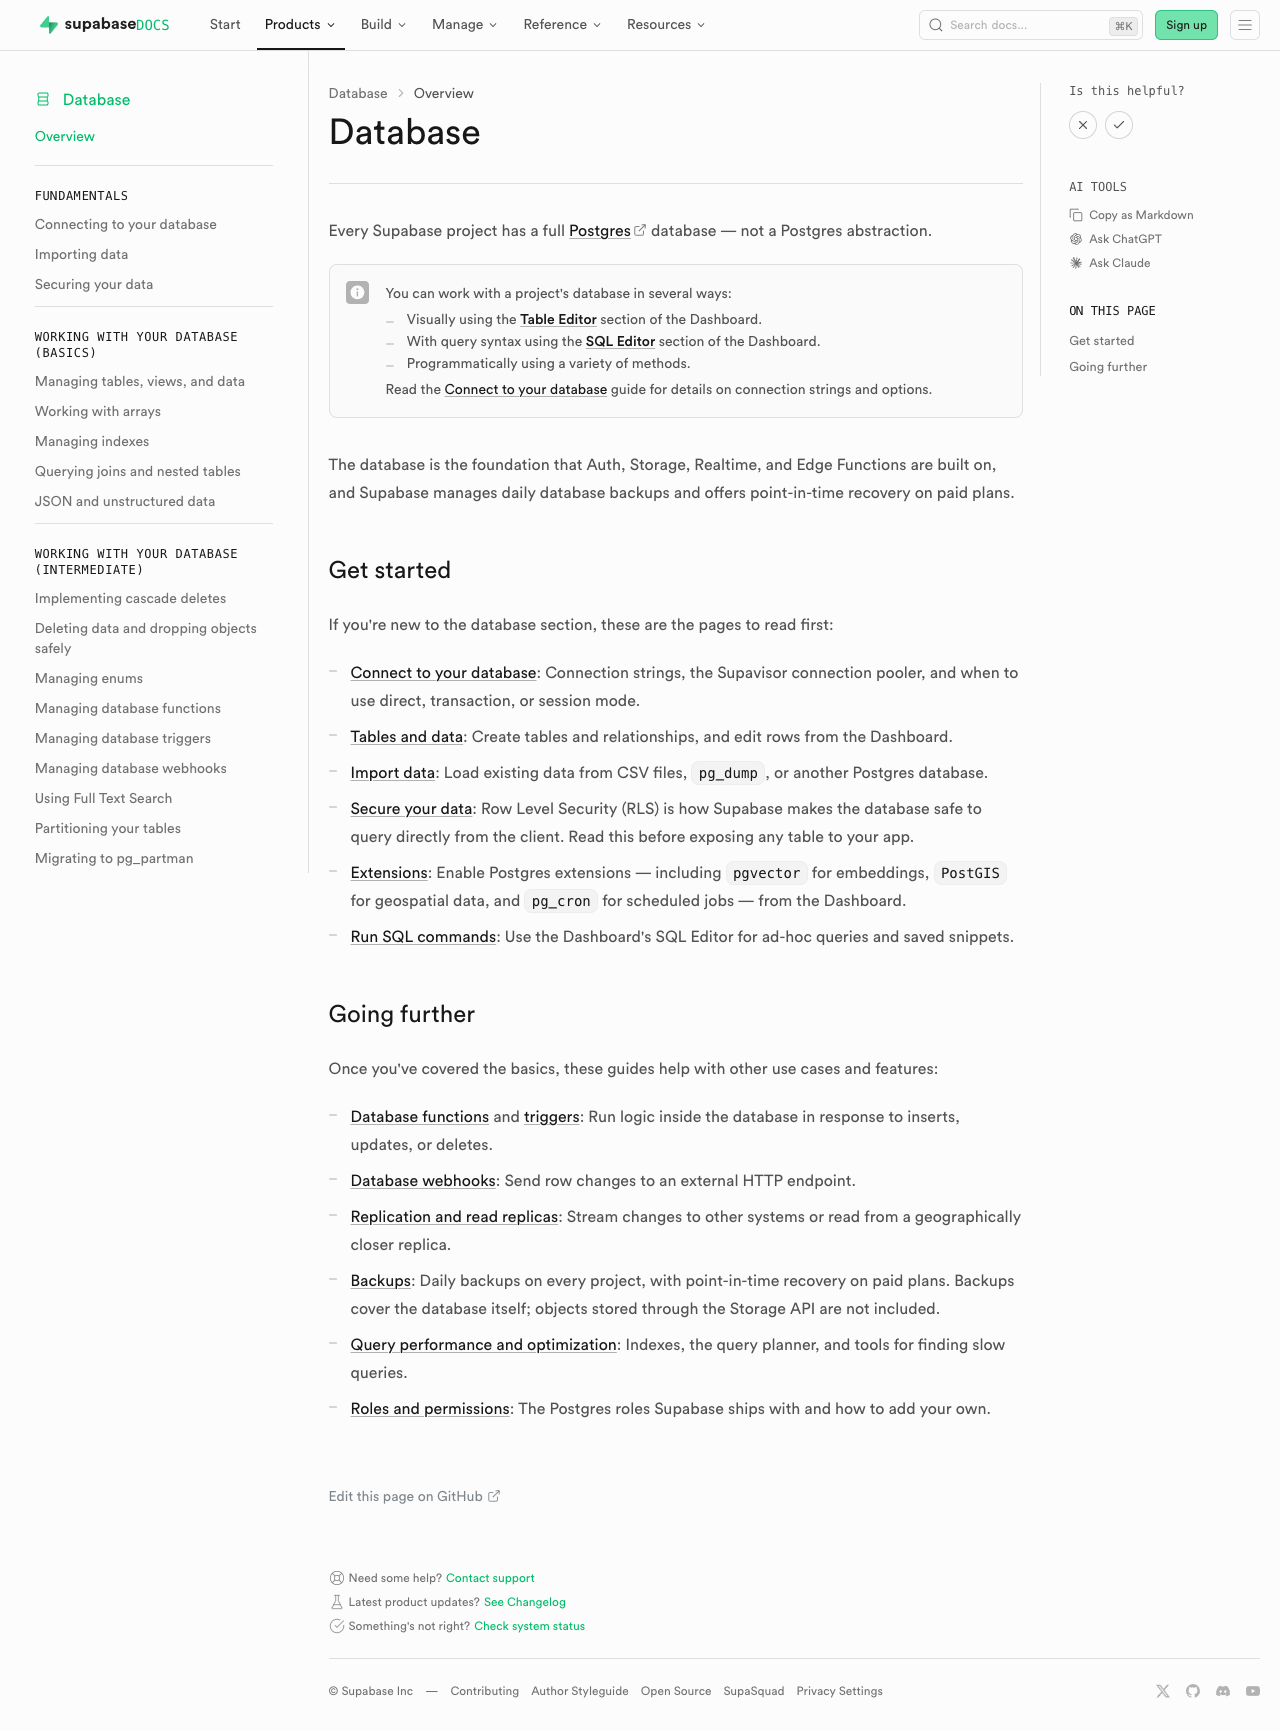 | 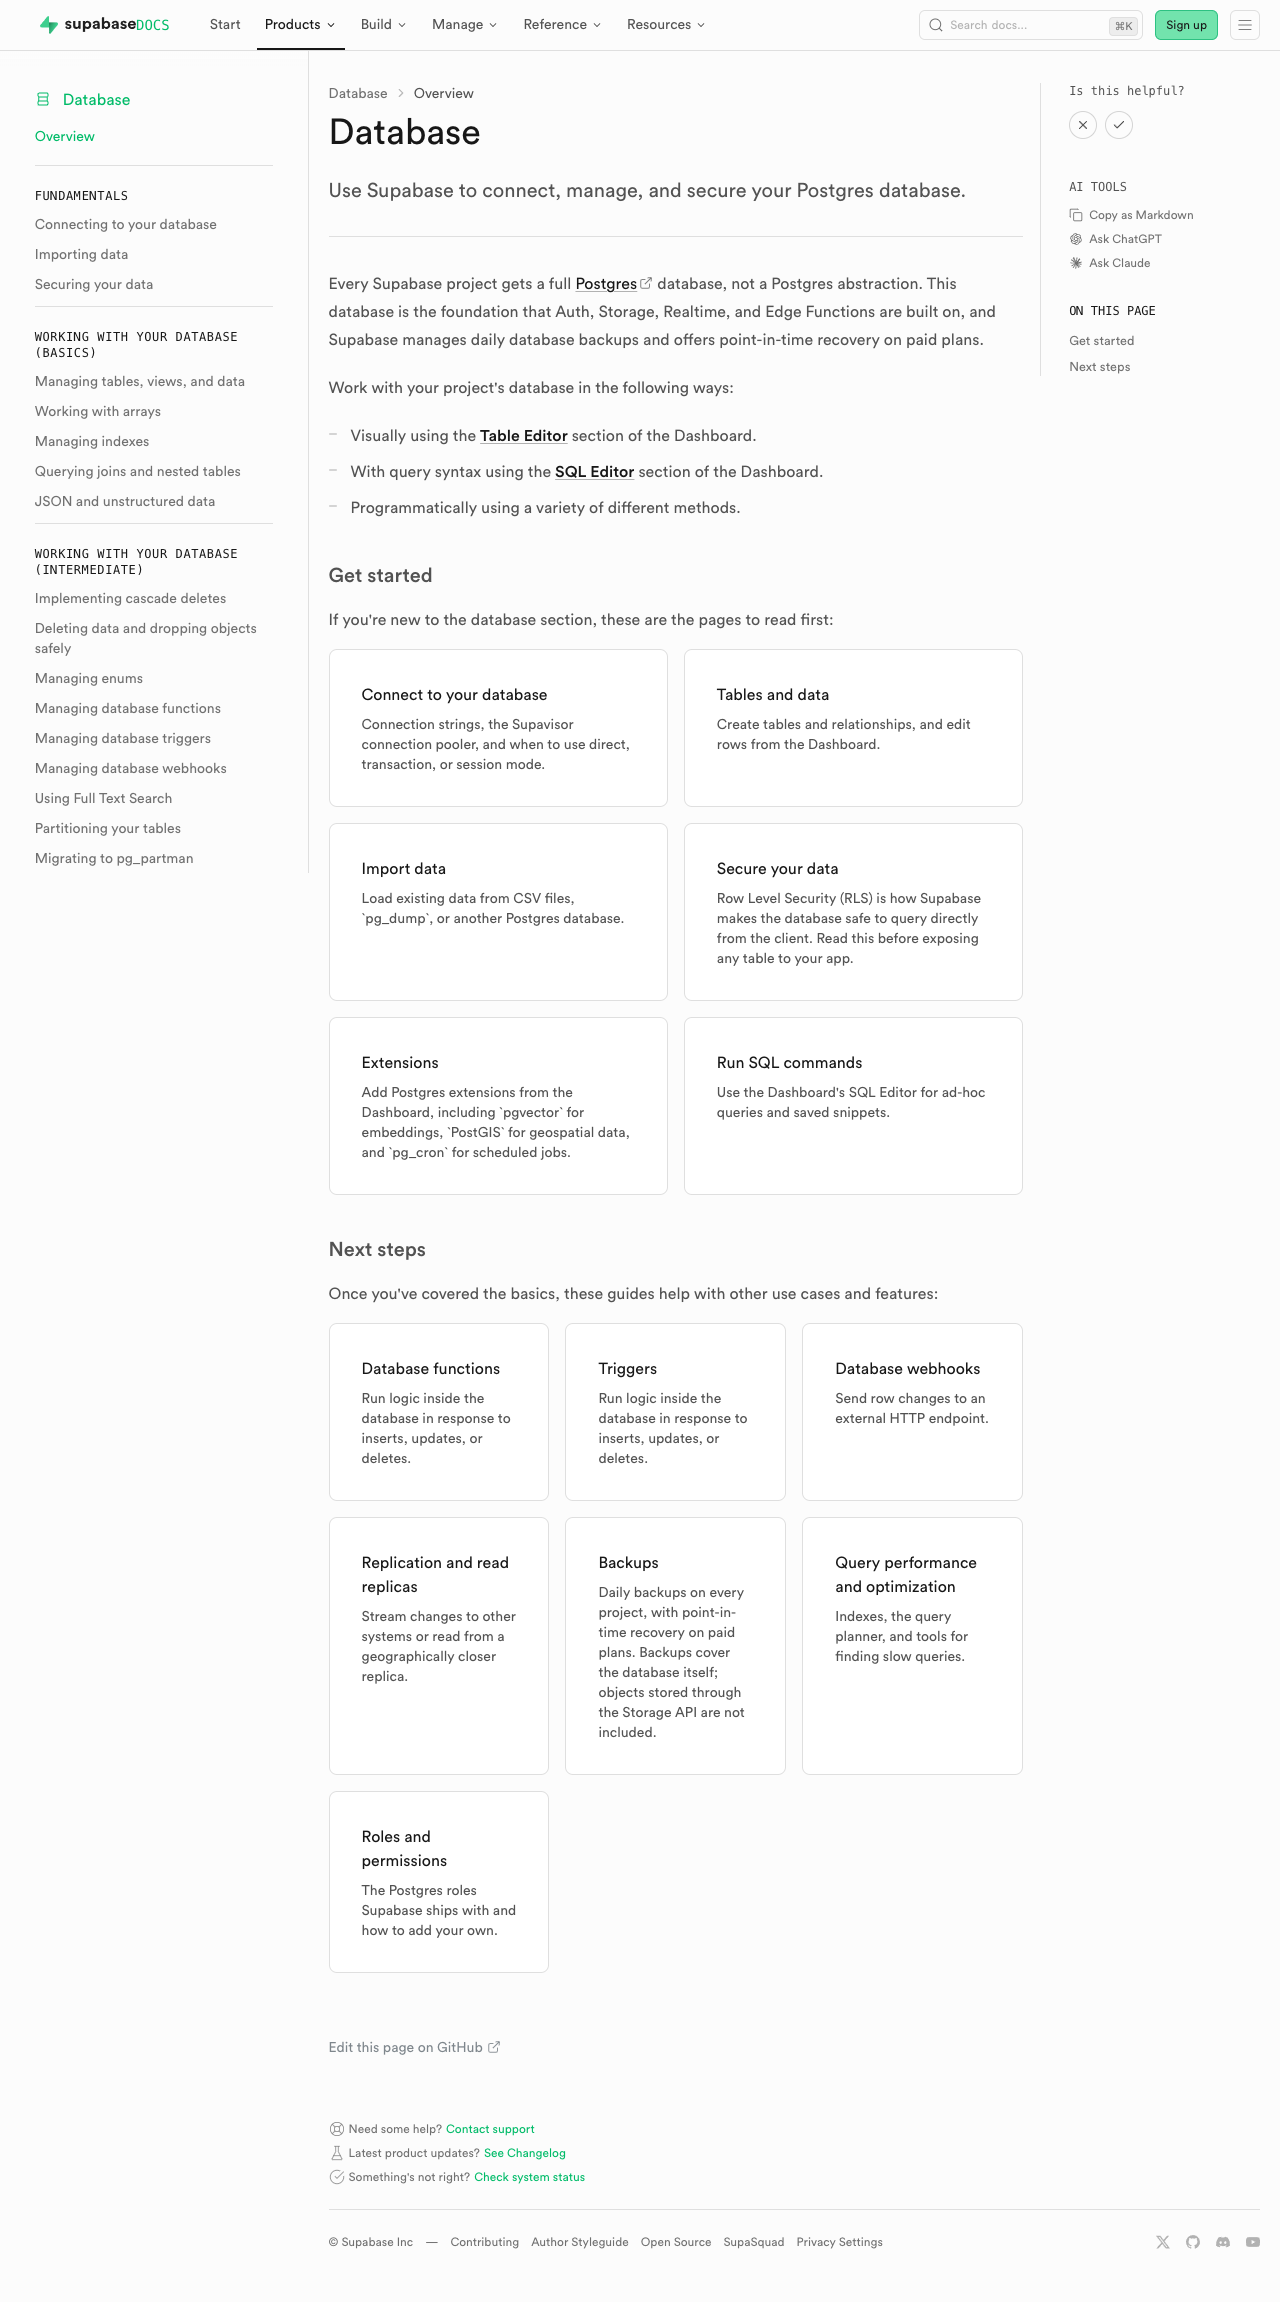 | #### Edge Functions | [Before (production)](https://supabase.com/docs/guides/functions) | [After (preview)](https://docs-git-fork-nrichers-nikrichers-docs-1032-sta-e2a8cb-supabase.vercel.app/docs/guides/functions) | | -------------------------------------------------------------------------------------------------------------------------------------------- | -------------------------------------------------------------------------------------------------------------------------------------------- | | 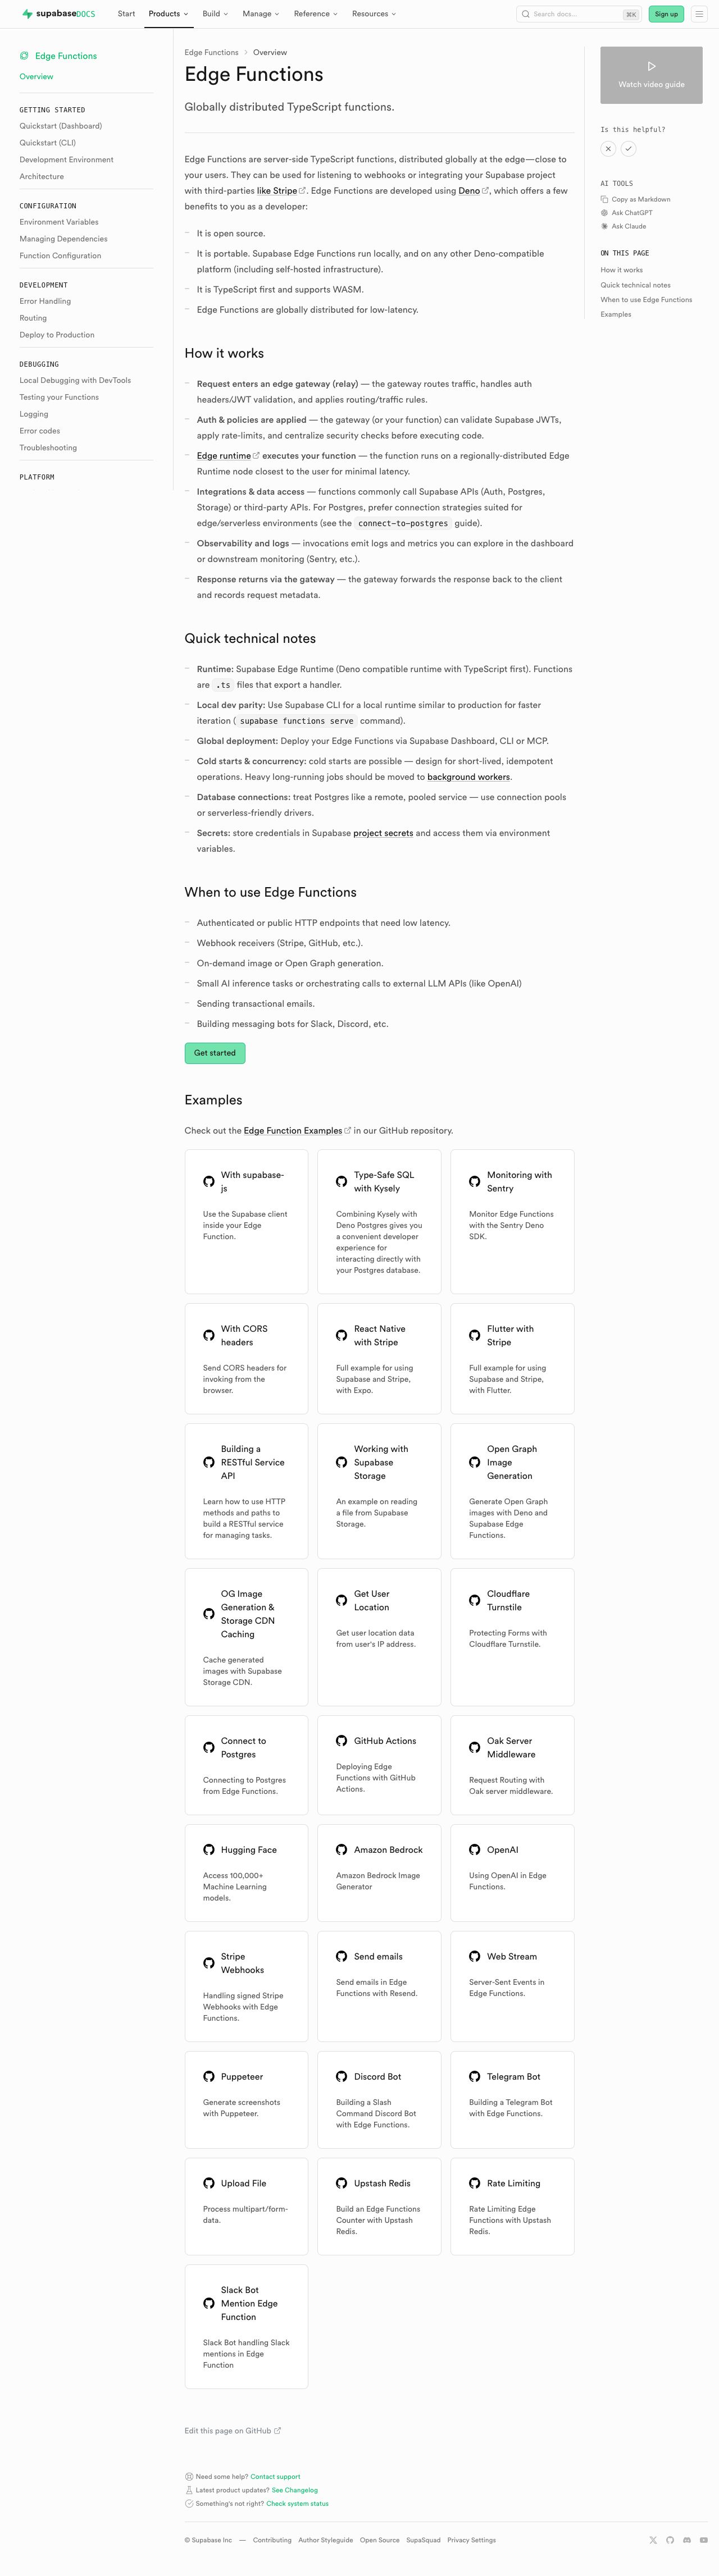 | 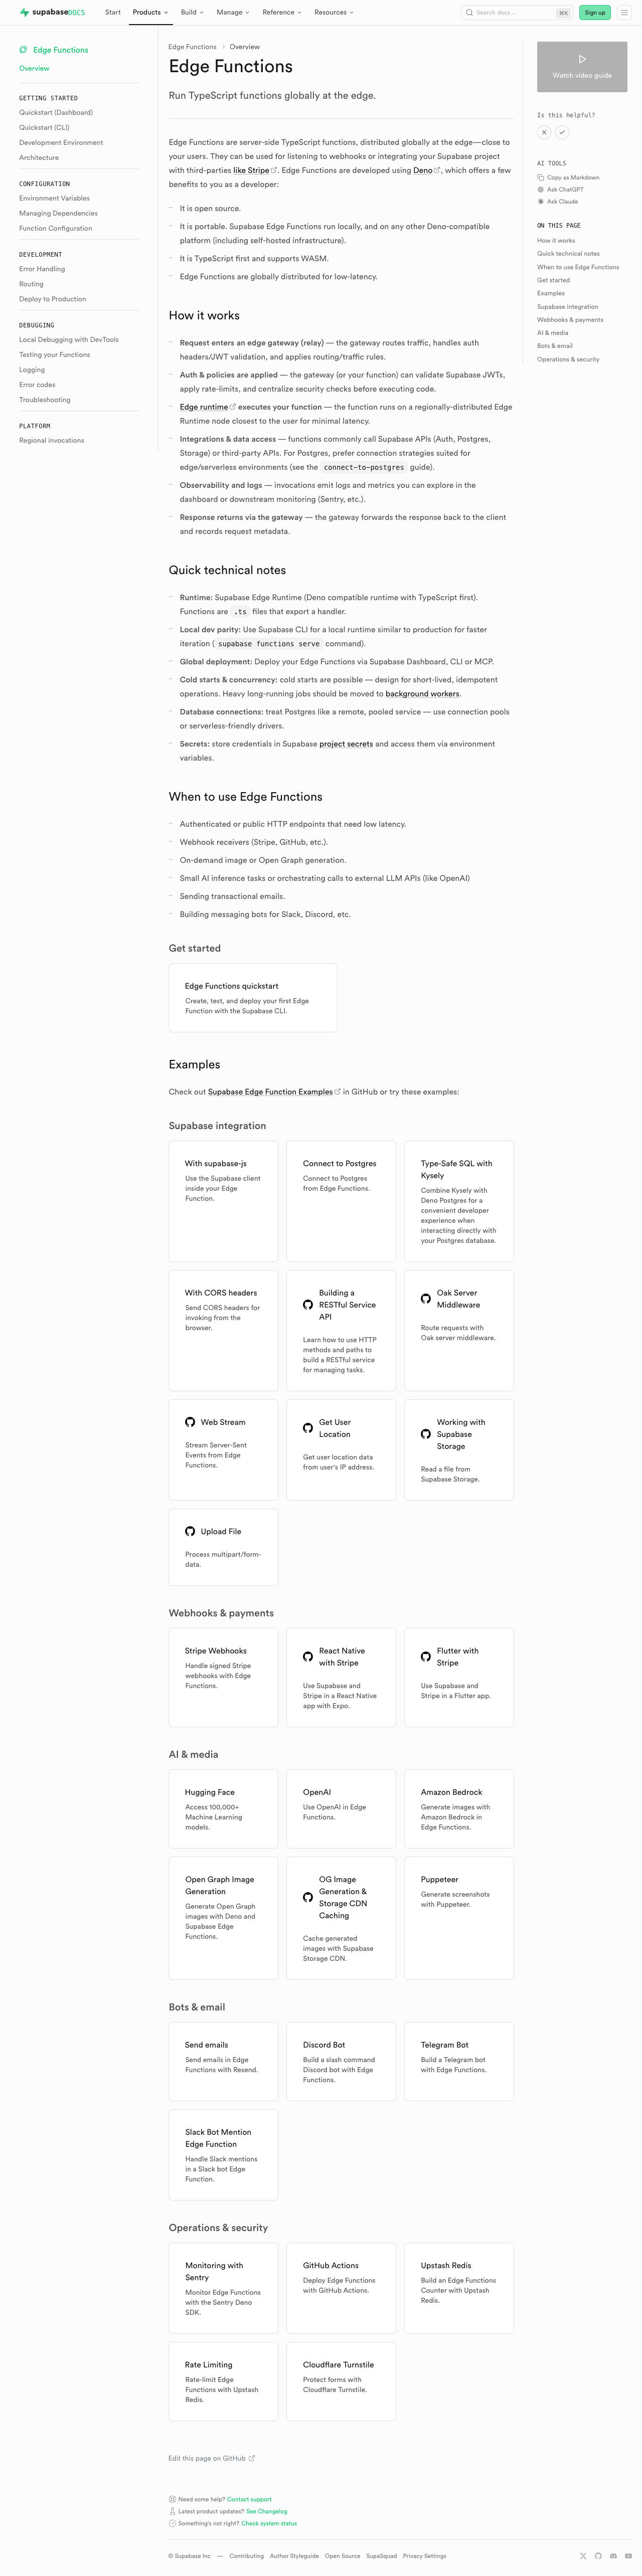 | #### Storage | [Before (production)](https://supabase.com/docs/guides/storage) | [After (preview)](https://docs-git-fork-nrichers-nikrichers-docs-1032-sta-e2a8cb-supabase.vercel.app/docs/guides/storage) | | ---------------------------------------------------------------------------------------------------------------------------------------- | ---------------------------------------------------------------------------------------------------------------------------------------- | | 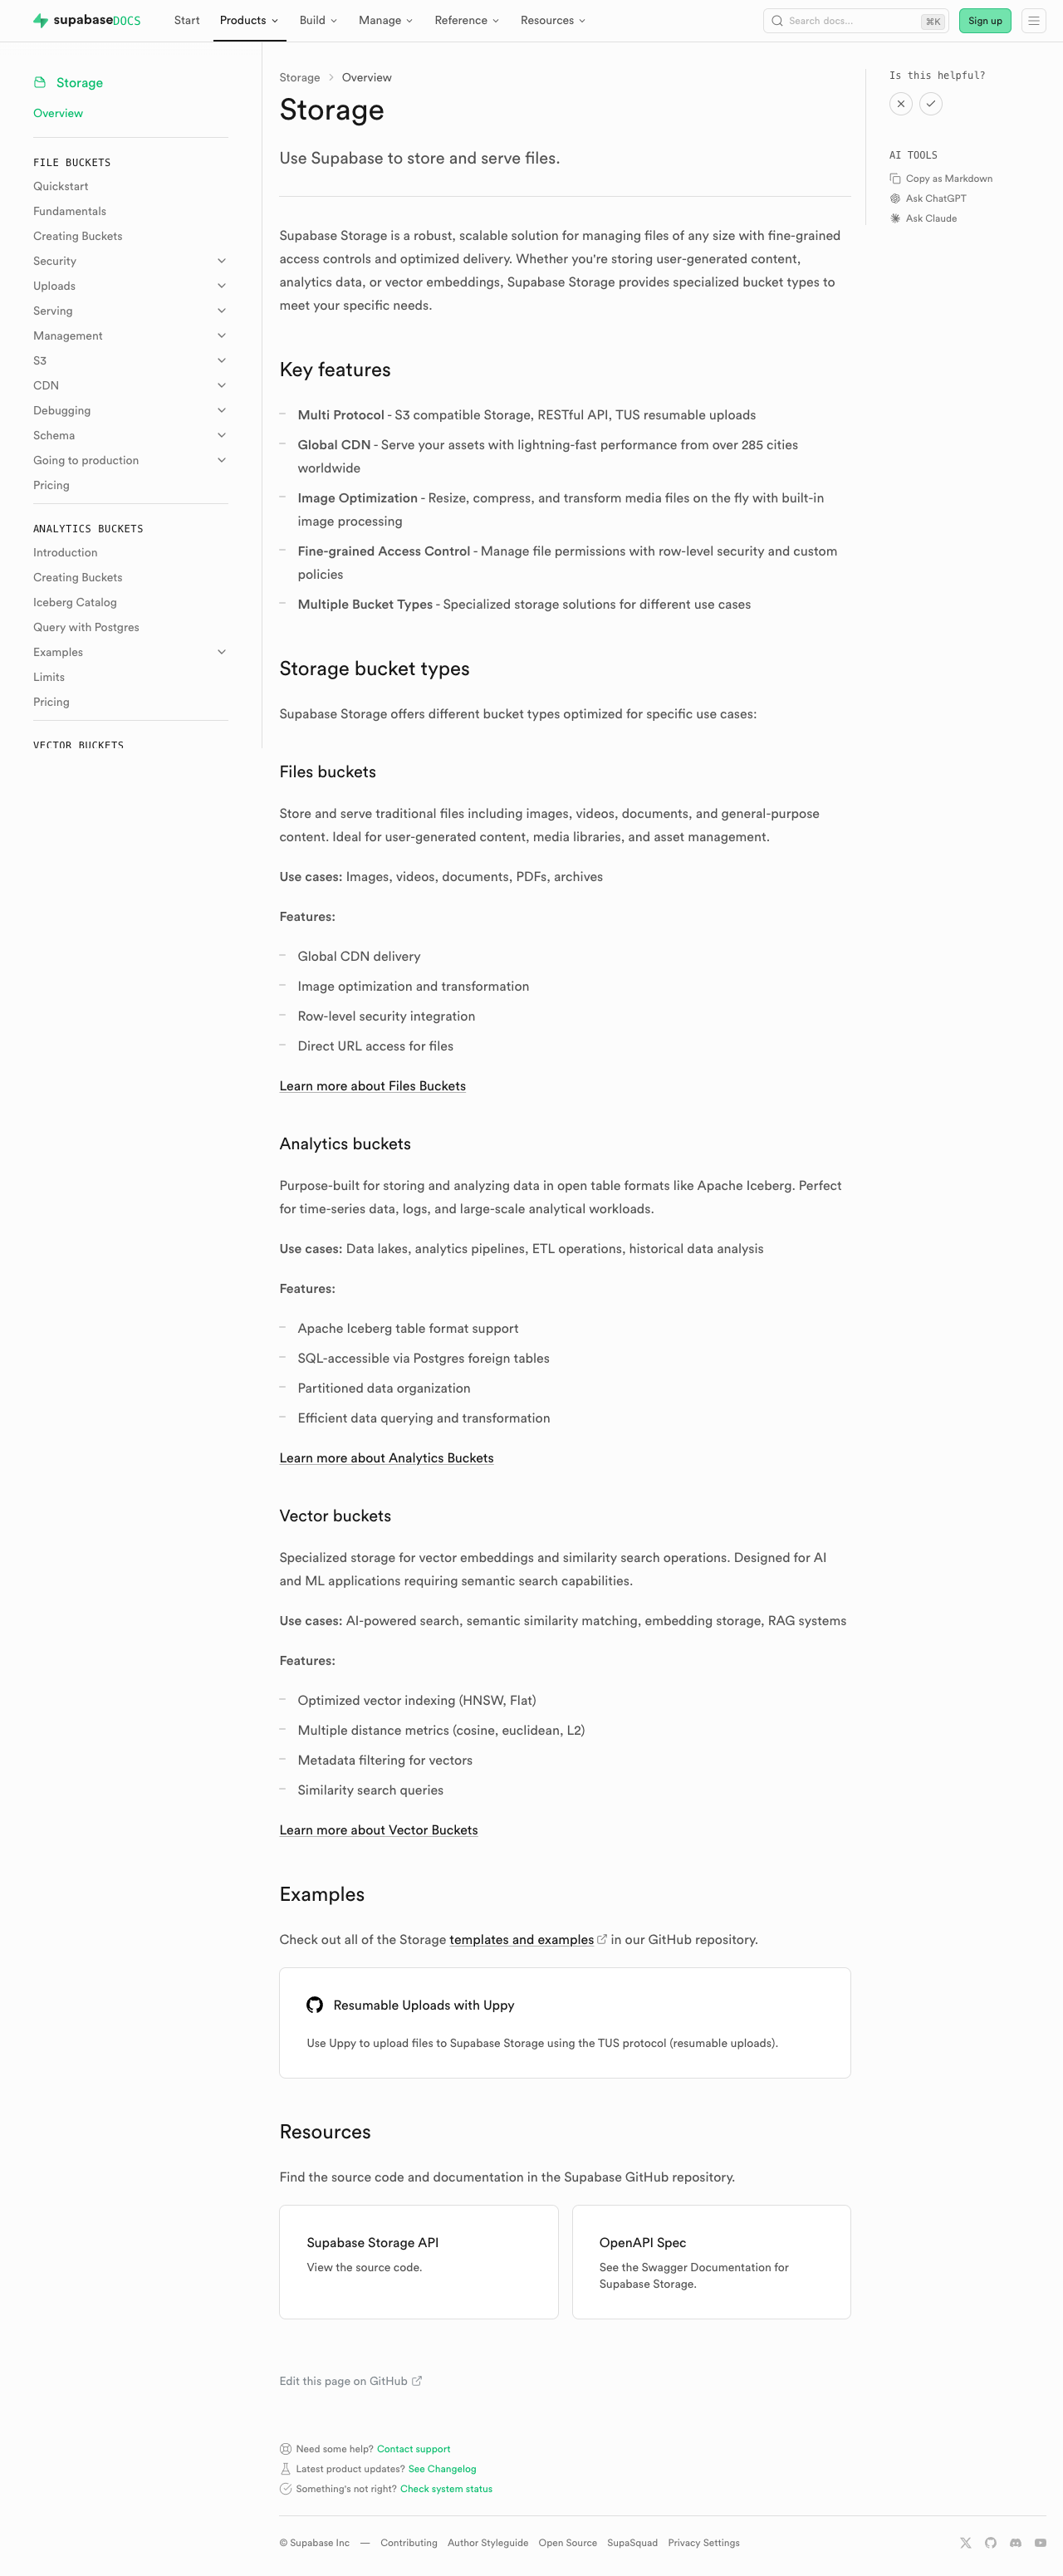 | 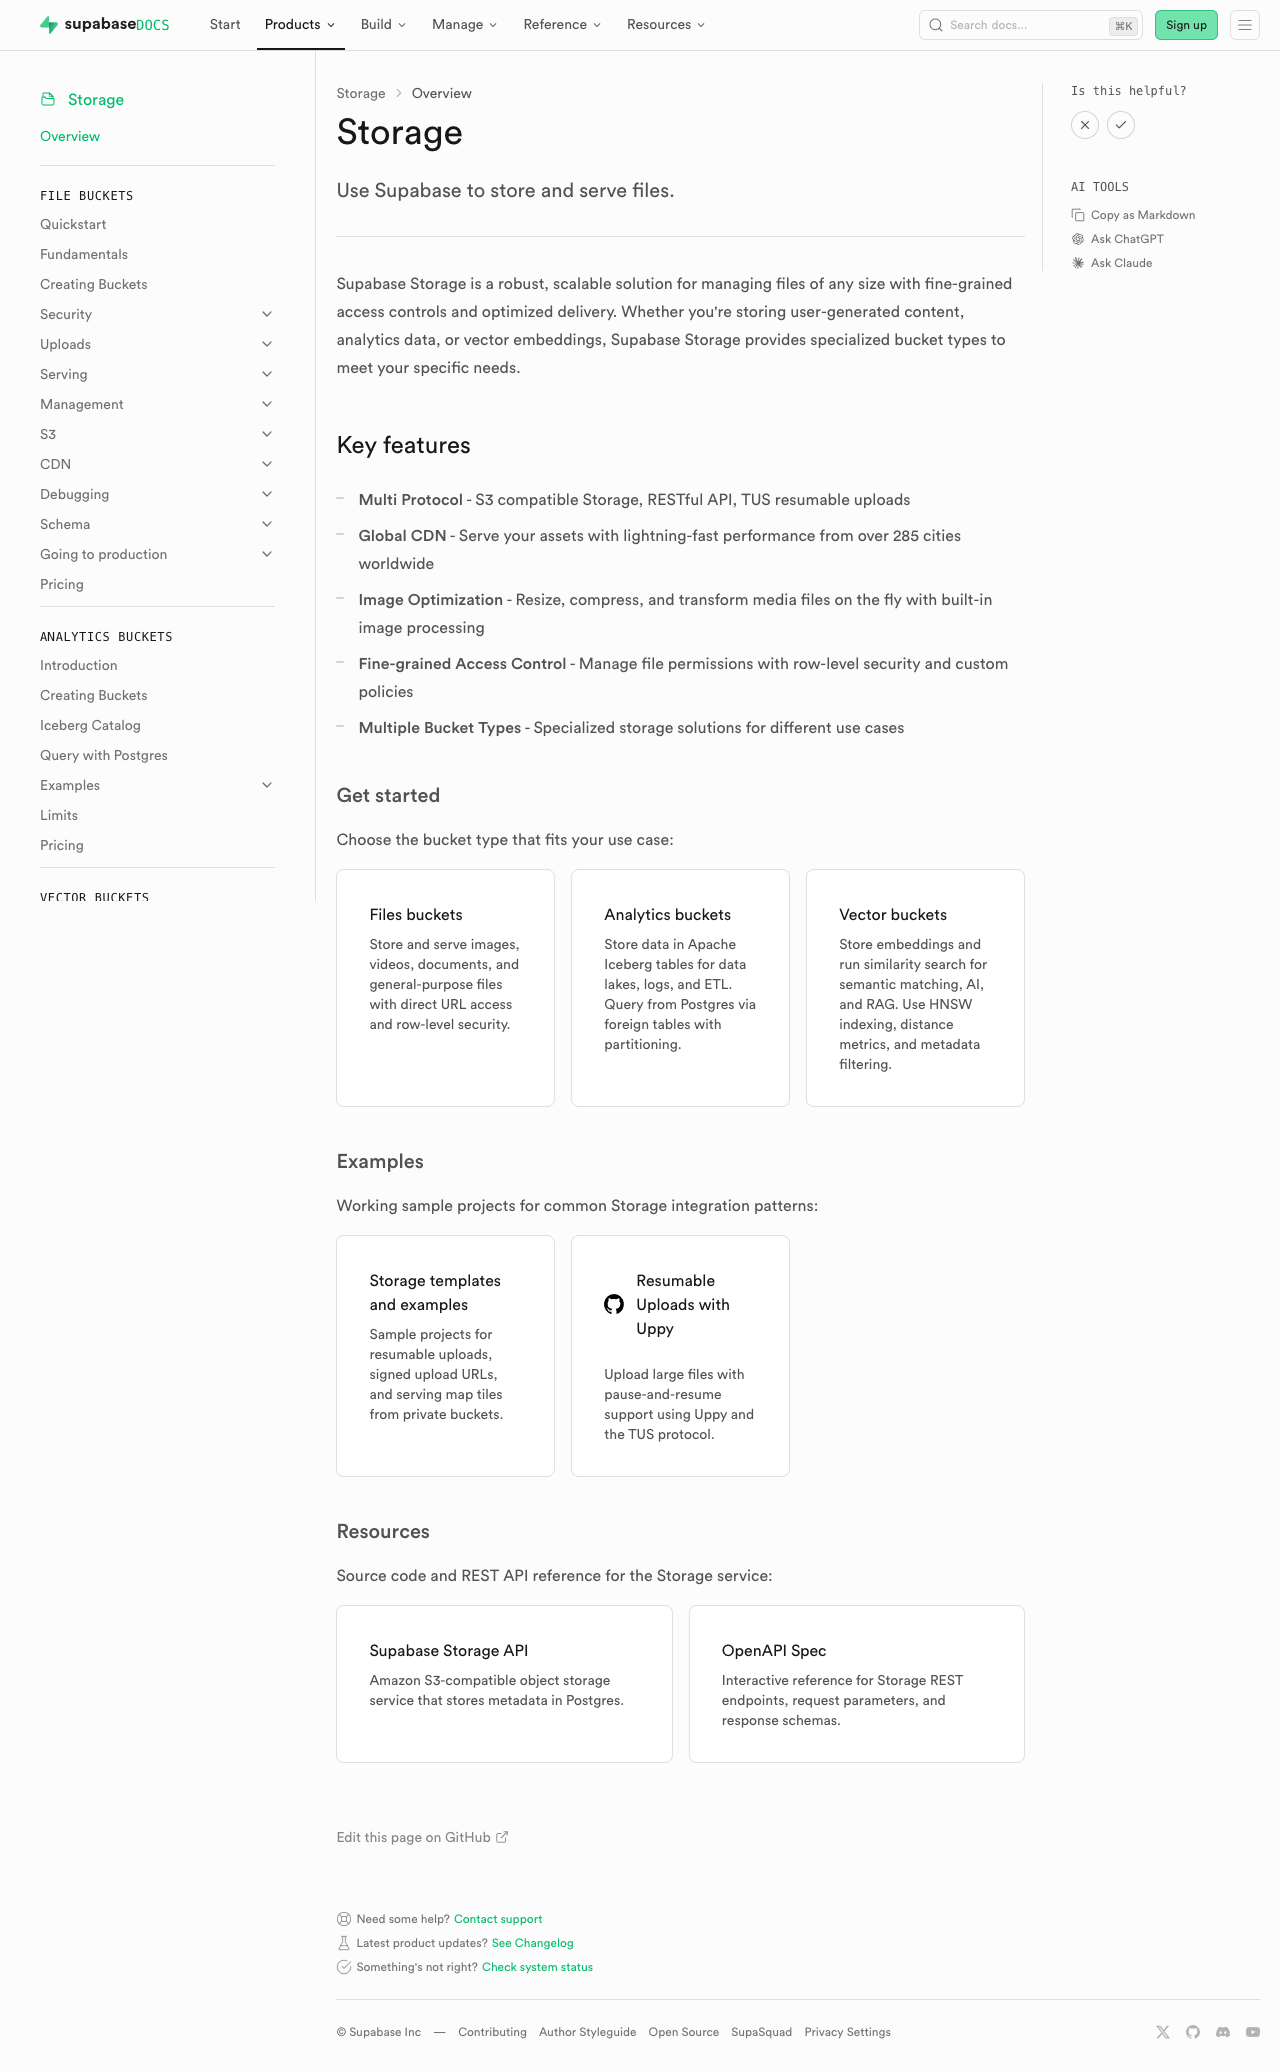 | #### Realtime | [Before (production)](https://supabase.com/docs/guides/realtime) | [After (preview)](https://docs-git-fork-nrichers-nikrichers-docs-1032-sta-e2a8cb-supabase.vercel.app/docs/guides/realtime) | | ------------------------------------------------------------------------------------------------------------------------------------------- | ------------------------------------------------------------------------------------------------------------------------------------------- | | 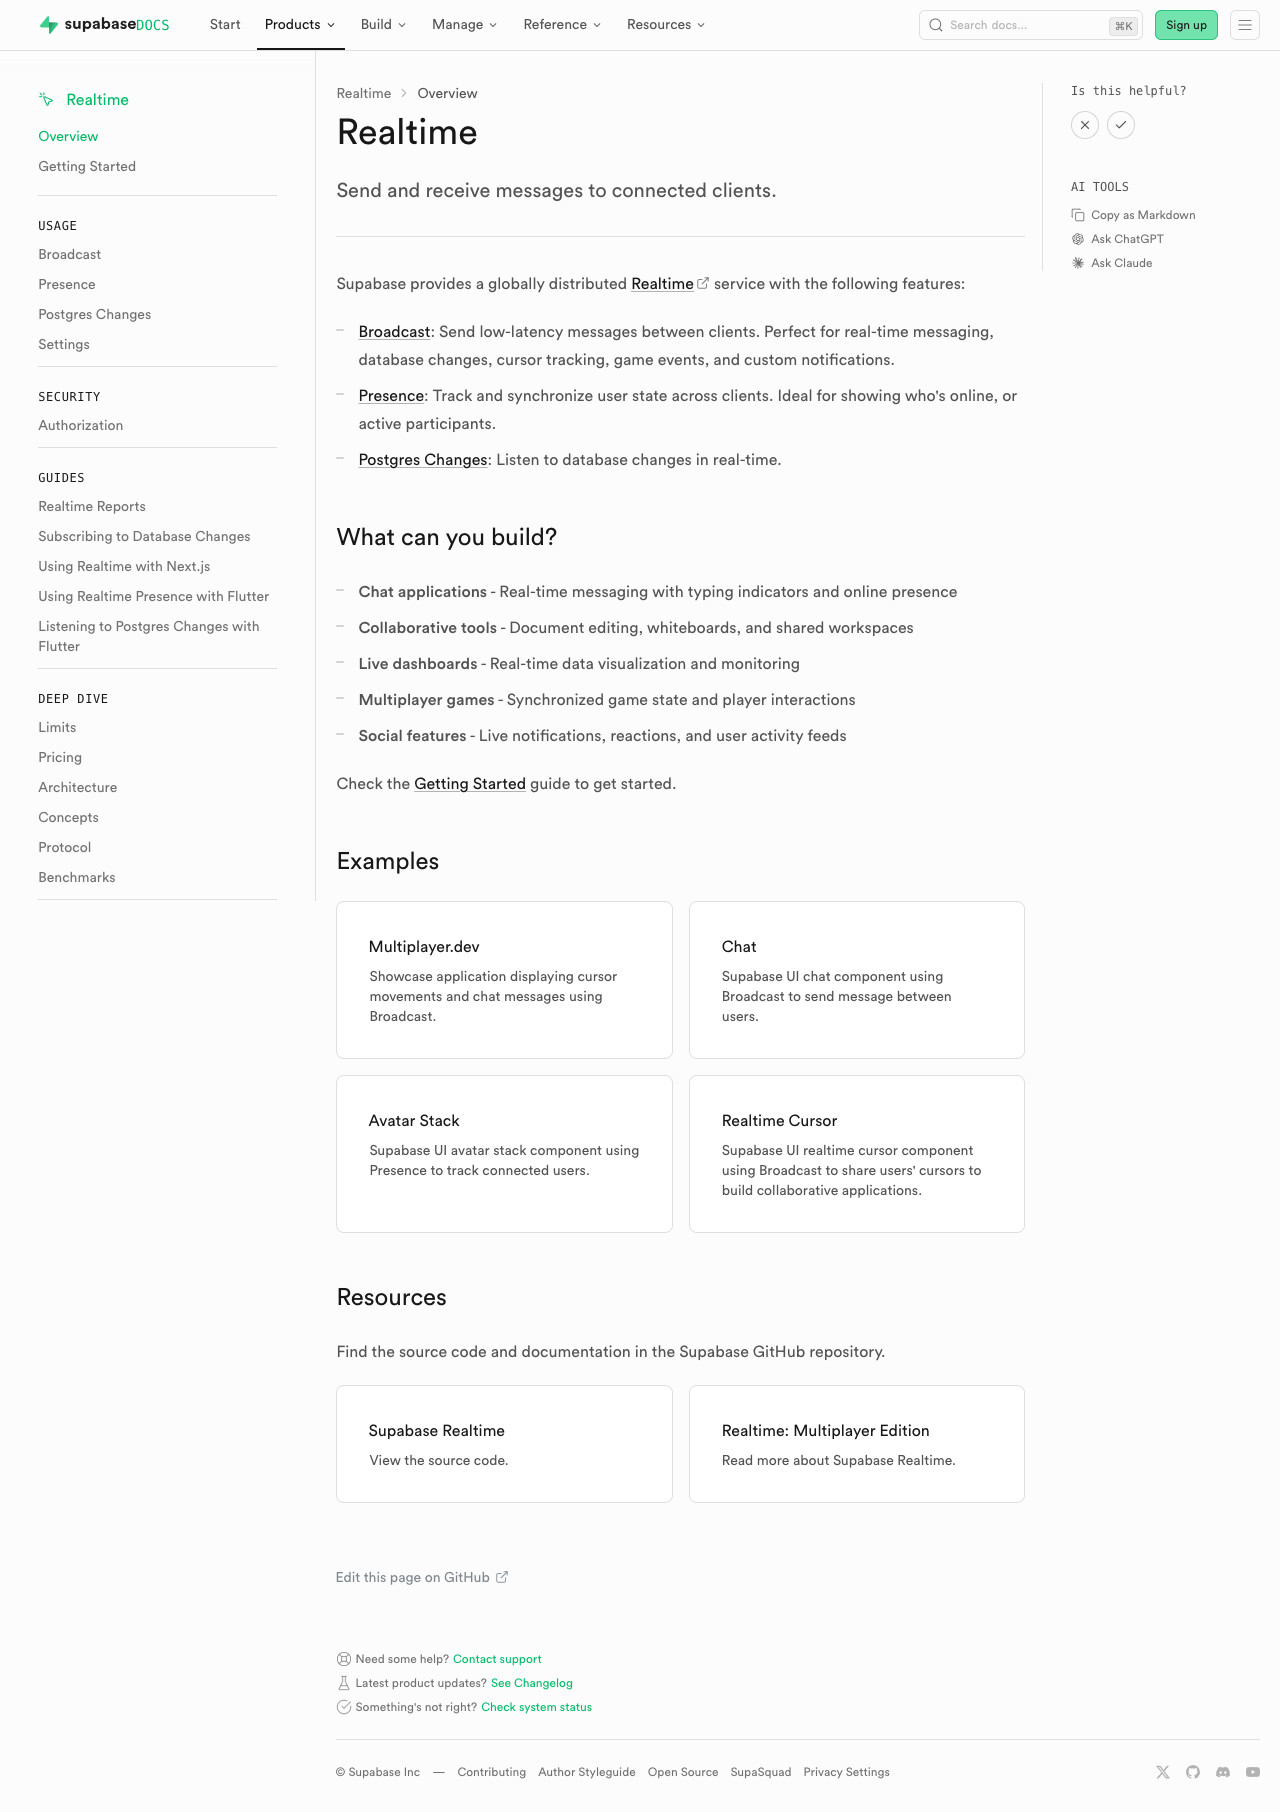 | 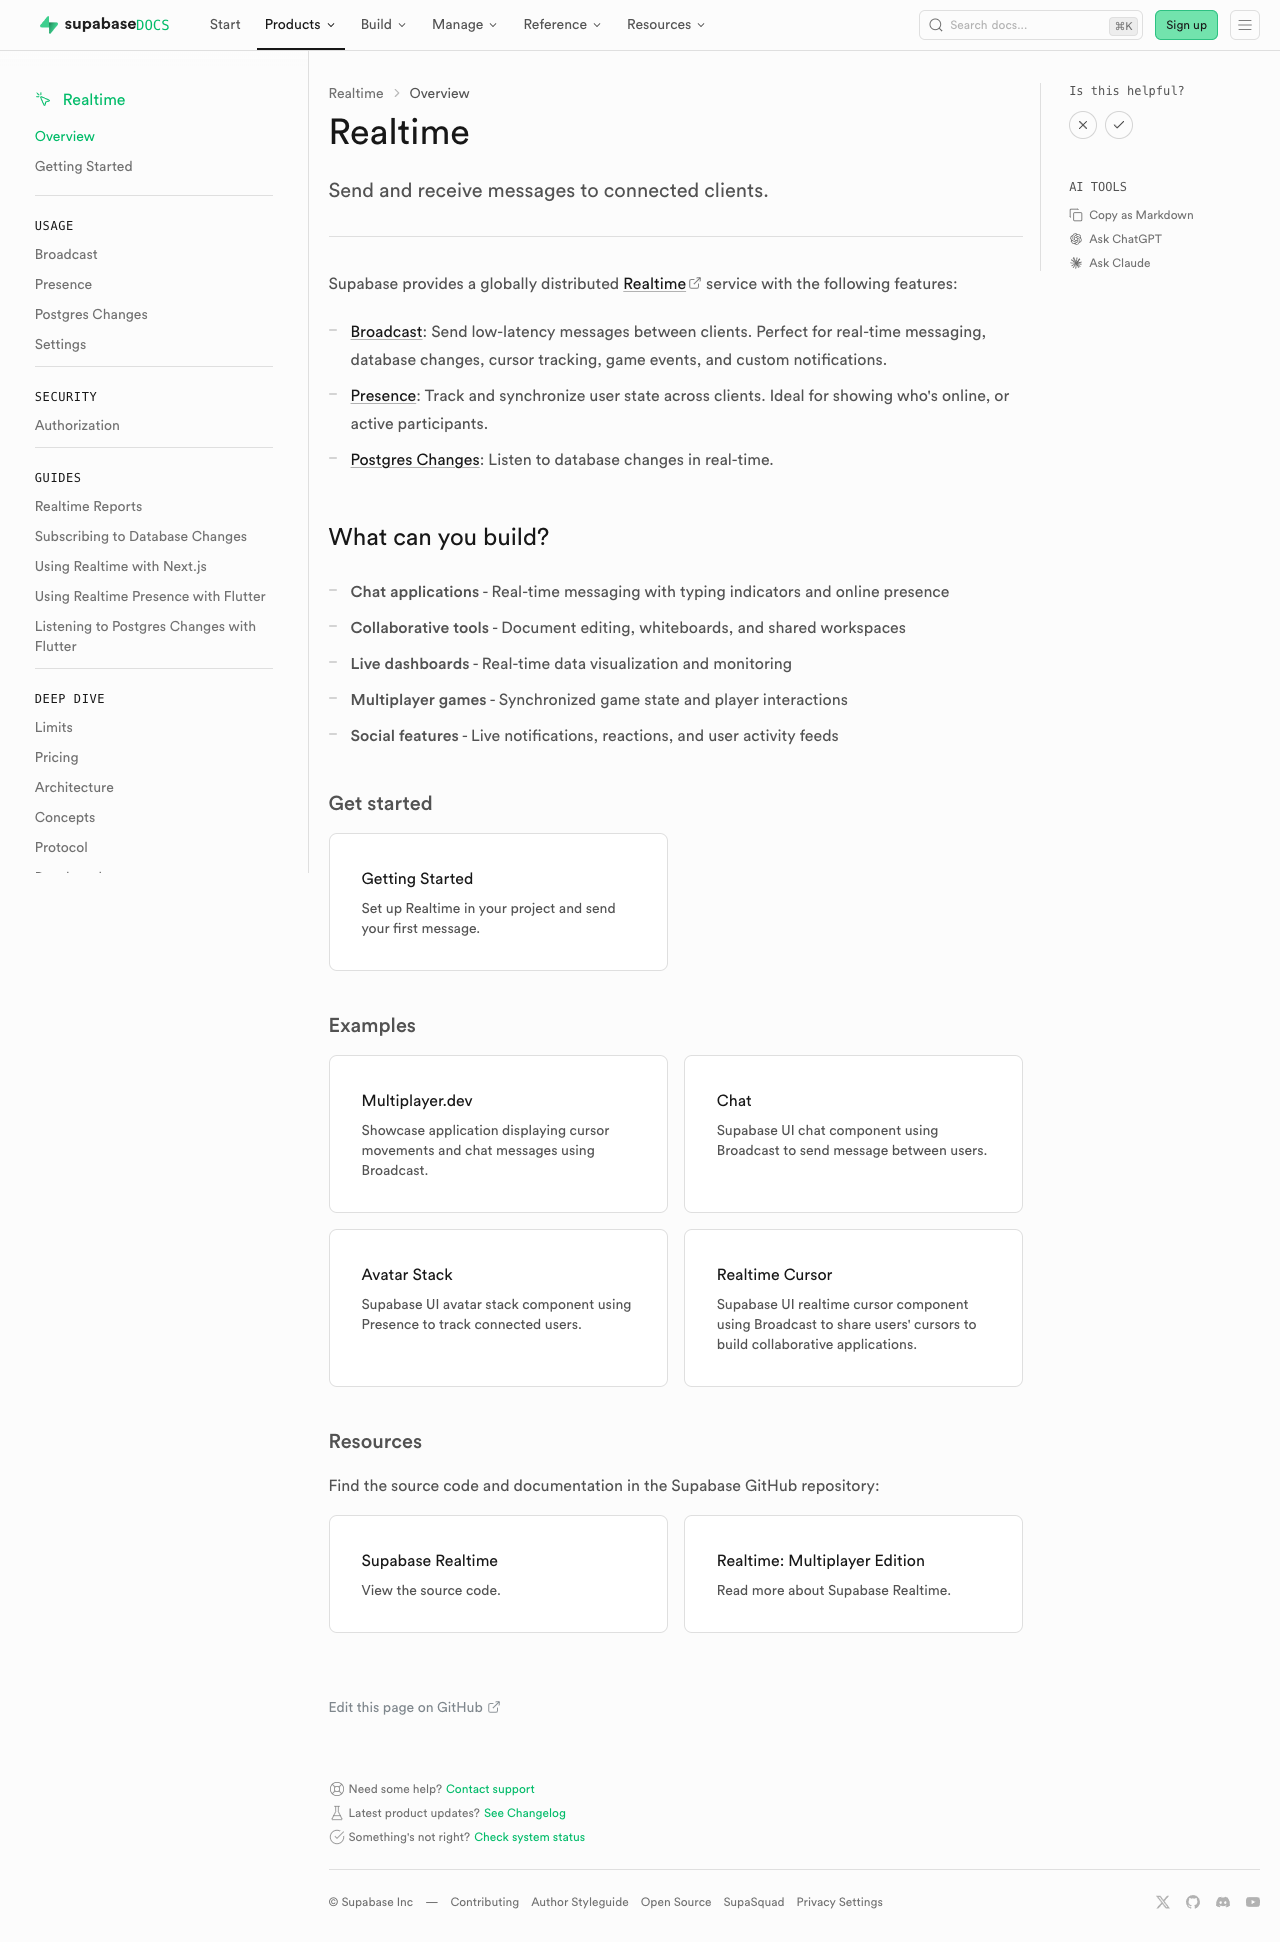 | #### Getting Started (partial migration for demoing) | [Before (production)](https://supabase.com/docs/guides/getting-started) | [After (preview)](https://docs-git-fork-nrichers-nikrichers-docs-1032-sta-e2a8cb-supabase.vercel.app/docs/guides/getting-started) | | ------------------------------------------------------------------------------------------------------------------------------------------------------ | ------------------------------------------------------------------------------------------------------------------------------------------------------ | | 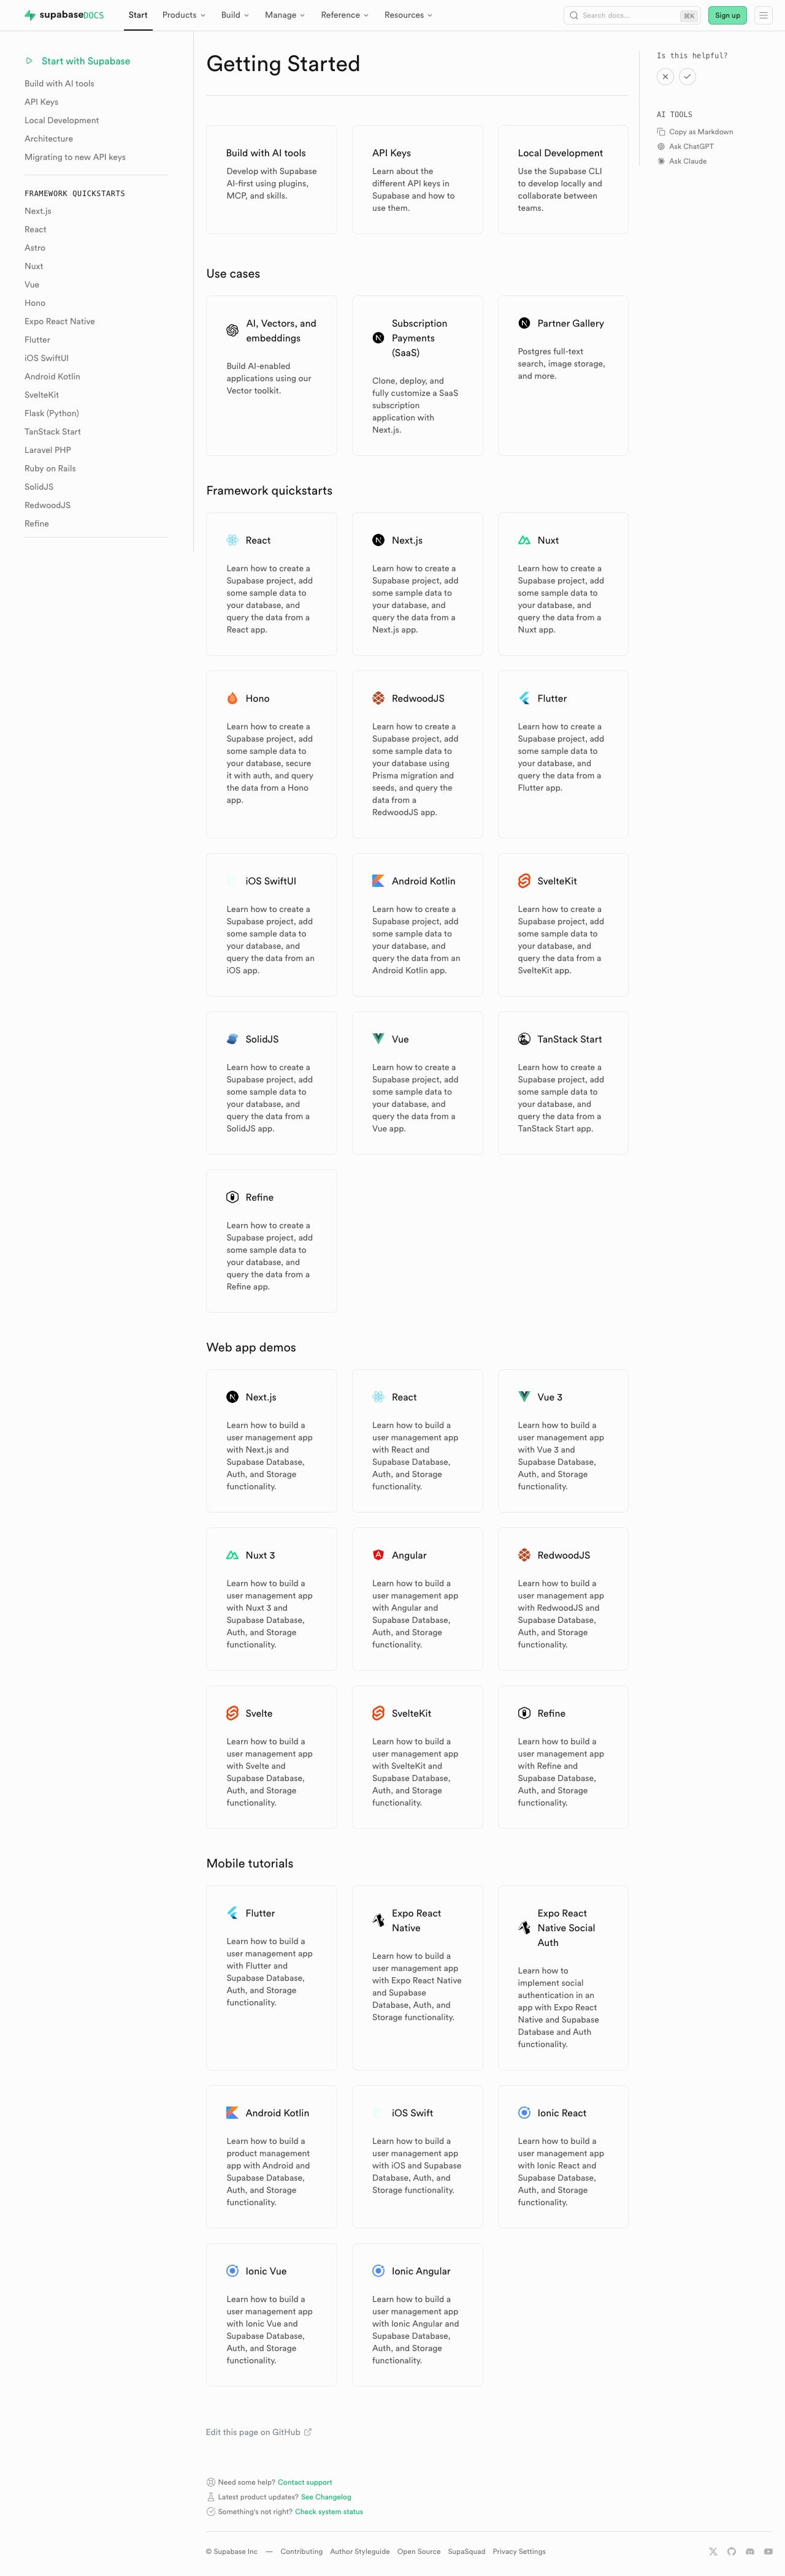 | 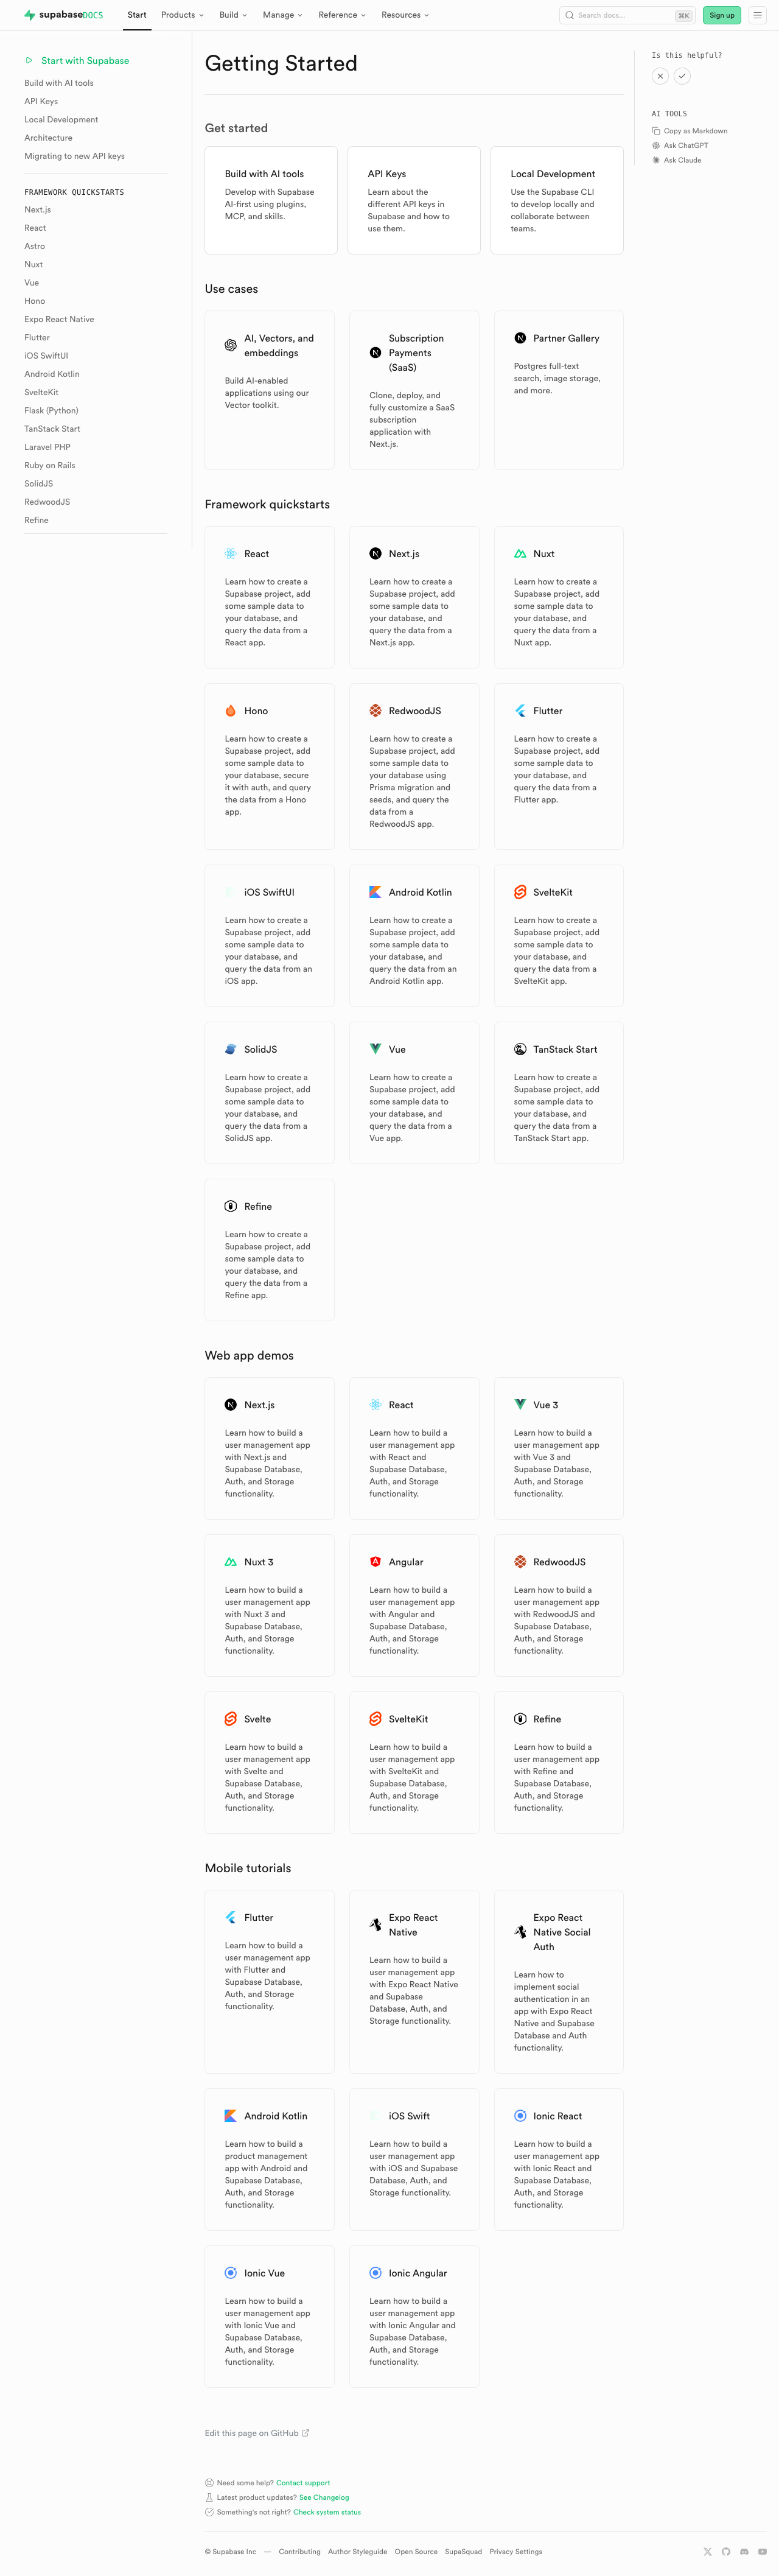 | ### Test plan - [ ] Visually verify migrated pages render correctly: - [ ] `/guides/auth` — grid "Get started", conditional pricing list, grid "Next steps" - [ ] `/guides/database/overview` — get started + next steps listings - [ ] `/guides/getting-started` — top 3-column grid - [ ] `/guides/functions` — get started + example listings - [ ] `/guides/storage` — get started, examples, resources listings - [ ] `/guides/realtime` — get started, examples, resources listings - [ ] Confirm listings render at explicit page positions - [ ] Click a content listing link and verify `docs_content_listing_clicked` fires in PostHog with expected properties (the new `listingId` is the namespaced kebab-case id, e.g. `storage-get-started`) - [ ] Build docs and confirm `.md` alternate output includes listing sections at component placement (e.g. `public/markdown/guides/storage.md`) - [ ] Run unit tests: `pnpm test:local lib/content-listings.test.ts` in `apps/docs` ## Summary by CodeRabbit ## Release Notes * **New Features** * Introduced a standardized content listings system for organizing related guides and resources. * Content listings now support both grid and list layouts for consistent presentation. * Added click telemetry for content listing interactions. * **Documentation** * Updated authentication, database, functions, getting started, realtime, and storage guide pages to use the new content listing components. * Improved MDX structure examples and listing markup formatting in contributor documentation. <!-- end of auto-generated comment: release notes by coderabbit.ai --> <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit ## Release Notes * **New Features** * Introduced a new content listings component for displaying guide content in list and grid layouts across documentation pages. * Added telemetry tracking for content listing interactions to measure user engagement. * **Documentation** * Updated guide pages (Authentication, Database, Functions, Storage, Realtime, Getting Started) to use the new listings layout. * Added contribution guidelines for creating and managing content listings in documentation. * **Tests** * Added comprehensive test coverage for content listings validation, serialization, and rendering. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Nik Richers <nik@validmind.ai> Co-authored-by: Jeremias Menichelli <jmenichelli@gmail.com> |
||
|
shaziya
|
d582d3cd8f |
feat(www): add TRAE webinar event landing page (#47415)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? - Adds event landing page for the Supabase x TRAE webinar (July 22, 2026 at 7pm PT) - Adds Gary Qi (TRAE) to authors.json - Adds TRAE logos and Gary Qi avatar ## Test plan - [ ] Preview the page at `/events/supabase-trae-high-quality-apps` - [ ] Confirm speaker cards render correctly - [ ] Confirm TRAE logo appears in the event header 🤖 Generated with [Claude Code](https://claude.com/claude-code) <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added a new MDX event page for an upcoming webinar about building high-quality Supabase apps with TRAE. * Included event details such as schedule, duration, timezone, speaker information, and a registration/CTA link. * Added supporting content covering what attendees will learn, plus live Q&A and recording availability. * Updated the authors list by adding Gary Qi to support refreshed speaker/content attribution. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Charis
|
b34a9a027f |
fix: snippet content missing after move or rename (#47409)
Snippet content was wiped blank after a move or rename (until dashboard refreshed) because it depended on the API returning the new content, but the API returns under the `content` field, not the `unchecked_sql` field that is expected. Added a `remapSqlContentField` remap to fix. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Bug Fixes** * Improved the saved content response so snippet fields are mapped consistently before being returned. * Kept the saved status unchanged while updating the returned data shape for better accuracy. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Danny WhiteandCursor
|
3acc53cca3 |
chore(studio): minor database UI polish (#47356)
## What kind of change does this PR introduce? Chore ## What is the current behavior? - Add-column uses implicit button styling - Replication row tooltip says "Open in Table Editor" ## What is the new behavior? - Add-column explicitly uses `variant="default"` - Auth Users explicitly uses `variant="default"` - Replication row tooltip says "Table Editor" --------- Co-authored-by: Cursor <cursoragent@cursor.com> |
||
|
Charis
|
0abfbdd3d7 |
fix(studio): preserve session and redirect to MFA when AAL elevation is needed (#47145)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? Bug fix. ## What is the current behavior? `withAuth` calls `signOut()` and redirects to `/sign-in` whenever the current AAL is below the required level. For IdP-initiated SSO logins — where the user lands directly on `/dashboard` rather than passing through `/sign-in-mfa` — this destroys the valid AAL1 session that was just established. Subsequent mgmt-api requests then return 401 Unauthorized, and the user is dumped on `/sign-in` with no way to recover except restarting the SSO flow (which loops them back to the same state). The platform already returns an actionable `403 Insufficient AAL: MFA required` on the first mgmt-api request, but the dashboard does not capture it. ## What is the new behavior? `withAuth` now distinguishes between "not logged in" and "needs AAL elevation": - **Logged in but AAL1** → `router.push('/sign-in-mfa?returnTo=…')`, session preserved. The existing `/sign-in-mfa` page picks up the session, renders the MFA form, and bounces the user to `returnTo` after a successful challenge. - **Not logged in** → unchanged: `signOut()` then redirect to `/sign-in?returnTo=…`. - `/sign-in-mfa` is also added to the "already there, do nothing" guard so the user isn't re-redirected mid-challenge. This relies on the gotrue client's local AAL state via `useAuthenticatorAssuranceLevelQuery`, which fires before any mgmt-api request, so no fetcher-level error parsing is needed. ## Additional context <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Bug Fixes** * Improved multi-factor authentication (MFA) elevation flow to preserve user sessions instead of forcing sign-out and requiring users to restart sign-in. * Fixed unnecessary redirects when users are already on sign-in pages. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Prashant Sridharan
|
8e5ac61e3a | Cleaned up the Perplexity webinar landing page (#47413) | ||
|
|
3dffdefd6e |
fix(docs) Resolve 196 mdx lint warnings for just, quickly, actually, PostgreSQL (#47358)
Closes DOCS-1057 Contributes to DOCS-1052 ## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## Problem We have hundreds of MDX lint warnings in our docs going against style best practices. ## Solution Remove and replace in context the following: - PostgreSQL. There was only one. There was concern about exceptions, but I found none. - Just - Quickly - Actually ### What changed Edits follow the [Google developer documentation style guide](https://developers.google.com/style): concise, direct, active voice. The flagged words were removed when the sentence still read well, or replaced when meaning needed to be preserved. ### Common patterns | Flagged word | Approach | Example | |---|---|---| | **just** (filler) | Removed | "you just installed" → "you installed" | | **just** (limiting) | **only** | "just one row" → "only one row" | | **just like** | **like** / **the same as** | "function just like regular users" → "function like regular users" | | **not just** | **not only** | "not just errors" → "not only errors" | | **quickly** (performance) | **efficiently** or removed | "find rows quickly" → "find rows efficiently" | | **quickly** (time) | **soon** / **rapidly** / removed | "expires too quickly" → "expires too soon" | | **actually** (filler) | Removed | "actually execute" → "execute"; "is actually the most common" → "is the most common" | ## Tophatting 1. See the diff. 2. See that content continues to make sense in context. 3. Locally, `cd apps/docs` and run `pnpm run lint:mdx`. 4. Search for "just," "actually," "quickly", and "PostgreSQL" and see there are 0 warnings. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Documentation** * Updated wording across quickstarts, guides, and troubleshooting articles for grammar, clarity, and consistent step-by-step phrasing. * Clarified key concepts including Row Level Security policy evaluation across Supabase products, deferred foreign key constraint behavior, and when `EXPLAIN ANALYZE` executes queries (and related side effects). * Refined several troubleshooting instructions and added guidance to cap log payload size to reduce billed Logs Ingest volume. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: github-actions[bot] <41898282+github-actions[bot]@users.noreply.github.com> Co-authored-by: Nik Richers <nrichers@gmail.com> Co-authored-by: Chris Chinchilla <chris.ward@supabase.io> |
||
|
shaziya
|
9b3d57f05c |
Add recording to Perplexity webinar page (#47407)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? Add recording / change CTA ## What is the current behavior? It links to the GoToWebinar page. ## What is the new behavior? It will now link to the on-demand recording :) ## Additional context Add any other context or screenshots. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Updated the event page to feature a watchable recording instead of a registration link. * Added an embedded video section and a new “Key takeaways” area for easier recap. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Andrey A.
|
8a9a9948a8 | fix(studio): self-hosted folder listings return metadata only (#47403) | ||
|
Ivan Vasilov
|
fd85c81e6c |
chore: Bump all rate limits in Auth to match the API (#47405)
<!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Bug Fixes** * Increased the allowed maximum values for rate-limit settings, enabling much larger numeric inputs. * Updated validation messages so error text matches the new limits and time-window wording. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Jordi EnricandClaude Sonnet 4.6
|
6ba5bef9da |
fix(logs): load saved query content from api instead of stale url param FE-3733 (#47393)
## Problem Refreshing the browser while viewing a saved log query loads stale query content. The sidebar navigation link embeds the SQL in the `q` URL param at the time it is rendered. When the query is updated and saved, the URL still holds the old SQL. On refresh, the editor initialises from that stale `q` param instead of fetching the latest content from the API. ## Fix When a `queryId` is present in the URL, the `q` param is now ignored for initialising the editor. Instead, a new effect populates the editor from the API response once `useContentQuery` resolves. If the user previously ran a modified query (stored in the `search`/`s` param), that takes precedence over the saved content, preserving existing behaviour. ## How to test - Open Logs Explorer and create a new query, save it as "test". - Change the query content, click "Save query" to update it. - Refresh the browser. - Expected: the editor shows the updated query content, not the old content. - Navigate away and back, then refresh again. - Expected: the updated content still loads correctly. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Bug Fixes** * Improved the logs explorer so that selecting a saved query reliably loads its SQL into the editor. * Updated behavior so URL query text no longer overwrites the editor contents when a saved query is selected. * Ensured editor content is preserved when searching, preventing unexpected replacements. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Claude Sonnet 4.6 <noreply@anthropic.com> |
||
|
Seid Muhammed
|
affdcb35ff |
fix(studio): sum numeric-string columns in cumulative SQL charts (#47378)
Fixes: #47377 ## What is the current behavior? Enabling **Cumulative** on a results chart concatenates Y-axis values instead of summing them whenever the column is a `bigint`, `numeric`, `money`, or `count(*)` aggregate — which Postgres returns as JSON strings. For per-row values `10, 20, 30` the chart plots `10, 1020, 102030`. `getCumulativeResults` ran `(prev[yKey] || 0) + row[yKey]` on raw result rows. The Y-axis selector explicitly allows numeric-string columns, so this is a common, fully-supported path (e.g. any `count(*) ... group by`). ## What is the new behavior? Both operands are coerced with `Number()` before the addition, keeping the existing `|| 0` fallback for null/undefined/non-numeric values. The series now sums correctly: `10, 30, 60`. The cumulative logic was previously duplicated in `ChartConfig.tsx` and `QueryBlock.utils.ts` (which is how this bug slipped in twice). It is now a single shared, tested helper: `getCumulativeResults` lives in `QueryBlock.utils.ts`, and `ChartConfig.tsx` imports it instead of re-declaring its own copy. The shared helper's `ChartConfig` type import is `import type` to avoid a runtime circular dependency, and its signature accepts `readonly` rows so both call sites type-check. ## Additional context - Added regression tests for numeric-string inputs and for null/undefined/non-numeric fallback to `0`. The existing tests only covered literal `number` inputs, never the string form Postgres actually returns. - Verified the new tests fail against the old code (`y: '010'`, `'05undefined'`) and pass with the fix. Full `QueryBlock.utils.test.ts` suite: 18 passing. No migrations, no API changes, no infra changes. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Bug Fixes** * Fixed cumulative chart calculations so numeric values are always added correctly, even when results arrive as strings. * Improved handling of empty or non-numeric values in cumulative totals so they are treated as zero instead of breaking the sum. * **Tests** * Added coverage for cumulative result calculations with numeric strings and missing values. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Aaditya BhusalandAli Waseem
|
719434a7fd |
fix(studio): batched table edits issues (#47319)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? Bug fix ## What is the current behavior? Fixes #47318 Supabase Studio's batched table edit queue has a few related row identity issues: - Editing a row's primary key can make later queued edits or deletes lose track of the original row. - Editing a primary key and another column in the same row before saving can save only the primary key change, because later updates still use the old primary key in the `WHERE` clause. - Adding a row in batched edit mode and then deleting it before saving may not remove the pending row correctly. ## What is the new behavior? - Preserves the original row identity for queued operations after primary key edits. - Applies multiple queued edits for the same row as a single update when saving. - Correctly deletes newly added pending rows before they are saved. - Adds regression coverage for these batched table edit cases. ## Additional context https://github.com/user-attachments/assets/75672361-d781-4fe5-a542-071574ad57bd <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Bug Fixes** * Improved row identity handling for grid edits, optimistic updates, and queued operations so changes stay correctly attached when primary keys are edited, reverted, or “taken” by another row. * Updated header row deletion to delete from the currently visible/targeted rows rather than relying on the full dataset. * Reduced retry noise for missing tables by clearing conflicting sorts and preventing repeated retries for the same “does not exist” error. * More reliably consolidated queued edits for the same row into fewer combined save statements. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Ali Waseem <waseema393@gmail.com> |
||
|
Gildas Garcia
|
c6fc456910 |
chore: cleanup duplicate exports studio (#47387)
## Problem Knip reports many duplicate exports (both named and default). Besides, we're moving away from default exports and even have an eslint rule to enforce it on new code. ## Solution - Cleanup those exports - Update imports when necessary No functional changes. If it builds, it's fine |
||
|
Vaibhav
|
27ca9ee64d |
fix: expanded editor shortcut (#47374)
## TL;DR fixes `Cmd/Ctrl+Enter` in the expanded editor by wiring the save shortcut directly to monaco... ## ref: - closes https://github.com/supabase/supabase/issues/47368 <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added a Ctrl/Cmd+Enter shortcut in both the JSON and text editors to trigger validation and save actions. * **Bug Fixes** * Improved editor reliability by standardizing how editor actions are wired and executed after mounting. * **Performance** * Reduced unnecessary re-renders by memoizing the shared save/validation handlers used by the editor and the action bar. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
|
2aa1b52234 |
feat(studio): add feature to rewrite queries DEBUG-145 (#47266)
## Problem Moving the Logs Explorer to ClickHouse means users' saved BigQuery queries no longer run. <img width="2430" height="1010" alt="CleanShot 2026-06-29 at 11 36 04@2x" src="https://github.com/user-attachments/assets/ae0ab155-7d3d-4ae9-81c3-22bf3a88cf8c" /> ## Fix Rewrite the query with AI instead of a SQL transpiler. AI handles the long tail of nested fields and dialect differences far better than a rule-based rewriter, and it needs no extra runtime dependency. - `rewriteLogsSqlWithAI` posts the current query to `/api/ai/code/complete` with `dialect: 'clickhouse'`. The endpoint skips the Postgres schema and best-practices for that dialect and uses logs-specific instructions and model so the output is ClickHouse logs SQL (FROM `logs` + `source` filter, no `unnest` joins, nested fields read from `log_attributes['...']`). - The query's `source` is detected and its real `log_attributes` keys are fetched and passed to the model, so it maps to exact paths instead of guessing. - The rewrite runs in the background and is proposed as a side-by-side accept/discard diff in the editor. The AI Assistant panel is not opened. - Entry points: a banner shown only for legacy-looking queries (dismissal persisted), and a "Fix Query" button next to Field Reference. - The Field Reference drawers discover `log_attributes` keys from real data so the listed fields match what the source actually emits. ## Dependencies Built on top of #47265 (Logs Explorer -> OTEL endpoint) — that is the base branch of this PR. Merge #47265 first. Behind `otelLegacyLogs` (off by default). Part of DEBUG-145 (split from #47087). ## How to test - Open the Logs Explorer with a BigQuery logs query (the templates have some), click "Fix Query", and confirm the diff shows valid ClickHouse SQL. Accept it and confirm the applied query runs. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added an OTEL legacy logs workflow (behind a feature flag) with an interactive banner and a “Fix Query” ClickHouse rewrite action, including an accept/discard diff review overlay. * Introduced OTEL-aware field reference rendering with dynamic discovery of `log_attributes` keys and updated OTEL source insertion behavior. * Enabled dialect-aware SQL completion for ClickHouse logs, using logs-specific instructions and output constraints. * **Bug Fixes** * Improved rewrite flow validation and handling, including log source detection and cleanup of AI-generated SQL formatting. * **Tests** * Added Vitest coverage for rewrite prompt generation, detection/classification utilities, SQL fence stripping, OTEL field mapping, and OTEL log attribute key discovery. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Claude Opus 4.8 (1M context) <noreply@anthropic.com> Co-authored-by: Joshen Lim <joshenlimek@gmail.com> |
||
|
|
3d931aceb7 |
feat(studio): TanStack app shell — root + auth/org routes (stack 3/6, from #46424) (#47112)
**Stack 3/6** of the TanStack Start migration (#46424). Stacked on **#47110** (S2) → review that first; this PR's diff is the app shell. > [!NOTE] > Thin route wrappers that render the existing pages-router page components through the compat shims (S2). Next is untouched — it builds `pages/` and ignores `routes/`. The app doesn't function end-to-end on TanStack until the API + project routes land (S4/S5) and the flag is flipped. ## What's in this PR - `routes/__root.tsx` — root layout + a `beforeLoad` that runs the shared redirect rules; `router.tsx`. - `routes/_auth/*` — sign-in/up, forgot/reset password, SSO/MFA/partner sign-in, CLI login, Stripe-projects login. - `routes/_app/*` — account (me/security/audit/tokens), `org/$slug/*` (general/billing/team/usage/…), support. - `routeTree.gen.ts` — **regenerated** by the tanstackStart vite plugin for exactly the routes in this PR (the migration branch's tree references all ~300 routes, so it can't be copied verbatim here). It's a generated artifact; the meaningful review surface is the route files. ## Verification On top of S1+S2: `studio` typecheck ✓, lint (0 errors) ✓. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Refactor** * Enhanced internal routing infrastructure to improve application performance and code organization. These behind-the-scenes updates ensure a more stable and maintainable foundation for the platform without affecting existing functionality or user experience. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Alaister Young <10985857+alaister@users.noreply.github.com> Co-authored-by: Ivan Vasilov <vasilov.ivan@gmail.com> |
||
|
Joshen Lim
|
e938016141 |
Chore/minor logs explorer nudges (#47391)
## Context Just minor nits i noticed with the logs explorer ## Changes involved - Add a tooltip to the + button here - wasn't clear what this was doing <img width="306" height="90" alt="image" src="https://github.com/user-attachments/assets/8fa18544-9ed3-413f-9816-1e8e760cc0c2" /> - Clear query params when deleting a saved query that you're currently on (reset back to default state) - Saving a logs query should use the value that's in the monaco editor <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added a tooltip-enhanced “New query” action in the logs sidebar to make navigation to the query explorer clearer. * **Bug Fixes** * After deleting a saved query, the logs page now clears the related URL query parameters when the deleted item is currently open. * Saving an existing query now uses the latest SQL from the editor, ensuring the stored query text is up to date. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
supabase-supabase-autofixer[bot]andgithub-actions[bot]
|
f341452edb |
[bot] Decrease ESLint ratchet baselines (#47369)
Automated weekly decrease of ESLint ratchet baselines. Co-authored-by: github-actions[bot] <github-actions[bot]@users.noreply.github.com> |
||
|
Kanishk Dudeja
|
1f03c0dc0e |
fix(billing): trim Tax ID inputs to trigger required validation (#47311)
### Summary This PR trims the Tax ID value on the frontend so that whitespace-only entries (e.g. " ") are correctly treated as "not set" instead of a valid value. Previously the "is the Tax ID set?" checks relied on string length/truthiness, so whitespace-only input slipped through as a real value - bypassing validation and getting persisted. ### Testing - Subscription upgrade & top-up forms: verified the form no longer submits when only whitespace is entered for the Tax ID. The validation message now shows. - Billing address form: no inline message is shown, but the Tax ID is submitted as null, which clears it. This is unchanged from current behaviour. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Bug Fixes** * Tax ID values are now trimmed before validation and submission, reducing errors caused by accidental leading or trailing spaces. * Billing and payment flows now consistently use the cleaned Tax ID value when deciding whether to save or send it. * Customer tax ID details passed to payment setup now reflect the trimmed value, helping avoid mismatches with external payment processing. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Joshen Lim
|
3d10f2cab9 |
Add user flow for iceberg wrapper if api keys are rotated (#47336)
## Context We found an issue regarding Analytics Buckets and the Iceberg wrapper - upon creation of an analytics bucket, the wrapper is automatically created for the users which involves using the project's API keys as the catalog's token. However, if the user were to rotate the API keys, this will cause the wrapper to break and there's currently no clear user flow for the user to self-remediate - the only indicator they'll see is just a 403 error (e.g when trying to view the analytics bucket table via FDW on the table editor or SQL editor) ## Changes involved Am adding a user path for users to self-remediate a little, starting from the Table Editor - we'll add a contextual error message as such if we detect a 403 that's caused by an invalid token: <img width="1110" height="320" alt="Screenshot 2026-06-26 at 17 33 11" src="https://github.com/user-attachments/assets/28ea4ce6-5b81-4217-9952-880acb02f2bd" /> We'll subsequently also float this issue up in the Analytics Bucket UI (which is linked from the contextual error above) <img width="1114" height="466" alt="Screenshot 2026-06-26 at 17 31 52" src="https://github.com/user-attachments/assets/8d112e5b-6ecc-458b-b4dc-7e7647da3fb2" /> And users can then choose to use another API key as the catalog token <img width="585" height="246" alt="Screenshot 2026-06-26 at 17 31 56" src="https://github.com/user-attachments/assets/3d9689a5-b18d-4f07-a5a5-d882e41c5958" /> The warning will thereafter go away, and users will be able to query the FDW again via Table Editor or SQL Editor ## To test - [ ] Create an analytics bucket, set up a table and foreign schema (via Query via Postgres) - [ ] Insert some data, or verify that you can view the iceberg table from the Table Editor - [ ] Now rotate your API secret key (delete the old, create a new) - [ ] Verify that you'll run into that error if you view the iceberg table from the Table Editor - [ ] Follow the flow -> Go to the Analytics Bucket UI to update the catalog token - [ ] Verify that thereafter, you can view the iceberg table again from the Table Editor <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added clearer Iceberg/analytics bucket setup prompts for missing, outdated, or uninstalled wrappers. * Added an “Update catalog token” dialog and a collapsible “View error” troubleshooting UI. * **Bug Fixes** * Improved detection of Iceberg authorization failures and now shows a more specific error with guidance. * Warn users when the saved catalog token no longer matches available API keys. * Enhanced post-update refresh behavior so updated token values display correctly. * **Documentation** * Clarified vault token description to indicate it may be a secret or service role key. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
|
8192d97008 |
feat: surface send-email hook status in template UI and hook deletion dialog (#46319)
## What kind of change does this PR introduce? Feature. Implements [AUTH-1215](https://linear.app/supabase/issue/AUTH-1215/improve-studio-ui-when-send-email-hook-is-active-or-deleted). Follow-up to #45396. ## What is the current behavior? When a send-email hook is configured, email templates are bypassed entirely. Auth passes event metadata to the hook, not rendered HTML. The template list and editor give no indication of this. Deleting the send-email hook silently reverts Auth to using email templates with no warning. For post-cutoff Free plan projects without custom SMTP, this also locks template editing. ## What is the new behavior? ### Admonition when send-email hook is active A new `SendEmailHookActiveAdmonition` is shown on both the template list and individual template editor pages when `HOOK_SEND_EMAIL_ENABLED` and `HOOK_SEND_EMAIL_URI` are set: > **Email templates are not used** > A Send Email hook is active. Event metadata is passed directly to your hook, meaning these templates are bypassed entirely. With a **Manage hook** link to the hooks page. ### AlertDialog for Send Email hook deletion Deleting the Send Email hook now uses a dedicated `DeleteSendEmailHookConfirmationDialog`: - **Always:** "The {default or built-in} email templates will be used to send auth emails." - **Post-cutoff Free plan, no custom SMTP:** adds "Email templates cannot be edited on the Free plan without custom SMTP." The dialog stays open with a loading state while the deletion is in-flight and closes on success. | After | | --- | | <img width="1862" height="880" alt="CleanShot 2026-05-25 at 15 57 41@2x" src="https://github.com/user-attachments/assets/8a441bb2-9112-4b19-bd0b-02c9d1989ec1" /> | | <img width="884" height="578" alt="CleanShot 2026-05-25 at 15 57 21@2x" src="https://github.com/user-attachments/assets/44e5bd79-2bd9-44ee-8f53-5fdaeefd68c6" /> | <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added a Send Email hook warning in the template editor with “Manage hook” and “Learn more” links. * **UI Improvements** * Refined template editor alerts to reflect when templates are bypassed vs blocked. * Updated hook cards/actions to a dropdown with separate Edit and Delete flows, including documentation links. * **Bug Fixes** * Improved template editor and hook deletion flows to better reflect pending states and current authentication configuration. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Joshen Lim <joshenlimek@gmail.com> Co-authored-by: Claude Sonnet 4.5 <noreply@anthropic.com> Co-authored-by: Cursor <cursoragent@cursor.com> |
||
|
|
4fa106e53c |
fix(studio): stop GraphiQL from corrupting other Monaco editors (#47363)
GraphiQL (`@graphiql/react`) runs a second Monaco instance that injects
two global, page-wide styles which corrupt Studio's other editors once a
GraphiQL chunk has loaded (it persists across client-side navigation, so
a full reload hides it). After visiting GraphiQL and returning to e.g.
the SQL editor, the editor collapses to a ~5px sliver and its syntax
colors swap to GraphiQL's theme.

**Changed:**
- `monaco.css` — a higher-specificity counter-rule
(`.monaco-editor.monaco-editor { position: relative !important }`) beats
GraphiQL's runtime-injected `.monaco-editor { position: absolute
!important }`, which otherwise pulls Studio's `@monaco-editor/react`
wrapper out of flow and collapses it to ~5px.
- GraphiQL now uses the primary `supabase` Monaco theme instead of a
separate `supabase-graphql-*` theme, so the global `.mtk*` token palette
stays identical and syntax colors no longer bleed into other editors.

**Added:**
- E2E test (`monaco-graphiql-coexistence.spec.ts`) reproducing both bugs
via client-side SQL editor → GraphiQL → SQL editor navigation (a full
reload unloads the chunk and hides the bug).
- Component test (`CodeEditor.test.tsx`) guarding the height-class
precedence regression from #47339/#47350 — a caller height (e.g. the
email template editor's `h-96`) must win over the default `h-full`.
Covered as a component test since the email source editor isn't
reachable on self-hosted.

## To test

- Open the SQL editor → **Integrations → GraphiQL** → back to the SQL
editor (in-app navigation, not a reload). It should stay full height and
keep its own syntax colors.
- Confirm autocomplete still works in the SQL editor.
- `pnpm --prefix e2e/studio run e2e --
features/monaco-graphiql-coexistence.spec.ts`
- `pnpm --prefix apps/studio test -- CodeEditor.test`


<!-- This is an auto-generated comment: release notes by coderabbit.ai
-->

## Summary by CodeRabbit

* **Bug Fixes**
* Improved Monaco editor styling so GraphiQL no longer affects the SQL
editor’s theme or layout when navigating between them.
* Fixed editor sizing so a custom height now takes precedence over the
default full-height setting.
* Polished GraphiQL panel styling for more consistent spacing and
appearance across themes.

* **New Features**
* GraphiQL now uses the shared editor theme for better visual
consistency with Studio.

<!-- end of auto-generated comment: release notes by coderabbit.ai -->

---------

Co-authored-by: Alaister Young <10985857+alaister@users.noreply.github.com>
Co-authored-by: Joshen Lim <joshenlimek@gmail.com>
|
||
|
supabase-supabase-autofixer[bot]andphamhieu
|
eb21ae25f7 |
feat: update mgmt api docs (#47382)
This PR updates mgmt api docs automatically. Co-authored-by: phamhieu <689843+phamhieu@users.noreply.github.com> |
||
|
Pamela ChiaandAlaister Young
|
20290c71bd |
fix(docs): stop named-bot markdown 404s on guides (#47337)
## Summary Since the guides UA-redirect shipped (GROWTH-811), named LLM bots requesting `/docs/guides/*` get rewritten to the markdown handler, which returns a 404 when no `.md` file exists. About 90K of those 404s per day land on real pages that serve HTML 200 fine: the bot gets nothing on a page that works. The root cause is that the docs middleware hardcoded `hasMarkdownVariant: true` for every guide path, so it never checked whether a `.md` actually existed. I fixed it in two layers: 1. A build-time slug manifest makes `hasMarkdownVariant` truthful. Guide pages with no `.md` now fall through to HTML 200 instead of a 404. This is content-source-agnostic and future-proof: a new content source can never silently regress to a 404. 2. A second generator pass emits real markdown for the troubleshooting collection (the largest source, ~70% of the 404 volume), so those bots get clean markdown rather than just HTML. ## Changes - Add a shared `markdown-sources` module: a single source of truth for which slugs get a `.md` (guides + troubleshooting), so the generator output and the manifest cannot drift. - Generate markdown for the troubleshooting collection (196 pages, TOML frontmatter parsed via `smol-toml`), written under `public/markdown/guides/troubleshooting/`. - Emit a build-time slug manifest (a gitignored generated `.ts` module, regenerated in `prebuild`, `predev`, and `pretypecheck`, mirroring the existing `__generated__/graphql.ts` lifecycle). - Gate the middleware's `hasMarkdownVariant` on the manifest: serve HTML 200 instead of a 404 for guide paths with no markdown variant. This PR intentionally does not generate markdown for the ai-prompts, YAML config, and externally-fetched (splinter) sources. The HTML fallback covers them now; generating their markdown is follow-up work. ## Testing Local verification (deterministic, against the real manifest and the real negotiation function): - Manifest invariant holds: 744 manifest slugs equal 744 generated `.md` files. - Generator emits 196 troubleshooting files with zero warnings, frontmatter stripped, no leaked delimiters. - Negotiation decision matrix, 6/6: covered slug + bot UA to markdown; uncovered real page + bot UA to pass (HTML 200); nonexistent + bot UA to pass; browser to HTML; covered + `.md` suffix to markdown; uncovered + `.md` suffix to pass. Verified on the Vercel preview deploy: - [x] `User-Agent: ChatGPT-User` on a troubleshooting page returns `200 text/markdown` (real markdown body, frontmatter stripped). - [x] `User-Agent: ChatGPT-User` on an uncovered real page (`ai-tools/ai-prompts/code-format-sql`) returns `200 text/html` (was 404). - [x] Browser request to the same uncovered page returns `200 text/html` (unchanged for humans). - [x] `User-Agent: ChatGPT-User` on a covered standard guide returns `200 text/markdown` (no regression). - [x] `User-Agent: ChatGPT-User` on a nonexistent guide URL returns `404` (correct). Known limitation: an explicit `.md`-suffix request on an uncovered page still 404s by design (an explicit markdown request for a page that has no markdown). The ~90K/day volume is plain-URL UA-based, so it is unaffected. Post-deploy, I will re-run the request-grain 404 reclassification in the GROWTH-915 BQ workspace to confirm fixable guide markdown 404s drop to near zero. ## Linear - fixes GROWTH-946 <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added generated markdown slug tracking for docs guides, improving markdown availability detection. * Added automated manifest generation and validation during docs build and CI workflows. * **Bug Fixes** * Improved guide markdown negotiation so only supported guide slugs are treated as having a markdown variant. * Standardized markdown source handling for guides and troubleshooting pages. * **Tests** * Added coverage for guide and troubleshooting slug generation. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Alaister Young <10985857+alaister@users.noreply.github.com> |
||
|
Danny WhiteandCursor
|
a074b62ed1 |
chore(studio): use sentence case for Data API access label (#47353)
## What kind of change does this PR introduce? UI copy + agent guidance. ## What is the current behavior? - The Table Editor labels the Data API setting as "Data API Access" (title case). - Agents have no scoped pointer to our copywriting rules ## What is the new behavior? - Label uses sentence case: "Data API access" (e2e and test docs updated). - Agents are pointed at `apps/design-system/content/docs/copywriting.mdx` via `studio-copy.instructions.md` and `studio-ui-patterns` skill. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Bug Fixes** * Standardized the **“Data API access”** label casing across the Studio UI. * Updated end-to-end tests to assert the corrected label text. * **Documentation** * Updated Studio E2E test review instructions and examples to use **“Data API access”**. * Added/expanded Studio UI copywriting guidance, including where to source copy and how to apply consistent casing. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Cursor <cursoragent@cursor.com> |
||
|
Miranda Limonczenko
|
5fc0c86007 |
feat(studio) Link observability pages to relevant docs (#47351)
Closes DOCS-488 <img width="1266" height="353" alt="Screenshot 2026-06-26 at 11 02 57 AM" src="https://github.com/user-attachments/assets/67b5d47b-249e-4e53-9230-2bbcb7f037b7" /> ## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## Problem We have helpful documentation that delves into each observability metric, but it is not easily findable in the moment it is needed while viewing the dashboards. ## Solution Solution includes: - Add a docs link in Studio in every relevant place with the `DocsButton` component - Add aria-hidden on the `DocsButton` icon - An added `constants.ts` to see all of the docs links in one place - A contextual aria-label for the docs so that screenreader users know where they're going | Page | Docs link | |------|-----------| | Overview | `/guides/telemetry/reports` | | Query Performance / Query Insights | `/guides/platform/performance#examining-query-performance` | | API Gateway | `/guides/telemetry/reports#api-gateway` | | Database | `/guides/telemetry/reports#database` | | Data API | `/guides/telemetry/reports#postgrest` | | Auth | `/guides/telemetry/reports#auth` | | Edge Functions | `/guides/telemetry/reports#edge-functions` | | Storage | `/guides/telemetry/reports#storage` | | Realtime | `/guides/realtime/reports` | | Custom reports | `/guides/telemetry/reports#using-reports` | Query Performance and Query Insights already had the button in their custom headers. They now use the shared constants. ## Tophatting 1. Go to a project `/observability`. 2. Click into each of the panels and see a **Docs** link in the top right. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added direct documentation links across observability report pages, making it easier to open relevant help content from each view. * Added clearer, page-specific labels for observability headers and docs links. * **Bug Fixes** * Improved accessibility for icon buttons so icons are hidden from assistive technologies while button labels remain clear. * Adjusted report navigation layouts to keep controls aligned with the new docs buttons. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
|
f78c9db32e |
Make mfa lockout risk clear in dashboard (#47344)
## Problem #47330 is not enough. We want the alert to really catch users attention ## Solution <img width="1670" height="1138" alt="image" src="https://github.com/user-attachments/assets/3dab5145-2abf-4213-a591-45116eeacb6a" /> <img width="1634" height="1048" alt="image" src="https://github.com/user-attachments/assets/c70ac8cc-2af0-4778-a68b-3ea9ea8f8166" /> <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Bug Fixes** * Moved the “permanently locked out” MFA warning to the account security page when only one authenticator app is configured. * Removed the duplicate warning from the authenticator factor list so the message is shown in a single, consistent location. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: mo khan <mo@mokhan.ca> Co-authored-by: Danny White <3104761+dnywh@users.noreply.github.com> |
||
|
Ali Waseem
|
f1f80dd0bf |
fix(studio): restore email template source editor height (#47350)
## What Restores the email template **source editor** height, which had collapsed to a single line. ## Root cause Earlier today, #47339 ("prevent Monaco editor collapse after visiting GraphiQL") appended `h-full` to the shared `CodeEditor`: ```ts className={cn(className, 'monaco-editor', 'h-full')} ``` `cn` is `twMerge(clsx(...))`. tailwind-merge resolves conflicting height utilities by keeping the **last** one, so the trailing `h-full` clobbered any caller-supplied height. The email template editor (`TemplateEditor.tsx`) passes `h-96`, and its wrapper has no explicit height — so `h-full` resolved to 0 and the editor collapsed to a single line. ## Fix Reorder so `h-full` is a default that a caller's height wins over: ```ts className={cn('monaco-editor', 'h-full', className)} ``` - Email editor passes `h-96` → comes last → wins → 384px height restored. - Callers that set no height (GraphiQL, etc.) → `h-full` still applies → #47339 fix preserved. ## Testing - [ ] Email template source editor renders at full height again - [ ] GraphiQL → editor navigation still does not collapse Fixes FE-3728 <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Bug Fixes** * Improved editor sizing so custom height classes are respected instead of being overridden by the default full-height styling. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Nik RichersandNik Richers
|
032a368221 |
fix(docs): overhaul Ionic Vue tutorial auth flow and example app (#47142)
## I have read the CONTRIBUTING.md file.
YES

## What kind of change does this PR introduce?
Bug fix, docs update

Closes DOCS-353.

## What is the current behavior?
- Linear item: Overhaul Ionic Vue tutorial
- Debug email shown on login page after submit
- Login redirect / route guard issues
- Email missing on account page
- HTML5 `type="url"` blocks profile update for `example.com`
- Tutorial `.env` used `VUE_APP_SUPABASE_KEY` but app expects
`VUE_APP_SUPABASE_PUBLISHABLE_KEY`

## What is the new behavior?
- Removed debug `<p>{{ email }}</p>` from Login.vue
- Route guards in `router/index.ts`; simplified App.vue user sync
- Account email from `getClaims()`; website `type="text"`;
`useIonRouter` for logout
- Store typed as `User | null`
- Tutorial MDX env var fixed
- Audit skills moved to
[supabase/docs-agent-skills](https://github.com/supabase/docs-agent-skills):
[`audit-ionic-vue-tutorial`](https://github.com/supabase/docs-agent-skills/blob/main/.claude/skills/audit-ionic-vue-tutorial/SKILL.md),
[`audit-docs-tutorials`](https://github.com/supabase/docs-agent-skills/blob/main/.claude/skills/audit-docs-tutorials/SKILL.md)
— both require **live Supabase platform** E2E (not just build/lint)

**Tutorial preview:** [Build a User Management App with Ionic
Vue](https://supabase.com/docs/guides/getting-started/tutorials/with-ionic-vue)


## Additional context
- Verification (author): `npm install && npm run build` — **pass**
(warnings only)
- E2E: profiles migration applied to project `moijyfpvgnmgoxvwcikq`; add
`.env` from `.env.example` with publishable key for full auth flow test

### Test plan
- [ ] `cd examples/user-management/ionic-vue-user-management && npm
install && npm run build`
- [ ] Confirm tutorial MDX `.env` uses
`VUE_APP_SUPABASE_PUBLISHABLE_KEY`
- [ ] Copy Project URL + publishable key into `.env`
- [ ] `npm run dev` — login page shows no email after magic-link submit
- [ ] Magic link redirects to `/account`
- [ ] Email displays on account page
- [ ] Update profile with `example.com` and `https://example.com` — both
save
- [ ] Logout returns to `/`; `/account` blocked without auth
- [ ] Install audit skills from
[docs-agent-skills](https://github.com/supabase/docs-agent-skills) (`ln
-sf
~/GitHub/supabase/docs-agent-skills/.claude/skills/audit-ionic-vue-tutorial
~/.claude/skills/audit-ionic-vue-tutorial` and same for
`audit-docs-tutorials`), then run
[audit-ionic-vue-tutorial](https://github.com/supabase/docs-agent-skills/blob/main/.claude/skills/audit-ionic-vue-tutorial/SKILL.md)
platform E2E (magic link, profile update verified via SQL)
- [ ] Run
[audit-docs-tutorials](https://github.com/supabase/docs-agent-skills/blob/main/.claude/skills/audit-docs-tutorials/SKILL.md)
— confirm platform E2E column is filled for with-ionic-vue


<!-- This is an auto-generated comment: release notes by coderabbit.ai
-->

## Summary by CodeRabbit

* **New Features**
* Improved authentication handling in the Ionic Vue user-management
example, with smoother sign-in/sign-out redirects and account access
checks.
  * Updated account details to display the user’s email more reliably.

* **Bug Fixes**
* Adjusted navigation so authenticated users are routed to the account
page and unauthenticated users are sent back to the home page.

* **Documentation**
* Updated setup instructions and example environment variables for the
Supabase integration.

<!-- end of auto-generated comment: release notes by coderabbit.ai -->

---------

Co-authored-by: Nik Richers <nik@validmind.ai>
|
||
|
Ivan Vasilov
|
a9565c1645 |
refactor: Optimize Sentry user ids (#47342)
<!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Bug Fixes** * Improved signed-in user identification in error tracking to use the current authenticated user ID directly. * Removed reliance on previously stored anonymous identifiers, reducing inconsistent user matching across sessions. * **Tests** * Added coverage to confirm error tracking user identity is set when a user is signed in and not set when signed out. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |











