mirror of
https://github.com/supabase/supabase.git
synced 2026-10-05 17:35:10 +03:00
2cd9b42e803277edefaa02e8aa5e4cdc27c19bb2
5550
Commits
| Author | SHA1 | Message | Date | |
|---|---|---|---|---|
 Prashant Sridharan |
c38117b613 |
Added new go page for CISO dinner at Select (#50360)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? Added a CISO dinner landing page and integration with Notion. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added an RSVP page for the Supabase Select 2026 CISO Dinner in San Francisco. * Included event details, host information, attendee fields, and RSVP submission with confirmation redirect. * Added a thank-you page confirming successful registration and sharing event timing and security resources. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
|
c3ccf9179f |
fix(www): skip the careers-page globe when WebGL is unavailable (#50350)
## Summary
- `cobe`'s `createGlobe()` resolves the canvas context internally as
`getContext('webgl2') || getContext('webgl') || 'experimental-webgl'` (a
context-name *string*, not an actual context). When both `webgl2` and
`webgl` are unavailable, it falls through to that string, but modern
browsers no longer support the `experimental-webgl` context name, so the
resulting context is `null` and cobe crashes internally reading
`.enable(...)` on it.
- `apps/www/components/Globe.tsx` (used only on `/careers`) had no guard
for this, so a browser/device with WebGL disabled or unavailable (GPU
blocklist, corporate policy, privacy setting) crashes the entire careers
page via `globalErrorBoundary`.
- Fix: detect WebGL support ourselves (`getContext('webgl2') ||
getContext('webgl')`) before mounting the globe, and skip rendering it
(no globe, rest of the page renders fine) when unsupported.

## Evidence (Sentry, past week)
- [WWW-41](https://supabase.sentry.io/issues/7731263201/) — `TypeError:
Cannot read properties of null (reading 'enable')` on `/careers`, leaf
frame inside `cobe`/`phenomenon`.

## Test plan
- [ ] Manually confirmed `Globe.tsx` is only imported by
`apps/www/pages/careers.tsx`
- [ ] No automated test added (this is a purely decorative,
non-interactive canvas element with no existing test coverage); happy to
add one if reviewers want it

🤖 Generated with [Claude Code](https://claude.com/claude-code)

https://claude.ai/code/session_01RUrmUfMBpPqkgerh9onNTM

---
_Generated by [Claude
Code](https://claude.ai/code/session_01RUrmUfMBpPqkgerh9onNTM)_

---------

Co-authored-by: Claude <noreply@anthropic.com>
Co-authored-by: Ali Waseem <waseema393@gmail.com>
|
||
|
Ivan VasilovandAli Waseem
|
c60bb37a74 |
chore: Bump nextjs to non-vulnerable version (#50341)
<!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Chores** * Updated the Next.js version used by the application and documentation sites. * Aligned workspace tooling with the latest supported Next.js 16.3.5 release and refreshed related platform builds. * Updated application and documentation sites to Next.js 15.5.24. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Ali Waseem <waseema393@gmail.com> |
||
|
Anthony Lio
|
819df2ae4d |
feat(www): menu nav enhancements (#50282)
## What kind of change does this PR introduce? feature reworks the www header dropdowns ## What is the current behavior? menu dropdown navigation animation between items feels scattered ## What is the new behavior? - adds dropdown card resize with a transition and the content crossfades when switching - removes dead zone between or under nav items - sets card is centered on the screen + enhance tablet bp - adds slight ui refresh spacing, colors, sizes | state | preview | | -------|------| | before | <video src="https://github.com/user-attachments/assets/acd8e161-a697-4070-b751-4f4e9f1eab19" /> | | after | <video src="https://github.com/user-attachments/assets/fe403afd-0074-4cb5-9223-fd6cdd2f7d5a" /> | <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Navigation dropdowns now provide smoother directional transitions, keyboard-focus states, and reduced-motion support. * Product navigation is organized into clearer Products and Modules sections. * Navigation layouts adapt earlier across screen sizes with responsive two-column arrangements. * **Style** * Updated dropdown spacing, colors, borders, menu item styling, and customer imagery sizing. * Refined blog loading placeholders with slightly tighter spacing. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Jordi Enric
|
fb22534439 |
fix: share sentry crash policy and enable www reporting (#50232)
## Problem The website initializes Sentry only on the server and edge runtimes, leaving browser crashes unreported. Its crash-reporting setup also needs the same consent and third-party filtering policy that docs and Studio otherwise maintain separately. ## Fix Add www browser initialization and tagged crash capture for both Next.js routers, with accessible fallback focus. Move the shared consent/platform and third-party filtering into common/sentry, reuse it from all three apps, and remove the duplicated docs/www helpers and tests. Preserve each app's initialization and Studio's additional noise filtering, sampling, and sanitization. Include the source-map upload token in www's build cache inputs, and trigger the shared/www and Studio test workflows when the shared policy changes. ## How to test - Run `pnpm --filter www test ../../packages/common/sentry.test.ts lib/sentry-capture.test.tsx`: all 22 shared-policy and real-SDK capture tests passed locally. - Run `pnpm --filter studio exec vitest run lib/sentry-client-options.test.ts`: all 42 Studio options and policy-parity tests passed locally. - The www capture tests exercise the actual initializer and both router handlers with an in-memory transport, verify crash tags and fallback focus, and enforce consent. Removing initialization, capture calls, boundary tags, or consent gating was verified to fail these tests. - On a www preview with its DSN configured, accept telemetry consent and trigger temporary render errors in both routers. Verify they reach the www Sentry project with the boundary tag and readable stack traces. Formatting passes. Full local app typechecks encounter existing dependency/generated-file drift, with no diagnostics in changed files. Three unchanged TanStack mock call-count tests fail locally and reproduce against the pre-refactor implementation. Live Sentry ingestion and source-map uploads remain deployment checks. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit - **Accessibility** - Error pages now automatically move focus to a clearly labeled error message, helping screen-reader and keyboard users understand when a page fails. - **Reliability** - Browser error reporting now captures application crashes more consistently across supported page types and navigation transitions. - Reporting respects consent and platform availability while filtering unrelated third-party failures. - **Testing** - Expanded automated coverage for error capture, reporting rules, consent handling, and accessible error-page behavior. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Miranda Limonczenko
|
86f3a98399 |
fix(docs): stop reporting guide 404s to Sentry, redirect missing paths (#50279)
Closes DOCS-1388 ## Problem Expected guide-path 404s were reported to Sentry as errors. They made up roughly 246k events and nearly all Docs volume, with 0 users impacted. The cause is a type check that never matched. `getGuidesMarkdownInternal` tested `error.cause instanceof FileNotFoundError`, but `GuideModelLoader.fromFs` rethrows `FileNotFoundError` directly and sets `cause` to the underlying `ENOENT` error. Every missing guide path fell through to the `else` branch and hit `Sentry.captureException`. Nine storage section paths and `database/postgrest` also 404 in production. They are section `url` values in the nav config with no landing page and no redirect. They are not reachable from the sidebar, because a nav item with children renders as an accordion button, so the traffic is inbound links and crawlers. ## Solution - Check the error itself as well as its cause, so expected 404s take the quiet branch. - Add `ignoreErrors` for `FileNotFound` to `sentry.server.config.ts`, matching the filtering the client config already does. - Redirect nine storage section paths to their first child page, following the existing `storage/cdn` and `storage/uploads` pattern. - Redirect `database/postgrest` to the Data API guide. The path has no git history, so its 27k hits are external inbound links. - Add the missing leading slash to the `storage/access-control` destination. It resolves correctly today, so this is a cleanup, not a fix. ## Redirect previews Redirects are served by the `www` config, so the **Redirect** column uses the www preview. The www preview cannot render `/docs/**` pages, so each link lands on a 404 after the hop. That is expected. Check the `Location` header, or use the **Destination** column to confirm the page itself. | Source | Redirect | Destination | | :--- | :--- | :--- | | `/docs/guides/storage/production` | [test](https://zone-www-dot-com-git-docs-sentry-404s-and-guide-fa783f-supabase.vercel.app/docs/guides/storage/production) | [storage/production/scaling](https://docs-git-docs-sentry-404s-and-guide-redirects-supabase.vercel.app/docs/guides/storage/production/scaling) | | `/docs/guides/storage/security` | [test](https://zone-www-dot-com-git-docs-sentry-404s-and-guide-fa783f-supabase.vercel.app/docs/guides/storage/security) | [storage/security/ownership](https://docs-git-docs-sentry-404s-and-guide-redirects-supabase.vercel.app/docs/guides/storage/security/ownership) | | `/docs/guides/storage/serving` | [test](https://zone-www-dot-com-git-docs-sentry-404s-and-guide-fa783f-supabase.vercel.app/docs/guides/storage/serving) | [storage/serving/downloads](https://docs-git-docs-sentry-404s-and-guide-redirects-supabase.vercel.app/docs/guides/storage/serving/downloads) | | `/docs/guides/storage/management` | [test](https://zone-www-dot-com-git-docs-sentry-404s-and-guide-fa783f-supabase.vercel.app/docs/guides/storage/management) | [storage/management/copy-move-objects](https://docs-git-docs-sentry-404s-and-guide-redirects-supabase.vercel.app/docs/guides/storage/management/copy-move-objects) | | `/docs/guides/storage/s3` | [test](https://zone-www-dot-com-git-docs-sentry-404s-and-guide-fa783f-supabase.vercel.app/docs/guides/storage/s3) | [storage/s3/authentication](https://docs-git-docs-sentry-404s-and-guide-redirects-supabase.vercel.app/docs/guides/storage/s3/authentication) | | `/docs/guides/storage/debugging` | [test](https://zone-www-dot-com-git-docs-sentry-404s-and-guide-fa783f-supabase.vercel.app/docs/guides/storage/debugging) | [storage/debugging/logs](https://docs-git-docs-sentry-404s-and-guide-redirects-supabase.vercel.app/docs/guides/storage/debugging/logs) | | `/docs/guides/storage/schema` | [test](https://zone-www-dot-com-git-docs-sentry-404s-and-guide-fa783f-supabase.vercel.app/docs/guides/storage/schema) | [storage/schema/design](https://docs-git-docs-sentry-404s-and-guide-redirects-supabase.vercel.app/docs/guides/storage/schema/design) | | `/docs/guides/storage/vector` | [test](https://zone-www-dot-com-git-docs-sentry-404s-and-guide-fa783f-supabase.vercel.app/docs/guides/storage/vector) | [storage/vector/introduction](https://docs-git-docs-sentry-404s-and-guide-redirects-supabase.vercel.app/docs/guides/storage/vector/introduction) | | `/docs/guides/storage/analytics/examples` | [test](https://zone-www-dot-com-git-docs-sentry-404s-and-guide-fa783f-supabase.vercel.app/docs/guides/storage/analytics/examples) | [storage/analytics/examples/duckdb](https://docs-git-docs-sentry-404s-and-guide-redirects-supabase.vercel.app/docs/guides/storage/analytics/examples/duckdb) | | `/docs/guides/database/postgrest` | [test](https://zone-www-dot-com-git-docs-sentry-404s-and-guide-fa783f-supabase.vercel.app/docs/guides/database/postgrest) | [api](https://docs-git-docs-sentry-404s-and-guide-redirects-supabase.vercel.app/docs/guides/api) | | `/docs/guides/storage/access-control` | [test](https://zone-www-dot-com-git-docs-sentry-404s-and-guide-fa783f-supabase.vercel.app/docs/guides/storage/access-control) | [storage/security/access-control](https://docs-git-docs-sentry-404s-and-guide-redirects-supabase.vercel.app/docs/guides/storage/security/access-control) | All eleven return `308` on the www preview with the `Location` shown in the Destination column. Every destination returns `200`. ## Manual testing 1. Open any **Redirect** link above. The URL changes to the Destination path, confirming the redirect fires. 2. Open any **Destination** link. The page renders. 3. Confirm the sources 404 on production today, for example `https://supabase.com/docs/guides/storage/production`. 4. On the [docs preview](https://docs-git-docs-sentry-404s-and-guide-redirects-supabase.vercel.app/docs/guides/storage/schema), request a missing guide path and check the deployment logs. The line reads `Could not read Markdown at path`, not `Error processing Markdown file at path`. The second form is the branch that calls `Sentry.captureException`. |
||
|
Anthony Lio
|
42f1401769 |
fix(ui-patterns): a11y accessible names for ExpandableVideo (#50226)
## What kind of change does this PR introduce? bug fix a11y `ExapndableVideo` ## What is the current behavior? `ExpandableVideo` blurred thumbnail has `alt="Video guide preview"` sitting behind an overlay that already reads "Watch video guide" making screen readers announcing the same thing twice ## What is the new behavior? - adds an optional `videoTitle` prop that names the video once and feeds both the button's `aria-label` and the player's `title`. ## Test 1. visit `/docs/guides/functions` <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit - **Enhancements** - Video previews in guides now display the relevant guide title. - Partner introduction videos now include a descriptive title. - Video controls and embedded players provide more specific accessibility labels when titles are available. - Preview images without meaningful alternative text are treated as decorative to reduce redundant screen-reader output. - **Bug Fixes** - Guide titles with Markdown formatting now appear as clean, readable text in video labels. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Pamela Chia
|
f012dfa850 |
fix(www): sitemap lists all changelog slugs (#50275)
The www sitemap generator reads changelog URLs from the build-generated RSS feed but only accepted links whose slug starts with a number, the shape `computeChangelogEntrySlug` produces solely for entries carrying `legacy_gh_discussion`. Every changelog entry authored since that migration has a plain text slug and was silently missing from `sitemap_www.xml`. I widened the link match to any non-empty slug; the RSS builder is the only producer of that file and emits exactly one link per item, so no other filter is needed. I added a text-slug RSS item to the fixture-driven sitemap test and asserted that the changelog URL list equals the RSS item list, so a future filter that drops entries fails the suite. **Note:** text-slug entries now pass through the same fail-the-build pubDate check that numeric-prefixed entries already did after #50198. A changelog entry with no `publish_date` and no date-prefixed filename would produce an unparseable pubDate and stop the www build. The alternative, shipping the URL without lastmod, is a one-line change. I kept the gate because every current changelog entry carries a date-prefixed filename, the changelog repo documents that convention, and the build error names the entry URL. ## To test Tested on Vercel preview: - [x] Count `<item>` blocks in `<preview>/changelog-rss.xml`, then count `/changelog/` locs in `<preview>/sitemap_www.xml`, expect the two counts to match - [x] Search the preview sitemap for `/changelog/pipelines`, expect one `<loc>` entry with a `<lastmod>` date - [x] Search the preview sitemap for a numeric-prefixed entry such as `/changelog/47796-developer-update-july-2026`, expect it still present ## Linear - fixes GROWTH-1212 <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit - **Bug Fixes** - Changelog pages with text-based slugs are now correctly recognized in the sitemap. - Sitemap entries for these changelog pages now use their RSS publication dates. - RSS links are matched more reliably, ensuring all valid changelog URLs are included. - Invalid publication dates are rejected instead of producing incorrect sitemap metadata. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
AnaandAna
|
ed4162e055 |
feat(www): add Select Hackathon day-of go page (#50243)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? - Adds a new `/go` page for the Select Hackathon (Oct 3, 2026, YC) at `supabase.com/go/select-2026/hackathon` - New page definition `apps/www/_go/events/select-2026/hackathon.tsx` (`lead-gen` template) - Registers it in the go page registry `apps/www/_go/index.tsx` ## What is the current behavior? There is no day-of one-pager for the Select Hackathon on the site. ## What is the new behavior? - A day-of one-pager rendered as a `selecthackathon2026.sql` code-block section (run of show, wifi, how to submit, prizes) - `noIndex` by default (day-of page, not for search) - Removable after Select 2026 (tagged in the registry alongside the other `select-2026` go pages) ## Additional context `hackathon.supabase.com` is handled at DNS/Vercel and can point at this path. wifi network/password and help-desk location are still placeholders pending final details. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added a dedicated Supabase Select Hackathon 2026 schedule page. * Includes event timing, Wi‑Fi details, submission instructions, prize information, and mentor support guidance. * Updated the run of show to list sponsor arrival at 9:00 AM and doors opening/check-in at 9:15 AM. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Ana <ana1337x@users.noreply.github.com> |
||
|
Pamela Chia
|
e315fbcb53 |
feat(www): emit sitemap lastmod from content dates (#50198)
I added content dates to `sitemap_www.xml` and `dateModified` to blog
JSON-LD so crawlers can compare freshness with page metadata. Both use
`updated` when present, otherwise the publication date.
**Changed:**
- **Consistent dates:** I use the same frontmatter parser for the blog
page and sitemap. It preserves authored dates across quoting and
timezones and rejects JavaScript frontmatter.
- **Invalid dates stop the build:** I reject impossible calendar days,
out-of-range times and offsets, malformed dates, and `updated` before
publication. Content changes run the generator in CI.
- **Authoring:** I documented optional `updated` for substantive
revisions. Events, static pages, and `/evals` omit `<lastmod>`.
**Note:** Changelog dates come from RSS. Existing sitemap omissions for
nonnumeric changelog slugs (GROWTH-1212) and app-router pages
(GROWTH-1214) remain separate.
## To test
On the preview:
- [x] Open `/sitemap_www.xml`: blog, alternatives, customer stories, and
included changelog entries should carry `YYYY-MM-DD` lastmod values.
Verified on the
|
||
|
Pamela Chia
|
c6a1c2052c |
feat(www): cross-list openapi and mcp endpoint (#50180)
`/.well-known/ard.json` advertises the Management API OpenAPI spec and the MCP server, but `/llms.txt` listed neither and `/.well-known/api-catalog` listed only the Management API. I added both resources to the two surfaces that were missing them, so an agent finds the same spec and endpoint whichever discovery file it reads first. **Changed:** - **llms.txt gains an `## API and agent resources` section**: two described links, the same-origin `/openapi.json` spec and `https://mcp.supabase.com/mcp`, from a small list in `lib/agent-resources.ts`. A named heading rather than `## Optional`, since llmstxt.org defines Optional as links an agent may skip. The descriptions restate ard.json's on purpose; ard.json is curated to the ARD schema and stays untouched. - **api-catalog lists the MCP endpoint**: added as a catalog `item` plus its own linkset member carrying `service-doc` (the MCP guide) and `service-meta` (the OAuth protected-resource metadata the endpoint's 401 response already points at). - **Tests cover what the two files advertise**: `ard-catalog.test.ts` now parses api-catalog, checks that its `item` list and its anchored members agree, and runs every same-origin URL from api-catalog and the llms.txt resource list through the existing dead-URL resolver (public file, app route, rewrite, or docs guide). The www tests workflow now checks out `apps/docs/content/guides` (the directory the llms.txt route already reads at runtime) and runs on changes to it, so moving a guide that a catalog links to fails that PR rather than the next www one. **Note:** `/openapi.json` is an external rewrite served uncached on every request (338 KB). I tried `Cache-Control` and then the documented `x-vercel-enable-rewrite-caching` + `CDN-Cache-Control` pair on that path; the preview kept returning `x-vercel-cache: MISS`, so both are reverted. Caching the alias is a separate change. ## To test Tested on Vercel preview: - [x] `curl -s <preview>/llms.txt | tail -5`: expect an `## API and agent resources` heading followed by the OpenAPI spec link and the MCP server link; the diff against production `llms.txt` is those appended lines only - [x] `curl -s <preview>/.well-known/api-catalog | jq '.linkset[2]'`: expect a member anchored at `https://mcp.supabase.com/mcp` with `service-doc` and `service-meta`, served as `application/linkset+json` ## Linear - fixes GROWTH-1207 <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit - **New Features** - Added API and agent resource links to `llms.txt`, including the Management API specification and MCP server. - Added the Supabase MCP server to the API catalog with service documentation and metadata links. - **Tests** - Expanded catalog validation to cover API catalog entries, agent resources, and documentation guide links. - Updated pull request checks to run when guide content changes. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Danny White
|
476d4a5851 |
refactor(ui): drop redundant Button variant="default" props (#50161)
## What kind of change does this PR introduce? Mechanical cleanup on top of the Button default-variant change (#50160). ## What is the current behavior? Many callsites still pass `variant="default"` even though that is now the component default. ## What is the new behavior? Removes redundant static `variant="default"` from legacy `Button` and `ButtonTooltip` callsites. Keeps explicit defaults where they document the API: - `button-default.tsx` and `button-sizes.tsx` demos - `DocsButton`, which pins neutral styling at the wrapper boundary ## To test Studio: - [Auth → Rate Limits](https://studio-staging-2s957kwc4-supabase.vercel.app/dashboard/project/_/auth/rate-limits): dirty the form so Cancel appears; Cancel stays neutral, Save stays green - [Project Settings → API Keys](https://studio-staging-2s957kwc4-supabase.vercel.app/dashboard/project/_/settings/api-keys): `DocsButton` in the header actions stays neutral Design system: - [Design system → Button](https://design-system-git-dnywh-dc924ac1-supabase.vercel.app/design-system/docs/components/button): `button-default` / `button-sizes` still show explicit default styling; Primary (green) is restricted to the Primary section (and `asChild`) WWW: - [www → Brand assets](https://zone-www-dot-com-git-dnywh-dc924ac1-supabase.vercel.app/brand-assets): Download logo kit / Download button kit stay neutral |
||
|
Gildas GarciaandAlaister Young
|
737b8595f2 |
Update API types (#50234)
## Problem platform, v1 and v2 have been already completely migrated and introduced some changes. Some types have been renamed, some outputs and inputs updated. ## Solution - Update the API types - Fix the TS errors ## Update Taking this over to unblock #50134, which needs the new scoped token permission ids from the regenerated types. - Merged `master`. - Regenerated `api-v2.d.ts` from the production spec. The previous files came from a local API that exposed a webhook events endpoint production doesn't have yet. Production has since added standardized 400 error responses on the v2 organization endpoints. `api-v1.d.ts` and `platform.d.ts` already matched production. - Fixed `verify-production-types`. It formatted the regenerated files in a temp directory outside the repository, so Prettier fell back to its defaults and the comparison could never match the committed files. It now passes the repository config explicitly. `pnpm api:verify-types` passes on this branch. - Verified locally: `pnpm typecheck`, `pnpm api:verify-types`, Studio unit tests. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Bug Fixes** * Preserved descriptions when saving, sharing, moving, or unsharing notebooks, reports, SQL snippets, and saved queries. * Improved handling of empty or null values across notebook descriptions, billing usage, pooler settings, and infrastructure fields. * Improved read-replica connection handling, including read-only connection strings. * Updated storage configuration and capability handling to match current settings. * **API and Compatibility** * Updated organization, project, storage, OAuth, billing, and infrastructure data handling to match current API responses. * OAuth app creation and updates now require scopes. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Alaister Young <10985857+alaister@users.noreply.github.com> |
||
|
|
1966209483 |
chore(deps): upgrade vitest to v5 (#49994)
Upgrades Vitest from 4.1.4 to 5.0.0 across the monorepo, fixes the handful of things v5 turned into hard errors, and drops the `vi.clearAllMocks()` boilerplate that v5's `clearMocks` default makes redundant. **Changed:** - `vitest`, `@vitest/ui`, `@vitest/coverage-v8` 4.1.4 → 5.0.0 (catalog) - `vi.mock` calls that lived inside `beforeAll`/`beforeEach`/test bodies moved to module scope (v5 throws on nested calls). Affects the Studio and docs setup files and four Studio tests. - `detectBrowser` test restores `navigator` via `vi.unstubAllGlobals()` instead of assigning `global.navigator`, which now reaches jsdom's getter-only property. - `RowEditor.utils.test.ts` restores its `JSON.stringify` spy. It used to leak a throwing mock for the rest of the file, which v5's coverage provider now trips over. A later test in the same file had been asserting the leak's side effect (valid JSON reported as invalid) and now asserts the correct behavior. - `@testing-library/jest-dom` 6.6 → 7.0.1. Its vitest type augmentation resolves through a peer now, so it lands on each package's own `vitest` instead of whichever copy pnpm hoisted. Fixes `toBeInTheDocument` type errors in dev-tools after the reshuffle. - `@testing-library/react` 16.0.0 → 16.3.3 for the React 19 peer range. - `vite: catalog:` added to dev-tools, www, and common. Without it they resolved a newer vite than the catalog pin, which forked a second vitest instance in the lockfile. There's now one. - ai-commands custom matcher types use v5's `Matchers<R, T>` form. - 110 test files: `vi.clearAllMocks()` removed from `beforeEach`/`afterEach` hooks, along with hooks that only did that and the imports they left unused. Calls that also reset/restore mocks are untouched. Second commit, mechanical. **Added:** - `.vitest/` to the root gitignore (v5 writes JSON/JUnit/HTML reporter output there) **Removed:** - `vite-tsconfig-paths` catalog entry and deps. Vitest 5 resolves tsconfig paths itself. Release-age note: this sat in draft with a temporary `minimumReleaseAgeExclude` entry for `vitest` and `@vitest/*` while 5.0.0 was inside the workspace's 3-day `minimumReleaseAge` window. That window has closed, so the exclusion is gone and nothing bypasses the release-age gate. **Perf** (local, medians of 3 runs, same machine): | Suite | v4.1.4 | v5.0.0 | |---|---|---| | studio | 144.1s | 141.7s (-2%) | | studio `--coverage` | 156.9s | 146.4s (-7%) | | ui-patterns | 6.27s | 5.07s (-19%) | | ui `--coverage` | 3.35s | 2.14s (-36%) | | www | 0.89s | 0.47s (-47%) | Studio is dominated by jsdom environment setup per file, which v5 doesn't change. `vitest doctor` recommends keeping the current pool config: the vm pools and `isolate: false` all break tests. ## To test - `pnpm install --frozen-lockfile` succeeds with no `minimumReleaseAgeExclude` entry for vitest. - CI: Studio unit tests, ui, ui-patterns, www, docs, and typecheck/lint should all be green. The lint ratchet was checked locally: warning counts on touched Studio files are identical to master. - `pnpm test:studio` locally passes with coverage (588 files, 6240 tests). - Open a Studio test that uses `toBeInTheDocument` in your editor and confirm no type errors on jest-dom matchers, in Studio and in `packages/dev-tools`. - Known pre-existing failures unrelated to this PR: one dev-tools test (`getEventCountBadge` capped pill) fails on master too. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit ## Tests - Improved test coverage for JSON validation and mobile navigation behavior. - Updated test setup, cleanup, environment configuration, and matcher support across application and shared package suites. - Removed obsolete coverage for alternate MCP transport selection. ## Chores - Streamlined TypeScript path resolution and Vitest reporter output handling. - Updated testing libraries and Vitest tooling across documentation, Studio, website, and shared packages. - Added Vitest reporter output to ignored files. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Alaister Young <10985857+alaister@users.noreply.github.com> Co-authored-by: Ivan Vasilov <vasilov.ivan@gmail.com> |
||
|
Anthony Lio
|
b8b92fe566 |
fix(www): careers page error (#50185)
## What kind of change does this PR introduce?

bug fix careers page on anchor link click

## What is the current behavior?

on `/careers`, clicking "open positions", scrolling down and back up,
then clicking it again crashes the page

## What is the new behavior?

destructuring defaults on the page props, so an empty-props render is
harmless instead of fatal _ prefetch still returns `{}`, but the
sequence now renders normally instead of throwin

<!-- This is an auto-generated comment: release notes by coderabbit.ai
-->

## Summary by CodeRabbit

* **Bug Fixes**
* Improved the careers page so it renders correctly when job listings,
placeholder job details, or contributor information are unavailable.

<!-- end of auto-generated comment: release notes by coderabbit.ai -->
|
||
|
Danny White
|
1131e3e2ce |
fix(ui): default Button variant to default instead of primary (#50160)
## What kind of change does this PR introduce? Bug fix / design-system alignment for the legacy `Button` from `ui`. ## What is the current behavior? Omitting `variant` on the legacy `Button` falls back to brand-green `primary`. That makes accidental greens easy, and it is hard to spot the real main action on busy pages. ## What is the new behavior? - Legacy `Button` now defaults to neutral `default` - Intentional primary CTAs (create, save, submit, marketing CTAs, and matching `ButtonTooltip` usages) now set `variant="primary"` so their appearance is unchanged - Neutral actions that previously relied on the old fallback (cancel, close, back, dashboard nav, and similar) become grey/white - Design-system docs updated; regression tests cover the new default `Button_Shadcn_` is unchanged. It already uses its own CVA default. This is PR 1 of 2 in a stack. PR 2 drops now-redundant `variant="default"` props. ## To test Studio (http://localhost:8082): - `/sign-in`: Sign in stays green - Open a project → Database → Tables: New table stays green - Auth → Users → Invite: Invite user stays green; Cancel / dismiss controls stay neutral - Project Settings → General: edit a field so Cancel and Save appear. Cancel is neutral, Save is green Design system (http://localhost:3003): - Components → Button: default demo is neutral; primary demo is green; featured preview is the default variant Marketing (optional): - www header: Start your project stays green; logged-in Dashboard is neutral <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit - **Style** - Buttons now default to a neutral style, while primary actions across Studio, documentation, marketing pages, forms, dialogs, and error states use prominent primary styling. - Updated button examples and previews clarify the distinction between default and primary variants. - Event registration now includes a directional arrow icon. - **Tests** - Added coverage confirming default button styling and explicit primary styling behave as expected. - Updated related test fixtures to use primary styling where appropriate. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Miranda Limonczenko
|
23a5bd4707 |
fix: update inbound links to the pooling guide (#50187)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? Bug fix. Link string changes only, no content changes. ## What is the current behavior? Nine inbound links in `apps/www` and `apps/studio` point at anchors on the connecting to Postgres guide that don't exist. All nine are already broken on production today: `#connection-pooler`, `#connection-pool`, `#how-connection-pooling-works`, `#serverside-poolers`, and `#connecting-with-drizzle` are all missing from the live page. #49869 moves the pooling content to a child page, so these links need current destinations either way. ## What is the new behavior? Point each link at the page that holds the content now. - **Studio, 3 links.** The Connect sheet's Drizzle link goes to the Drizzle guide. The connection pooling and pooling modes links go to `pooling-and-limits#how-connection-pooling-works`. - **www, 6 links.** Three blog posts, the Heroku comparison page, and the Dedicated poolers feature entry go to `pooling-and-limits`. The feature entry uses `#shared-pooler`. ## Additional context Split out of #49869. These paths belong to `@supabase/marketing` and `@supabase/Dashboard` in CODEOWNERS, and pulling both teams into a docs-only restructure for nine link strings isn't a good trade. Merge after #49928. The destinations don't exist on production until the docs pages land. ## Manual testing 1. Open [Supavisor: Scaling Postgres to 1 Million Connections](https://zone-www-dot-com-git-fix-pooler-docs-links-supabase.vercel.app/blog/supavisor-1-million). The "connection pooling" link in the opening paragraph resolves to `connecting-to-postgres/pooling-and-limits#how-connection-pooling-works`. 2. Open [Dedicated poolers](https://zone-www-dot-com-git-fix-pooler-docs-links-supabase.vercel.app/features/dedicated-poolers). The docs link resolves to `pooling-and-limits#shared-pooler`. 3. Open [Supabase vs Heroku Postgres](https://zone-www-dot-com-git-fix-pooler-docs-links-supabase.vercel.app/alternatives/supabase-vs-heroku-postgres). Both connection pooling links resolve to `pooling-and-limits#how-connection-pooling-works`. 4. Open [Connection pooling and limits](https://docs-git-docs-connecting-to-postgres-technical-supabase.vercel.app/docs/guides/database/connecting-to-postgres/pooling-and-limits) on the #49928 docs preview. The `how-connection-pooling-works` and `shared-pooler` headings both render with those IDs. 5. Open the Connect dialog on any project. Under Drizzle, the docs link opens the Drizzle guide. 6. Open Database settings, then Connection pooling. The pooler link opens Connection pooling and limits. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Documentation** * Updated connection pooling links across Studio, product pages, blogs, and comparison content to point to the relevant pooling guidance. * Refined links for Drizzle ORM, dedicated poolers, direct connections, and shared poolers. * Improved navigation to specific documentation sections explaining connection pooling modes and behavior. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
shaziya
|
fe0b18efb8 |
Add blog post: Supabase is now available in Gemini Enterprise (#50154)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? New blog post announcing the Supabase connector in Google Cloud Gemini Enterprise, publishing 2026-09-09. ## What is the current behavior? N/A — new content. ## What is the new behavior? - Adds `apps/www/_blog/2026-09-09-supabase-is-now-available-in-gemini-enterprise.mdx` (live at `/blog/supabase-is-now-available-in-gemini-enterprise`) - Adds og/thumb images from the Notion draft under `apps/www/public/images/blog/2026-09-09-supabase-is-now-available-in-gemini-enterprise/` - Adds two new author entries to `authors.json`: `shaziya_bandukia` and `elsa_heffernan` (plus Elsa's avatar image) - Embeds the launch video (YouTube `IUb6W60S9Wg`) Verified locally: post page renders with both authors, TOC, tags, and video embed; post appears as the featured card on `/blog`; og:image meta resolves. ## Additional context **Before merging:** - [x] ~Swap the two "Get started" links~ — CTA now points to the partner catalog listing (`/partners/catalog/google-gemini`) - [ ] Marketing +1 in #team-marketing <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit ## Summary by CodeRabbit - **New Content** - Added a blog post announcing Supabase’s prebuilt connector for Google Cloud Gemini Enterprise. - Covers natural-language queries, real-time data retrieval, multi-tool responses, access controls, connection steps, and edition-specific setup. - Includes a product video, partnership details, and links to connect or start a Supabase project. - Added author profiles for Elsa Heffernan and Shaziya Bandukia. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Francesco Sansalvadore
|
58e77483b4 |
chore(www): add open position to careers btn (#50139)
Add number of open position on the main cta button in the careers page. ## Before <img width="1328" height="614" alt="Screenshot 2026-09-08 at 16 57 24" src="https://github.com/user-attachments/assets/7c640e52-afdf-4e77-9705-fe539ed045a7" /> ## After <img width="1352" height="639" alt="Screenshot 2026-09-08 at 16 57 05" src="https://github.com/user-attachments/assets/40c265dd-b28e-44e7-9170-f45a330edfbb" /> <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * The careers page now displays the current number of open positions. * The “Open positions” call-to-action includes the position count and uses a medium-sized button style. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
|
fb28b70fe7 |
Update PostgresConf SJC 2026 contest page content (#50112)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? Content update to a `/go` landing page. ## What is the current behavior? The PostgresConf San Jose 2026 contest page (`supabase.com/go/postgresconf-sjc-2026/contest`) shows a "Learn about Multigres" CTA linking to multigres.com, a "Conference Talk: Thursday, April 23, 2026 2:30pm PDT" line, and a contest entry deadline of Monday, May 4, 2026. ## What is the new behavior? - Removed the outdated "Conference Talk" date/time line - Changed the CTA to "Watch the webinar," linking to the recording (https://www.youtube.com/watch?v=ahhQ0n1SHiQ) - Updated the contest entry deadline to Monday, September 14, 2026 at 12:00 PM PST ## Additional context Content-only change to `apps/www/_go/events/postgresconf-sjc-2026/contest.tsx`. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit - **Content Updates** - Updated the event page to link to the webinar recording with a “Watch the webinar” label. - Changed the contest deadline to September 14, 2026, at 12:00 PM PST. - Removed the talk description from the event page. <!-- end of auto-generated comment: release notes by coderabbit.ai --> Co-authored-by: Wendie Cheung <wendie.cheung@supabase.io> Co-authored-by: Claude Sonnet 5 <noreply@anthropic.com> |
||
|
Joshen Lim
|
ac0d4563d6 |
Add GH token for fetchAgentSkills to mitigate rate limits (#50106)
## Context As per PR title - just a nice to have as our `www` preview builds occasionally fail, likely due to rate limits on the GH API Env var `AGENT_SKILLS_GITHUB_TOKEN` has been added to the `www` app on Vercel <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Chores** * Added optional GitHub authentication support for retrieving agent skills. * Preserved existing request behavior when no authentication token is provided. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Alaister YoungandAlaister Young
|
ec1029dff0 |
chore: migrate from clsx + tailwind-merge to shadcn-ui/cn (#49938)
Migrates the repo off `clsx` + `tailwind-merge` to [shadcn-ui/cn](https://github.com/shadcn-ui/cn). Every app and package already gets `cn` from `packages/ui`, so the swap happens in that one helper and flows through to Studio, docs, www, and the rest. **Changed:** - `packages/ui` `cn` helper now uses `createCn` from `cn/config`, keeping the custom `card`/`content` spacing scale so `p-card` still overrides `p-4`. It has an explicit signature and re-exports `ClassValue`. - The four www Launch Week files that imported the `ClassValue` type from `clsx` now import it from `ui`. - `blocks/vue` local `lib/utils.ts` re-exports `cn` from the package. - Comments/README that referenced tailwind-merge. **Removed:** - Direct `clsx` and `tailwind-merge` deps from `ui`, `ui-patterns`, `www`, and `blocks/vue`. `ui-patterns` and `www` declared them without importing. **Added:** - `packages/ui/src/lib/utils/cn.test.ts` covering clsx-style joining, conflict resolution, the custom spacing scale, and variant handling. Not migrated: the standalone apps under `examples/`. They're outside the workspace and mostly on Tailwind v3, which `cn` doesn't support. Lockfile note: after merging master, the lockfile diff is only the intended swap (`clsx` and `tailwind-merge` out, `cn@0.2.5` in). `tailwind-merge` stays in the lockfile as a transitive dep of a third-party package. Release-age note: this sat in draft with a temporary `minimumReleaseAgeExclude` entry for `cn` while `cn` was inside the workspace's 3-day `minimumReleaseAge` window. That window has closed, so the exclusion is gone and nothing bypasses the release-age gate. ## To test - `pnpm install --frozen-lockfile` succeeds with no `minimumReleaseAgeExclude` entry for `cn`. - `pnpm --filter ui test` – new `cn.test.ts` passes, including `cn('p-4', 'p-card')` → `p-card`. - Typecheck passes for studio, ui, ui-patterns, vue-blocks. www typecheck panics under tsgo on master already (pre-existing, unrelated); it passes with the JS `tsc` binary. - Spot-check Studio locally: class overrides still win in the usual places (e.g. `CodeEditor` height, `Button` variants with a custom `className`). https://claude.ai/code/session_01MkAt16tsPRDTm9oB5Jr8Ub <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Improvements** * Standardized Tailwind class merging across shared UI utilities while preserving conditional classes, custom spacing classes, and variant behavior. * Updated related components and examples to use the standardized class-merging utility. * **Tests** * Added coverage for conditional class handling, conflicting utility resolution, custom spacing classes, and variant separation. * **Documentation** * Updated usage guidance to reflect the standardized Tailwind class-merging approach. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Alaister Young <10985857+alaister@users.noreply.github.com> |
||
|
|
e0280cb650 |
docs: restructure observability navigation and overview (#49505)
<!-- CURSOR_AGENT_PR_BODY_BEGIN --> ## Stack Draft stack extracted from `docs/monitoring`. Merge bottom-up. The troubleshooting *catalog* rewrite (`content/troubleshooting` and the Diagnosing UI) stays out of scope. 1. #49503 move inspect and advisors 2. #49501 split Studio logs from ClickHouse queries 3. #49500 treat reports as signal dashboards 4. #49502 add Observe the data hub 5. #49506 add agent setup components 6. #49504 add hire-an-agent templates 7. **#49505** restructure observability nav, overview, Detecting, and flatten Observe the data ← **this PR** ## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? Docs update. Top layer in the observability stack. ## What is the current behavior? The section is still titled Monitoring and Debugging, with a Debugging / Monitoring split that does not match the new pages. The debugging guide is still the master layer-isolation + symptom table. Observe the data is split into “what data” vs “where to observe it,” which duplicates the source pages. ## What is the new behavior? - Section title is Observability - Overview groups Observe the data, Detect and resolve, Hire an agent, and Export - **Observe the data is flattened by source.** Logs, Metrics API, Database, Advisors, and Reports each list where to read that source. There is no separate MCP/API/CLI/Studio nav group. - **Observe vs Detecting:** Observe is the catalog (what exists, how to access it). Detecting is how to *use* those sources to pick up a Health / Security / Performance / Usage signal. Named errors skip to Diagnosing. - Studio Logs sits under Logs. Reports sits beside the other sources. - Troubleshooting stays in the global menu and also appears as Diagnosing under Detect and resolve ## Additional context This is the last PR in the stack. Together the seven PRs reconstruct the `docs/monitoring` observability IA and guide content, without shipping the troubleshooting catalog overhaul. <!-- CURSOR_AGENT_PR_BODY_END --> <div><a href="https://cursor.com/agents/bc-a3cb5ece-925b-4046-b58a-5d69e9a9d794?cursor_ref=pr_footer&cursor_cta=open_in_web"><picture><source media="(prefers-color-scheme: dark)" srcset="https://cursor.com/assets/images/open-in-web-dark.png"><source media="(prefers-color-scheme: light)" srcset="https://cursor.com/assets/images/open-in-web-light.png"><img alt="Open in Web" width="114" height="28" src="https://cursor.com/assets/images/open-in-web-dark.png"></picture></a> <a href="https://cursor.com/background-agent?bcId=bc-a3cb5ece-925b-4046-b58a-5d69e9a9d794&cursor_ref=pr_footer&cursor_cta=open_in_cursor"><picture><source media="(prefers-color-scheme: dark)" srcset="https://cursor.com/assets/images/open-in-cursor-dark.png"><source media="(prefers-color-scheme: light)" srcset="https://cursor.com/assets/images/open-in-cursor-light.png"><img alt="Open in Cursor" width="131" height="28" src="https://cursor.com/assets/images/open-in-cursor-dark.png"></picture></a> </div> --------- Co-authored-by: Cursor Agent <cursoragent@cursor.com> Co-authored-by: Saxon Fletcher <SaxonF@users.noreply.github.com> Co-authored-by: Nik Richers <nik@validmind.ai> |
||
|
|
0bbd64743c |
docs: move inspect and advisors into observability (#49503)
<!-- CURSOR_AGENT_PR_BODY_BEGIN --> ## Stack Draft stack extracted from `docs/monitoring`. Merge bottom-up. Troubleshooting / debugging-guide rewrite is out of scope. 1. **#49503** move inspect and advisors ← **this PR** 2. #49501 split Studio logs from ClickHouse queries 3. #49500 treat reports as signal dashboards 4. #49502 add Observe the data hub 5. #49506 add agent setup components 6. #49504 add hire-an-agent templates 7. #49505 restructure observability nav and overview ## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? Docs update. First layer in the observability stack. ## What is the current behavior? Inspect and advisors live under Database (`/guides/database/inspect`, `/guides/database/database-advisors`). Observability readers have to leave the monitoring section to find them. ## What is the new behavior? - Moves inspect into `/guides/monitoring-and-debugging/inspect` - Adds `/guides/monitoring-and-debugging/advisors` (replaces the Database Advisors page) - Adds redirects and updates Studio/docs links so old URLs keep working - Adds both pages to the existing Monitoring nav so they are discoverable before the later IA PR ## Additional context Inspect and advisors pages render as standard MDX. Redirects cover `/docs/guides/database/inspect`, `/docs/guides/database/database-advisors`, and `/docs/guides/database/database-linter`. Debugging-guide content is unchanged except the inspect URL. ## Self-review - No leftover `/guides/database/inspect` or `/guides/database/database-advisors` links in docs guides or Studio linter/AI surfaces (historical blog posts left as-is) - Smoke test path updated to `/docs/guides/monitoring-and-debugging/advisors` <!-- CURSOR_AGENT_PR_BODY_END --> <div><a href="https://cursor.com/agents/bc-a3cb5ece-925b-4046-b58a-5d69e9a9d794?cursor_ref=pr_footer&cursor_cta=open_in_web"><picture><source media="(prefers-color-scheme: dark)" srcset="https://cursor.com/assets/images/open-in-web-dark.png"><source media="(prefers-color-scheme: light)" srcset="https://cursor.com/assets/images/open-in-web-light.png"><img alt="Open in Web" width="114" height="28" src="https://cursor.com/assets/images/open-in-web-dark.png"></picture></a> <a href="https://cursor.com/background-agent?bcId=bc-a3cb5ece-925b-4046-b58a-5d69e9a9d794&cursor_ref=pr_footer&cursor_cta=open_in_cursor"><picture><source media="(prefers-color-scheme: dark)" srcset="https://cursor.com/assets/images/open-in-cursor-dark.png"><source media="(prefers-color-scheme: light)" srcset="https://cursor.com/assets/images/open-in-cursor-light.png"><img alt="Open in Cursor" width="131" height="28" src="https://cursor.com/assets/images/open-in-cursor-dark.png"></picture></a> </div> <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit - **New Features** - Added a centralized Advisors guide for security and performance checks. - Updated database inspection guidance with live Postgres statistics, cache hit-rate context, and query-analysis resources. - **Documentation** - Reorganized Advisors and database inspection content under Monitoring and Debugging. - Updated navigation, cross-references, in-product help links, and CLI documentation links. - Added permanent redirects from previous documentation URLs to preserve access. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Cursor Agent <cursoragent@cursor.com> Co-authored-by: Saxon Fletcher <SaxonF@users.noreply.github.com> Co-authored-by: Nik Richers <nik@validmind.ai> |
||
|
Nik RichersandNik Richers
|
8a41a74e36 |
fix(www): prevent mobile blog layout overflow (#49983)
## I have read the CONTRIBUTING.md file. YES ## What kind of change does this PR introduce? This PR fixes a mobile layout bug on blog posts where long unwrapped URLs made the article column wider than its flex parent. With `justify-center`, that overflow centered the column and clipped content on both sides. It also hardens the reading progress bar so it no longer uses `100vw`, matching the overflow-safe pattern already used on changelog prose. ## What is the current behavior? - On mobile Safari, `/blog/are-supabase-docs-agent-friendly` shifts left with empty space on the right and clipped title/body text - A raw long URL in a blockquote (`row-level-security.md`) expands the flex column past the parent width - The reading progress fill uses `w-screen` (`100vw`) with a negative `translate3d`, which can widen layout outside the blog `overflow-x-clip` shell ## What is the new behavior? - Blog main column uses `min-w-0 w-full` so flex children cannot outgrow the parent - Blog prose uses `wrap-break-word` (same as changelog) so long URLs wrap - Scroll progress bar uses parent width plus `overflow-hidden` instead of `w-screen` ## Additional context - Branch: `fix-docs-agents-blog-post-on-mobile` - Files: `apps/www/components/Blog/BlogPostRenderer.tsx`, `apps/www/components/ScrollProgress.tsx` - Verification: | Check | Result | | --- | --- | | Production at 390px: title `h1` left ≈ -42 (shifted) | pass (reproduced) | | Preview at 390px: title `h1` left = 24, right = 366 | pass | | `scrollWidth === clientWidth` on preview | pass | | Progress bar still fills on scroll | pass | | Hero image still `hidden lg:block` (unchanged) | pass | ### Proof: mobile blog no longer shifts left **Verified:** production before vs PR www preview after, both captured at CSS viewport 390×844 via `page.setViewport` (not Chrome `--window-size`) | [Before (production)](https://supabase.com/blog/are-supabase-docs-agent-friendly) | [After (PR preview)](https://zone-www-dot-com-git-fix-docs-agents-blog-post-4e52df-supabase.vercel.app/blog/are-supabase-docs-agent-friendly) | | --- | --- | | 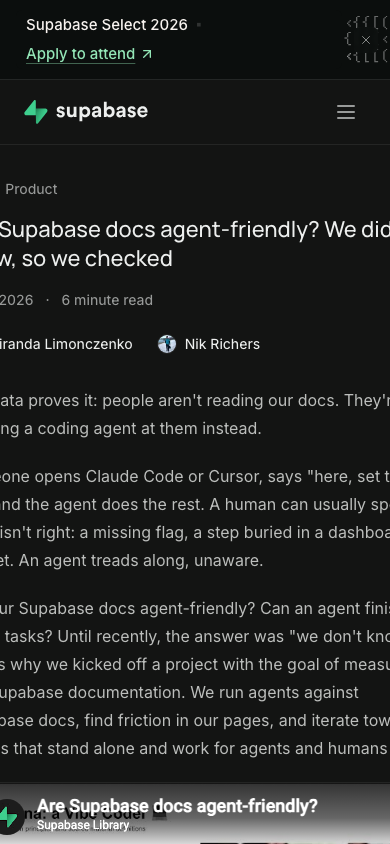 | 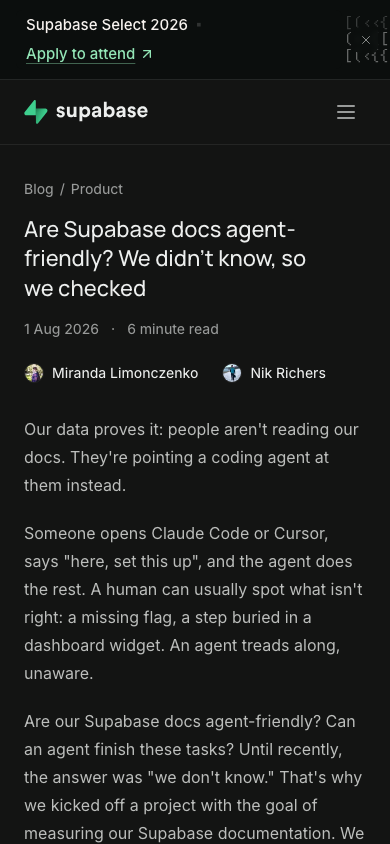 | - **Before:** https://supabase.com/blog/are-supabase-docs-agent-friendly - **After:** https://zone-www-dot-com-git-fix-docs-agents-blog-post-4e52df-supabase.vercel.app/blog/are-supabase-docs-agent-friendly ### Test plan - [ ] Open [production](https://supabase.com/blog/are-supabase-docs-agent-friendly) at ~390px and confirm the clipped/shifted layout - [ ] Open the [PR www preview](https://zone-www-dot-com-git-fix-docs-agents-blog-post-4e52df-supabase.vercel.app/blog/are-supabase-docs-agent-friendly) at ~390px - [ ] Confirm title, authors, and body are fully visible with no empty strip on the right - [ ] Confirm `document.documentElement.scrollWidth === document.documentElement.clientWidth` - [ ] Scroll and confirm the green reading progress bar still fills - [ ] Spot-check another blog post without a raw long URL for no layout regression Co-authored-by: Nik Richers <nik@validmind.ai> |
||
|
Danny White
|
e4ea619251 |
fix(www): prevent State of Startups banner collision (#49932)
## What kind of change does this PR introduce? Bug fix. ## What is the current behavior? The Supabase Select 2026 announcement is rendered outside the fixed navigation stack on `/state-of-startups`, so the navigation overlaps the banner. At shorter viewport heights, the hero's viewport-based minimum height also lets its headline sit beneath the fixed banner and navigation. ## What is the new behavior? On State of Startups routes, the announcement is rendered inside the fixed navigation stack. The hero content also reserves the stack's responsive height as its minimum top inset, keeping the headline clear when the viewport is short without shifting it at normal heights. Dismissing the banner moves the navigation back to the top without a hard-coded navigation offset. Other routes keep the existing announcement and sticky navigation layout. | Before | After | | --- | --- | | <img width="1040" height="618" alt="State of Startups 2026 Supabase" src="https://github.com/user-attachments/assets/2dc42574-1485-465c-93b1-6690e44a26e4" /> | <img width="1040" height="618" alt="State of Startups 2026 Supabase" src="https://github.com/user-attachments/assets/626374cf-8a6b-4519-bbcd-21acfc822fa0" /> | ## To test 1. Open `/state-of-startups` on the deploy preview with the Supabase Select 2026 announcement visible. 2. Confirm the announcement sits above the navigation without overlap at desktop and mobile widths. 3. Reduce the viewport height to around 500px and confirm the State of Startups headline remains below the navigation. 4. Dismiss the announcement and confirm the navigation moves to the top of the viewport without leaving a gap. 5. Open another www route and confirm the announcement remains above the sticky navigation. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Bug Fixes** * Updated the announcement banner placement on State of Startups pages so it appears within the sticky navigation area. * Preserved the existing announcement banner placement on other pages. * Increased top spacing above the State of Startups header content across mobile and desktop layouts. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Danny White
|
59af339b8f |
fix(ui): standardise nav logout label to "Sign out" (#49874)
## What kind of change does this PR introduce? Copy fix across nav dropdowns. ## What is the current behavior? Authenticated nav dropdowns use mixed logout wording: Studio shows "Log out", while www, docs, and learn show "Logout". Studio error flows already use "Sign out". | Before | | --- | | <img width="482" height="670" alt="CleanShot 2026-09-02 at 13 07 46@2x" src="https://github.com/user-attachments/assets/d87b7c18-94c0-4c1c-917e-e17e4cb16dd3" /> | ## What is the new behavior? All four nav dropdowns use **Sign out**, matching the Sign in / Sign up standard and the direction in [DOCS-1328](https://linear.app/supabase/issue/DOCS-1328). Related: [Slack thread](https://supabase.slack.com/archives/C0429V78ACX/p1787081498302919) ## To test Only Studio is possible to test (before merge) given how authentication works across apps on staging: 1. **Studio** (`/dashboard`): open the account avatar dropdown. Confirm the bottom item reads **Sign out**. 2. **www** (`supabase.com`): open the account avatar dropdown. Confirm **Sign out**. 3. **docs** (`supabase.com/docs`): open the account avatar dropdown. Confirm **Sign out**. 4. **learn** (`supabase.com/learn`): open the account avatar dropdown. Confirm **Sign out**. |
||
|
|
ef09af21f0 |
Add blog post: Are Supabase docs agent-friendly? (#49800)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? Adds a new `apps/www` blog post, "Are Supabase docs agent-friendly? We didn't know, so we checked," backdated to 2026-08-01 so it slots in chronologically between the existing 2026-07-31 Evals launch post and the 2026-08-05 post. The post writes up an eval-driven audit of the Row Level Security guide built on `supabase/evals`: the first eval run found the guide let agents grant the `anon` role write access to everything by default, and the fix that stuck was structural, moving test guidance next to the exact policy code a reader (human or agent) would copy. ## What is the current behavior? No blog post exists yet for this project. Miranda Limonczenko and Nik Richers also don't have author entries in `apps/www/lib/authors.json`. ## What is the new behavior? - New post at `apps/www/_blog/2026-08-01-are-supabase-docs-agent-friendly.mdx` - New author entries for `miranda_limonczenko` and `nik_richers` in `apps/www/lib/authors.json` - Demo video embedded via YouTube (`youtube-nocookie.com/embed`), matching the pattern used by other recent posts - New image assets under `apps/www/public/images/blog/are-supabase-docs-agent-friendly/`: the eval pass/fail chart (`eval-chart.png`) and the `og.png`/`thumb.png` hero images (cropped/resized to the standard 2400x1260 format) Check the preview: [Are Supabase docs agent-friendly? We didn't know, so we checked](https://zone-www-dot-com-git-nikrichers-blog-agent-frie-514f83-supabase.vercel.app/blog/are-supabase-docs-agent-friendly) ## Remaining work before merge - [x] Marketing +1 review per the Blog Post Process (post in `#team-marketing`) ## Additional context - Branch created directly off `origin/master` (no Linear ticket associated; this is blog content, not a docs bug/feature). - Content is adapted from an internal Notion writeup, tightened for blog voice; internal Notion discussion-thread markup and an internal Linear project link were stripped since they aren't accessible to public readers. ### Test plan - [ ] `pnpm run dev:www` and confirm `/blog/are-supabase-docs-agent-friendly` renders: title, description, both author bylines/positions, backdated date, chart image, video embed, og:image meta tag - [ ] Confirm `/blog` index card shows the new post with the thumb image - [ ] Confirm `/blog/authors/miranda_limonczenko` and `/blog/authors/nik_richers` render Verified locally (2026-09-01): all of the above pass. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit - **New Content** - Added a blog post evaluating Supabase documentation with AI coding agents, highlighting lessons for clearer, more effective guides. - Added two contributors to the author directory. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Nik Richers <nik@validmind.ai> Co-authored-by: Claude Sonnet 5 <noreply@anthropic.com> |
||
|
Prashant SridharanandCursor
|
d159f03b86 |
fix: use correct Notion database ID for VIP dinner RSVPs (#49920)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? Bug fix ## What is the current behavior? Submitting the `/go/select-2026/vip-dinner` form fails with a Notion 400: `Provided ID 37d5004b-775f-80c5-85c7-fc15377098dc is a page, not a database.` The form was writing to the Notion page that contains the RSVP database, not the database itself. ## What is the new behavior? RSVPs now write to the VIP dinner Notion database (`37d5004b775f809e8cc4e29fdec302aa`). ## Additional context No visual changes. This only updates the Notion `database_id` on the VIP dinner go page. Made with [Cursor](https://cursor.com) <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Bug Fixes** * Updated the VIP dinner RSVP form’s backend configuration to ensure submissions are directed to the correct destination. * No changes were made to the form fields, configuration, or CRM mapping. <!-- end of auto-generated comment: release notes by coderabbit.ai --> Co-authored-by: Cursor <cursoragent@cursor.com> |
||
|
Prashant SridharanandCursor
|
90f59aebbc |
Add VIP dinner go pages back (#49915)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? Feature ## What is the current behavior? The Select 2026 VIP Dinner RSVP pages were removed. VIP Experience remains live as one invite cohort for the same dinner. ## What is the new behavior? Restores `/go/select-2026/vip-dinner` and its thank-you page as a second invite cohort for the same Penny Roma dinner (October 1, 2026, 7:00 PM / 7:30 PM). RSVPs write to the VIP Dinner Notion database. VIP Experience is unchanged. ## Additional context Same event, two invite lists. Venue, time, and hosts match VIP Experience. ## Test plan - [ ] Open `/go/select-2026/vip-dinner` and confirm Penny Roma, October 1, 2026, and the RSVP form render - [ ] Submit a test RSVP and confirm a row lands in the VIP Dinner Notion database - [ ] Confirm `/go/select-2026/vip-experience` still works and writes to its own database Made with [Cursor](https://cursor.com) <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit - **New Features** - Added a Select 2026 VIP dinner event page with event details, venue information, host profiles, and seat reservation form. - Added RSVP submission and confirmation flow, including a dedicated thank-you page with confirmation details. - Added event pages to the website’s public page registry. <!-- end of auto-generated comment: release notes by coderabbit.ai --> Co-authored-by: Cursor <cursoragent@cursor.com> |
||
|
Jeremias Menichelli
|
dd57c1476f | chore: Add redirects to www for kb project (#49780) | ||
|
Prashant SridharanandCursor
|
8af724806e |
feat(www): add Deepthi to Select VIP experience and remove dinner pages (#49858)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? Feature / cleanup for Select 2026 go pages. ## What is the current behavior? The unused VIP dinner RSVP pages are still registered. The VIP experience page only lists Paul, Ant, and Sugu as hosts, and Deepthi's author photo comes from GitHub. ## What is the new behavior? - Removes `select-2026/vip-dinner` and its thank-you page - Adds Deepthi Sigireddi as a host on the VIP experience page - Overrides Deepthi's GitHub avatar with a local headshot ## Additional context Prettier was run on the changed files with the repo config (`SORT_IMPORTS=false` check matches CI). Made with [Cursor](https://cursor.com) <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit - **New Features** - Added Deepthi Sigireddi to the VIP experience hosts section. - Updated the host layout to display all hosts in a responsive grid. - Updated Deepthi Sigireddi’s profile image. - **Removed** - Removed the VIP dinner RSVP page and attendance confirmation page. - Removed these pages from the event site navigation. <!-- end of auto-generated comment: release notes by coderabbit.ai --> Co-authored-by: Cursor <cursoragent@cursor.com> |
||
|
Pamela Chia
|
121332c1ac |
feat(www): add service json-ld to homepage (#49849)
Follow-up to #49768. Agent-readiness scanners grade schema breadth by extended schema.org types (Service, FAQPage, Product); SoftwareApplication alone doesn't register, so I added a Service block whose offer catalog mirrors the products already rendered on the homepage. I also brought `/.well-known/api-catalog` up to the RFC 9727 API-catalog profile. **Changed:** - **Homepage emits Service JSON-LD**: new `serviceSchema` builder in `lib/json-ld.ts`; the offer catalog lists the six products the homepage products section renders (Database, Authentication, Storage, Edge Functions, Realtime, Vector). - **api-catalog leads with the catalog context**: `linkset[0]` now anchors the catalog URL and carries an `item` link to the Management API base, per the RFC 9727 profile; the existing service-desc context moves to `linkset[1]` unchanged. ## To test Tested on Vercel preview: - [ ] View source on the preview homepage: expect a fourth `application/ld+json` script with `"@type":"Service"` and six offerings - [ ] `curl <preview>/.well-known/api-catalog`: expect `linkset[0]` to contain an `item` array pointing at `https://api.supabase.com/v1` ## Linear - fixes GROWTH-1175 <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added structured service information to the home page, including Supabase’s platform offerings. * Added an API catalog entry linking to the Supabase API endpoint. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Pamela Chia
|
eba2aeb517 |
chore: remove stale references to the removed build:llms pipeline (#49848)
## What The `build:llms` script no longer exists in apps/docs (its output, `apps/docs/public/llms/*.txt`, is superseded by `apps/www/app/llms/[slug]/route.ts` serving the generated reference markdown directly). Four stale references remained: - `apps/docs/.gitignore`: removed the `public/llms/` entry and its comment referencing the dead script. Nothing writes to that directory anymore; if you have leftover local files there, delete them. - `apps/docs/spec/reference/README.md`: the react-server `tsx` warning cited `pnpm build:llms` as the consumer. Replaced with `pnpm embeddings`, a live script that runs under `tsx --conditions=react-server`. I verified the constraint still holds: importing `Reference.utils.ts` crashes under `--conditions=react-server` (in `next/navigation`) and loads fine under plain `tsx`. - `apps/www/pages/modules/vector.tsx`: the maintenance comment pointed at `public/llms/vector.txt`, which doesn't exist in www. The hand-maintained markdown sibling lives at `content/md/modules/vector.md`. - `.agents/skills/ask-the-docs/reference/llm-agent-parity.md`: the "In-flux / stale wiring" bullet asserted the exact `.gitignore` line this PR deletes (and its "generation path is unclear" caveat no longer holds; per-source links resolve live via `apps/www/app/llms/[slug]/route.ts`). Removed the bullet so the ask-the-docs skill doesn't report a gitignore entry that no longer exists. No behavior change; docs and comments only (plus a gitignore entry). <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit - **Documentation** - Updated the embeddings documentation to use the current `pnpm embeddings` command. - Clarified where vector module content should be maintained alongside the corresponding page. - Removed outdated references to generated per-source LLM files and retired documentation describing stale generation paths. - Improved consistency between reference documentation and the current content-generation workflow. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Pamela Chia
|
3dddb60149 |
feat(www): publish agent discovery catalog and complete json-ld (#49768)
I added the agent-discovery surfaces the www app was missing: a resource catalog at `/.well-known/ard.json` plus completed structured data on the homepage. I scoped this from the agent-readiness gaps that are truthfully closable on the www side; the catalog lists only resources that already exist and serve 200 (MCP OAuth metadata, Management API OpenAPI spec, llms.txt, agent-skills index). **Changed:** - **Agents can discover our machine-readable resources from one document**: new static catalog at `/.well-known/ard.json` (Agentic Resource Discovery format); the legacy `/.well-known/ai-catalog.json` path serves the same file via rewrite, keeping a single source artifact. - **Organization JSON-LD carries verifiable company details**: adds `legalName`, a support `contactPoint`, and the registered address already public on our Terms of Service. - **Homepage declares the product as an application entity**: emits `SoftwareApplication` JSON-LD via the existing `softwareApplicationSchema` builder, same pattern as the vector module page. ## To test Tested on Vercel preview: - [ ] `curl <preview-url>/.well-known/ard.json`: expect 200 with a JSON catalog of 5 entries - [ ] `curl <preview-url>/.well-known/ai-catalog.json`: expect the same document with status 200 (rewrite, not a redirect) - [ ] View homepage page source: expect three `application/ld+json` scripts: Organization now includes `address` and `contactPoint`, and a `SoftwareApplication` block is present ## Linear - fixes GROWTH-1164 <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit - **New Features** - Added an Agent Resource Description catalog listing Supabase’s MCP, API, documentation, and agent skill resources. - Added support for the legacy AI Catalog URL through a canonical redirect. - Enhanced website structured data with software application details, legal information, support contact details, and business address. - **Tests** - Added validation ensuring discoverable `.well-known` resources are cataloged and resolve correctly. - **Chores** - Updated marketing site test coverage for `.well-known` resource changes. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Ivan Vasilov
|
02cf09212e |
chore: Remove tsconfig paths (#49770)
This PR removes all `paths` in `tsconfig.json` for all apps and packages. They were added previosly because some of the components had a `_Shadcn` suffix because of an ongoing migration. How that the migration is done, the paths can be removed. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Refactor** * Standardized shared UI component, utility, and icon imports across design-system examples and application screens. * Simplified shared component access and project configuration. * Added shared access to anchor-link helpers and animation styles. * **Compatibility** * Updated component exports and imports without changing existing behavior. * No changes to user-facing workflows, screens, or functionality. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Pamela Chia
|
8aade77966 |
fix(www): gate changelog md alternate on slug set (#49754)
Changelog entry pages advertised a `.md` alternate tag unconditionally while the page is ISR, so an entry published in the changelog repo between www deploys pointed agents at a `.md` sibling that 404s until the next build (the static file and `CHANGELOG_PAGES` are both build-time artifacts). PR #49357 made bare-URL negotiation fail closed for those entries; I gate the advertising side here the same way. **Changed:** - **No more dead `.md` links on freshly published entries**: `getStaticProps` passes a `hasMarkdownVariant` flag computed from `CHANGELOG_PAGES` membership and the page renders the alternate tag only when true. An entry published between deploys carries no tag until the build that ships its `.md` file; the set reference stays inside `getStaticProps`, so the generated module stays out of the client bundle. - **Drift coverage**: `md-alternates.test.ts` gains the changelog direction, source-level like the existing `_app.tsx` drift test; the assertion pins the full `CHANGELOG_PAGES.has(` + backtick-`changelog/${entry.slug}`-backtick + `)` expression so a dropped key prefix fails the suite, and removing the gate fails it too. **Note:** without changelog sync secrets `CHANGELOG_PAGES` is empty, so the tag never renders in local dev. Preview and prod are the verification surface. ## To test Tested on Vercel preview: - [x] Open a published changelog entry page and view source: expect `<link rel="alternate" type="text/markdown" href="/changelog/<slug>.md">` in the head — observed exact href `/changelog/19669-supavisor-1-0.md` - [x] Fetch that href: expect 200 with `content-type: text/markdown` — observed 200, `text/markdown; charset=utf-8` - [x] (added) Client-side nav from `/changelog` into an entry: alternate tag appears with that entry's slug; hopping to a second entry updates the href (no stale tag) - [x] (added) Navigating back to `/changelog`: entry tag gone; the index shows its own pre-existing `/changelog.md` alternate (hardcoded in `pages/changelog.tsx`, outside this diff), and `/changelog.md` returns 200 `text/markdown` - [x] (added) Console: zero new errors across all scenarios vs page-load baseline ## Linear - fixes GROWTH-1120 <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Bug Fixes** * Changelog pages now advertise a Markdown alternate link only when a Markdown version is available. * Prevented links to unavailable Markdown content from appearing on changelog entries. * **Tests** * Added coverage to verify correct Markdown alternate detection and rendering. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Danny White
|
8439b0c77e |
fix(www): prevent Safari publicity logo clipping (#49742)
## What kind of change does this PR introduce? Bug fix for [DEPR-658](https://linear.app/supabase/issue/DEPR-658/fix-clipped-v0-and-langchain-logos-in-safari). ## What is the current behavior? Inline publicity logos reuse the same SVG clip-path ID. Safari can resolve v0 and LangChain against another logo's clipping rectangle, causing the artwork to appear cropped or letterboxed. ## What is the new behavior? Each publicity logo uses a namespaced clip-path ID. A focused regression test verifies that SVG IDs are unique and every `url(#...)` reference has a matching definition. | Figure | | --- | | Before | | <img width="2200" height="388" alt="CleanShot 2026-08-31 at 09 58 44@2x" src="https://github.com/user-attachments/assets/99ef02e4-e436-4155-880a-6291364ea4cd" /> | | After | | <img width="2196" height="370" alt="CleanShot 2026-08-31 at 09 58 00@2x" src="https://github.com/user-attachments/assets/d36a9b83-737b-47f1-9f12-a110b3c82f23" /> | ## To test 1. Open the deploy preview homepage in Safari. 2. Scroll to “Trusted by fast-growing companies worldwide”. 3. Confirm the v0 and LangChain logos are fully visible and the other publicity logos are unchanged. |
||
|
Pamela ChiaandAleksi Immonen
|
35531ea2f4 |
feat(www): serve openapi spec at /openapi.json (#49587)
Agent-readiness scanners and agent fetchers look for an OpenAPI spec at conventional same-origin paths, but the Management API spec is only served on api.supabase.com and linked from the /.well-known/api-catalog linkset, which scanners do not read. I added a rewrite so supabase.com/openapi.json proxies the spec from its source of truth at api.supabase.com/api/v1-json, using the same fall-through proxy mechanism as /humans.txt and /evals. **Note:** no cache or CORS headers on purpose: no consumer needs them today, and the upstream response's set-cookie header defeats edge caching regardless. I rejected a checked-in copy of the spec in favor of proxying live (staleness). The /.well-known/api-catalog linkset already points at the spec (PR #44880) and is untouched here; this PR only adds the conventional same-origin path. **Merge order:** merge only after supabase/platform#37571 deploys. The spec currently ships `servers: []`, so OpenAPI consumers resolve relative paths against the fetch origin; without the platform fix this proxy would point spec-compliant clients at supabase.com/v1/*. ## To test Tested on Vercel preview: - [x] `curl -s https://<preview-url>/openapi.json | head -c 40` returns `{"openapi":"3.0.0"` - [x] `curl -sI https://<preview-url>/openapi.json` returns 200 with `content-type: application/json` - [x] `curl -sI https://<preview-url>/humans.txt` returns 200 (control: rewrite fall-through chain intact) ## Linear - fixes GROWTH-1138 <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added access to the OpenAPI specification at `/openapi.json`. * Requests are automatically routed to the API specification endpoint. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Aleksi Immonen <aleksi@supabase.io> |
||
|
Wendie CheungandWendie Cheung
|
658a5c7fee |
Update Lingo.dev customer story slug to lingodotdev (#49623)
## What kind of change does this PR introduce? Content: slug update for an already-live customer story. ## What is the current behavior? The Lingo.dev customer story (originally added in #49595) lives at `/customers/lingo-dev`. ## What is the new behavior? - Renames `apps/www/_customers/lingo-dev.mdx` to `apps/www/_customers/lingodotdev.mdx`. - Updates the `url` in `apps/www/data/CustomerStories.ts` to `/customers/lingodotdev`. - Adds a permanent redirect from `/customers/lingo-dev` to `/customers/lingodotdev` in `apps/www/lib/redirects.js`. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added a customer story highlighting Lingo.dev’s localization workflow, platform usage, security practices, results, and future plans. * **Bug Fixes** * Updated the customer story link to its new URL. * Added a permanent redirect so existing links to the previous URL continue to work. <!-- end of auto-generated comment: release notes by coderabbit.ai --> Co-authored-by: Wendie Cheung <wendie.cheung@supabase.io> |
||
|
kemal.earth
|
5802f4f83e |
fix(www): career page apply button sizing (#49647)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? Noticed this by accident, simplified the apply button area sizing on large screens. | Before | After | |--------|--------| | <img width="390" height="228" alt="Screenshot 2026-08-27 at 15 25 36" src="https://github.com/user-attachments/assets/7f49021c-1332-4a00-b19c-5544537c1cb4" /> | <img width="491" height="274" alt="Screenshot 2026-08-27 at 15 45 11" src="https://github.com/user-attachments/assets/846faff8-bd72-4141-b8d4-01d7ddd97b6d" /> | <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Style** * Improved job listing badge layout and responsiveness. * Long location names now truncate cleanly instead of overflowing. * Reduced location icon size for a more balanced presentation. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
|
292c08b7b7 |
Added new /regions page (#49306)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? Feature ## What is the current behavior? Region and data residency information is split across docs, `/security`, and legal pages. [MARKET-1866](https://linear.app/supabase/issue/MARKET-1866/package-and-display-available-regions-better-on-website) ## What is the new behavior? Adds `/regions`: a catalog of all 17 regions generated from `regions.ts`, plus what stays in-region, the Europe vs EU caveat, and links to the DPA, GDPR guide, sub-processor list, and security page. Regions is in the footer under Security & Compliance. The security page residency card now links here. ## Test plan - [ ] Open `/regions` in light and dark mode - [ ] Confirm the region count and list match `packages/shared-data/regions.ts` - [ ] Confirm footer Regions link and `/security` residency link go to `/regions` Made with [Cursor](https://cursor.com) <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit - **New Features** - Added a Regions page showcasing available AWS regions by geography. - Added an interactive map and region list with selection, hover states, keyboard accessibility, and residency badges. - Included data residency guidance, legal resources, and a call-to-action for next steps. - Added Regions links in the site footer and security documentation. - **Documentation** - Updated agent skill resources with expanded troubleshooting and operational guidance. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Cursor <cursoragent@cursor.com> Co-authored-by: Francesco Sansalvadore <f.sansalvadore@gmail.com> |
||
|
Pamela Chia
|
164de2c347 |
feat(www): markdown 404 for markdown-negotiated paths (#49596)
Nonexistent paths return a real 404 everywhere, but always with an HTML body, even when the client asked for markdown via `Accept: text/markdown` or a `.md` suffix. Middleware can't fix this: it gates on a static slug allowlist and can't know a path will 404. I added two `fallback` rewrites (`.md` suffix; Accept header containing `text/markdown` or `text/*`) that run only after every route has failed to match and route the request to a small `md-404` handler returning a short markdown 404 pointing at /docs, /sitemap.xml, and /llms.txt. Real pages are structurally unaffected. **Note:** `lib/rewrites.js` is untouched (the plain rewrites array became the `afterFiles` phase), so #49587 merges independently. I updated next.config.test.ts's rewrites assertion for the phased shape; it now also pins the two fallback rules. ## To test I verified on the Vercel preview: - [x] `curl -s -D - -H "Accept: text/markdown" <preview>/definitely-not-a-page` (404, `Content-Type: text/markdown`, body with the three pointers) - [x] Same URL with a browser Accept header (existing HTML 404, unchanged) - [x] `curl -s -D - <preview>/definitely-not-a-page.md` (markdown 404) - [x] `curl -s -D - -H "Accept: text/markdown" <preview>/auth` (200 markdown, unchanged) and `<preview>/support` (200 HTML, unchanged) - [x] `/homepage.md` still 308s to `/index.md` (redirects phase wins); `Accept: text/*` gets the markdown 404, matching real-page negotiation Known boundary: `/changelog/<unknown>` keeps the HTML 404 body (pages-router `fallback: 'blocking'` routes take priority over fallback rewrites per Next docs); the status is still 404, verified on the preview. ## Linear - fixes GROWTH-1142 <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit - **New Features** - Added Markdown-formatted 404 responses for unmatched documentation and `.md` page requests. - Included helpful documentation links in not-found responses. - Requests that explicitly accept Markdown now receive a consistent Markdown response. - Added appropriate response headers for security, caching, and content variation. - **Bug Fixes** - Improved routing for unmatched Markdown paths, ensuring they are handled by the appropriate not-found response instead of returning an unexpected format. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Wendie CheungandWendie Cheung
|
ff5376c9f0 |
Add go page: Postgres Summit US 2026 contest (#49597)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? Feature — new marketing landing page (`/go` page). ## What is the current behavior? No landing page exists yet for Supabase's presence at Postgres Summit US 2026 (Sept 30 - Oct 2, 2026, NYC). ## What is the new behavior? Adds a contest landing page and thank-you page, modeled on the existing `pgconf-dev-2026/contest` go page pattern: - `supabase.com/go/postgres-summit-2026/contest` — MacBook Neo giveaway entry page, featuring the "Everything to know about Postgres Locks" talk by Brian Brennglass (Supabase), Wed Sept 30, 4:00–4:50 PM EDT, Rossi Intermediate room - `supabase.com/go/postgres-summit-2026/contest/thank-you` — confirmation page after entry - Registered both in `apps/www/_go/index.tsx` with a `// remove after October 31, 2026` cleanup marker, since this is a temporary event page - HubSpot form wired to a real form GUID, with field mapping verified against the form's actual internal property names (note: `company_name` maps to `name` on the HubSpot **Company** object, not the usual `company` Contact property — verified directly in the HubSpot form editor rather than assumed) Verified locally: both pages render correctly (hero, speaker section with headshot, how-to-enter steps, form) via `pnpm --filter www dev`. ## Additional context - Contest entry deadline is currently set to Monday, October 12, 2026, 12:00 PM PDT — a placeholder estimate (~12 days post-event, matching the pattern used on other event contest pages), not sourced from an official deadline. Flagging for review before this goes live. - No talk-slides link exists yet for this session, so the "View session details" CTA links to the official postgresql.us session page instead. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added a Postgres Summit US 2026 contest landing page featuring prize information, event content, entry instructions, and a contest entry form. * Added a thank-you page with submission confirmation, contest details, onboarding guidance, and links to the dashboard and website. * Added registration for both pages with availability through October 31, 2026. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Wendie Cheung <wendie.cheung@supabase.io> |
||
|
|
8291ed1401 |
Add Lingo.dev customer case study (#49595)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? Content: new customer case study for supabase.com/customers. ## What is the current behavior? Lingo.dev doesn't have a case study on supabase.com/customers yet. Source content: [Notion case study doc](https://app.notion.com/p/supabase/Lingo-dev-3c05004b775f81e5a936dd40f77e2781) (Linear: [MARKET-1468](https://linear.app/supabase/issue/MARKET-1468/case-study-lingodev)). ## What is the new behavior? - Adds `apps/www/_customers/lingo-dev.mdx`: how Lingo.dev runs retrieval augmented localization on Supabase Database, Vector, Auth, and Storage, and clears every enterprise security review (Mistral AI, Solana Foundation, Veriff) without a database question raised. - Registers the story in `apps/www/data/CustomerStories.ts` so it surfaces on the customer stories listing. - Adds logo (on-light/on-dark) and founder headshot assets for Max Prilutskiy and Veronica Prilutskaya. ## Additional context Ran through `supabase-writing` and `humanize` style passes before finalizing copy. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Content** * Added a customer story highlighting Lingo.dev’s localization platform, architecture, security practices, and operational results. * Added the story to the customer stories collection with supporting imagery, description, and call-to-action details. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Wendie Cheung <wendie.cheung@supabase.io> Co-authored-by: Claude Sonnet 5 <noreply@anthropic.com> |
||
|
Pamela Chia
|
013af4ed58 |
feat(www): homepage json-ld, canonical, 404 links (#49533)
An agent-readiness scan of supabase.com (is-agentic.com, public report) flagged that the homepage serves no structured data and no canonical tag in raw HTML, and that the 404 page gives crawlers and agents no recovery path. I fixed both. **Changed:** - **Homepage structured data**: the raw HTML now carries Organization and WebSite JSON-LD plus `<link rel="canonical" href="https://supabase.com">`. The schema builders already existed in `lib/json-ld.ts` but were never wired to any page; this reuses the exact inline-script pattern from the blog post pages. The canonical is hardcoded to the production origin on purpose: `SITE_ORIGIN` resolves to the branch URL on previews. - **404 recovery links**: the 404 body now links to the docs, the sitemap, and llms.txt, so a dead URL leads somewhere instead of a dead end. The decorative giant "404" backdrop is a `div` instead of a second `h1`, marked `aria-hidden`, and gets `pointer-events-none`: browser testing showed the absolutely positioned backdrop was silently swallowing clicks on the new links (positioned elements paint above static siblings for hit-testing even when visually behind). - **Drift-guard test**: `md-alternates.test.ts` asserted the literal one-liner `alternates: mdAlternates('<slug>')`, which the canonical wrapper breaks. I broadened the assertion to accept the spread shape too; the rule it guards (every markdown-served slug advertises its `.md` sibling) is unchanged and still enforced. ## To test Tested locally against the dev server: - [x] `curl -s localhost:3000` and parse the two `application/ld+json` blocks: both valid JSON, types Organization and WebSite - [x] `curl -s localhost:3000 | grep canonical`: expect `<link rel="canonical" href="https://supabase.com"/>`, with the existing `text/markdown` alternate link still present - [x] `curl -s localhost:3000/some-nonexistent-page`: expect HTTP 404 with hrefs to `/docs`, `/sitemap.xml`, `/llms.txt` and exactly one `<h1>` in the body On the Vercel preview (verified via curl + Playwright browser run): - [x] View source on the preview homepage: the two JSON-LD blocks present and a canonical pointing at `https://supabase.com` (prod origin, even on the preview host) - [x] Open a nonexistent preview URL: 404 page renders the new link row under the "Head back" button, visually unchanged otherwise (screenshots in session records) - [x] Added: click each recovery link: element hit-testing returns the anchor for all three, and clicking Sitemap navigates to a valid `/sitemap.xml` document (this check caught the pointer-events regression, fixed in this PR) ## Linear - Part of GROWTH-1124 (kept open: remaining scan findings are tracked in a sub-issue) <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit - **SEO & Discoverability** - Added canonical URL metadata and structured organization and website information to the homepage. - Improved 404 page navigation with links to Documentation, Sitemap, and `llms.txt`. - **Accessibility** - Updated the 404 page’s decorative background marker to be non-interactive and hidden from screen readers. - Added reduced-motion handling for page transitions. - **Tests** - Updated metadata validation to support multiple alternate metadata configurations. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Pamela Chia
|
6d4263bf1a |
fix(www): pricing table spacing and sticky offset (#49532)
Multi-line cells in the /pricing comparison table rendered as one cramped block once lines wrapped: the stacked values had no gap between entries, and the continuation lines' `leading-4` is a no-op at `text-xs`. At the same narrow desktop widths (1024 to 1280px), category headers clipped behind the sticky plan header because their hardcoded `top-[108px] xl:top-[84px]` offsets desync from the plan header's variable height. **Changed:** - **Value cells get vertical padding**: the value tds were `pl-6 pr-2` with no vertical padding, so tall multi-line cells pressed text against the row dividers; they now carry `py-5` like the row-label column (text ink sits ~21px off both borders, measured). - **Stacked price lines read as separate entries**: `gap-2` between entries while wrapped lines inside one entry stay tight (`leading-4`), so each price reads as its own block. Two earlier iterations that only widened the entry gap (`gap-1`, then `gap-2` with looser `leading-5` wraps) reviewed as still-cramped; the missing cell padding was the dominant cause. Mobile untouched. - **Category headers never clip behind the plan header**: a ResizeObserver measures the sticky thead's real height and publishes `--pricing-category-top` as a CSS variable on the table; the category header consumes it via `var()`, keeping the old 108px/84px values as pre-hydration fallbacks so SSR paint is unchanged. Runs in a layout effect so the first client paint already has the measured value. **Note:** I rejected re-tuning the hardcoded offsets: numbers desyncing from the header's content-driven height is the root cause, and new constants re-break on the next copy or breakpoint change. ## Before / after **Before** (prod: multi-line prices pressed against the row dividers as one dense block; rows clipped under the sticky category header): <img width="1442" height="450" alt="pr-before" src="https://github.com/user-attachments/assets/91d428df-e04c-4494-b454-84a8a46b3ddd" /> **After** (this PR: padded cells, each price its own block, headers pin flush): <img width="1497" height="375" alt="pr-after" src="https://github.com/user-attachments/assets/5aa2c3c7-b41e-42c0-8159-bb294a5d1dea" /> ## To test Tested on the Vercel preview (Playwright, measured values in parens): - [x] At a 1024 to 1280px viewport, open /pricing and find the Pipelines row: the 3 price lines in the Pro and Team cells read as distinct blocks (row-gap 8px between entries, tight 16px line boxes within an entry, 20px cell padding; verified on localhost pre-push and on the preview, light and dark) - [x] Multi-line cell text no longer touches the row dividers: ~21px from border to text ink top and bottom (was 0-3px) - [x] At the same width, scroll the whole comparison table: Database and Auth section headers pin flush below the plan-price header, with no row text clipped between them (pinned category top within 0.2px of thead bottom) - [x] At ~1800px wide: Pipelines and Point in time recovery (Enterprise) cells show the same separated lines (PITR Enterprise is a single wrapping string, renders cleanly) - [x] Resize across 1280px after load: category headers stay flush under the plan header (ResizeObserver refires; same 0.2px alignment after 1900px to 1150px resize without reload) - [x] Below 1024px: the mobile comparison view is unchanged - [x] Added: cold navigation to /pricing#compare-plans lands with `--pricing-category-top` already applied (151px at 1150px width) and the pinned header flush - [x] Added: no new console errors versus the page's pre-existing baseline ## Linear - fixes GROWTH-1137 |
||
|
Danny White
|
b5462ee7bb |
feat(www + studio): promote Select 2026 in www and Dashboard (#49511)
## What kind of change does this PR introduce?

Feature. Promotes Supabase Select 2026 across www and the Dashboard.

## What is the current behavior?

There is no active Select promotion on www or in the Dashboard.

## What is the new behavior?

- Adds a dismissible Select 2026 banner above the www navigation.
- Adds a low-priority Banner Stack card across hosted Studio project
pages.
- Shares a lightweight pixel lockup and CSS-only motion across both
surfaces, with light, dark, and reduced-motion treatments.
- Opens the application page in a new tab and automatically expires both
placements after October 2 in San Francisco.

## To test

- Open `/database` on the www preview. Confirm the banner is legible in
light and dark mode, the complete message remains visible at a phone
width, and the CTA opens `select.supabase.com` in a new tab.
- Dismiss the www banner, then refresh the page. Confirm it stays
dismissed.
- Open any `/project/{ref}` route in the Dashboard preview. Confirm the
Select card appears in the bottom-right Banner Stack behind
higher-priority notices.
- Dismiss the Dashboard card, navigate to another project page, and
confirm it stays dismissed.


<!-- This is an auto-generated comment: release notes by coderabbit.ai
-->
## Summary by CodeRabbit

* **New Features**
* Added a time-limited Select 2026 promotional banner across the website
and Studio.
* Added responsive themed artwork, animated visuals, campaign messaging,
and an external “Apply to attend” CTA.
  * Banner dismissal preferences are saved and respected across visits.
  * Promotion automatically disappears after the campaign ends.

* **Accessibility**
* Improved announcement dismissal controls with semantic buttons and
accessible labels.
  * Added reduced-motion support for promotional artwork.

* **Bug Fixes**
* Improved product-card loading effects to prevent hydration
inconsistencies.
<!-- end of auto-generated comment: release notes by coderabbit.ai -->
|
||
|
claude[bot]andClaude
|
580af6e336 |
fix(www): stop blog tag and author breadcrumbs from becoming the page h1 (#49507)
<!-- ccr-slack-attribution --> _Requested by **Pam Chia** · [Slack thread](https://supabase.slack.com/archives/C07P3AU3J2D/p1787616624076769)_ **Before:** searching "supabase blog" on Google surfaces blog tag sitelinks titled `Blog/Tags/Supabase` and `Blog/Tags/Community`, each with the same snippet scraped from the footer newsletter form ("Get product updates and news from Supabase"). **After:** those results use the route's real title, `Blog | Supabase`, with a description specific to the tag, for example "Blog posts tagged Supabase." This change stops the visible breadcrumb on blog tag and author pages from being the page's only `<h1>`, and gives tag and category pages distinct meta descriptions. ## How this changes the Google result The bad sitelinks come from two independent mechanisms, and each half of this PR targets one of them: **Titles.** Google prefers a page's `<h1>` over its `<title>` when the two disagree, and on tag pages the only `<h1>` is the breadcrumb, whose textContent is exactly `Blog/Tags/Supabase` (JSX strips the whitespace between the children). Demoting the breadcrumb to a `<nav>` removes the conflicting heading, so Google should fall back to the route's real `<title>`: - `Blog/Tags/Supabase` becomes `Blog | Supabase` - `Blog/Tags/Community` becomes `Blog | Community` **Snippets.** The "Get product updates and news from Supabase. Subscribe ..." text is not a meta description; it is Google's own synthesized snippet, scraped from the footer newsletter form. Every tag and category page shipped the byte-identical description "Latest news from the Supabase team.", and Google discards a description duplicated across many URLs. With a unique per-page description, Google has a usable candidate again: - tag rows should show `Blog posts tagged Supabase.` / `Blog posts tagged Community.` - category rows (`Blog | Engineering`, `Blog | Product`) already had correct titles but the same scraped snippet; they should now show `Blog posts in Engineering.` / `Blog posts in Product.` Two caveats. Meta descriptions are suggestions, not directives, so Google can still synthesize its own snippet; removing the duplicate-description cause makes the supplied one much more likely to win, but does not force it. And the replacement `<h1>` is the constant sr-only `Supabase Blog` on every listing page: if Google again prefers the h1 over the title, all sitelinks would read `Supabase Blog`. A page-specific heading ("Posts tagged Supabase", "Posts by <author>") would eliminate that residual risk and is a candidate follow-up. Neither change appears in search results until Google recrawls and reprocesses these URLs (see Additional context; the tag routes are absent from the sitemap, which slows this). Requesting reindexing of a few of these URLs in Search Console would speed it up. ## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? Bug fix (SEO / accessibility), `apps/www` only. ## What is the current behavior? Two separate defects feed the same bad search result. Google prefers a page's `<h1>` over its `<title>` when the two disagree, and on tag pages the only `<h1>` is the breadcrumb. `apps/www/app/blog/tags/[tag]/TagClient.tsx:21-27` wraps `Blog` / `/` / `Tags` / `/` / `<tag>` in an `<h1>`; JSX strips the whitespace between those children, so the element's textContent is exactly `Blog/Tags/Supabase`. The route's own `<title>` is already fine (`apps/www/app/blog/tags/[tag]/page.tsx:26`). `apps/www/app/blog/authors/[author]/AuthorClient.tsx:55-60` has the identical defect. Category pages escape it because `apps/www/app/blog/BlogLayoutShell.tsx:19` counts `/blog/categories/` as a listing route and renders the sr-only `<h1>Supabase Blog</h1>` at line 23, while `CategoryClient.tsx` renders no `<h1>` of its own. Separately, every tag and category page shipped the byte-identical description `Latest news from the Supabase team.` (`apps/www/app/blog/tags/[tag]/page.tsx:27`, `apps/www/app/blog/categories/[category]/page.tsx:23`). Google discards a description reused verbatim across many pages and generates its own snippet, in this case from the footer newsletter copy at `apps/www/components/Footer/index.tsx:179`. ## What is the new behavior? - `BlogLayoutShell.tsx` — `isListingRoute` now covers `/blog/tags/` and `/blog/authors/` alongside `/blog/categories/`, via a `LISTING_ROUTE_PREFIXES` constant. Those routes now render the same sr-only `<h1>Supabase Blog</h1>` category pages already had. - `TagClient.tsx` and `AuthorClient.tsx` — the breadcrumb is now a `<nav aria-label="Breadcrumb">` instead of an `<h1>`. Every existing className, the `/` separator spans and their `px-2` padding are unchanged. The `h1` element selector in `apps/www/styles/globals.css:176-179` applies `font-heading font-medium tracking-normal`, so those three utilities move onto the `nav` to keep the rendering byte-identical. No visual change is intended; only the element and its accessible role change. - `tags/[tag]/page.tsx` and `categories/[category]/page.tsx` — `generateMetadata` now returns `Blog posts tagged ${label}.` and `Blog posts in ${label}.`, matching the shape the author route already uses (`apps/www/app/blog/authors/[author]/page.tsx:37`). Both use `startCase` from `apps/www/lib/helpers.tsx:75-81` rather than `capitalize`, so `launch-week` reads "Launch Week" and matches the filter chip label at `apps/www/components/Blog/BlogFilters.tsx:56-57`. Title and description use the same label. ## Additional context `apps/www` is owned by `@supabase/marketing` per `.github/CODEOWNERS:13`, so marketing should review this. Recovery is not immediate: Google has to recrawl these routes before the corrected titles and descriptions show up in search results. Noted follow-ups, deliberately out of scope here: - `/blog/tags/*` and `/blog/authors/*` are absent from the generated sitemap (`apps/www/internals/generate-sitemap.mjs`), which slows discovery and recrawl. - The page bodies still pass a `capitalize`-derived label to `TagClient` and `CategoryClient`, so the visible tag breadcrumb reads "Launch week" while the title now reads "Launch Week". Aligning the visible label would be a rendered-text change, so it is left for a separate PR. - `openGraph` metadata on these routes is untouched and still carries the generic copy. ### How it was tested Prettier passes on the five changed files with the repo config, in both the default and the `SORT_IMPORTS=false` mode CI uses. Full typecheck and lint could not be run in this environment (no `node_modules`); the changes are type-trivial — a `string[]`.`some()` predicate, a JSX tag swap, and two template literals over an existing exported `startCase(string): string` helper — and the diff parses clean under `tsc` with module resolution disabled. Worth a reviewer eyeballing the tag and author pages side by side against production to confirm the breadcrumb renders identically. --- _Generated by [Claude Code](https://claude.ai/code/session_0164goAzGTkGnoxzCKagJ3Hw)_ --------- Co-authored-by: Claude <noreply@anthropic.com> |
||
|
shaziya
|
e616c6d267 |
Add blog post: Enterprise-managed auth for the Supabase MCP server (#49493)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? New blog post announcing enterprise-managed auth for the Supabase MCP server, built with Anthropic and Okta. ## What is the current behavior? No blog post exists for this launch. ## What is the new behavior? Adds `/blog/enterprise-managed-auth-for-the-supabase-mcp-server` dated 2026-08-24, authored by Cemal Kılıç and Greg Richardson, with the OG and thumbnail images. Supersedes #49492 (closed by a branch rename). <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Documentation** * Announced general availability of enterprise-managed authentication for the Supabase MCP server. * Added details on Okta-based administration through Claude, user-specific roles and permissions, and centralized onboarding, offboarding, and access reviews. * Included plan availability requirements and setup guidance. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |