mirror of
https://github.com/supabase/supabase.git
synced 2026-10-09 03:15:06 +03:00
docs/debugging-guide
140
Commits
| Author | SHA1 | Message | Date | |
|---|---|---|---|---|
 Jeremias Menichelli |
f5c0074a47 | fix: visual tweaks and telemetry added to projectConfigVariables (#47532) | ||
|
Joshen Lim
|
9f1ce56322 |
Add edge log type with service filters (#47493)
## Context Couple of changes to the Unified Logs logic, mainly to align unified logs filters with legacy logs behaviour ## Changes involved - Postgrest + Storage logs will no longer overlap with edge logs source - They will specifically just pull logs from their own sources only - This will match legacy logs behaviour + also the observability overview behaviour as well - Re-introduce "API Gateway" as a log type (was there in the old UI) - Added service filters for convenience <img width="271" height="233" alt="image" src="https://github.com/user-attachments/assets/6264b7c5-e3e8-4db8-a378-4d8c46af3d62" /> <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added **API Gateway** (“Edge”) logs to Unified Logs, including new sub-filters for auth, storage, and postgrest activity. * Updated the default log selection to include API Gateway logs. * **Bug Fixes** * Improved how log types are bucketed and filtered, ensuring edge, postgrest, and storage sources display under the correct views and toggles. * Refined “connection logs” filtering so results and counts remain consistent with the selected options. * **Style** * Refined the Unified Logs filter checkbox layout and nested expand/collapse controls. * **Tests** * Updated and expanded query tests to cover the new edge filter behavior. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Pamela Chia
|
98cfe3307e |
feat(telemetry): fix creation-funnel tracking gaps (#47386)
## Summary The creation-funnel instrumentation that shipped Jun 25 (#47291, #47293) had real gaps, surfaced by the weekly telemetry audit and confirmed against production PostHog data before I touched code. The two automated reports also contradicted each other on `errorReason`; I checked production (every value is a controlled slug) and the emit path (only `useTrackFunnelError` sets it, and it only accepts classified slugs), so I left the type as-is rather than add a cross-package abstraction for a risk that cannot occur today. ## Changes - Classify HTTP 401/403/404 API errors as `unauthorized` / `forbidden` / `not_found` instead of the catch-all `other`. In production the `org_creation` `other` bucket was ~96% 401s (~1,300 real over 4 days), invisible in reason breakdowns. The status-code fallback runs after the message-pattern match, so specific reasons still win and it only rescues errors that would otherwise be `other`. - Add a single `tier` property (`tier_free` / `tier_pro` / `tier_payg` / `tier_team`) to `organization_creation_completed`, which previously carried no properties. One canonical billing slug (matching `SubscriptionTier`) instead of two overlapping plan/tier fields, so the org-creation funnel segments cleanly by tier and joins against subscription data. `tier_payg` is uncapped PRO. - Freeze the submitted tier at submit time (snapshot in `createOrg`) rather than reading live form state in the success callback, so the event records the tier that was actually created even if the user edits the form during the async payment flow. - Emit `project_creation_form_exposed` with `surface: 'vercel'` on the integration deploy-button project-creation page (the enum value existed but was never fired). Gated on the URL `slug` so the impression is captured as soon as the form renders, matching the sibling exposure hook on that page. I also checked the confirm-modal error path flagged in the insights post: it already classifies via the shared `useProjectCreateMutation.onError`, so adding instrumentation there would double-count. No change made. ## Testing These are analytics events with no UI change, so correctness is in what lands in PostHog. Post-deploy validation I will run against production (project 34344): - `dashboard_error_created` where `origin='org_creation'` and `errorReason='other'` drops ~96%, with `unauthorized` / `not_found` appearing. - `organization_creation_completed.tier` populated on 100% of new events with one of the four tier slugs. - `project_creation_form_exposed` with `surface='vercel'` goes from 0 to greater than 0. ## Linear - fixes GROWTH-948 <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added telemetry for organization creation completion that includes the selected billing tier. * Added one-time telemetry when the Vercel project creation form is exposed. * **Bug Fixes** * Improved API error classification to more accurately distinguish unauthorized, forbidden, and not found responses. * **Documentation** * Updated telemetry event definitions to require tier metadata for organization creation events. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Joshen Lim
|
1de298ff31 |
Reinstate https://github.com/supabase/supabase/pull/45143 into latest master (#47433)
## Context Previous PR was [here](https://github.com/supabase/supabase/pull/45143) but it got stale with lots of conflicts so figured it'll be easier redo it off the latest master Moves policies page from Auth to Database under an Access Control section along with Roles. This moves all existing files, applies redirects, and updates urls to point to the new route <img width="274" height="412" alt="image" src="https://github.com/user-attachments/assets/7952c185-64ae-4355-ba36-45397efe1787" /> <img width="453" height="471" alt="image" src="https://github.com/user-attachments/assets/04b3dcb3-48a5-4049-9893-d01109fb46a9" /> ## To test - [ ] Verify that policies now live under Database correctly <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added a quick navigation shortcut to open **Database > Policies (RLS)**. * **Bug Fixes** * Updated Policies and RLS-related links across the product to open the **Database policies** area (menus, command palette, context actions, alerts, and link-outs). * Added a permanent redirect from the old **auth policies** URL to the new **database policies** URL. * **Documentation** * Updated RLS Dashboard and security checklist instructions to reference **Database > Policies**. * **Tests** * Adjusted automated tests to validate the new Policies route. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
|
635b2d6050 |
docs: standardise next steps on overview pages with content listings (#47097)
## I have read the CONTRIBUTING.md file. YES ## What kind of change does this PR introduce? This PR helps standardise link sections which is useful for overview pages that frequently use similar sections such as "Next steps", "Get started", or "Examples". Six high-traffic overview pages are migrated as a pilot, with a skill in the new [supabase/docs-agent-skills](https://github.com/supabase/docs-agent-skills) repo to audit and convert the rest in a follow-on PR. Refactored from an initial YAML front matter approach per review feedback from @jeremenichelli. Now implemented as a React component and using existing linting & Markdown export functionality. A second round of review feedback further simplified the architecture: the per-listing component registry was removed in favor of a single `<ContentListings id="..." />` component backed by an ID-keyed data lookup, the listing data moved out of `apps/docs/components/` into `apps/docs/data/content-listings/`, the listing-specific link wrapper was replaced with the existing `<Link>` + `<GlassPanel>` pattern from the rest of the docs, and the headings now defer to the shared `<Heading>` from `MdxBase.shared.tsx` (no parallel marker-to-tag mapping, no typography overrides). Great feedback, thank you! 🙏 Relates to DOCS-1032. ## What is the current behavior? Authors implement these sections however they wish. As a result, overview and index pages use inconsistent patterns for orientation links: some use hand-rolled Markdown lists, some use custom panel/grid components, some use buttons, and some have no guidance about where to go next at all. There is no shared component for these sections and no analytics on those clicks. ## What is the new behavior? Authors add orientation sections in two steps: 1. Define listing data in a `.data.ts` file under `apps/docs/data/content-listings/` (for example, `storage.data.ts`). Each `ContentListingGroup` has a globally-unique `id` like `storage-get-started`. 2. Place a single `<ContentListings id="..." />` component inline in guide MDX. The ID is also the telemetry `listingId`, so the same value disambiguates the section in PostHog dashboards. Grid and list layouts, optional icons (such as `/docs/img/icons/github-icon` with `-light.svg` variants for dark mode), and external URLs are supported. Conditionals that use `$Show` around inline components are also supported, for example for auth pricing. ### Usage example from "Storage" overview page `apps/docs/data/content-listings/storage.data.ts`: ```ts export const storageGetStarted: ContentListingGroup = { id: 'storage-get-started', heading: 'Get started', description: 'Choose the bucket type that fits your use case:', type: 'grid', items: [ { title: 'Files buckets', href: '/guides/storage/quickstart', description: 'Store and serve images, videos, documents, and general-purpose files with direct URL access and row-level security.', }, { title: 'Analytics buckets', href: '/guides/storage/analytics/introduction', description: 'Store data in Apache Iceberg tables for data lakes, logs, and ETL. Query from Postgres via foreign tables with partitioning.', }, { title: 'Vector buckets', href: '/guides/storage/vector/introduction', description: 'Store embeddings and run similarity search for semantic matching, AI, and RAG. Use HNSW indexing, distance metrics, and metadata filtering.', }, ], } ``` `apps/docs/content/guides/storage.mdx`: ```mdx <ContentListings id="storage-get-started" /> ``` Renders as: <img width="689" alt="Storage Get started listing — Files, Analytics, and Vector buckets" src="https://github.com/user-attachments/assets/0d1b9531-962f-40ae-891e-b1e93ff1c939" /> <br>Exported in Markdown as: ```md ## Get started Choose the bucket type that fits your use case: - **[Files buckets](/docs/guides/storage/quickstart):** Store and serve images, videos, documents, and general-purpose files with direct URL access and row-level security. - **[Analytics buckets](/docs/guides/storage/analytics/introduction):** Store data in Apache Iceberg tables for data lakes, logs, and ETL. Query from Postgres via foreign tables with partitioning. - **[Vector buckets](/docs/guides/storage/vector/introduction):** Store embeddings and run similarity search for semantic matching, AI, and RAG. Use HNSW indexing, distance metrics, and metadata filtering. ``` Click tracking fires via PostHog (`docs_content_listing_clicked`): ```json { "action": "docs_content_listing_clicked", "custom_properties": { "targetPath": "/guides/storage/quickstart", "linkTitle": "Files buckets", "groupTitle": "Get started", "listingId": "storage-get-started" } } ``` Still finding my way around PostHog, but I verified on preview deploy that clicking a content listing on `/docs/guides/auth` sends `docs_content_listing_clicked` to `https://api.supabase.green/platform/telemetry/event` and receives HTTP 201. ### Authoring experience Three ways to add or convert content listings: copy the agent prompt first, use snippets for manual edits, or invoke the audit skill for batch follow-on work. Refer to `CONTRIBUTING.md` for the full authoring guide. #### 1. Agent prompt Copy into Cursor or another AI assistant: ```text Add a content listing block for [TOPIC] / [SECTION] (for example, Storage / Examples). Follow CONTRIBUTING § Content listings in apps/docs. - Add data to apps/docs/data/content-listings/[topic].data.ts - Use a globally-unique kebab-case id like `[topic]-[section]` - Place inline in the guide MDX with <ContentListings id="..." /> - Copy structure from storageGetStarted in apps/docs/data/content-listings/storage.data.ts - Run pnpm test:local lib/content-listings.test.ts from apps/docs ``` #### 2. VS Code / Cursor snippets Type these prefixes in the docs workspace (`.vscode/content-listing.code-snippets`): | Prefix | Inserts | | ----------- | -------------------------------------------------------- | | `cl-data` | `ContentListingGroup` export skeleton with namespaced id | | `cl-inline` | `<ContentListings id="…" />` in guide MDX | <img width="658" height="274" alt="image" src="https://github.com/user-attachments/assets/5ef20954-7aee-4925-887d-79a5ae766b37" /> #### 3. Batch audit skill For follow-on overview page conversion or maintenance, use the [`audit-content-listings`](https://github.com/supabase/docs-agent-skills/blob/main/.claude/skills/audit-content-listings/SKILL.md) skill in `docs-agent-skills` (skill, `conversion-manifest.json`, and validation script). Example: ```text Use audit-content-listings. Audit getting-started.mdx, update conversion-manifest.json, then convert the next unconverted section only. ``` ## Additional context The implementation includes a presentational `<ContentListings />` component (grid/list layouts, GlassPanel, telemetry) backed by ID-keyed data modules, and a single markdown export handler that reads the same `id` prop from the JSX and looks up data via the shared registry. Key files: - **Data:** `apps/docs/data/content-listings/` (one `.data.ts` file per guide topic, plus `index.ts` exporting `CONTENT_LISTINGS` and `getContentListingById`) - **Renderer:** `apps/docs/components/ContentListings/` (single `<ContentListings id="…" />` component); registered in `apps/docs/features/docs/MdxBase.shared.tsx` - **Types/helpers:** `apps/docs/lib/content-listings.schema.ts` (zod schemas, type aliases, grid/heading/href helpers) - **Markdown export:** `apps/docs/internals/markdown-schema/Listings.ts` (single ID-driven handler) wired into `apps/docs/internals/generate-guides-markdown.ts` - **Telemetry:** `docs_content_listing_clicked` defined in `packages/common/telemetry-constants.ts`, fired from `ContentListings.client.tsx` - **Authoring guide:** `apps/docs/CONTRIBUTING.md` (Components and elements → Content listings) - **VS Code snippets:** `.vscode/content-listing.code-snippets` (`cl-data`, `cl-inline`) ### Before & After #### Auth | [Before (production)](https://supabase.com/docs/guides/auth) | [After (preview)](https://docs-git-fork-nrichers-nikrichers-docs-1032-sta-e2a8cb-supabase.vercel.app/docs/guides/auth) | | --------------------------------------------------------------------------------------------------------------------------- | --------------------------------------------------------------------------------------------------------------------------- | | 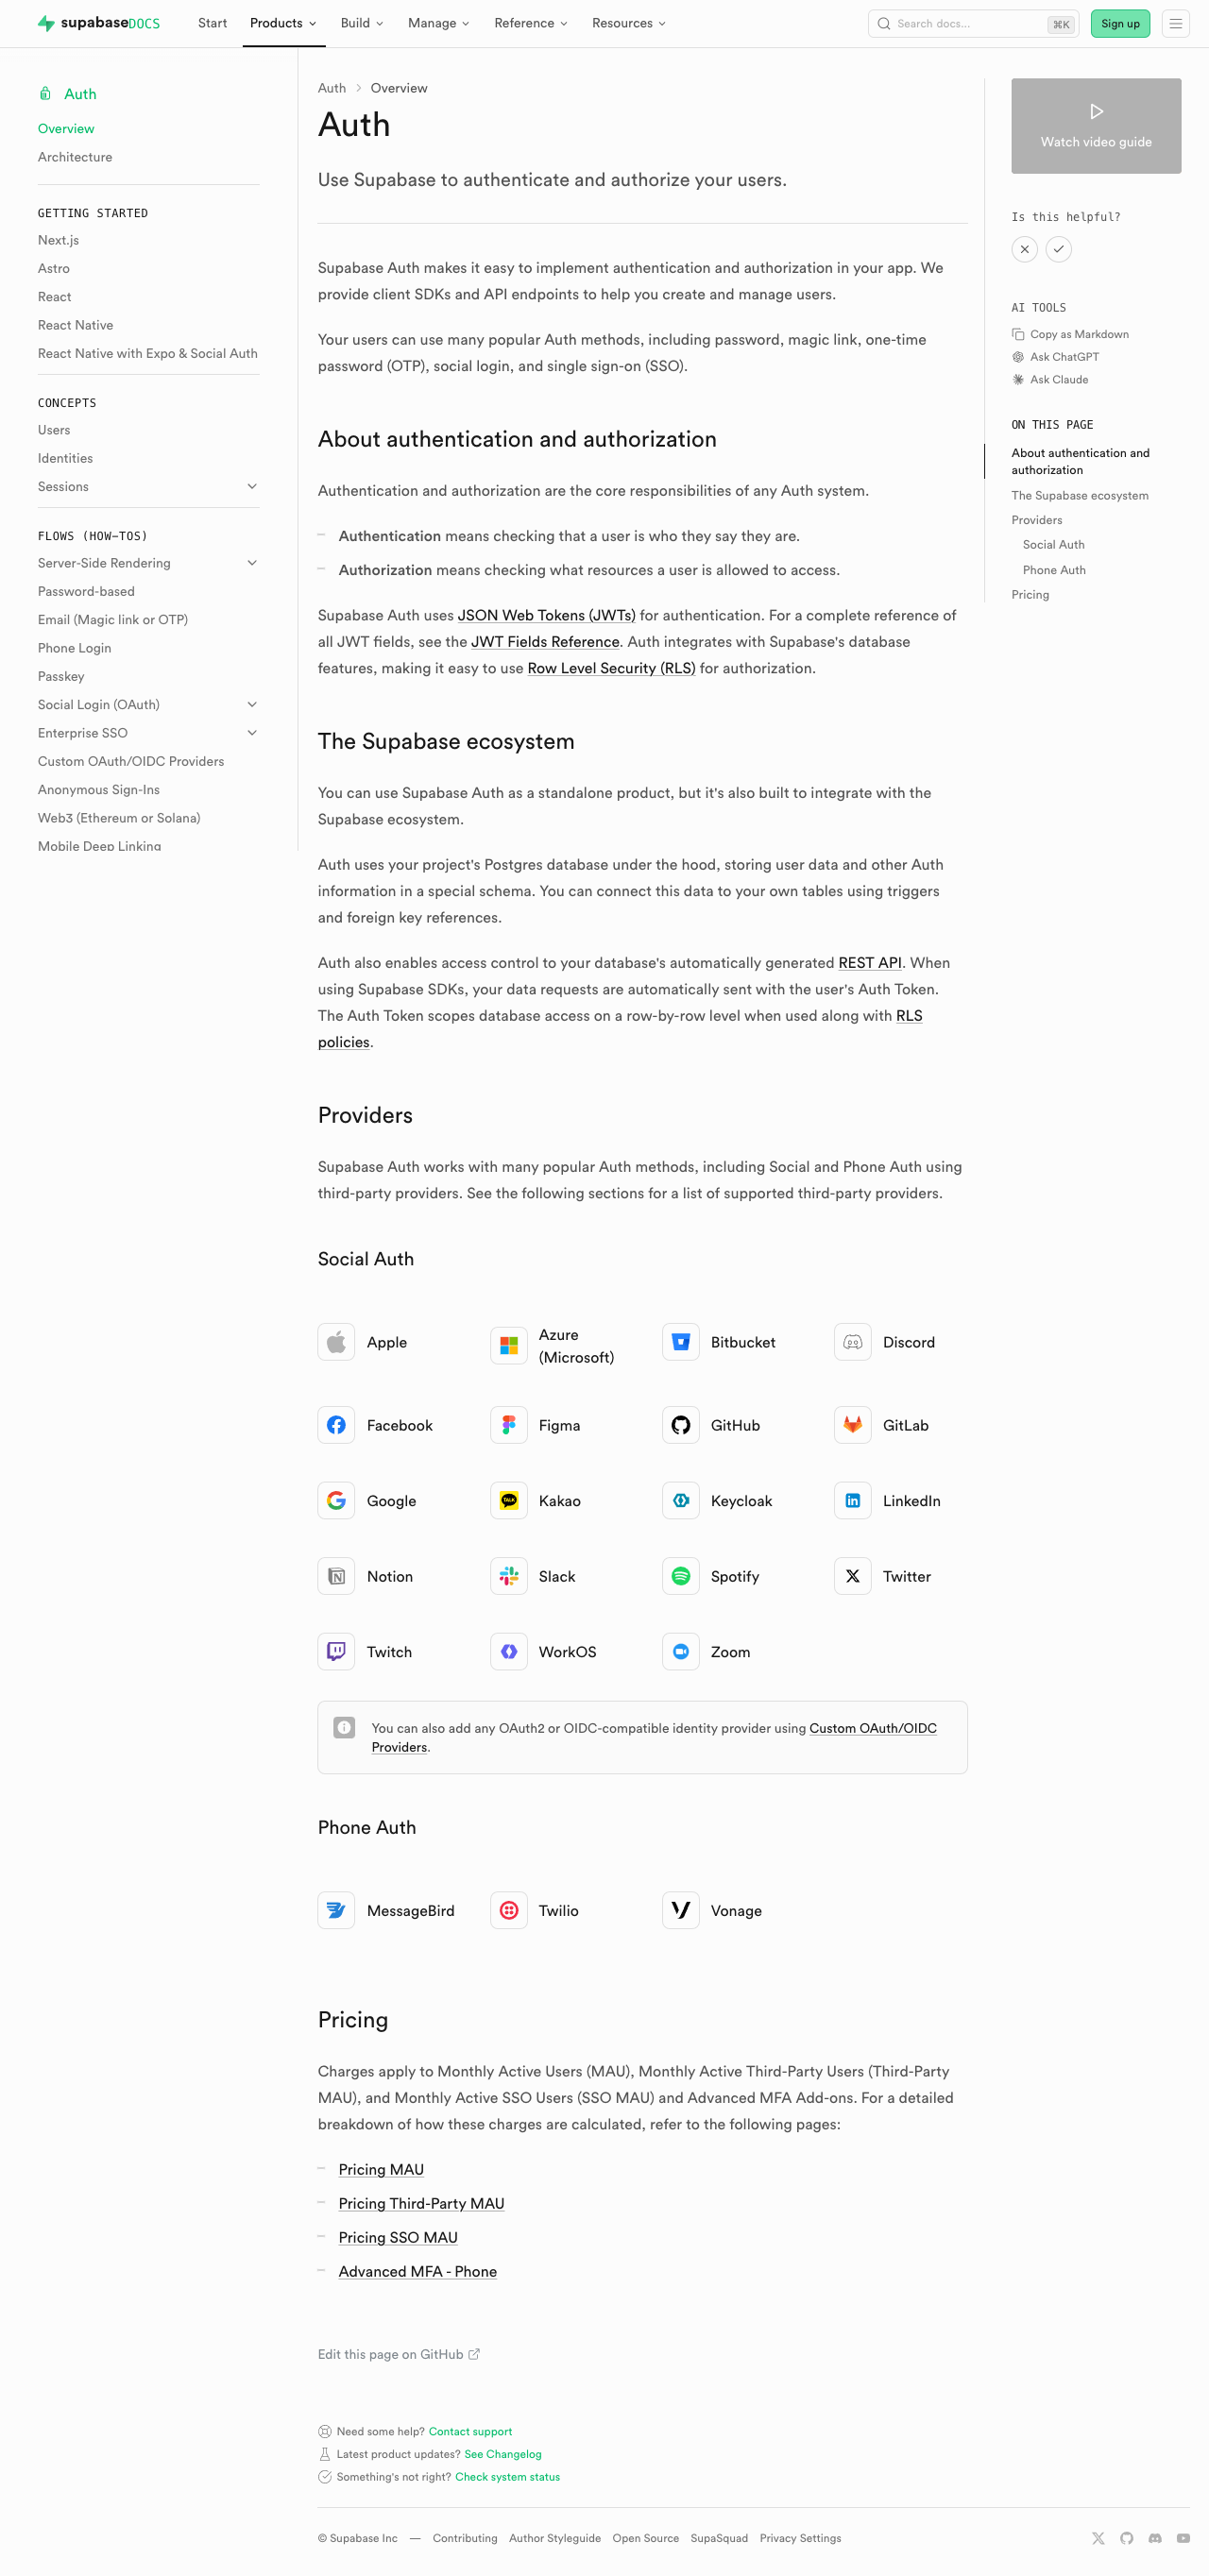 | 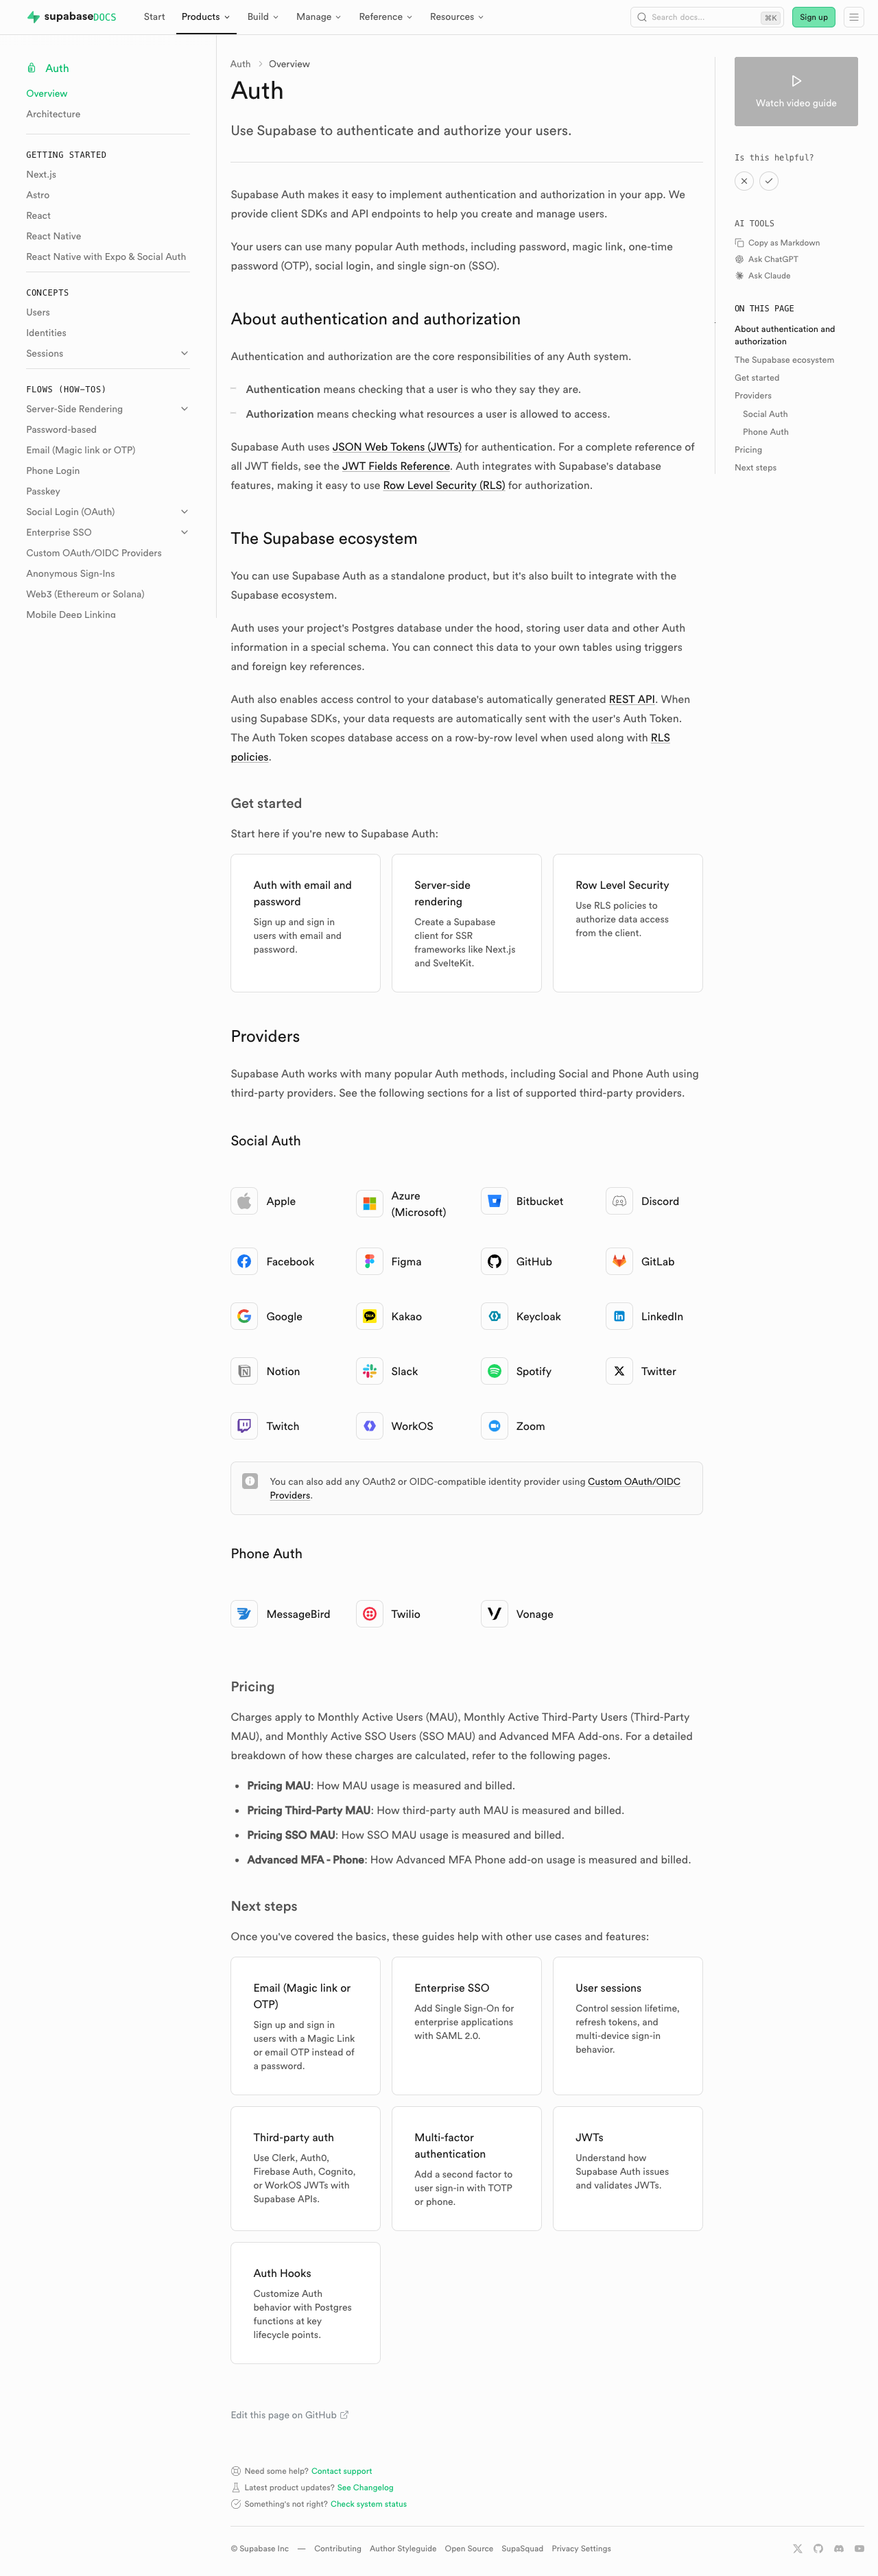 | #### Database overview | [Before (production)](https://supabase.com/docs/guides/database/overview) | [After (preview)](https://docs-git-fork-nrichers-nikrichers-docs-1032-sta-e2a8cb-supabase.vercel.app/docs/guides/database/overview) | | -------------------------------------------------------------------------------------------------------------------------------------------------- | -------------------------------------------------------------------------------------------------------------------------------------------------- | | 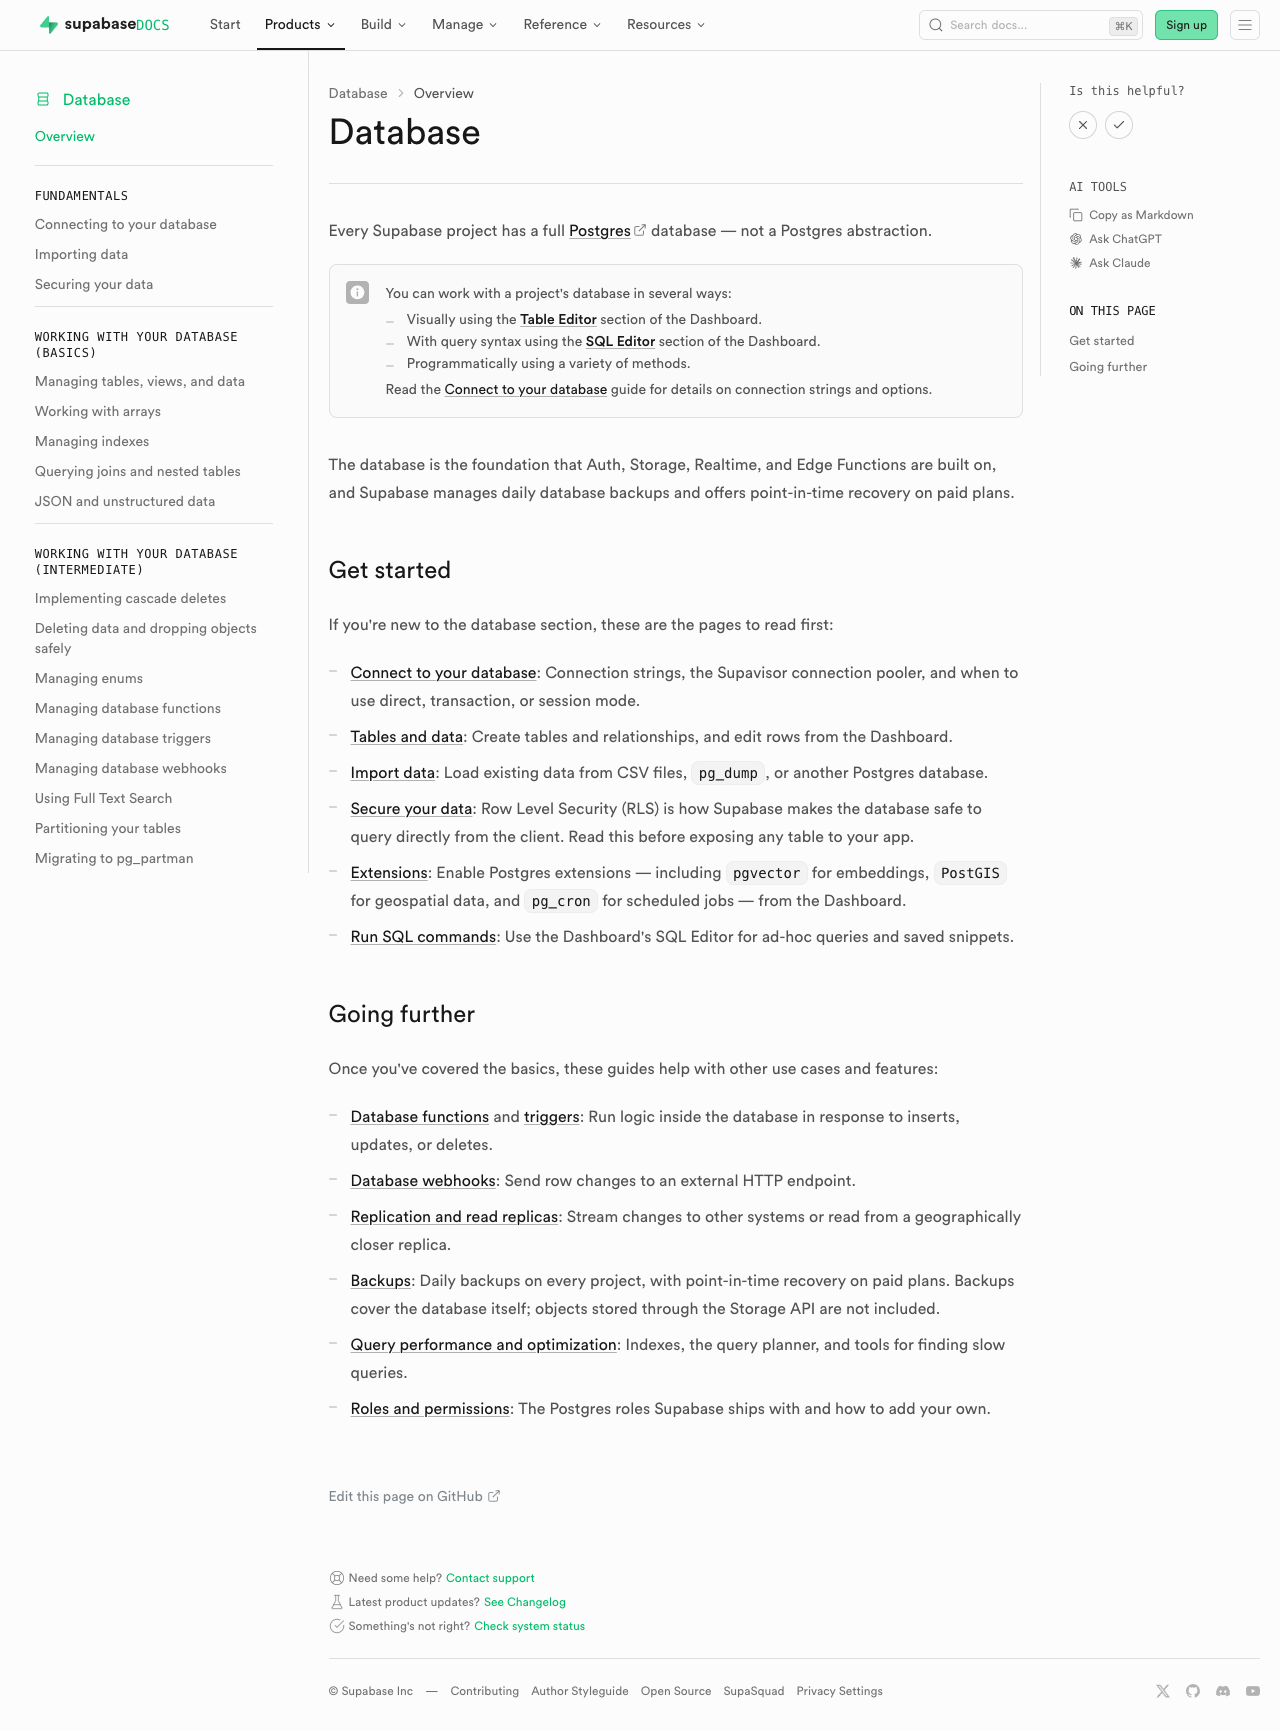 | 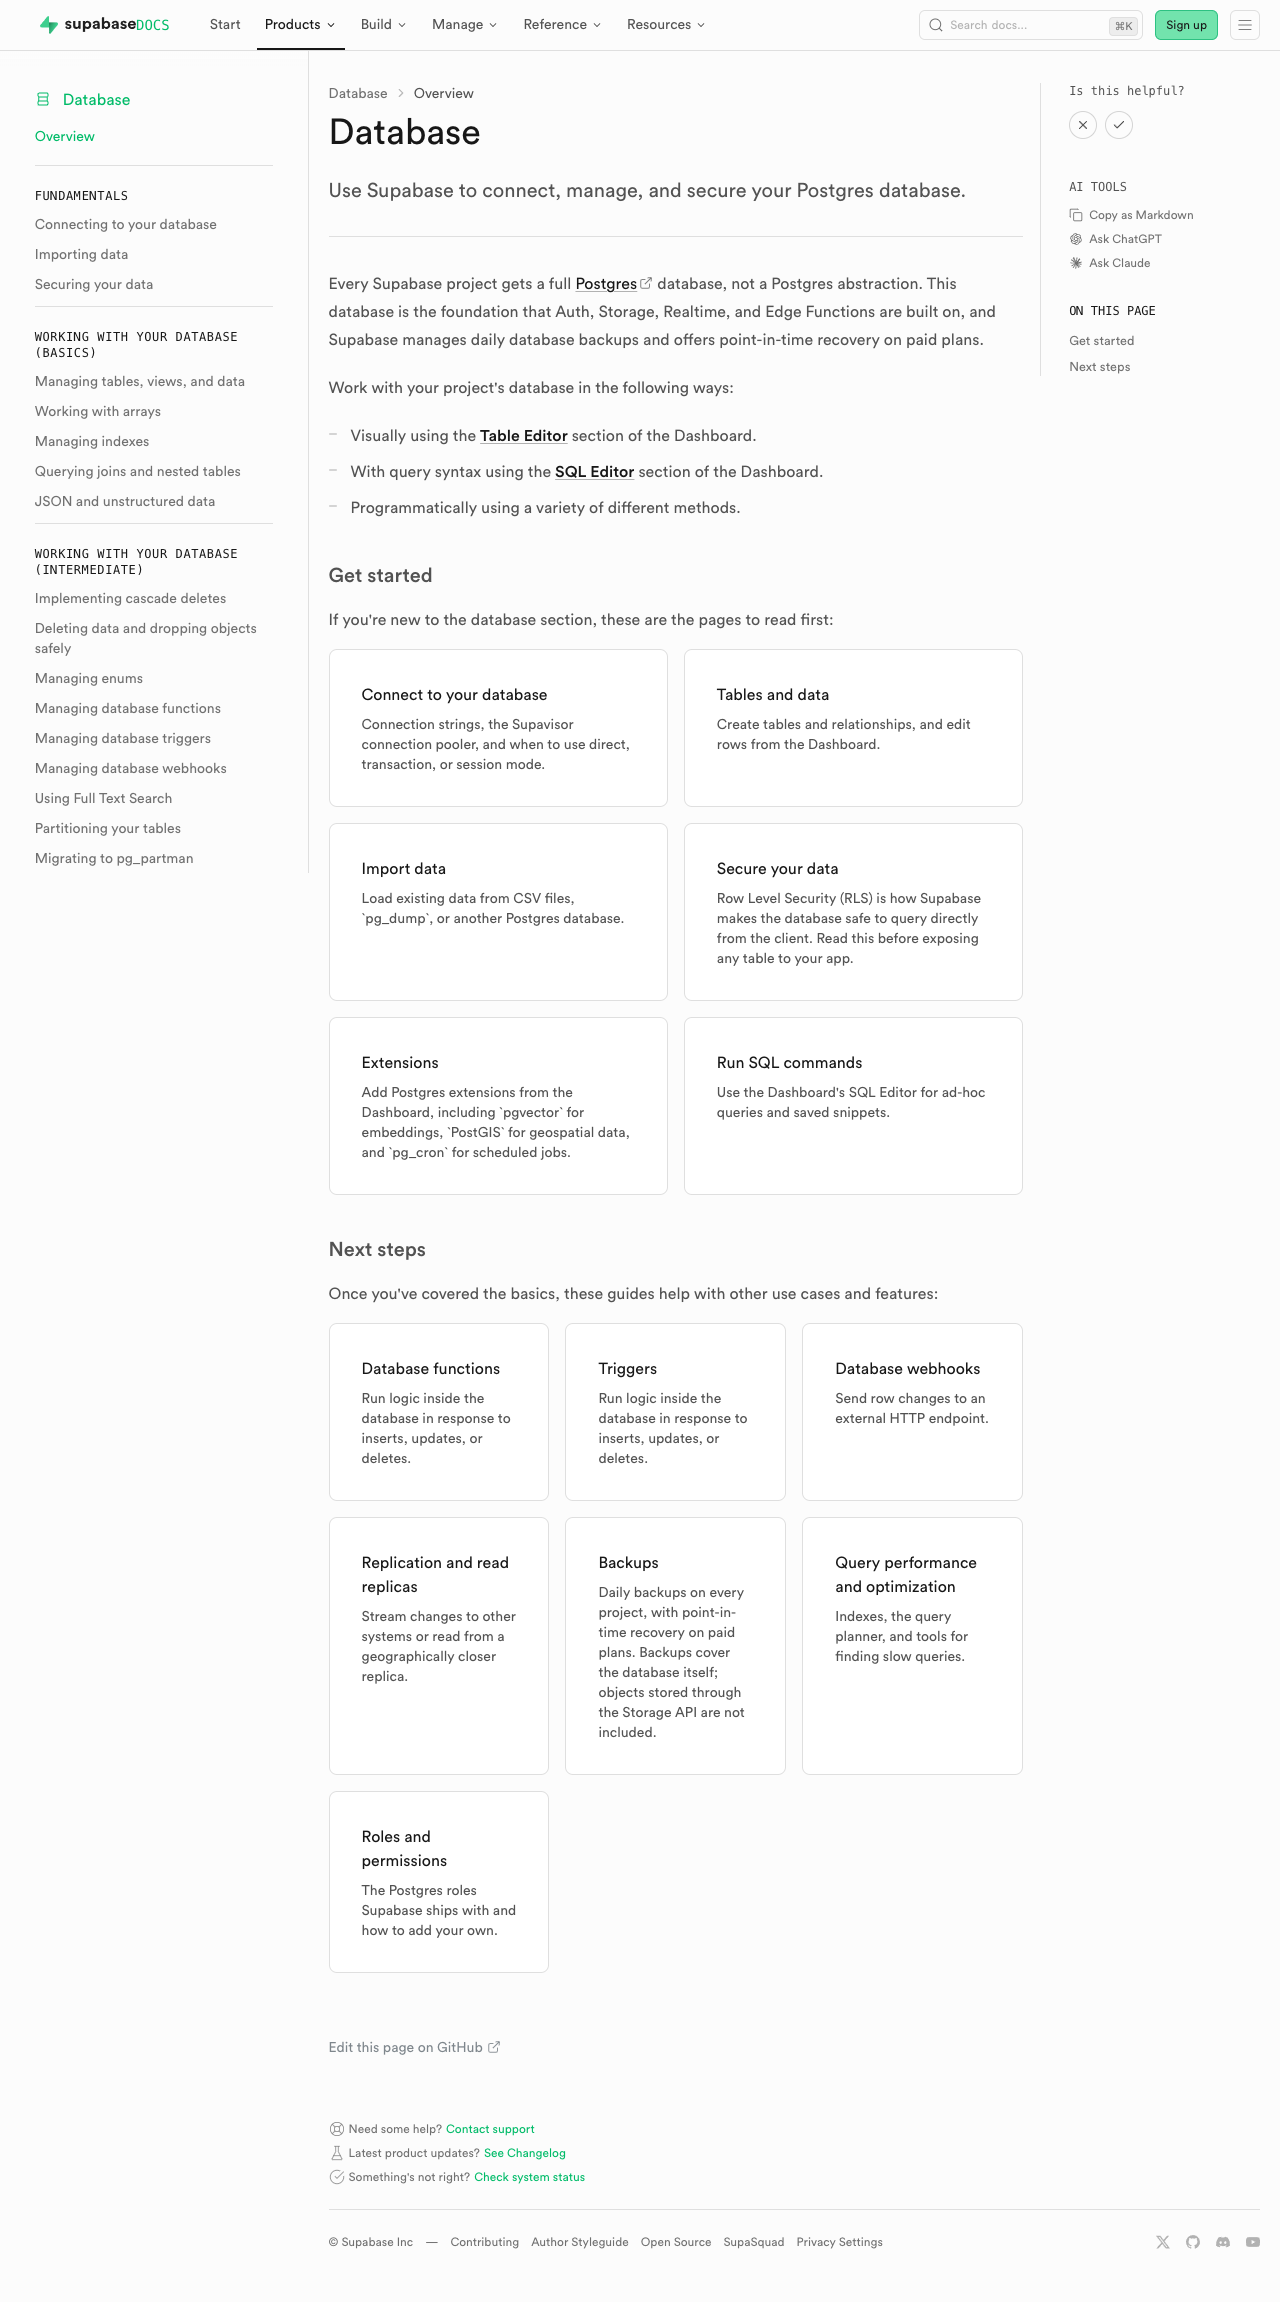 | #### Edge Functions | [Before (production)](https://supabase.com/docs/guides/functions) | [After (preview)](https://docs-git-fork-nrichers-nikrichers-docs-1032-sta-e2a8cb-supabase.vercel.app/docs/guides/functions) | | -------------------------------------------------------------------------------------------------------------------------------------------- | -------------------------------------------------------------------------------------------------------------------------------------------- | | 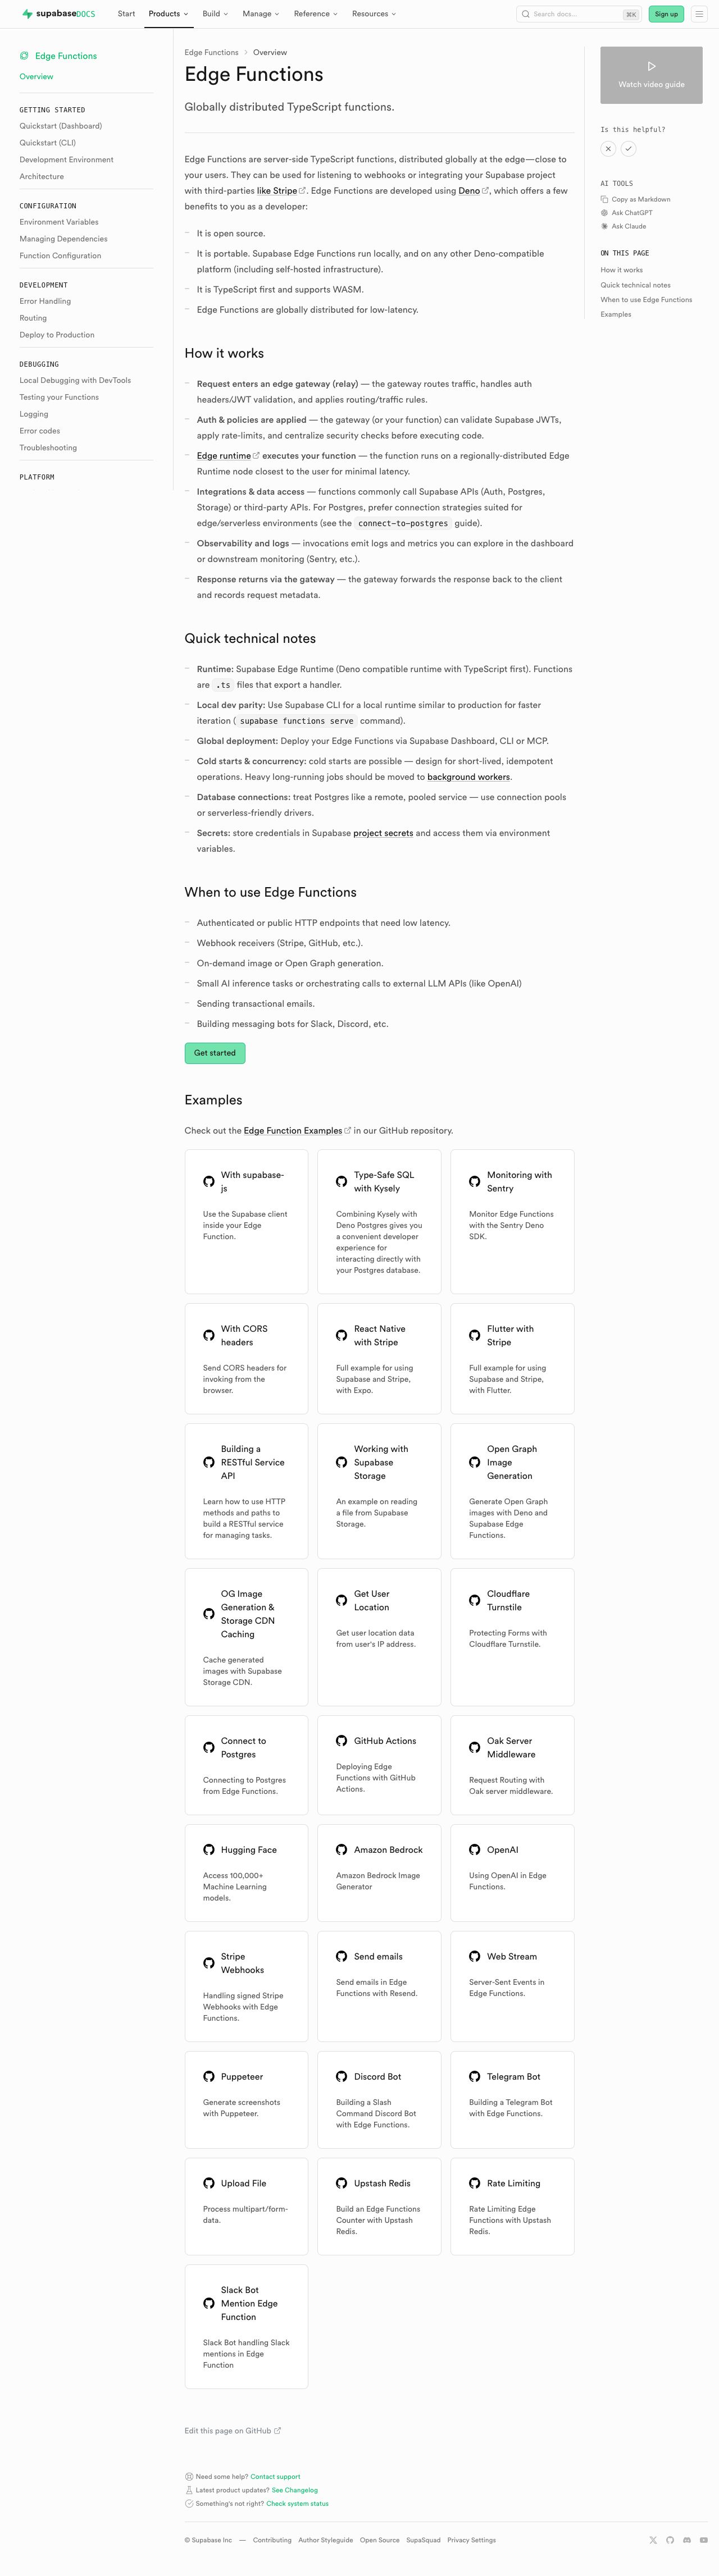 | 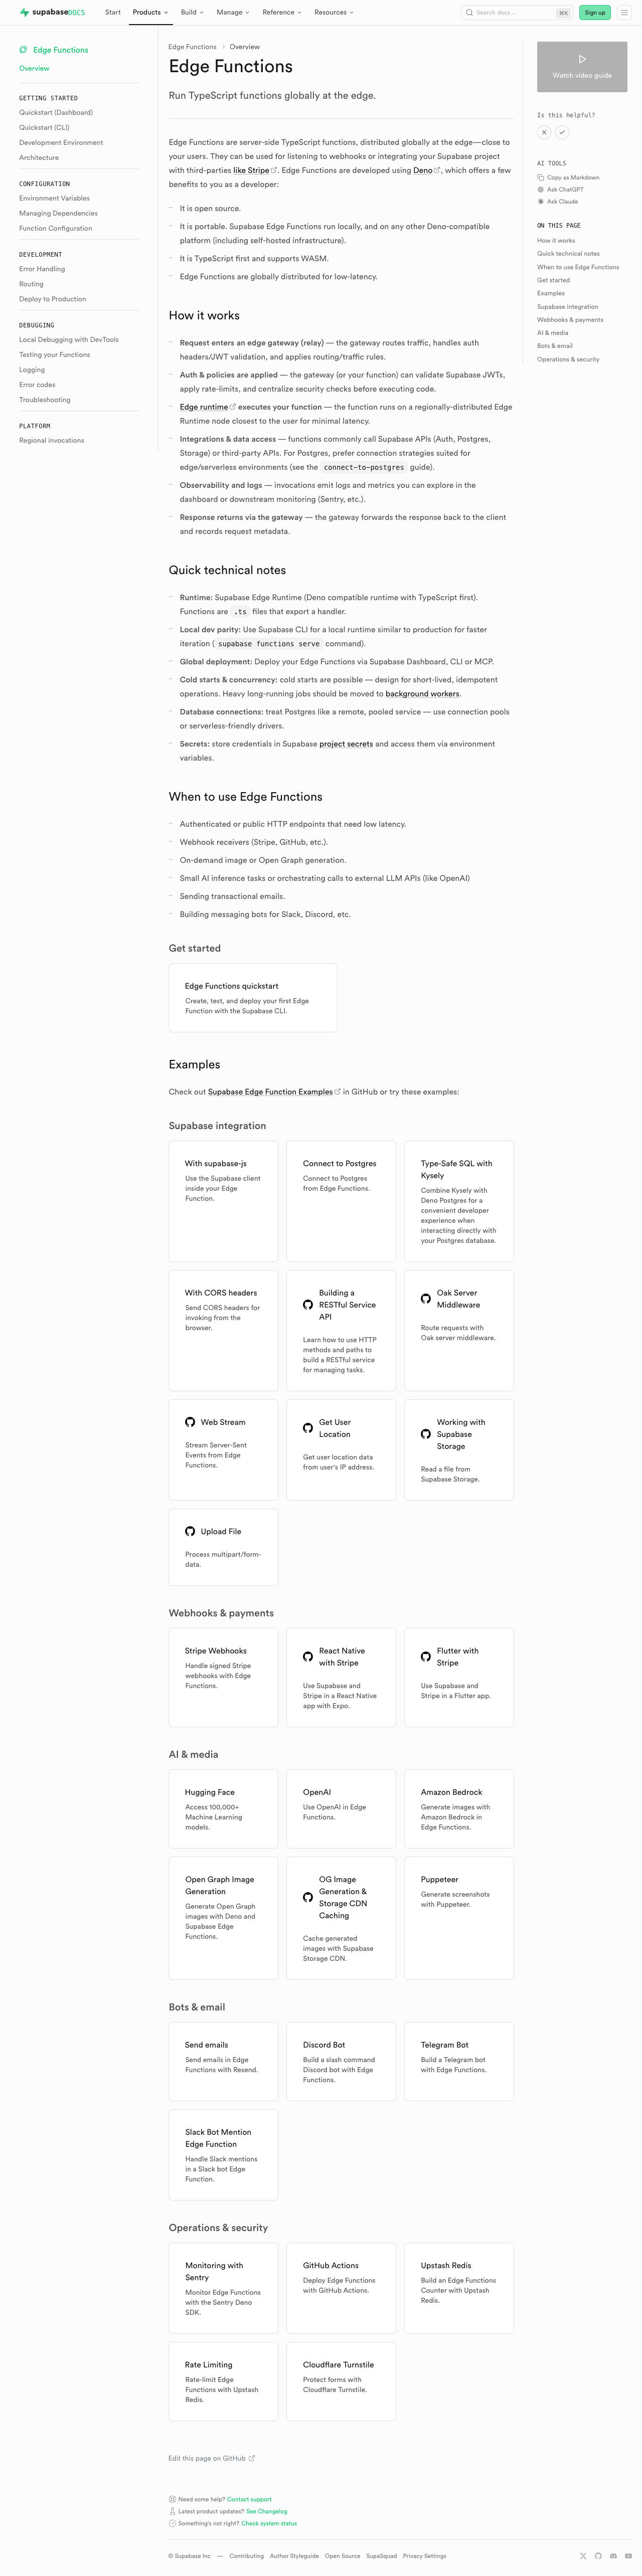 | #### Storage | [Before (production)](https://supabase.com/docs/guides/storage) | [After (preview)](https://docs-git-fork-nrichers-nikrichers-docs-1032-sta-e2a8cb-supabase.vercel.app/docs/guides/storage) | | ---------------------------------------------------------------------------------------------------------------------------------------- | ---------------------------------------------------------------------------------------------------------------------------------------- | | 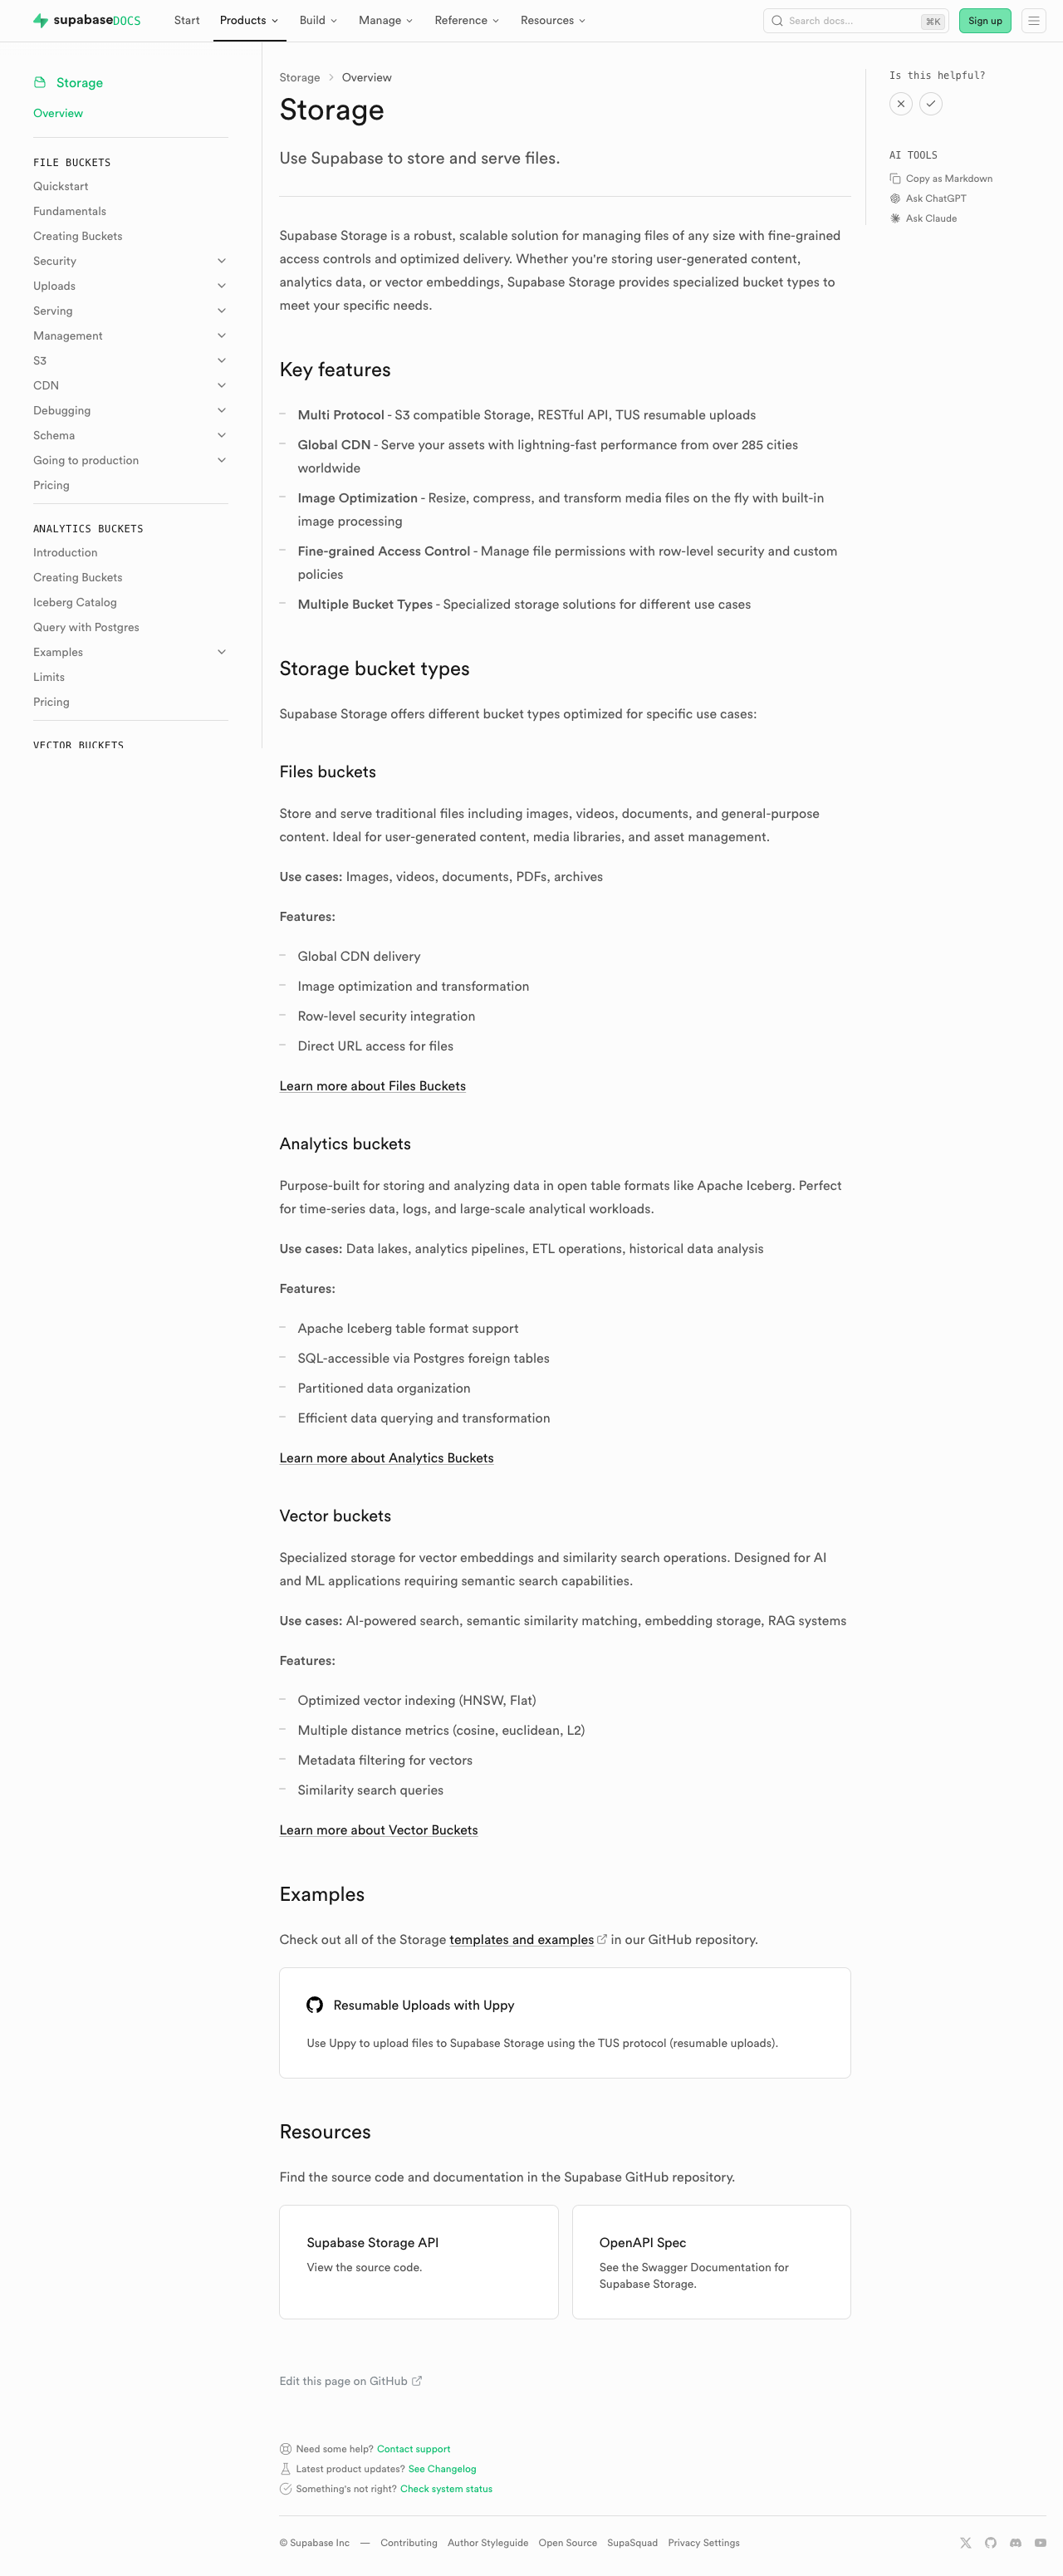 | 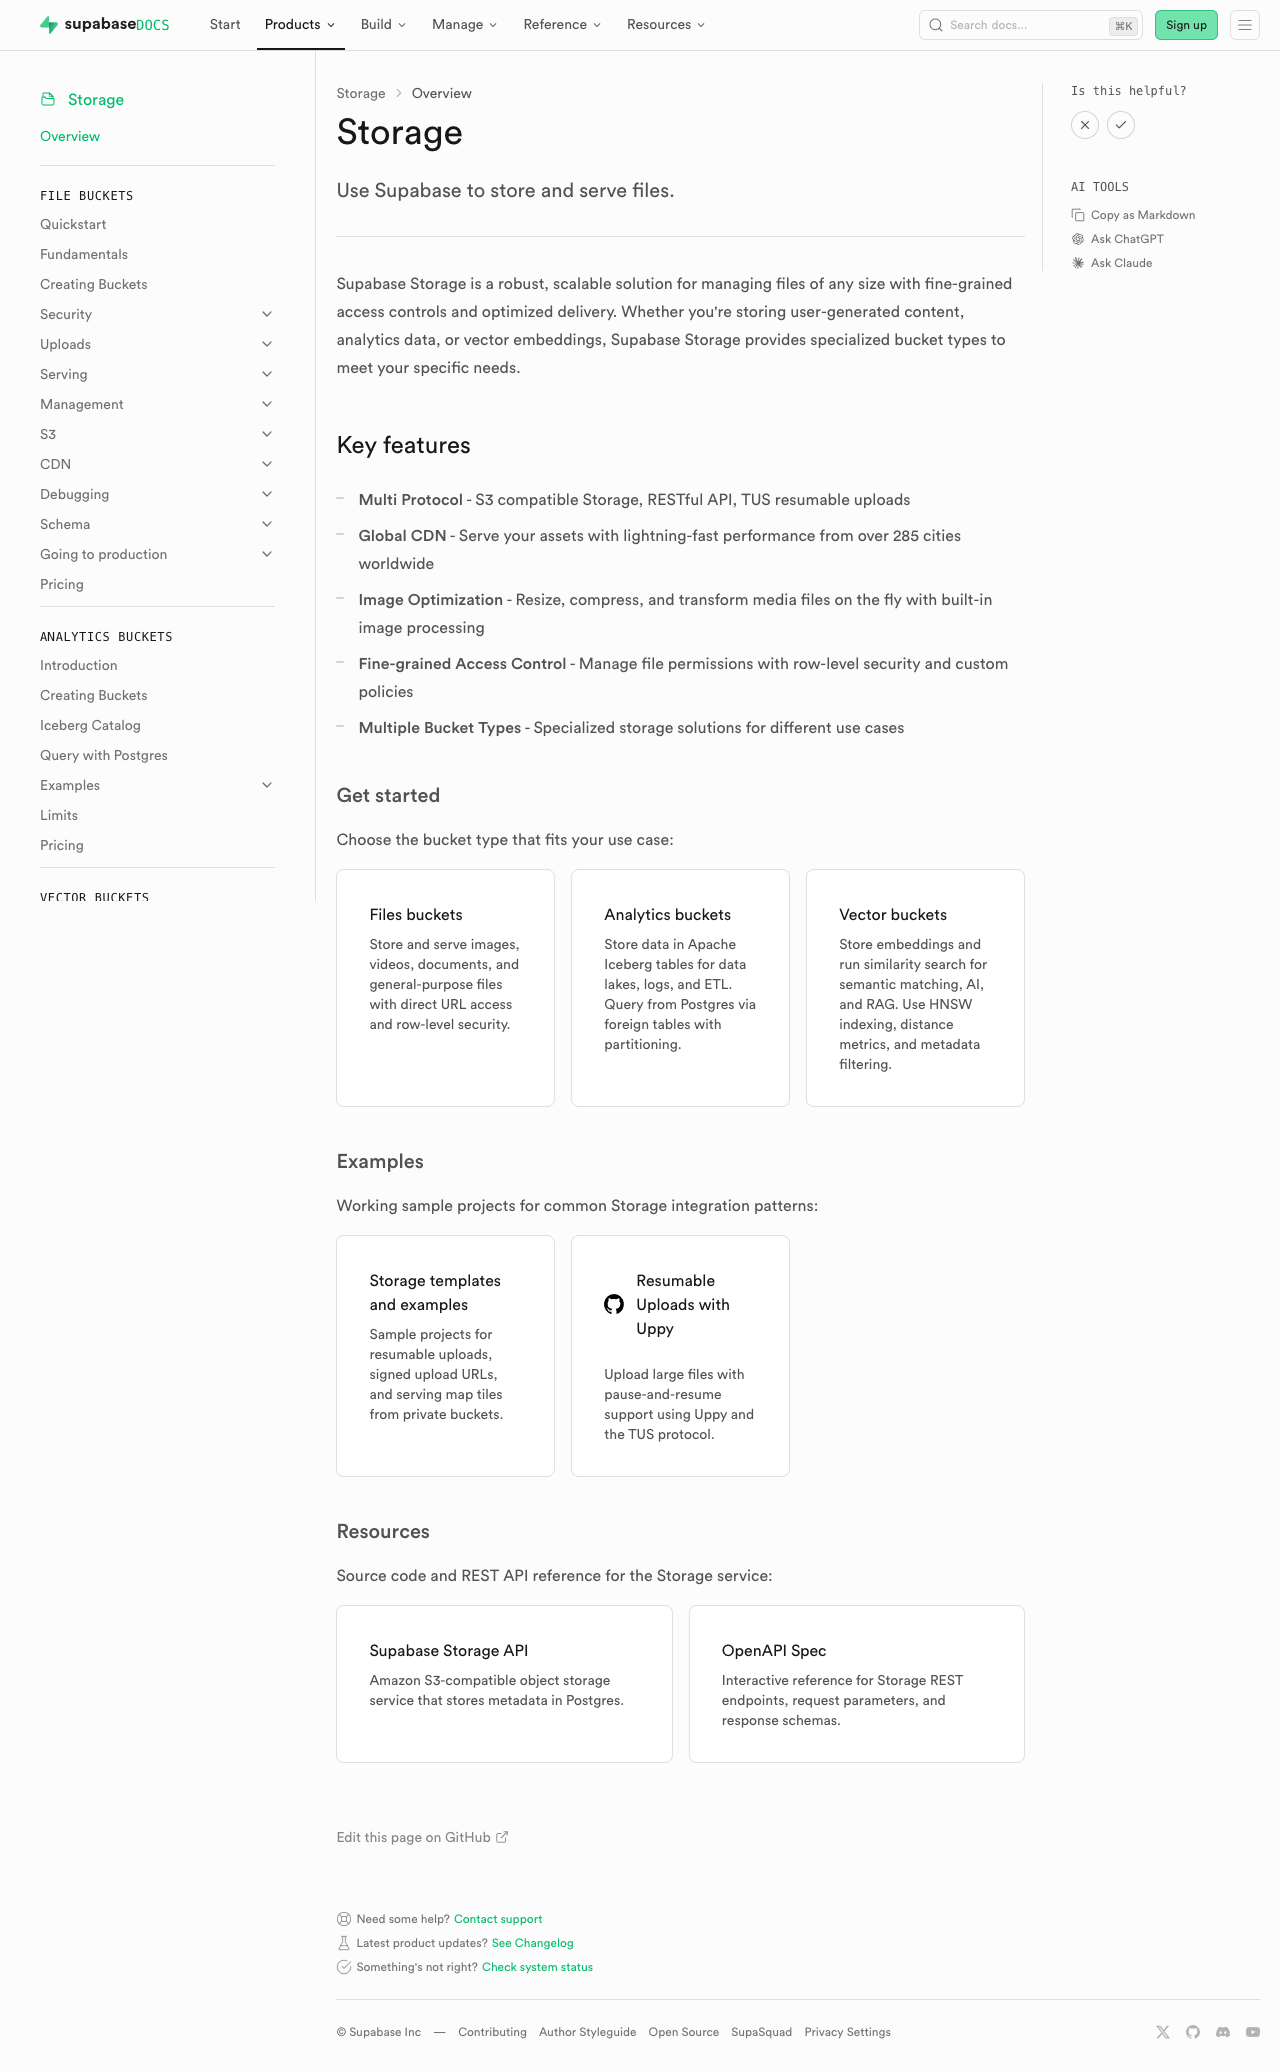 | #### Realtime | [Before (production)](https://supabase.com/docs/guides/realtime) | [After (preview)](https://docs-git-fork-nrichers-nikrichers-docs-1032-sta-e2a8cb-supabase.vercel.app/docs/guides/realtime) | | ------------------------------------------------------------------------------------------------------------------------------------------- | ------------------------------------------------------------------------------------------------------------------------------------------- | | 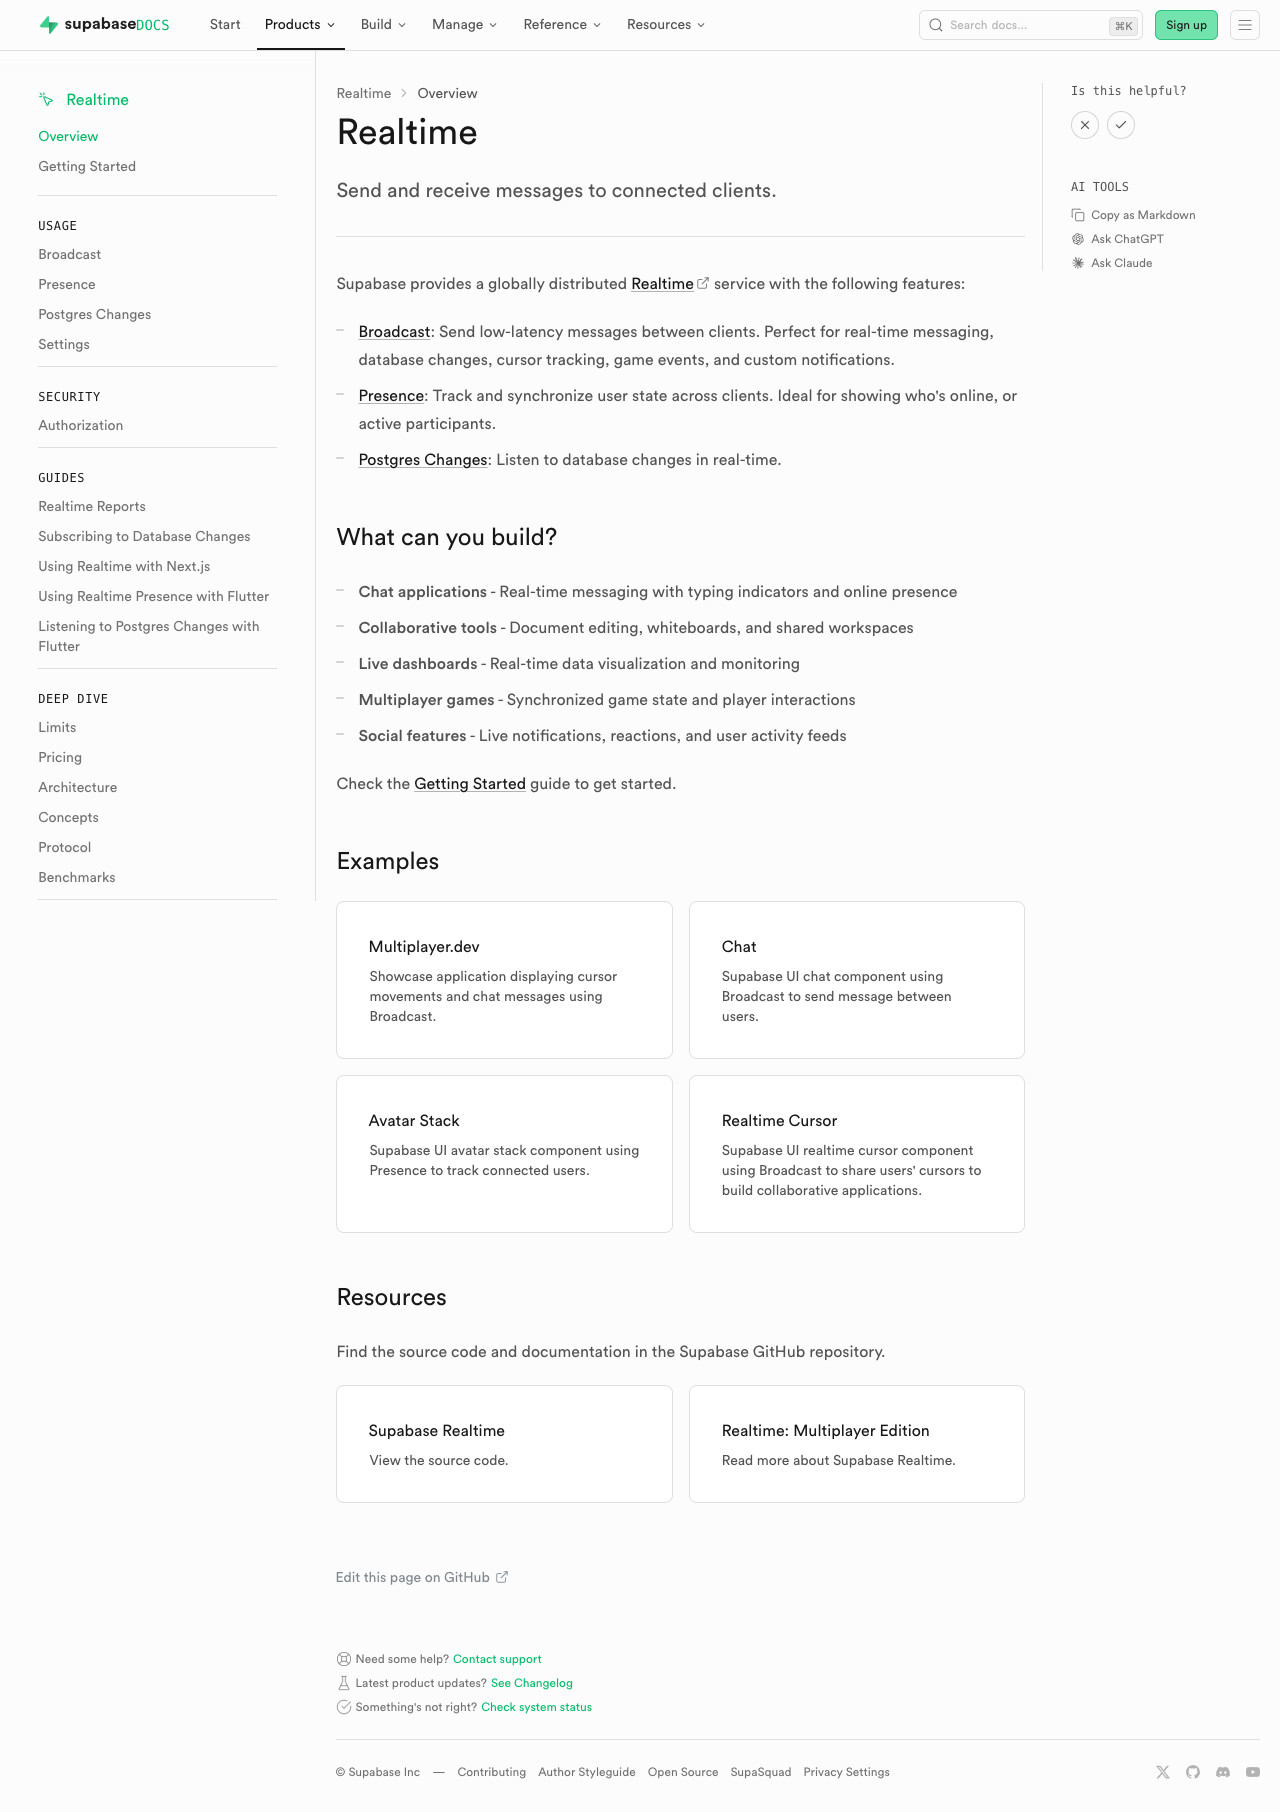 | 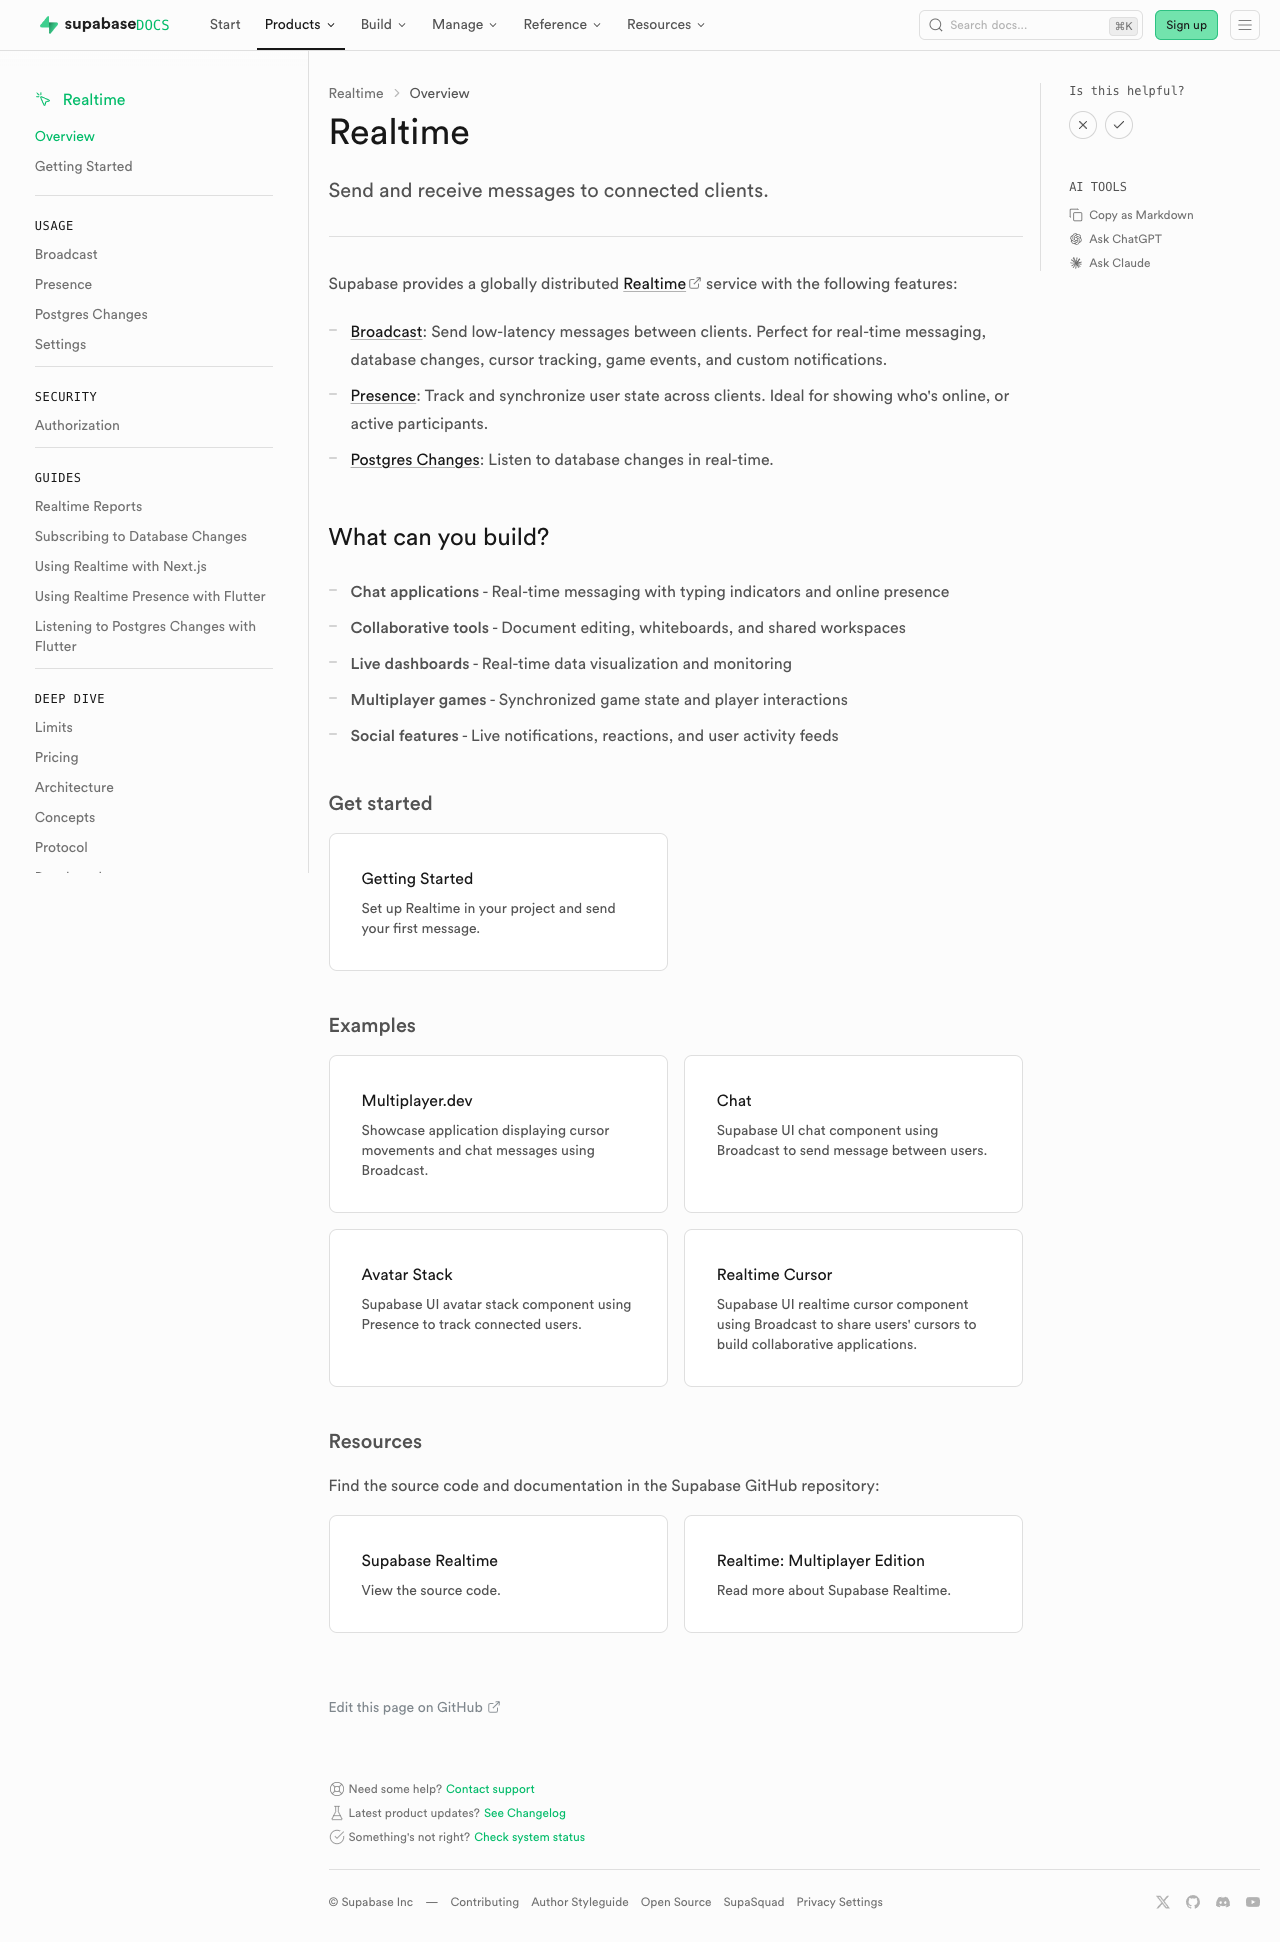 | #### Getting Started (partial migration for demoing) | [Before (production)](https://supabase.com/docs/guides/getting-started) | [After (preview)](https://docs-git-fork-nrichers-nikrichers-docs-1032-sta-e2a8cb-supabase.vercel.app/docs/guides/getting-started) | | ------------------------------------------------------------------------------------------------------------------------------------------------------ | ------------------------------------------------------------------------------------------------------------------------------------------------------ | | 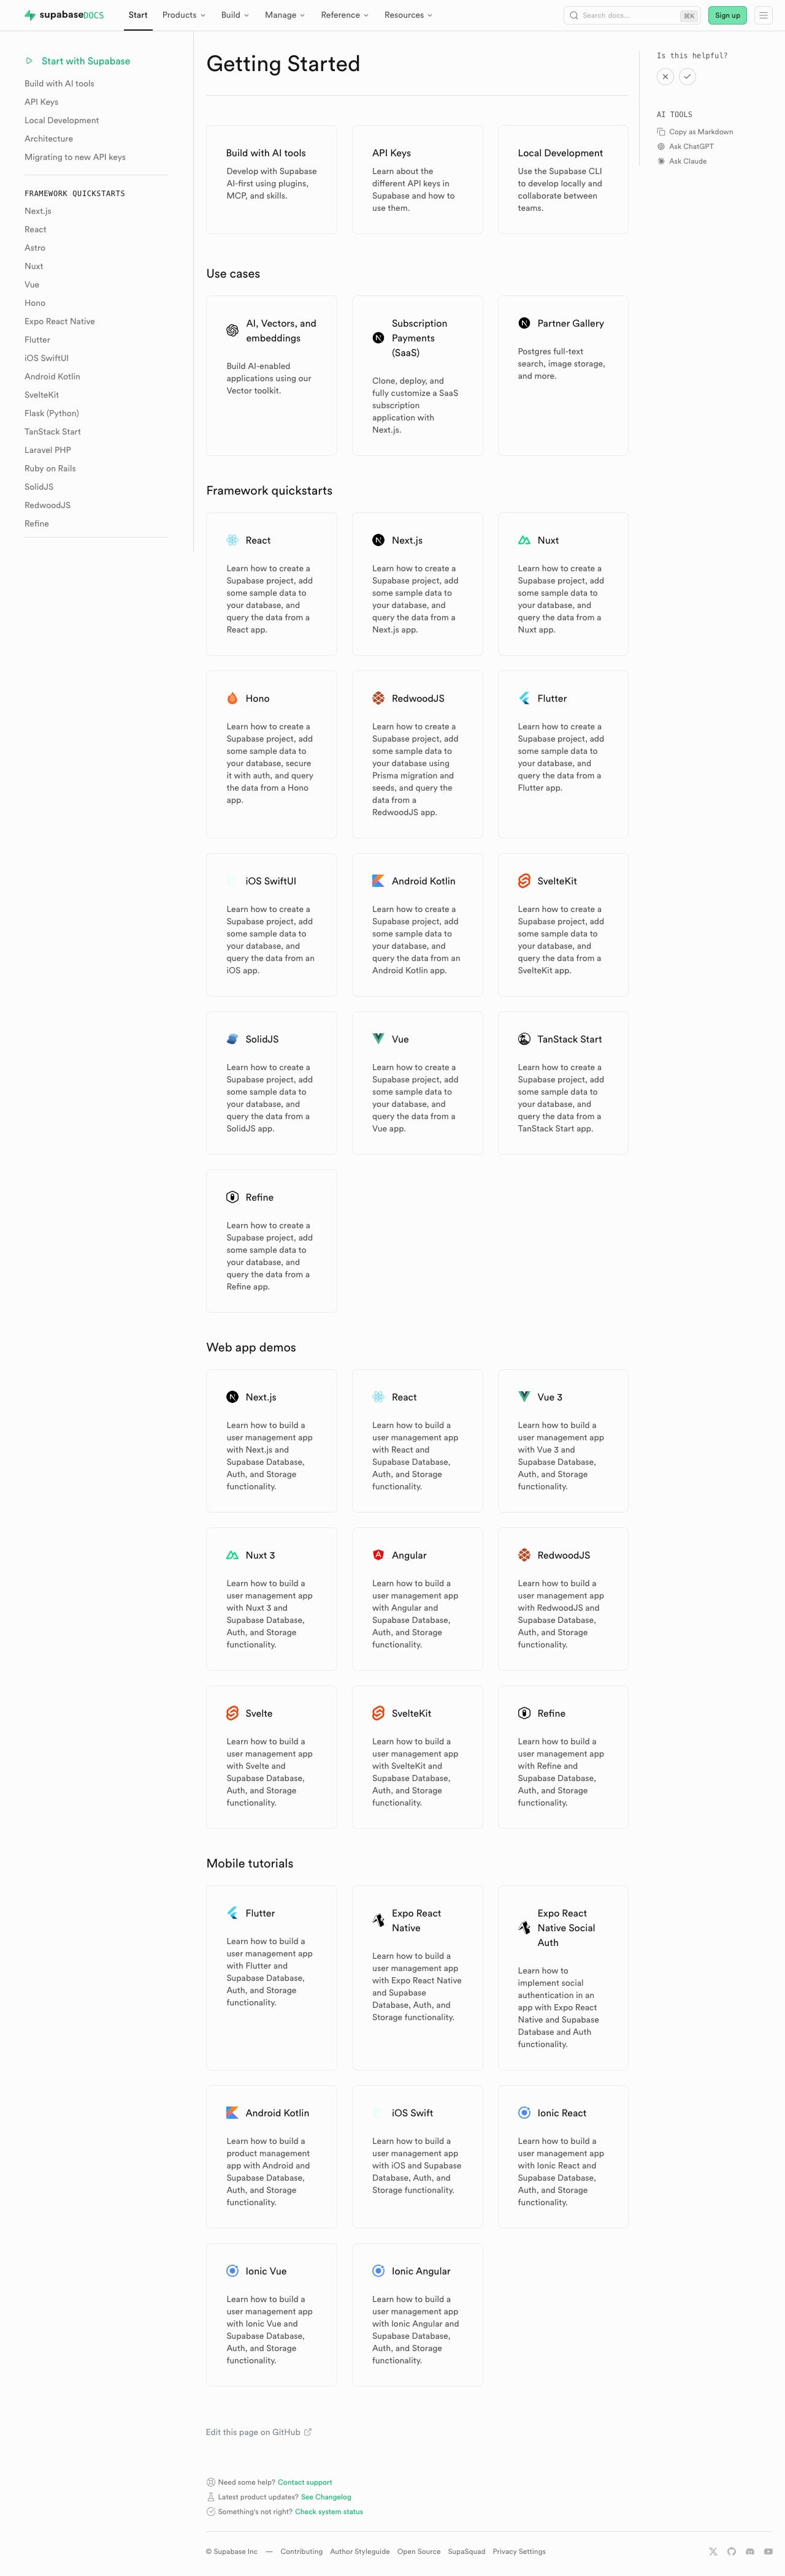 | 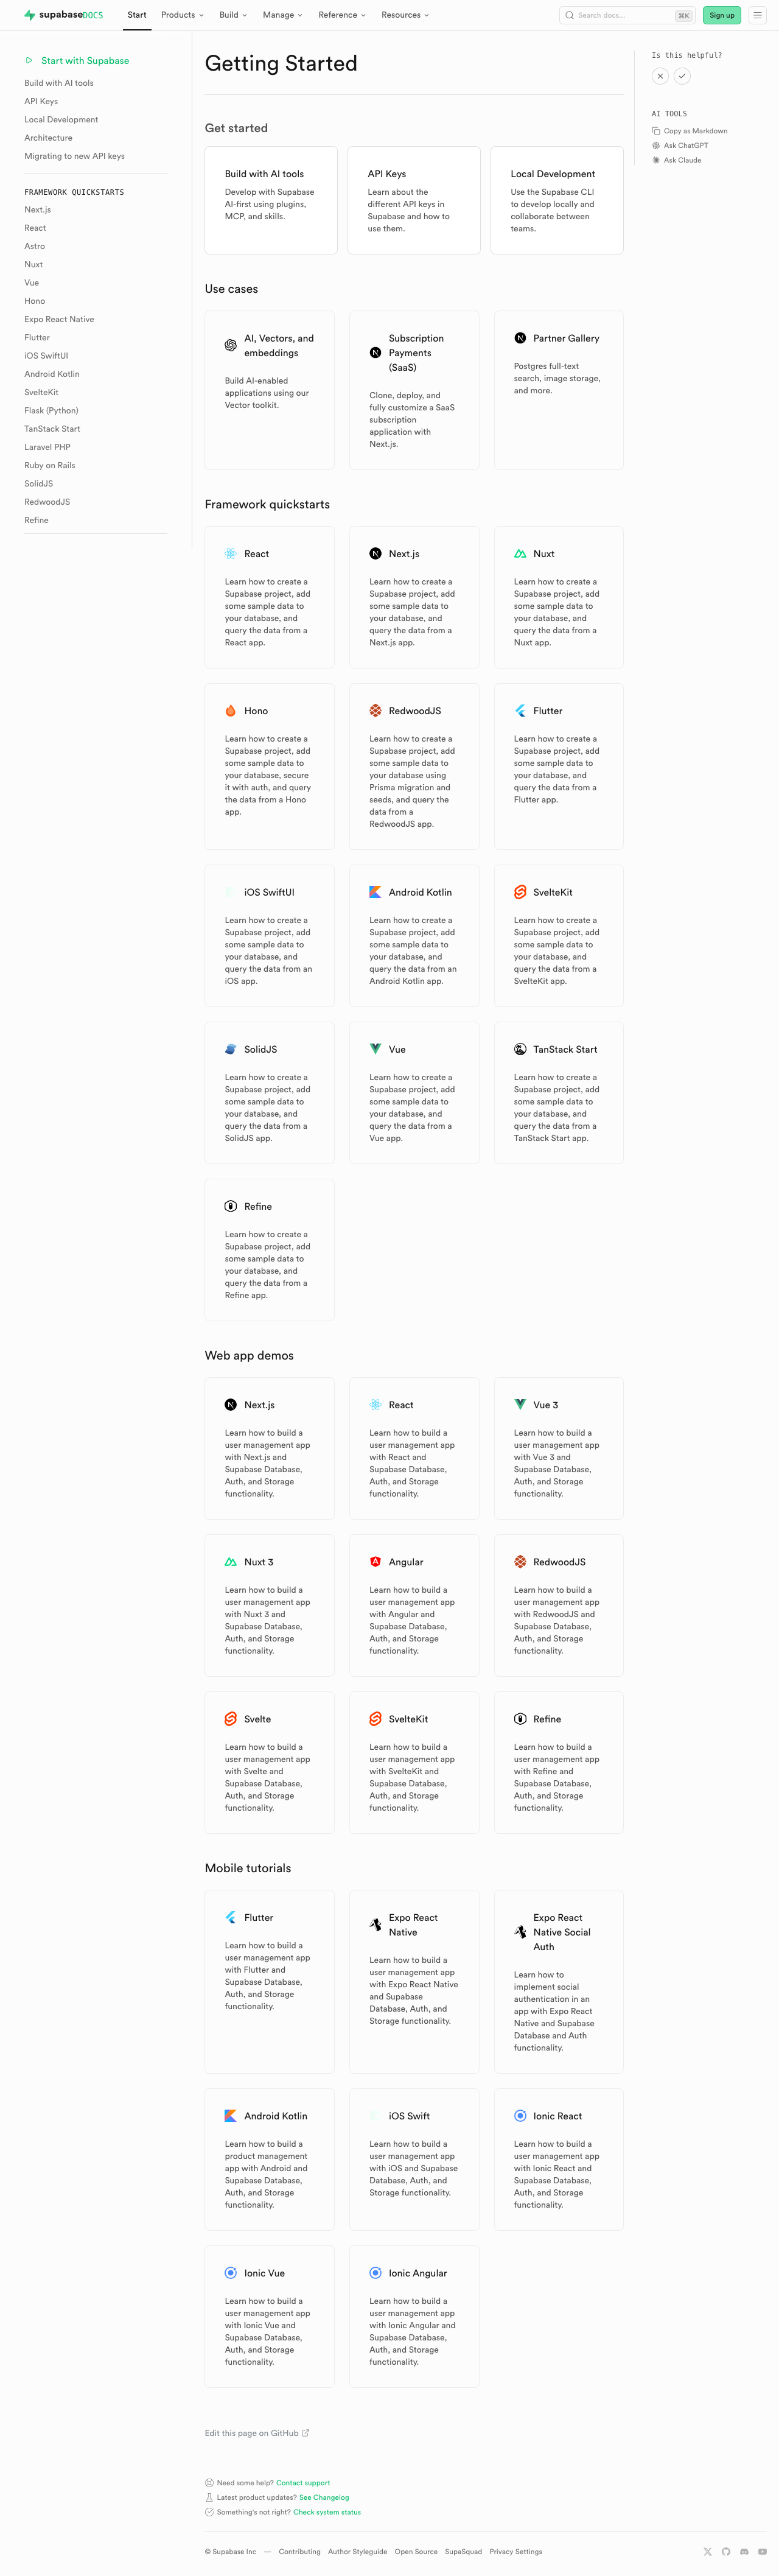 | ### Test plan - [ ] Visually verify migrated pages render correctly: - [ ] `/guides/auth` — grid "Get started", conditional pricing list, grid "Next steps" - [ ] `/guides/database/overview` — get started + next steps listings - [ ] `/guides/getting-started` — top 3-column grid - [ ] `/guides/functions` — get started + example listings - [ ] `/guides/storage` — get started, examples, resources listings - [ ] `/guides/realtime` — get started, examples, resources listings - [ ] Confirm listings render at explicit page positions - [ ] Click a content listing link and verify `docs_content_listing_clicked` fires in PostHog with expected properties (the new `listingId` is the namespaced kebab-case id, e.g. `storage-get-started`) - [ ] Build docs and confirm `.md` alternate output includes listing sections at component placement (e.g. `public/markdown/guides/storage.md`) - [ ] Run unit tests: `pnpm test:local lib/content-listings.test.ts` in `apps/docs` ## Summary by CodeRabbit ## Release Notes * **New Features** * Introduced a standardized content listings system for organizing related guides and resources. * Content listings now support both grid and list layouts for consistent presentation. * Added click telemetry for content listing interactions. * **Documentation** * Updated authentication, database, functions, getting started, realtime, and storage guide pages to use the new content listing components. * Improved MDX structure examples and listing markup formatting in contributor documentation. <!-- end of auto-generated comment: release notes by coderabbit.ai --> <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit ## Release Notes * **New Features** * Introduced a new content listings component for displaying guide content in list and grid layouts across documentation pages. * Added telemetry tracking for content listing interactions to measure user engagement. * **Documentation** * Updated guide pages (Authentication, Database, Functions, Storage, Realtime, Getting Started) to use the new listings layout. * Added contribution guidelines for creating and managing content listings in documentation. * **Tests** * Added comprehensive test coverage for content listings validation, serialization, and rendering. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Nik Richers <nik@validmind.ai> Co-authored-by: Jeremias Menichelli <jmenichelli@gmail.com> |
||
|
Pamela Chia
|
0a797ef4ea |
feat(studio): add creation funnel telemetry (#47291)
## Summary Adds frontend funnel telemetry to the organization-creation and project-creation flows in Studio, so each is measurable as a funnel (form exposed → completed) entirely from frontend events. Feeds the KPI 3 FE Benchmark Friction dashboard. Org creation had zero frontend funnel events before this (only a backend event that fires across every surface), and project creation had no clean form-view impression. ## Changes - Define `organization_creation_form_exposed`, `organization_creation_completed`, and `project_creation_form_exposed` in the telemetry constants. - Fire `organization_creation_form_exposed` when the new-org form renders, gated on the profile resolving so pre-auth redirects are not counted. Fire `organization_creation_completed` from the create success callback, covering both the free and the paid pending-payment-intent paths, attaching the new org slug as the organization group. - Fire `project_creation_form_exposed` once the org and the create-project permission have resolved, so it anchors on the form being visible rather than the route loading. Project completion reuses the existing client-side success event, so no duplicate completion event was added. ## Notes I chose exposed → completed over exposed → submitted. The org slug only exists after the create API resolves, so the completion event is the only org-funnel event that can carry the organization group; a submit-time event cannot, which would break org-level segmentation. A pageview is not a sufficient exposure anchor either: pageview capture is off, and the manual pageview fires on route change before the form is interactive (pre-auth redirect, async permission load, the no-org redirect). The `completed` verb follows the repo's approved-verb list (`.claude/skills/telemetry-standards`); the repo previously migrated `branch_merge_succeeded` to `branch_merge_completed` for the same reason. ## Testing Tested on the preview deploy: - [x] `/dashboard/new` while signed in → `organization_creation_form_exposed` fires once. - [x] Create a free org → `organization_creation_completed` fires with the organization group set. - [x] `/dashboard/new/[slug]` with create permission → `project_creation_form_exposed` fires once with `surface=main` and the organization group. - [x] No event re-fires on re-render or tab refocus. Post-deploy: confirm in PostHog prod (project 34344) via HogQL that each event fires with the expected properties and the organization / project group set. ## Linear - fixes FE-3690 <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added improved tracking for organization and project creation flows, including when forms are shown and when organization creation completes. * Captures creation metadata to support better reporting on onboarding and setup progress. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Pamela Chia
|
2d0bcd4714 |
feat(telemetry): classify funnel creation errors (#47293)
## Summary The KPI-3 friction dashboard needs to know *why* users hit errors on the signup, project-creation, and org-creation funnels, not just that they did. The existing `dashboard_error_created` event already fires for these paths (10% sampled, with `$pathname`), but carries no reason: ~98.5% of events have no `errorType` and no property carries an error message. This adds PII-safe classification computed client-side from a controlled vocabulary, so raw error text never leaves the browser. Validation errors (previously invisible, since they are inline form errors that never raise a toast) are now captured on invalid submit. ## Changes - Extend `dashboard_error_created` with `origin`, `errorCategory`, `errorReason`, `errorCode`, and a `form` source value - Add a pure, unit-tested classifier (`funnel-errors.ts`) and a 10%-sampled tracking hook (`use-track-funnel-error.ts`); the classifier maps errors to stable slugs and emits only slugs + HTTP status, never raw message text - Classify signup errors (API failures + validation) in `SignUpForm` - Classify project-creation errors (API failures, OrioleDB guard, validation) in the new-project wizard - Classify org-creation errors (API failures, payment/card declines, confirm-subscription, validation) in `NewOrgForm` ## Testing 13 unit tests cover every classifier branch (validation / api / network / payment, status-code handling, message-pattern matching, and fallbacks). To verify on the Vercel preview (events are 10% sampled; set the sample rate to 1 locally to observe each fire): - Signup with a weak but non-empty password: `origin=signup, source=form, errorCategory=validation, errorReason=password_invalid` - Signup with an already-registered email: `origin=signup, source=toast, errorCategory=api, errorReason=email_already_registered` - New project with an empty name: `origin=project_creation, source=form, errorReason=project_name_invalid` - New org with an empty name: `origin=org_creation, source=form, errorReason=org_name_missing` - New org with a declined test card: `origin=org_creation, errorCategory=payment` PII: raw `error.message` is never sent; only controlled slugs and HTTP status. Dashboard consumers must filter `origin IS NOT NULL` so these do not collide with the generic toast events the global tracker still emits. ## Linear - fixes FE-3691 <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added improved, categorized telemetry for signup, project creation, and organization creation errors, including payment, subscription-change, and validation failures. * Extended dashboard error events with optional structured diagnostics (origin, category, reason, and optional error code) and support for form-origin reporting. * **Bug Fixes** * Improved project-creation handling to record a validation telemetry event when an Oriole image is unavailable. * Ensured payment-related and subscription-change failures are captured consistently alongside existing user toasts. * **Tests** * Added unit tests covering API/network/validation/Stripe error classification and reason mapping. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Ali Waseem
|
cedc4c8187 |
feat: Add Server lib to connect w/ ability to copy env (#47056)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? Introduced a new library called Superbase/Server. To help developers using third party API frameworks, we want to make it easier than ever to install and use as needed. - One click copy - Custom prompt to get started - Validated API key permissions to ensure we don't leak secrets to other users in your org/project <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit ## New Features - Added a **Server** connection mode end-to-end, including mode-specific prompting and steps for installing **`@supabase/server`** and setting required variables. - Added a server **.env** panel with per-variable copy, **“Copy all variables”**, and permission-aware secret reveal/copy. ## Improvements - Updated connection UI layouts (mode selector grid and conditional config section). - Improved prompt copying to use mode-specific prompt text when available. ## Tests - Added UI tests for server env rendering, secret reveal/copy, **copy-all** behavior, and permission-restricted scenarios. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Jordi Enric
|
15ef851e67 | feat(studio): homepage usage charts backed by service-health, behind a flag (#46373) | ||
|
Pamela Chia
|
dc5ddd8c4c |
chore(telemetry): align event interface names with action strings (#47048)
## Summary Aligns 16 telemetry event interface identifiers in `packages/common/telemetry-constants.ts` so each interface name equals the PascalCase of its `action` string (`PascalCase(action) + Event`). This is a follow-up to the GROWTH-798 audit (#45964), which fixed the `action` strings and several interface names but left these 16 identifiers mismatched. I renamed identifiers only: every `action` string is untouched, so there is zero impact on PostHog event names or historical data. Before this change, 176/192 interfaces matched the convention. This brings it to 192/192. ## Changes Structural renames (interface name was dropping or reordering words vs the action): - `AskAIEvent` to `AskAiClickedEvent` - `CopyAsMarkdownEvent` to `CopyAsMarkdownClickedEvent` - `DocsRecommendation404ClickedEvent` to `Docs404RecommendationClickedEvent` (from #46990) - `EventPageCtaClickedEvent` to `WwwEventPageCtaClickedEvent` (completes the interface side of GROWTH-798 HIGH #1) - `ImportDataFileAddedEvent` to `ImportDataDropzoneFileAddedEvent` (also updates the consumer `apps/studio/hooks/ui/useCsvFileDrop.ts`) - `QueryPerformanceAIExplanationButtonClickedEvent` to `QueryPerformanceExplainWithAiButtonClickedEvent` Initialism casing (normalized to the file-majority lowercase transform; `Sql` 9:2, `Api` 3:2, `Ai` 6:2): - `CustomReportAddSQLBlockClickedEvent` to `CustomReportAddSqlBlockClickedEvent` - `CustomReportAssistantSQLBlockAddedEvent` to `CustomReportAssistantSqlBlockAddedEvent` - `HomepageGitHubButtonClickedEvent` to `HomepageGithubButtonClickedEvent` - `MetricsAPIBannerCtaButtonClickedEvent` to `MetricsApiBannerCtaButtonClickedEvent` - `MetricsAPIBannerDismissButtonClickedEvent` to `MetricsApiBannerDismissButtonClickedEvent` - `TableRLSEnabledEvent` to `TableRlsEnabledEvent` - `RLSGeneratePoliciesClickedEvent` to `RlsGeneratePoliciesClickedEvent` - `RLSGeneratedPolicyRemovedEvent` to `RlsGeneratedPolicyRemovedEvent` - `RLSGeneratedPoliciesCreatedEvent` to `RlsGeneratedPoliciesCreatedEvent` - `RLSTesterRunQueryClickedEvent` to `RlsTesterRunQueryClickedEvent` ## Testing Type-only change, no runtime or PostHog behavior to exercise. Verified that all 192 interfaces now match `PascalCase(action) + Event` (0 mismatches), the `TelemetryEvent` union has no duplicates, no old identifier names remain anywhere in the repo, and the one external consumer (`useCsvFileDrop.ts`) still resolves via its `['action']` indexed access since the action strings are unchanged. ## Linear - fixes GROWTH-928 <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Chores** * Updated internal telemetry infrastructure for consistency and maintainability. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Chris Chinchilla
|
309f4b2612 |
docs: Track 404 recommendation clicked (#46990)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added analytics telemetry for documentation 404 recommendation clicks, recording the clicked destination and the originating page. * **Improvements** * Enhanced the ButtonCard component to optionally handle click actions via an `onClick` callback and forward it to the underlying link element. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Pamela Chia
|
91982e6a2d |
feat(studio): track unified logs cta variant and auto-dismiss on explore (#46940)
## Summary The Unified Logs promo banner (shipped in #46847) had two telemetry/UX gaps I found while auditing the weekly PostHog event review. Its CTA fired one event for two different user paths with no way to tell them apart, and clicking "Explore" left the banner in place. This adds an `is_enabled` property to the CTA event and auto-dismisses the banner on the Explore path. ## Changes - Add `is_enabled: boolean` to `unified_logs_banner_cta_button_clicked`. It is `true` when the user is already enabled and the button navigates to the logs page ("Explore"), and `false` when not enabled and the button opens the feature-preview modal ("Enable"). The two cohorts are now queryable independently, which is what makes the CTA data usable for measuring adoption. - Auto-dismiss the banner when an already-enabled user clicks "Explore". Previously only the X button dismissed it, so an Explore click left the banner showing on the next project page load. Scoped to the Explore path on purpose: the not-enabled path only opens a preview modal (it does not enable), so dismissing there would hide the banner from users who never enabled. ## Testing Behavior to verify on the Vercel preview: - [x] Enabled user clicks "Explore Unified Logs": navigates to the logs page, banner does not reappear on the next project page load, CTA event fires with `is_enabled` true. - [x] Non-enabled user clicks "Enable Unified Logs": preview modal opens, banner is still present after closing the modal, CTA event fires with `is_enabled` false. - [x] X button: banner dismissed as before, dismiss event fires. Out of scope on purpose: no impression event (it would fire on every banner render, low-millions of events per month for one banner), so true click-through rate stays unmeasurable for now. ## Linear - fixes GROWTH-925 <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Improvements** * Unified Logs banner now intelligently updates behavior based on feature state. * When enabled, exploring the feature automatically dismisses the banner. * When disabled, the enable action opens the feature preview flow. * Enhanced tracking for banner interactions. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
kemal.earth
|
3162cad715 |
feat(studio): add a banner to promote unified logs (#46847)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? Adds a one time banner to the `<BannerStack />` to promote Unified Logs becoming available. This also fixes the `<BannerStack />` components issue with stacking varying height banners. https://github.com/user-attachments/assets/40f02709-0d67-43a9-ab95-750d9a4a582a <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added a dismissible "Unified Logs" banner with an animated sample-log carousel, CTA to Unified Logs, and a preview/enable flow for non-enabled users. Dismissal is persisted locally and telemetry is recorded for CTA and dismiss actions; banner appears only for eligible projects. * **Refactor** * Banner stack UI updated to display a single front banner with animated "peek" slivers and refined hover/animation behavior. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Mert YEREKAPANandkemal
|
2191669d08 |
feat(studio): add upgrade CTA placement experiment (#45858)
## Summary Replaces the header upgrade CTA (PR #44494, which design team wanted to iterate on) with a placement experiment that tests three non-chrome surfaces for the free-plan "Upgrade to Pro" CTA. PostHog flag `upgradeCtaPlacement` (free-plan users only) with four arms: | Variant | Surface | | --- | --- | | `control` | No CTA (baseline cohort, still tracked) | | `user_dropdown` | Full-width button pinned in the account dropdown | | `org_projects_list` | Project-card-shaped usage tile, first card in the org project grid | ## Details ### `user_dropdown` - Full-width `Upgrade to Pro` button in `UserDropdown`, gated to org-scoped routes only (`/project/*`, `/org/*`) so the org-billing CTA never shows on `/account`, `/organizations`, etc. — addresses the scope concern raised in review. - Dropdown uses controlled `open` state so it closes before navigation (it lives in the global layout, so a route change alone wouldn't dismiss the overlay). ### `org_projects_list` - `PlanUsageCard` renders as the first `<li>` in the project grid (via `ProjectList`'s `prependCard`), matching `ProjectCard` shape so it reads like another project tile. Also renders during the project-list loading state to avoid pop-in. <img width="3804" height="1494" alt="Arc 2026-06-08 20 02 54" src="https://github.com/user-attachments/assets/09c2218c-43d1-49ce-bae7-5075c9750d72" /> ### Shared card styling - Metric rows (Egress, Database size, Monthly active users, File storage) show `current / limit` with a progress ring; ring/value turn warning at ≥80% and over at ≥100%. - Rows are clickable deep-links to `/org/[slug]/usage#<anchor>` with a hover chevron and dashed separators; the same row component is used by both the embedded and project-card variants. - Skeleton placeholder renders from first paint so the card reserves layout while `useOrgUsageQuery` resolves. - Exposure is fired optimistically while the org query loads (skeleton shows immediately), but the experiment exposure event only fires once free-plan is confirmed. ### Telemetry - `upgrade_cta_clicked` with `placement: user_dropdown | home_usage_card | org_projects_list`. - `upgrade_cta_placement_experiment_exposed` with `variant` — the custom exposure event (snake_case experiment id `upgrade_cta_placement`; the flag key stays camelCase `upgradeCtaPlacement`). ### Header CTA sunset - `HeaderUpgradeButton` and its wiring in `LayoutHeader` / `MobileNavigationBar` removed (master's #46144 already removed the button; this branch drops the remaining `header_upgrade_cta_clicked` event). ## Before merging - [x] Create the `upgradeCtaPlacement` flag + experiment in PostHog (4 variants, free-plan targeting, custom exposure event `upgrade_cta_placement_experiment_exposed`). - [x] Archive the now-orphaned `headerUpgradeCta` flag. ## Test plan - [x] Override the flag per variant via the dev toolbar on staging; confirm each surface renders and `upgrade_cta_clicked` fires with the right `placement`. - [x] `control` shows no CTA but still emits the exposure event. - [x] Paid-plan org and self-hosted (`IS_PLATFORM=false`) show nothing. - [x] Clicking a metric row deep-links to the matching usage section; clicking Upgrade routes to billing. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Experimentally surface an “Upgrade to Pro” CTA in the user dropdown and on the projects page for eligible free-plan orgs. * Added a Plan Usage card showing free-plan metrics and upgrade prompts on the organization projects page; hides when irrelevant or errored. * Project list and its loading view support inserting a custom/prepend card in card mode. * **Telemetry** * Added tracking for CTA clicks and experiment exposure; placement is persisted per org. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: kemal <hello@kemal.earth> |
||
|
Jordi EnricandClaude Sonnet 4.6
|
9c572a56fd |
feat(logs): add realtime, supavisor, and pgbouncer to unified logs (#46786)
## Problem The unified logs view was missing three log sources that the backend already returns: Realtime (`realtime_logs`), Supavisor (`supavisor_logs`), and PgBouncer (`pgbouncer_logs`). Users had no way to filter or view logs from these services in the unified view. ## Fix - Added `realtime`, `supavisor`, and `pgbouncer` to `LOG_TYPE_PREDICATE` and `LOG_TYPE_EXPR` in the OTEL query builder so rows from these sources are matched and labeled correctly. - Added the three types to `LOG_TYPES` so filter chips appear in the UI. - Added icons (`Realtime` from the icons package, `Cable` from lucide-react for both pooler types) in `LogTypeIcon.tsx`. - Added display labels in `formatServiceTypeForDisplay` (`Realtime`, `Supavisor`, `PgBouncer`). - Fixed a pre-existing unsafe cast in `ServiceFlowPanel.tsx` where any log type not in the service flow allow-list (like the new types) would produce a truthy `serviceFlowType` and trigger a runtime error on row click. The fix checks against `SERVICE_FLOW_TYPES` before casting. Note: `pg_cron_logs` is not included because the backend otel query does not yet return that source. ## How to test 1. Open unified logs for a project that has Realtime activity. 2. In the log type filter, confirm `realtime`, `supavisor`, and `pgbouncer` chips are visible. 3. Toggle on `realtime` and confirm Realtime logs appear with the correct icon. 4. Click a realtime log row and confirm the detail panel opens on the raw JSON tab without a runtime error. 5. Toggle on `supavisor` or `pgbouncer` and confirm pooler logs appear if the project has connection pooler activity. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added support for three new log types — Realtime, Supavisor, and PgBouncer — in Unified Logs with display labels, icons, and filtering/viewing support. * **Bug Fixes / UI Behavior** * Service Flow “Overview” tab now only shows when the service type is recognized, preventing irrelevant overview content for unsupported log sources. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Claude Sonnet 4.6 <noreply@anthropic.com> |
||
|
Jordi EnricandClaude Opus 4.8
|
895726505f |
feat(studio): dedicated telemetry events for org audit log drains (#46733)
## Problem

The org Audit Log Drains page fires the same
`log_drain_save_button_clicked` and `log_drain_removed` telemetry events
as the project Log Drains page, even though they are distinct features
(project product logs vs. the org audit log). Org-scoped events should
have their own names and drop the project group.

## Fix

Add dedicated org-scoped events and use them in the org container:

- `audit_log_drain_save_button_clicked`
- `audit_log_drain_removed`

Both declare `groups: Omit<TelemetryGroups, 'project'>` (no project
group), matching the convention used by other org-scoped events (e.g.
the documents page events). The project Log Drains page keeps the
original `log_drain_*` events unchanged.

## How to test

- Open `/org/{slug}/audit-log-drains` (with the `auditLogsLogDrain` flag
enabled).
- Create a drain and confirm `audit_log_drain_save_button_clicked` fires
(with the destination type, org group, no project group).
- Delete a drain and confirm `audit_log_drain_removed` fires.
- Confirm the project Log Drains page still fires `log_drain_*` events.

<!-- This is an auto-generated comment: release notes by coderabbit.ai
-->

## Summary by CodeRabbit

* **Chores**
* Updated internal telemetry tracking for audit log drain operations to
improve monitoring and analytics of system behavior.

<!-- end of auto-generated comment: release notes by coderabbit.ai -->

Co-authored-by: Claude Opus 4.8 <noreply@anthropic.com>
|
||
|
Julian Domke
|
dfaf59010b |
feat(billing): show cancel subscription button on billing page (#46500)
Extracts the Cancellation Flow from the subscriptions side panel and adds a new button that initiates the flow (old journey is still possible): (screenshots see below) Verified manually: - ✅ confirmed the old downgrade flow works, Team -> Pro; Pro -> Free - ✅ confirmed the new downgrade flow works - ✅ button does not show up when on free plan; no flicker - ✅ button does not show up on enterprise/platform plan - ✅ verified button is disabled when managed by AWS marketplace (hardcoded in `useSelectedOrganizationQuery`) - ✅ verified button is disabled if `canUpdateSubscriton` is false, hardcoded in `useAsyncCheckPermissions` - ✅ modal for exceeding-free-projects shows up <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added a guided subscription cancellation flow with confirmation steps, member/usage checks, and an exit survey. * Exposed a visible "Cancel Subscription" control in billing settings, enabled/disabled with contextual tooltip messaging. * **Improvements** * Downgrade/exit survey confirm action can be disabled when appropriate; exit survey confirm label updated to "Downgrade Now". * **Chores** * Added frontend telemetry for cancellation button interactions. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Paul CioancaandKevin Grüneberg
|
bc6a459fd2 |
feat(upgrades): prevent upgrades for hibernated projects (#46109)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? * Prevents hibernated projects from undergoing database version upgrades <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added support for hibernating projects in upgrade warnings. Users will now see a clear message indicating their project is hibernating and will resume on the next supported request. * **Chores** * Extended log drain configuration to support additional destination types. <!-- review_stack_entry_start --> [](https://app.coderabbit.ai/change-stack/supabase/supabase/pull/46109?utm_source=github_walkthrough&utm_medium=github&utm_campaign=change_stack) <!-- review_stack_entry_end --> <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Kevin Grüneberg <k.grueneberg1994@gmail.com> |
||
|
Pamela Chia
|
7f5e3cab93 | chore(studio): remove expired Fly.io deprecation banner (#46535) | ||
|
Pamela Chia
|
9da249135c | fix(telemetry): fix and unify dashboard_error_created tracking (#46537) | ||
|
Saxon Fletcher
|
033daf223c |
Support form Assistant Streamdown (#46248)
Re-adds support form Assistant response using a lighter weight Streamdown component vs the more heavy `Message` component. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * AI Assistant follow-up card after ticket submission for project-scoped requests. * In-chat support request preview panels showing submitted subject and message. * **Improvements** * Smarter project selection when opening the support form via route/context. * Success screen: cleaner layout, project-name messaging, optional finish action, and a "Join Discord" button. * Category prompt text updated to "What issue are you having?" * New success/feedback section for consistent layouts. * **Tests** * Added tests covering support prompt serialization/parsing and UI previews. <!-- review_stack_entry_start --> [](https://app.coderabbit.ai/change-stack/supabase/supabase/pull/46248?utm_source=github_walkthrough&utm_medium=github&utm_campaign=change_stack) <!-- review_stack_entry_end --> <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Sean Oliver
|
2c651ddabc | fix(experiment): make dataApiRevokeOnCreateDefault flag reads shape-agnostic (#46289) | ||
|
Danny WhiteandClaude Sonnet 4.6
|
7283459a02 |
chore(studio): use ShortcutBadge in Connect command (#46245)
## What kind of change does this PR introduce?
Refactor
## What is the current behavior?
FE-3452: `Connect.Commands.tsx` has a local `ConnectShortcutBadge`
component that hand-rolls the same Fragment + `KeyboardShortcut` +
"then" separator loop that `ShortcutBadge` already provides.
FE-3453: The `'header_button' | 'connect_section' | 'keyboard_shortcut'`
union is written out twice: once in `app-state.ts` and once in the
`ConnectSheetOpenedEvent` telemetry type in `telemetry-constants.ts`.
## What is the new behavior?
FE-3452: `ConnectShortcutBadge` is removed; the badge uses
`<ShortcutBadge shortcutId={SHORTCUT_IDS.CONNECT_OPEN_SHEET} />` inline.
FE-3453: A `ConnectSheetSource` type is exported from
`telemetry-constants.ts` and imported into `app-state.ts`.
## Additional context
- Resolves FE-3452
- Resolves FE-3453.
<!-- This is an auto-generated comment: release notes by coderabbit.ai
-->
## Summary by CodeRabbit
* **Refactor**
* Consolidated shortcut badge rendering to use a shared component across
the application, improving code maintainability and reducing
duplication.
* Introduced a centralized type definition for connect sheet source
tracking, enhancing type consistency throughout the codebase.
<!-- review_stack_entry_start -->
[](https://app.coderabbit.ai/change-stack/supabase/supabase/pull/46245?utm_source=github_walkthrough&utm_medium=github&utm_campaign=change_stack)
<!-- review_stack_entry_end -->
<!-- end of auto-generated comment: release notes by coderabbit.ai -->
---------
Co-authored-by: Claude Sonnet 4.6 <noreply@anthropic.com>
|
||
|
Danny WhiteandAli Waseem
|
25c8194579 |
feat(studio): add Connect sheet shortcut guidance (#46185)
## What kind of change does this PR introduce? Feature, docs update. - Resolves FE-3419 - First pass for DEPR-578 ## What is the current behaviour? The Connect sheet can be opened from visible UI and command-menu actions, but it does not have a direct keyboard shortcut. Studio also has shortcut conventions in code, but limited agent-facing review guidance for contributors adding or touching Studio UI. ## What is the new behaviour? FE-3419: - Adds `O then C` to open the Connect sheet for active healthy projects. - Mounts the shortcut from the always-rendered Connect sheet, so it works without first opening the lazy command menu. - Surfaces the shortcut on the Connect button tooltip, in the shortcuts reference sheet, and on the Connect command-menu action. - Forces the tooltip closed while the sheet is open so Escape closes the sheet without also driving tooltip state. - Tracks keyboard shortcut opens with the existing Connect sheet telemetry event. - Moves single-item AI Assistant and Inline Editor shortcuts to the _Global Actions_ section in the cheatsheet. DEPR-578: - Adds a short Studio shortcut convention to `.claude/CLAUDE.md`. - Adds scoped Copilot review guidance for Studio shortcut coverage, discovery, and collision checks. - Points the guidance back to the existing shortcut registry, `useShortcut`, `Shortcut`, and `ShortcutTooltip` implementation context. | After | | --- | | <img width="1576" height="188" alt="CleanShot 2026-05-21 at 11 30 40@2x" src="https://github.com/user-attachments/assets/ba9d68c8-27ea-4c89-8016-d95d5bcea3ea" /> | | <img width="830" height="364" alt="CleanShot 2026-05-21 at 11 48 51@2x-FC627CB5-4A1C-49E2-B748-8AF0A3EBD7BC" src="https://github.com/user-attachments/assets/d6aa52c1-56b2-4731-8e6b-088e29da43ed" /> | Validation: - `pnpm --dir apps/studio exec vitest --run components/ui/GlobalShortcuts/ShortcutsReferenceSheet.test.tsx components/interfaces/ConnectButton/Connect.Commands.test.tsx components/interfaces/ConnectSheet/useConnectSheetShortcut.test.ts` - `git diff --check` <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Keyboard shortcut to open the Connect sheet from anywhere; Connect button displays the shortcut and is enabled only for eligible projects. * New "Global Actions" group in the shortcuts reference including AI Assistant, Inline Editor, and Connect. * **Documentation** * Added Studio keyboard-shortcuts guidance and linked it in project instructions. * **Tests** * Added tests covering connect shortcut behavior and command registration. * **Telemetry** * Connect-sheet open events now record keyboard shortcut as a source. <!-- review_stack_entry_start --> [](https://app.coderabbit.ai/change-stack/supabase/supabase/pull/46185?utm_source=github_walkthrough&utm_medium=github&utm_campaign=change_stack) <!-- review_stack_entry_end --> <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Ali Waseem <waseema393@gmail.com> |
||
|
Joshen Lim
|
d11bd4997e |
Revert "Support form Assistant" (#46194)
Reverts supabase/supabase#45861 <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit ## Release Notes * **New Features** * Support form now returns to home view upon completion within the help panel. * Success screen conditionally displays community (Discord) section for specific issue categories. * **Bug Fixes** * Improved project selection logic in support form initialization. * **Style** * Updated support form label text for clarity. * Redesigned success screen layout with updated styling and separators. * **Removed Features** * Removed support assistant follow-up card from success screen. * Removed support request message parsing from AI responses. <!-- review_stack_entry_start --> [](https://app.coderabbit.ai/change-stack/supabase/supabase/pull/46194?utm_source=github_walkthrough&utm_medium=github&utm_campaign=change_stack) <!-- review_stack_entry_end --> <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Saxon FletcherandGildas Garcia
|
af7d953f52 |
Support form Assistant (#45861)
When a support from is submitted, we believe there is an opportunity to help people before a human receives and responds. Human support is still involved regardless of whether Assistant helps or not, so this is to positioned as a "while you wait" type experience. ## To test: - Enable to `supportAssistantFollowUp` feature flag - Open a project - Open the support form and submit a request - Note the success state and the additional Assistant card - Note text generation in card - Clicking card should open the Assistant conversation <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * AI assistant follow-up card appears after submitting a support ticket to continue the conversation * Support request preview rendered in the assistant panel showing subject/message when present * **Bug Fixes** * Improved project selection fallback during support form initialization * **Improvements** * Refined success layout and messaging; finish action behavior simplified [](https://app.coderabbit.ai/change-stack/supabase/supabase/pull/45861) <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Gildas Garcia <1122076+djhi@users.noreply.github.com> |
||
|
Mert YEREKAPAN
|
1ef80fec23 |
chore(studio): remove HeaderUpgradeButton experiment code (#46144)
## Summary - Removes the `HeaderUpgradeButton` component, all call sites, and the `HeaderUpgradeCtaClickedEvent` telemetry type. The GROWTH-615 header upgrade CTA experiment ended on Apr 29. - Fixes the `Flag key "headerUpgradeCta" does not exist in PostHog flag store` console errors that were logging on every render. PostHog drops disabled flags from `/feature-flags` responses, so the still-mounted consumer logged a missing-flag warning continuously. Removing the consumer lets the flag be safely disabled again. Context: [Slack thread](https://supabase.slack.com/archives/C07P3AU3J2D/p1779250648219089?thread_ts=1779166940.445709&cid=C07P3AU3J2D) ## Test plan - [x] `pnpm dev:studio`, open the dashboard, confirm no `headerUpgradeCta` warning in the browser console - [x] Desktop header still renders correctly (the button was hidden behind the `test` variant; visually nothing changes for users since rollout was 100/0 control) - [x] Mobile nav bar still renders with `UserDropdown` to the right of the org/project selector <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Chores** * Removed the upgrade call-to-action button from the navigation header in both desktop and mobile layouts. <!-- review_stack_entry_start --> [](https://app.coderabbit.ai/change-stack/supabase/supabase/pull/46144?utm_source=github_walkthrough&utm_medium=github&utm_campaign=change_stack) <!-- review_stack_entry_end --> <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Sean Oliver
|
fdceb29260 |
fix(telemetry): exposure event captures dataApiDefaultPrivileges + drop race-fix hook (#46085)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? Bug fix. ## What is the current behavior? This PR addresses three issues with the implementation of the `dataApiRevokeOnCreateDefault` experiment ([GROWTH-858](https://linear.app/supabase/issue/GROWTH-858)) on the frontend side: 1. The `project_creation_default_privileges_exposed` event payload captures `dataApiEnabled`, which is the parent "Enable Data API" toggle. That value defaults to `true` for everyone in both arms, which doesn't help understand how people are interacting with the form. 2. The hook itself was gating on PostHog JS SDK values rather than our backend server values being sent from `/telemetry/feature-flags`. 3. The form on `/new/[slug]` captures `dataApiDefaultPrivileges` defaults once at mount via react-hook-form's `defaultValues`. If the flag is still loading when the page mounts, `useDataApiRevokeOnCreateDefaultEnabled()` returns `false` (coerced from undefined), and the form locks the field to the legacy default of `true`. The flag later resolving has no effect, and treatment users get the legacy default visually and in the exposure event. ## What is the new behavior? 1. Main-surface payload now sends `dataApiDefaultPrivileges` — the form field the experiment actually controls (`true` = legacy grants kept, `false` = revoked on create). Post-fix data will let us read out whether treatment users actually got the new default. 2. Hook is simplified: drop `orgCountReady`, drop the `onFeatureFlags` subscription, drop the `posthogClient` import. It now fires once when the flag resolves, period. Vercel surface is unchanged (still no `dataApiDefaultPrivileges` since there's no user-facing toggle there). Tests updated. 3. New useEffect in `/new/[slug]` watches the raw flag value and syncs `dataApiDefaultPrivileges` to the correct experiment-driven default when the flag resolves, gated on `getFieldState(...).isDirty` so we don't clobber intentional user input. ## Additional context Backend half of this fix is at supabase/platform#32933 (passes `org_count` and `signup_timestamp` in `personProperties` so the audience filter actually evaluates correctly). Both PRs are needed for the experiment to bucket at 5% and be measurable. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Changes** * Telemetry now records the selected default-privileges setting (dataApiDefaultPrivileges) in project-creation events; the previous dataApiEnabled field was removed. * Project-creation flows apply the experiment-driven default for that setting once the experiment resolves, but they do not overwrite user-edited choices. Vercel new-project flow syncs with the experiment until the user changes the checkbox. * **Tests** * Updated tests to validate tracking, deduplication, and sync/timing behaviors for dataApiDefaultPrivileges. <!-- review_stack_entry_start --> [](https://app.coderabbit.ai/change-stack/supabase/supabase/pull/46085?utm_source=github_walkthrough&utm_medium=github&utm_campaign=change_stack) <!-- review_stack_entry_end --> <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Pamela Chia
|
0bed80b340 |
chore(telemetry): clean up frontend event catalog (#45964)
## Summary Resolves 13 findings (2 HIGH, 5 MEDIUM, 6 LOW) from the frontend telemetry audit: 1 action-string collision, 1 camelCase experiment name, 9 dead events removed, 4 missing org groups attached, 1 ambiguous property renamed, 1 raw-string property narrowed, plus consolidations and a structural tightening on TABLE_EVENT_ACTIONS. ## Changes ### HIGH - Rename `EventPageCtaClickedEvent.action` to `www_event_page_cta_clicked` so it no longer collides with the pricing CTA event (which had a different schema sharing the same action string) - Snake_case the header-upgrade experiment exposure name (`headerUpgradeCta_experiment_exposed` → `header_upgrade_cta_experiment_exposed`); PostHog flag key and `?source=` URL param unchanged ### MEDIUM - Remove 4 dead `ProjectCreation*Step*` events (referenced a v2 route that doesn't exist; 0 emissions) - Remove 4 dead experiment exposure events: `ProjectCreationRlsOptionExperimentExposed`, `HomeNewExperimentExposed`, `TableCreateGeneratePoliciesExperimentExposed`, `TableCreateGeneratePoliciesExperimentConverted` (0 emissions) - Attach org group to `dpa_request_button_clicked` (0% had `$group_0` per Hex) - Delete `RegisterStateOfStartups2025NewsletterClicked` (interface naming outlier, 0 emissions, page renamed to 2026) - Rename `AssistantSuggestionRunQueryClickedEvent.category` to `mutationType` with tightened literal union (`'functions' | 'rls-policies' | 'unknown'`) - Attach org group to `project_creation_default_privileges_exposed` on Vercel surface via explicit `groupOverrides` (auto-injection misses because `useSelectedOrganizationQuery` is undefined on that page) ### LOW - Consolidate `IndexAdvisorBannerEnableButtonClickedEvent` + `IndexAdvisorDialogEnableButtonClickedEvent` into one event with `origin: 'banner' | 'dialog'` - Rename `ImportDataFileDroppedEvent` → `ImportDataFileAddedEvent` so the interface name matches the action and the verb is on the approved list - Rename `LogDrainConfirmButtonSubmittedEvent` → `LogDrainRemovedEvent` and action to `log_drain_removed` (fires on delete-confirm modal, matches `CronJobRemovedEvent` pattern) - Add `type` property to `CronJobRemovedEvent` (parsed from the job's command), matching the create/update event shape - Tighten `TABLE_EVENT_ACTIONS` values with `satisfies` against the event union so renames in the union fail typecheck here too - Attach org group to `www_pricing_plan_cta_clicked` at 5 emission sites when an org is available in the page context - Narrow `unified_logs_row_clicked.logType` from raw `string` to the 5-literal `LOG_TYPES` union (zod already validates server values) ### Bundled refactor Migrated 5 emission sites from deprecated `useSendEventMutation` to `useTrack` while their containing files were being edited: `DPA.tsx`, `DisplayBlockRenderer.tsx`, `Grid.tsx` (2 events), `DeleteCronJob.tsx`. Full sweep of the remaining ~79 files is a separate follow-up. ## Testing Mostly just renaming of events ## Linear - fixes GROWTH-798 <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Refactor** * Standardized telemetry to a unified tracking system for more consistent analytics. * Simplified experiment exposure reporting for upgrade prompts. * **New Features** * More granular tracking for CSV import, cron job deletions, log drain removals, DPA downloads/requests, and pricing CTAs. * Assistant now classifies mutation queries more precisely. * **Bug Fixes** * Improved default-privileges exposure logic on Vercel deployments (skips when org missing). <!-- review_stack_entry_start --> [](https://app.coderabbit.ai/change-stack/supabase/supabase/pull/45964) <!-- review_stack_entry_end --> <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Joshen Lim
|
2d47836f39 |
Joshen/fe 3213 make rls tester feedback callout more obvious (#45820)
## Context Minor nit to adjust the "Give feedback" button at the bottom to use default type + external link icon <img width="612" height="68" alt="image" src="https://github.com/user-attachments/assets/e74370cb-d284-4552-a69d-8c838f565af7" /> Also added telemetry for the "Run query" button <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added analytics tracking for RLS Tester query runs to better understand how the feature is used. * **Style** * Updated the "Give feedback" button in the RLS Tester to use the default button style and display an external-link icon for clarity. [](https://app.coderabbit.ai/change-stack/supabase/supabase/pull/45820) <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Pamela Chia
|
e55411da5e |
feat(studio): Fly.io deprecation banner (#45778)
## Summary Adding an in-dashboard banner for the Fly.io May 31 suspension. Banner targets users on a Fly project (or with a Fly project in their currently-selected org) and surfaces a per-project breakdown of what's affected in a dialog. Detection is self-correcting: as soon as the user migrates off Fly, the banner disappears with no follow-up. <img width="557" height="502" alt="Screenshot 2026-05-11 at 5 08 22 PM" src="https://github.com/user-attachments/assets/7bafb712-3490-4555-9667-66e9909f1b1a" /> <img width="1675" height="536" alt="Screenshot 2026-05-11 at 3 55 06 PM" src="https://github.com/user-attachments/assets/6c1bf9d1-4dcc-4aac-a679-2ed477d2ed1c" /> ## Changes - **Detection hook** (`useFlyDeprecationProjects`): reads only from already-cached data — `useSelectedProjectQuery` for the current project, plus `useOrgProjectsInfiniteQuery` scoped to the selected org. Zero cross-org fan-out: worst case is one paginated query per session (the same one the project list page already makes). - **Banner component** (`FlyDeprecationBanner.tsx`): mounted in `AppBannerWrapper`. Dynamic title (primaries / branches / both), dialog lists affected projects with org name, numbered migration steps, links to backup/restore CLI + Dashboard backup + branching docs. List truncates to 5 entries with "…and N more." tail when more are affected. - **Telemetry**: `fly_deprecation_banner_exposed` and `fly_deprecation_banner_dismissed` events emitted via `useTrack` (auto-injects project + org groups). Properties: `primaryCount`, `branchCount`. CTA click tracking intentionally omitted — migration outcome is measured via warehouse `cloud_provider = 'FLY'` decay. - **LocalStorage**: dated dismissal key `FLY_DEPRECATION_2026_05_31`; orphan `FLY_POSTGRES_DEPRECATION_WARNING` from PR #33510 removed in the same change so users who dismissed the Feb 2025 banner still see this one. - **Support contact**: email `success@supabase.io` only (no support ticket link), per Brian's outreach copy in the Linear issues. ## Coverage trade-off Banner renders on project pages (selected-project check) and pages where the selected org's projects list is cached (org overview, project list). It does **not** render on `/dashboard` home or other pages without org context. Email outreach from GROWTH-817 / GROWTH-819 handles those users. This was a deliberate trade-off to avoid cross-org fan-out load. ## Lifecycle Banner expires `2026-06-01T00:00:00Z` (right after the May 31 deadline). Stale client bundles stop rendering it without a redeploy. Cleanup PR planned post-deadline to remove the component, hook, localStorage key, and telemetry events. ## Testing Tested on the Vercel preview with React Query cache overrides to mock a Fly project: - [x] Banner renders for a user with at least one project where `cloud_provider === 'FLY'` - [x] Banner does **not** render for a user with no Fly projects - [x] Banner does **not** render on `/sign-in` - [x] Title varies by primaries-only / branches-only / both - [x] Dialog lists affected projects with org name in parens - [x] Dialog list truncates to 5 with "…and N more." for larger sets - [x] Migration guide / Dashboard backup / branching links open in a new tab - [x] Dismiss (×) closes the banner and persists across hard reload (localStorage `fly-deprecation-2026-05-31-dismissed`) - [x] PostHog receives one `fly_deprecation_banner_exposed` per mount with `primaryCount` + `branchCount` and `$groups.organization` populated - [x] PostHog receives one `fly_deprecation_banner_dismissed` on close with the same property shape ## Linear - fixes GROWTH-817 - fixes GROWTH-819 |
||
|
Joshen Lim
|
94851d1f8f |
Add assistant CTA for query errors in RLS tester (#45628)
## Context Adding an "Ask Assistant" CTA in the RLS tester if the query executed returns an error <img width="618" height="375" alt="image" src="https://github.com/user-attachments/assets/8b0a5069-3ec5-44aa-aa0b-f1cd8041960d" /> Which will open the Assistant panel with the following prompt (attaches the query as well) <img width="427" height="281" alt="image" src="https://github.com/user-attachments/assets/16debd7b-9447-4b84-bef5-05debd0062ee" /> Theres a chance that the error might be just from the query and not related to the policy hence the last sentence in the prompt <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Integrated AI assistant into the RLS tester so users can open the assistant prefilled with a debug prompt and relevant SQL to troubleshoot policy issues. * Added an "Ask Assistant" action on execution error messages to quickly start guided debugging. * Streamlined error display to prioritize parse errors, then client-code parse errors, then execution errors for clearer diagnostics. * **Chores** * Added telemetry source identifier for the RLS tester to track assistant usage. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Saxon FletcherandGildas Garcia
|
ae66a6a9c0 |
Connect GitHub during project creation (#44884)
<img width="1289" height="863" alt="image" src="https://github.com/user-attachments/assets/d661f107-b358-4894-8531-80441d60ab91" /> GitHub integration is now available on the free plan and so we'd like to start promoting code-first workflows as much as possible. One way to do that is to set the tone straight away by asking a user to connecting their GitHub repository to a project as part of project creation. This PR: - decouples GitHub connection and repo selection into a separate component we can make use of in integration settings and project creation. - Adds new GitHub fields to project creation form and sends them off to project creation endpoint - Pre-fills project name based on repo selection To test locally: - Ensure you have GitHub integration set up locally (using ngrok etc) - Ensure you are on the connected platform branch - Open create a new project page - Connect GitHub as part of the creation form and select a repo - Create the project and wait for status to be healthy - Check project settings integrations page and ensure repo is connected Note: - this requires changes on the management api end to accept new GitHub fields - it might make sense to pull out GitHub connection/authorization from GitHub repository selection but in the current state they are tied together. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit ## Release Notes * **New Features** * GitHub repository selection now available during project creation with integrated authorization flow * GitHub connection status and compute availability indicators now displayed on project dashboard * Project name auto-populates from selected GitHub repository name when available <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Gildas Garcia <1122076+djhi@users.noreply.github.com> |
||
|
Jordi Enric
|
d8bb0ade65 |
feat(studio): add timezone picker to user dropdown (#45517)
## Problem The dashboard renders all timestamps in the browser's local timezone. When debugging app issues, users often want to see logs and timestamps in a different timezone (e.g. their app's deployment region) without changing their OS clock. ## Fix - New Timezone submenu in the user-avatar dropdown, sitting next to the existing Theme picker. Search-as-you-type combobox over the full IANA catalog plus an Auto detect option. - Selection persists in localStorage (`supabase-ui-timezone`) and survives `clearLocalStorage()`. No backend schema change. - New `lib/datetime.tsx` exposes pure timezone-aware formatters (`formatDateTime`, `formatDate`, `formatTime`, `formatFromNow`, `toTimezone`) plus a `TimezoneProvider` and matching React hooks (`useTimezone`, `useFormatDateTime`, ...). The pure functions take `tz` explicitly so they're easy to unit test (17 vitest cases covering DST transitions, multi-tz formatting, unix-micro/Date inputs, invalid-tz fallback). - The selected timezone propagates to every existing `<TimestampInfo>` in Studio via a new `TimestampInfoProvider` context exported from `ui-patterns`. No per-callsite changes needed for those ~20+ surfaces. - The `UnifiedLogs` date column migrates off `date-fns` to the new `useFormatDateTime` hook (the rest of the date-fns callers stay as-is, since they're either internal range math or non-display). - `ALL_TIMEZONES` (~600 entries) moves out of `PITR.constants.ts` into a shared `lib/constants/timezones.ts`. PITR keeps a re-export shim so its callers don't move. New `TIMEZONES_BY_IANA` dedupes the catalog by primary IANA name (the original list contains both PDT and PST rows for `America/Los_Angeles`, etc.) and `findTimezoneByIana` provides reverse lookup. - Telemetry: `timezone_picker_clicked` PostHog event with `previousTimezone`, `nextTimezone`, `isAutoDetected` properties. Notes for reviewers: - Bare `dayjs(x).format(...)` calls (~157 files) intentionally still render in browser-local time. Surfaces opt in by switching to the new wrappers, so this PR is the abstraction plus logs adoption; broader migration is a follow-up. - Two `// prettier-ignore` lines (`apps/studio/pages/_app.tsx`, `apps/studio/components/interfaces/UnifiedLogs/UnifiedLogs.fields.tsx`) work around a pre-existing local-tooling issue where `prettier-plugin-sql-cst` strips angle-bracket type arguments under certain conditions. Project's pinned prettier (3.8.1) does not strip; the issue surfaces with a globally-installed prettier. Worth tracking separately. - Hydration: `guessLocalTimezone()` and `useLocalStorageQuery` are client-only. Studio is mostly CSR via the Pages Router, but any SSR'd `<TimestampInfo>` may briefly render in the server's tz before client hydration. Existing behavior already had this mismatch with `.local()`; this PR does not regress it. - Backend timestamps round-tripped through query params and mutations stay UTC. The picker is display-only. ## How to test - Run `pnpm dev:studio`, sign in. - Open the user avatar dropdown (top right). Hover Timezone. - Search for "tokyo", pick `(UTC+09:00) Osaka, Sapporo, Tokyo`. - Open any project, navigate to Logs (e.g. `Project > Logs > Edge Functions`). Hover a log row's timestamp; the popover should show UTC, the chosen tz (`Asia/Tokyo`), and the relative time. Visible cell text should be in JST. - Visit any page that uses `<TimestampInfo>` (Database > Backups, Project Pause state, Edge Function details). Same tooltip should reflect Asia/Tokyo. - Refresh the page; timezone is still Asia/Tokyo. - Reopen the picker, choose Auto detect; timestamps revert to browser local. - Run `pnpm --filter studio test lib/datetime.test.ts`. 17 tests should pass. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Timezone selector added to the user menu with auto-detect and manual override * App-wide timezone provider and hooks plus a shared timezone catalog for consistent timezone-aware display * Timestamp components accept an optional timezone prop and respect user preference (persisted) * **Bug Fixes / Improvements** * Logs and timestamp displays now use the new timezone formatting hooks * **Tests** * Added comprehensive datetime and timezone catalog tests * **Telemetry** * Telemetry event added for timezone picker interactions <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Mert YEREKAPAN
|
da81b2f14d |
feat(studio): add click tracking for top bar buttons (#45414)
## Summary Adds PostHog click/open tracking for every interactive element in the Studio top bar. Previously only 5 of ~16 surfaces were tracked. ### New events (16) | Event | Surface | |---|---| | `home_logo_clicked` | Supabase logo | | `header_back_to_dashboard_clicked` | Mobile back chevron | | `header_exceeding_usage_badge_clicked` | "Exceeding usage limits" badge | | `organization_dropdown_opened` | Org dropdown trigger | | `project_dropdown_opened` | Project dropdown trigger | | `branch_dropdown_opened` | Branch dropdown trigger | | `merge_request_button_clicked` | MR trigger (separate from existing success event) | | `connect_button_clicked` | Connect CTA | | `feedback_dropdown_opened` | Feedback dropdown trigger | | `advisor_button_clicked` | Advisor toggle | | `inline_editor_button_clicked` | SQL editor toggle | | `assistant_button_clicked` | AI Assistant toggle | | `user_dropdown_opened` | Account dropdown | | `local_dropdown_opened` | Local-dev settings dropdown | | `local_version_popover_opened` | CLI version popover | ### Notes - Uses `useTrack` (per `telemetry-standards`), all event names use approved `_clicked` / `_opened` verbs. - Dropdown `onOpenChange` handlers guard against Radix's double-fire by only tracking when `open === true`. - `merge_request_button_clicked` fires on the trigger click; the existing `branch_create_merge_request_button_clicked` continues to fire on successful MR creation. - Pre-existing tracked surfaces (`command_menu_opened`, `help_button_clicked`, `header_upgrade_cta_clicked`, `send_feedback_button_clicked`) are unchanged. ## Test plan - [x] Spot-check each event fires once per interaction in PostHog Live Events - [x] Verify no double-fire on dropdown close <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Chores** * Added telemetry tracking for many header/navigation interactions (logo, back-to-dashboard, usage badge, connect/merge/advisor/assistant/inline-editor buttons, and multiple dropdowns/popovers). * **Tests** * Updated tests to stub telemetry calls so UI tests remain stable and deterministic. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Alex Hall
|
baaf07002f |
chore(studio): add method property to integration installation events (#45473)
Add new `method` property to existing event to distinguish from server-side emitted events |
||
|
Mert YEREKAPAN
|
34241f1f66 |
revert(pricing): remove A/B experiment, keep control (#44293) (#45361)
Reverts the pricing page flexibility/visibility A/B experiment from #44293. We decided to keep the control (original pricing page). **Changes:** - `PricingPlansSection.tsx`: removed all experiment logic (PostHog flag evaluation, exposure tracking, flexibility section) - `PricingContent.tsx`: removed `PricingPageExperimentVariant` type export - `PricingPlans.tsx`: removed `experimentVariant` prop and all variant-conditional rendering - `telemetry-constants.ts`: removed `PricingPageExperimentExposedEvent` <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Refactor** * Consolidated pricing page component variants and simplified the component hierarchy by removing conditional experiment-dependent UI branches. * Removed pricing page experiment tracking and associated telemetry event definitions. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Saxon FletcherandJoshen Lim
|
3b756e4d9f |
Chore/project secure (#45108)
<img width="2652" height="830" alt="image" src="https://github.com/user-attachments/assets/3c3921e7-c255-4e59-a9c3-c5f97da87788" /> Adds a full screen alert behind a feature flag `projectNeedsSecuring` that prompts for fixing RLS issues. Adjusts a few other small styles to add more prominence to critical advisor issues. To test: - Enable the flag - Make sure you have a table with RLS disabled - Open project home and note the fade in of full page review - Click "copy prompt" or "fix" and note the prompt - Click skip to home and refresh the page, note it doesn't appear anymore <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Project-level security gate on project home with AI assistant prompts, table details, per-project dismissible notice, and a new telemetry event for CTA interactions. * **Improvements** * Stronger visual treatment for critical advisor items and advisor CTA when critical issues exist. * Assistant dropdown supports a copy-prompt callback; added local-storage key and utilities/types to support project security workflows. * **Tests** * Added tests covering gate behavior, navigation, and dismissal logic. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Joshen Lim <joshenlimek@gmail.com> |
||
|
kemal.earth
|
4ec48666d2 |
feat(studio): unified logs guard change (#44962)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? This changes the guard to expose unified logs to Enterprise. **To test:** - Create an Enterprise org. - Go to a project and then Logs. - Default view should be unified logs (with a CTA offering to switch back to old logs). <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added enterprise/Supabase-org eligibility checks and loading state for the unified logs preview. * **UX** * Updated messaging to state unified logs are only available to Enterprise plan organizations. * Sidebar and filter panels now show unified-logs preview panels based on eligibility. * **Analytics** * Track unified logs row clicks with a new telemetry event. * **Bug Fixes** * Prevent navigation until unified-logs eligibility and preview flag loading are resolved. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Alaister YoungandAlaister Young
|
75e08577c1 |
chore(studio): remove tableEditorApiAccessToggle flag (#45081)
Cleans up the `tableEditorApiAccessToggle` PostHog flag now that the gated UI is shipping to everyone. Follow-up to #45034 — the new project-creation checkbox makes the management UI a prerequisite, so no reason to keep it behind a flag. **Removed:** - `useDataApiGrantTogglesEnabled` hook - Old schemas-only multi-selector branch in the Data API settings page (the rich per-table / per-function toggles + default-privileges switch become the only UI) - Flag gate around the `<ApiAccessToggle>` section in the table editor side panel - Flag gates around `updateTableApiAccess` calls in the save pipeline (create / duplicate / update) - `tableEditorApiAccessToggleEnabled` telemetry property + stale JSDoc / docs references **Changed:** - `createTableApiAccessHandlerParams` no longer takes an `enabled` param — it was always `true` after removal ## To test - Integrations → Data API settings page: exposed tables, exposed functions, default-privileges toggle all render and save correctly - Table editor: creating, duplicating, and editing a table all run the expected Data API privilege updates - Project creation flow still works end-to-end (unchanged, but the submit telemetry no longer includes `tableEditorApiAccessToggleEnabled`) <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Improvements** * API access configuration is now always available in the table editor and PostgreSQL settings, removing previous conditional gating. * Simplified the "Automatically expose new tables and functions" interface by consolidating UI branches. * **Documentation** * Updated telemetry guidance and examples with current feature-flag references. <!-- end of auto-generated comment: release notes by coderabbit.ai --> Co-authored-by: Alaister Young <10985857+alaister@users.noreply.github.com> |
||
|
|
d1a7d64e63 |
[FE-3023] feat(studio): default privileges toggle at project creation (#45034)
<img width="783" height="414" alt="Screenshot 2026-04-20 at 3 02 37 PM" src="https://github.com/user-attachments/assets/a353c35a-3de5-4bfa-ab31-829c79c43165" /> Adds a "Default privileges for new entities" checkbox under "Enable Data API" in both the main create flow and the Vercel deploy-button flow. Default checked (current behaviour). When unchecked, runs `buildDefaultPrivilegesSql('revoke')` after the base init script so new entities in `public` aren't auto-granted to `anon` / `authenticated` / `service_role`. This PR decouples the two surfaces: - **`tableEditorApiAccessToggle`** — unchanged; still gates only the integrations → Data API settings UI. - **`dataApiRevokeOnCreateDefault`** (new) — controls only the default state of the new checkbox at project creation. `true` → checkbox unchecked by default (revoke runs); `false`/absent → checkbox checked by default (no behaviour change). The new flag is already live in PostHog at **0% rollout, off for everyone**, so shipping this PR changes nothing until the flag is explicitly flipped. ## Added - `apps/studio/hooks/misc/useDataApiRevokeOnCreateDefault.ts` — reads the new PostHog flag. Returns `false` in `IS_TEST_ENV` so existing E2E flows don't silently change default behaviour. - Checkbox UI in `SecurityOptions.tsx` (main flow) and `pages/integrations/vercel/[slug]/deploy-button/new-project.tsx` (Vercel flow), with copy matching the integrations → Data API settings page. - Tooltip + dimmed state for the main-flow checkbox when "Enable Data API" is unchecked (can't configure default privileges if Data API is off). - Telemetry: `dataApiDefaultPrivilegesGranted` (raw checkbox value) and `dataApiRevokeOnCreateDefaultEnabled` (raw flag, conditionally included using the existing raw-flag pattern so undefined flag state → omitted property, not `false`). - Vitest unit tests for the new hook. ## Changed - `pages/new/[slug].tsx`: removed the `false &&` rollback guard. Revoke SQL now runs only when `dataApi && !dataApiDefaultPrivileges`. Dropped the now-unused `useDataApiGrantTogglesEnabled` import. - `pages/integrations/vercel/[slug]/deploy-button/new-project.tsx`: this flow was **never rolled back** — it still ran revoke whenever `tableEditorApiAccessToggle` was on for a user. Now correctly gated on the new flag + checkbox state. - `packages/common/telemetry-constants.ts`: added the two new properties and corrected the `tableEditorApiAccessToggleEnabled` docstring (it no longer claims to control project-creation revoke behaviour). ## Kill switch Flipping `dataApiRevokeOnCreateDefault` to off in PostHog fully disables the revoke SQL for new projects without needing a redeploy — the checkbox just defaults to checked again. ## Follow-ups (not blockers) - joshenlim's review comments on PR 43704: (1) Auth Policies table row incorrectly showing "exposed via Data API" based on schema-level check instead of table-level at `apps/studio/components/interfaces/Auth/Policies/PolicyTableRow/index.tsx:64`; (2) Data API integrations page showing zero exposed tables even after exposing one. Both unrelated to this PR but will be more visible once the checkbox lands. - Once this flag fully rolls out, the old `tableEditorApiAccessToggle` docstring/comments elsewhere should stop claiming it controls project creation. ## To test - **Flag off (default state, simulates post-merge):** create a project with and without "Enable Data API" checked. The new "Default privileges for new entities" checkbox should default to **checked**. Submitting should produce an identical result to today — new tables in `public` are reachable via the Data API. - **Flag on (simulate rollout):** override the flag locally. The checkbox should default to **unchecked**. Creating a project with it unchecked should run the revoke SQL; create a new table in `public` afterwards and confirm it's not reachable via the Data API until grants are added. - **Enable Data API off:** the new checkbox should render disabled + dimmed with a tooltip reading "Enable the Data API to configure default privileges." The revoke SQL should not run in this case regardless of checkbox state. - **Vercel flow:** repeat at `/integrations/vercel/<slug>/deploy-button/new-project` — verify both checkbox states. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added an "Automatically expose new tables and functions" checkbox to project creation and Vercel deploy flow; enabled only when Data API is available (disabled with tooltip otherwise) and affects initial project provisioning. * **Telemetry** * Tracks exposure of the default-privileges control and includes checkbox state and feature-flag status on project-creation submissions. * **Tests** * Added tests for flag behavior, exposure tracking, deduplication, and submission telemetry. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Alaister Young <10985857+alaister@users.noreply.github.com> Co-authored-by: Sean Oliver <882952+seanoliver@users.noreply.github.com> |
||
|
Stephen MorganandJoshen Lim
|
bd55ad23a6 |
feat: iso27001 certificate (#44963)
Edit: Can be merged, mgmt api deployed Dashboard addition to frontend for access to the ISO 27001 certificate. View for Team customers: <img width="1737" height="1151" alt="image" src="https://github.com/user-attachments/assets/cd62d24f-8b6e-4600-9ded-943a170cd124" /> Resolves SEC-799 <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * ISO 27001 certificate added to Documents with a Download action, confirmation modal, new-tab open on success, and error toast on failure. * Users without billing permission see a no-permission view; users missing entitlement see an “Upgrade to Team” prompt. * **Refactor** * Upgrade-to-Team flows for SOC2 and related upgrade UI standardized to use the shared upgrade component. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Joshen Lim <joshenlimek@gmail.com> |
||
|
|
b721a2d780 |
feat(studio): advisor signal items for banned IPs (#44372)
## What kind of change does this PR introduce? Feature. Resolves DEPR-430. ## What is the current behaviour? The homepage Advisor summary, shared Advisor panel, and top-nav Advisor indicator only surface lints and notifications. Banned IPs are not represented as dismissible Advisor items, so network bans are easy to miss unless a user visits Database Settings directly. The `public bucket allows listing` warning is no longer part of this PR. That warning will move to a follow-up Splinter `WARN` lint so it can flow through the standard lint surfaces instead of a bespoke Studio signal path. ## What is the new behaviour? - adds a new Advisor `signal` source for banned IPs on the platform homepage, in the shared Advisor panel, and in the top-nav Advisor indicator - keeps dismissals client-side only for now, scoped by project and exact IP fingerprint - keeps banned IP signals at `warning` severity because they still indicate suspicious traffic and remain actionable if a user wants to review or remove a ban - leaves `/project/[ref]/advisors/security` as follow-up work because that surface is still lint-native, and banned IPs are management-plane signals rather than Splinter lints | After | | --- | | <img width="1728" height="997" alt="Mallet Toolshed Supabase-65A60B4A-107E-4D79-B9A8-23F754BEAB08" src="https://github.com/user-attachments/assets/c08ecbbb-c302-43bd-81bb-6ba7eb18b7b3" /> | ## Reviewer testing notes 1. Use a throwaway project. 2. Get the database connection string for that project. 3. Attempt to connect with the wrong password 3-4 times until you hit an `ECONNREFUSED`-style error, which should mean your IP has been banned. 4. Refresh Studio and confirm the project overview shows the new `Banned IP address` signal. 5. Open the Advisor Center and confirm: - the top-nav Advisor dot turns warning yellow - the signal detail shows `Entity`, `Issue`, and `Resolve` - `Edit network bans`, `Dismiss`, and `Learn more` are present 6. Open Database Settings > Network bans and confirm your banned IP appears there and can be unbanned. 7. Note that `/project/[ref]/advisors/security` will not show this item. That page is still lint-only, and this banned IP work is a short-term client-side signal rather than a true lint. Longer term, we likely want a more durable event model here so banned IPs can power notifications, webhooks, emails, and other project-level alerts. --------- Co-authored-by: kemal <hello@kemal.earth> Co-authored-by: Charis Lam <26616127+charislam@users.noreply.github.com> Co-authored-by: Claude Sonnet 4.6 <noreply@anthropic.com> Co-authored-by: Joshen Lim <joshenlimek@gmail.com> |
||
|
Ali Waseem
|
02325f00e7 |
feat(studio): add Copy as CSV option to SQL editor results (#44911)
## Summary - Adds a new "Copy as CSV" action to the export dropdown in the SQL editor results panel, alongside the existing Copy as Markdown, Copy as JSON, and Download CSV options - Registers a `Shift+Cmd+C` keyboard shortcut for the action, with a toggle in Account > Preferences > Keyboard shortcuts - Works everywhere `DownloadResultsButton` is used: SQL editor, logs, query performance, and linter pages Fixes FE-2991 ## Test plan - [x] Run a SELECT query in the SQL editor, open the Export dropdown, and verify "Copy as CSV" appears between "Copy as JSON" and "Download CSV" - [x] Click "Copy as CSV" and verify CSV data is copied to clipboard - [x] Use `Shift+Cmd+C` shortcut and verify it copies CSV to clipboard - [x] Go to Account > Preferences > Keyboard shortcuts and verify the "Copy results as CSV" toggle is present and functional - [x] Disable the shortcut in preferences, verify `Shift+Cmd+C` no longer triggers the copy - [x] Verify the same option appears in the logs export dropdown <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added "Copy as CSV" action to the results download menu, allowing users to quickly copy query results in CSV format to the clipboard. * Introduced a new hotkey preference setting to enable/disable the Shift+Meta+C keyboard shortcut for copying results as CSV. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Jordi EnricandClaude Sonnet 4.6
|
169a8ff44b |
feat(studio): add direct Upgrade compute CTA to exhaustion banners (#44675)
## Problem The `ResourceExhaustionWarningBanner` routed disk IO, CPU, and memory/swap exhaustion warnings to `/settings/infrastructure#<metric>` — an infra chart page with no direct fix available. The action button label "Learn more" didn't reflect a clear next step, and there was no way to get AI-assisted query optimization from the banner. ## Changes **Routing & CTAs** - Compute warnings (`disk_io`, `cpu`, `ram`) now route to `/settings/compute-and-disk` instead of the infra chart page - Free plan users are routed to `/org/[slug]/billing?panel=subscriptionPlan&source=resource_exhaustion_banner` - Primary CTA text changed to "Upgrade compute" for all compute warnings (paid and free plan) - Read-only mode CTA changed from "Learn more" to "Manage disk" **Troubleshoot dropdown** - For compute warnings (which have both a docs URL and an AI prompt), a "Troubleshoot" dropdown replaces the standalone "Learn more" button, offering: - Documentation — links to the relevant troubleshooting guide - Ask AI Assistant — opens the AI assistant with a pre-filled query to identify expensive queries via `pg_stat_statements` - For warnings with only a docs URL (read-only mode, disk space, auth), a direct "Learn more" button is shown as before **Telemetry** Two new events track user interactions with the banner: | Event | Fires when | Properties | |---|---|---| | `resource_exhaustion_banner_upgrade_clicked` | User clicks the primary CTA | `warningTypes: string[]`, `isFreePlan: boolean`, `destination: string` | | `resource_exhaustion_banner_ai_assistant_clicked` | User clicks "Ask AI Assistant" | `warningTypes: string[]`, `isFreePlan: boolean` | Both events include the standard `groups` payload (project + org). **Suppression fixes** - Banner is now hidden on `/settings/compute-and-disk` for paid-plan compute warnings (CTA would be a no-op) - Banner stays visible on `/settings/infrastructure` for compute warnings (CTA now links to a different page) **Description text** - Removed stale "Check the usage page for more recent and detailed statistics" from compute warning descriptions — no button in the banner leads there - Updated `multiple_resource_warnings` descriptions to reflect the upgrade-focused CTAs **Bug fixes** - Fixed: auth rate limit critical banner was showing when warning content had no title/description - Fixed: CTA disabled state now only applies to compute warnings while org data is loading (not all warning types) ## How to test - Trigger or mock a `disk_io_exhaustion`, `cpu_exhaustion`, or `memory_and_swap_exhaustion` warning - Paid plan: CTA reads "Upgrade compute" → `/project/<ref>/settings/compute-and-disk` - Free plan: CTA reads "Upgrade compute" → `/org/<slug>/billing?panel=subscriptionPlan&source=resource_exhaustion_banner` - Troubleshoot dropdown appears with Documentation and Ask AI Assistant options - Verify `is_readonly_mode_enabled` shows "Manage disk" CTA and a direct "Learn more" button (no dropdown) - Verify `disk_space_exhaustion` and auth warnings show a direct "Learn more" button (no dropdown) - Verify the banner is hidden on `/settings/compute-and-disk` for paid-plan compute warnings - Verify the banner is still visible on `/settings/infrastructure` for compute warnings - Verify `resource_exhaustion_banner_upgrade_clicked` and `resource_exhaustion_banner_ai_assistant_clicked` events fire with the correct properties --------- Co-authored-by: Claude Sonnet 4.6 <noreply@anthropic.com> |
||
|
kemal.earth
|
fa951a55a6 |
feat(studio): posthog events for scoped pats (#44850)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? This is a follow up for both our classic and scoped PAT's to add events for tracking created and deleted. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **Chores** * Enhanced telemetry for access token creation and removal. * Creation events now include token type (classic or scoped), expiry setting, scope/resource access and permission counts when applicable. * Removal events now include token type (classic or scoped). * Instrumentation added across token creation and deletion flows to improve analytics and auditing. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
|
83e5ee8c5c |
feat(studio): add advisor for public bucket rls (#44438)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? This connects the Advisor from the splinter repo. Below are the list of changes: - Register advisor which should appear in both the legacy Advisors and Advisors sidebar. - Adds a "Dismiss" button to the admonition inside the bucket view. - Makes the check for select policy on public buckets tiny bit stricter/truer. This is awaiting the [PR](https://github.com/supabase/splinter/pull/152) in splinter going in! <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added a security lint that flags public storage buckets allowing listing, with a direct "View bucket" link. * Users can dismiss public-bucket warnings per project+bucket for 14 days via a Dismiss button. * **Improvements** * Tightened policy detection to better target bucket-scoped select policies and avoid unrelated matches. * **Telemetry** * Added events for policy removal and dismiss-button clicks. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Danny White <3104761+dnywh@users.noreply.github.com> Co-authored-by: Claude Sonnet 4.6 <noreply@anthropic.com> |
||
|
|
6be596ea34 |
feat: add user preference to enable queue operations (#44366)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? - Remove queue operations from feature preview into settings - Refactor dashboard settings - Resolves DEPR-434 <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Dashboard settings panel in Account preferences with toggles for Inline Editor and Queue Operations; “Dashboard” added to project Configuration. * **Removed** * Old Inline Editor settings UI and the Queue Operations feature-preview UI removed. * **Refactor** * Consolidated dashboard preferences into a single settings surface; banners and actions now navigate to preferences; account/preferences layouts and back-navigation behavior adjusted for platform vs self-hosted. * **Tests** * Added tests for settings UI, menu generation, redirects, and local-storage. <!-- end of auto-generated comment: release notes by coderabbit.ai --> --------- Co-authored-by: Joshen Lim <joshenlimek@gmail.com> Co-authored-by: Danny White <3104761+dnywh@users.noreply.github.com> |
||
|
Mert YEREKAPAN
|
b9e83b25e1 |
feat(studio): adding upgrade button to header experiment (#44494)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES ## What kind of change does this PR introduce? - Add an always-visible "Upgrade to Pro" button in the dashboard header for free-plan users (GROWTH-615) - Button is gated behind a PostHog experiment (`headerUpgradeCta`) with `control` and `test` variants - Experiment exposure is tracked for both variants; click events are tracked when the button is clicked - Button reuses existing `UpgradePlanButton` component for routing, permissions, and billing logic ## What is the current behavior? <img width="3840" height="2160" alt="Arc 2026-04-02 16 36 22" src="https://github.com/user-attachments/assets/8a94db0c-06c8-4237-8ba5-6ac1fe111a56" /> ## What is the new behavior? <img width="3840" height="2160" alt="Arc 2026-04-02 16 36 12" src="https://github.com/user-attachments/assets/0e60d834-028b-49fd-845e-ce1b4cbcc960" /> ## Additional context Add any other context or screenshots. <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit * **New Features** * Added an upgrade call-to-action in the header and mobile navigation (visible on medium+ screens in platform builds) shown to free-plan users as part of a controlled experiment. * The CTA records experiment exposures and sends analytics for impressions and clicks, including the user's current plan, to measure engagement and upgrade interest. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |
||
|
Mert YEREKAPAN
|
f590319f0a |
feat(pricing): implement A/B experiment for pricing page flexibility/visibility (#44293)
## I have read the [CONTRIBUTING.md](https://github.com/supabase/supabase/blob/master/CONTRIBUTING.md) file. YES/NO ## What kind of change does this PR introduce? Includes 5 new variants to test pricing to solve cost flexibility and visibility concerns ## What is the current behavior? Current pricing page ## What is the new behavior? Variants: <img width="3840" height="2160" alt="CleanShot 2026-03-30 at 19 32 02@2x" src="https://github.com/user-attachments/assets/a4f3b048-fa0d-4137-9f24-2eb6d431f3c8" /> <img width="3840" height="2160" alt="CleanShot 2026-03-30 at 19 33 34@2x" src="https://github.com/user-attachments/assets/a9045a33-b8c3-4df1-a47d-00cf58495bb3" /> <img width="3840" height="2160" alt="CleanShot 2026-03-30 at 19 32 22@2x" src="https://github.com/user-attachments/assets/10511fc8-5e88-4e3c-baa1-56798009d86f" /> <img width="3840" height="2160" alt="CleanShot 2026-03-30 at 19 33 09@2x" src="https://github.com/user-attachments/assets/aa01aaf6-0e41-4466-bfc7-77ae912b6043" /> <img width="3840" height="2160" alt="CleanShot 2026-03-30 at 19 32 43@2x" src="https://github.com/user-attachments/assets/21834f7d-43cb-4981-9c29-934f44986714" /> <!-- This is an auto-generated comment: release notes by coderabbit.ai --> ## Summary by CodeRabbit ## Release Notes **New Features** - Launched A/B testing variants on the pricing page featuring customized pricing plan layouts, descriptions, and billing options based on your assigned experiment group. - Certain plan tiers now display optional flexibility information, hourly billing rates, and project scaling details to help optimize your cost estimation and plan selection. <!-- end of auto-generated comment: release notes by coderabbit.ai --> |












